 Log in

Ryan is joined by Gabriela Moreira, CEO at Quint, about why formal specification languages like TLA+ are essential for catching system design flaws before writing code, how Quint brings developer-friendly syntax and executability to formal methods, and the ways trace validation and model-based testing can verify AI-generated code against real-world production data.

|
Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
|

Pennsylvania, USA

Pennsylvania, USA

Most AI at work still starts the same way: a person opens a chat and types a prompt. No prompt, no work.
With Copilot Studio, that is changing. On October 15, Microsoft announced new Copilot Studio capabilities for delegating shared business processes to agents. Now rolling out through the Frontier program, they let agents built in Copilot Studio take care of tasks when they need to be done, without anyone prompting them. An email arrives, or it’s Tuesday morning and the weekly review is due, and the agent gets to work. It gathers the data, chases the missing explanations, remembers what was left open last time, and prepares the decision for people.
This is process automation with Copilot Studio agents. Rule-based flows already handle the predictable steps. Agents now take on the work between those steps, the parts that need judgment, follow-up and context. And they do it on their own, as part of the process rather than as a chat someone remembers to open.
What Copilot Studio brings in Frontier:
- Triggers → the agent starts the work. An email or a schedule starts the agent’s cycle, with no prompt needed. Soon agents can also use their own browser-enabled cloud computer.
- Agent accounts → the agent works as itself. It has its own credentials and scoped permissions in Microsoft 365. People can reach it in Teams and Outlook, @mention it in Office comments, and assign it tasks by email. Its actions are attributed to the agent, not to a person.
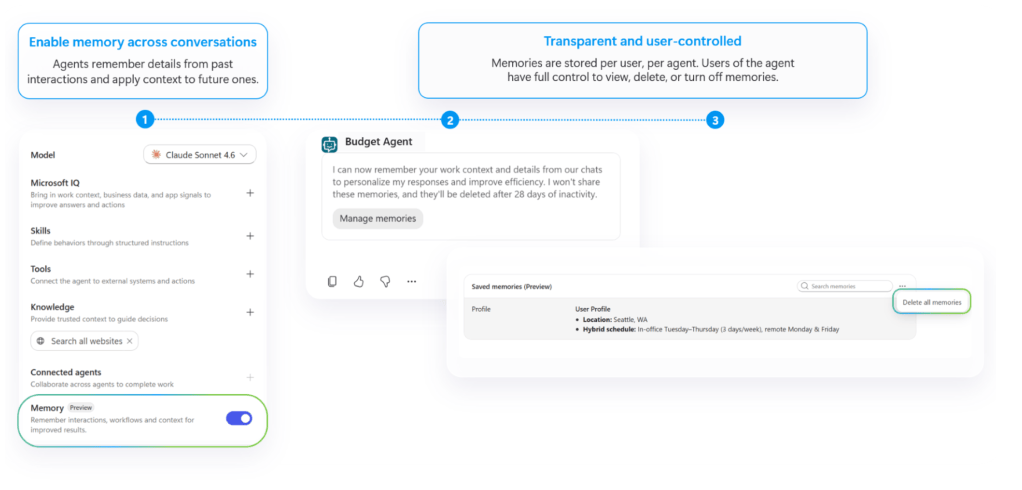
- Business process memory → each cycle builds on the last. Context and preferences carry forward, so nobody has to explain the process again.
- Agent refinements (coming) → the automation improves. The agent’s activity produces suggestions for turning stable steps into workflows, capturing reusable skills and choosing a better-suited model.
- Agent 365 → the agent is governed like any other identity. Agent accounts are provisioned and governed through Microsoft Agent 365, so admins get user-grade visibility and control.
Pro-code has made this possible for a while. Development teams have built agents that start on events, run under their own identities and keep state. With Copilot Studio, these become platform building blocks with admin controls, lifecycle management and attribution. Business units and makers will be able to automate shared processes with agents, not just developers.
This is how Copilot Studio helps organizations become AI-native: routine tasks get done because they need to be done, not because someone remembered to prompt for them. Agents prepare, follow up and remember. People decide.
It’s the next step in the story: first AI moved from answers to actions, then teams got a memory curated by AI, and now agents start the work themselves. Let’s take a closer look.
Triggers – the agent starts the work
This is the core of the announcement. Triggers in the GitHub Copilot harness let agents built on the harness stay “always on.” When configured, an external signal (like an email) or a set schedule starts the agent’s cycle, with no prompt needed.
That changes the role of AI in a process. Instead of waiting for someone to remember to ask, the agent runs its part of the work when the process needs it:
- On a schedule: every Tuesday before the budget review, at month-end close, before the weekly steering meeting.
- On an event: a proposal arrives by email, a supplier sends an update, a request lands in a shared mailbox.
Add the upcoming option for agents to use their own browser-enabled cloud computer, and processes that cross many systems become realistic candidates for redesign.
Automation that starts by itself needs clear limits, though. The more the agent does without a prompt, the more important it is to decide up front what it may do on its own and where it hands over to a person.
Agent accounts – the agent gets its own identity
An agent that starts work by itself also needs to work as itself. With an agent account, the agent works in Microsoft 365 with its own credentials, much like a person would.
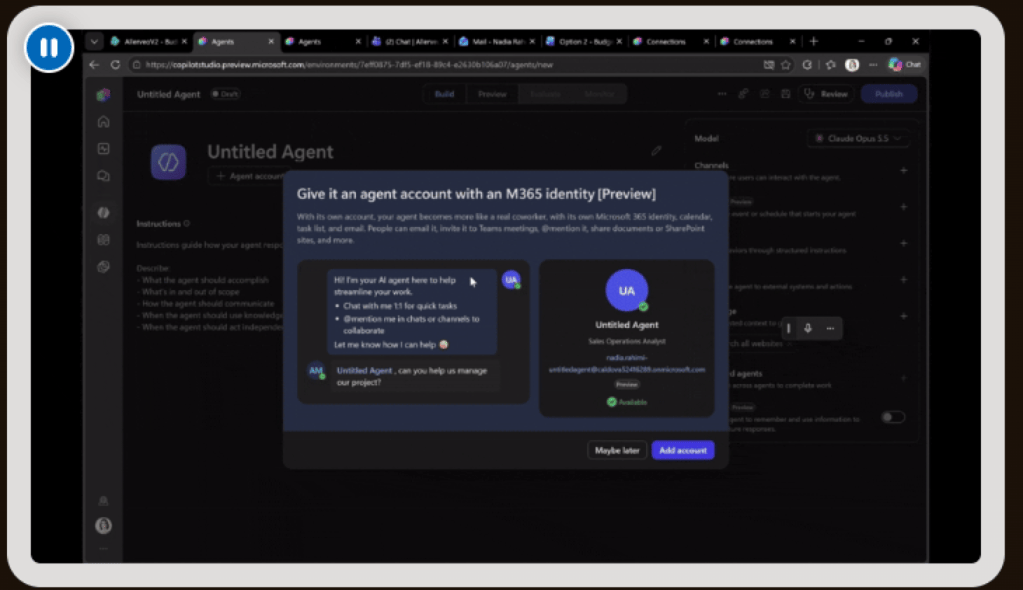
In practice:
- People can talk to the agent in Teams and Outlook to ask questions, assign work or give updates, without opening a separate agent chat for every task.
- The agent can be @mentioned in comments in Word, Excel and PowerPoint, just like any other process participant.
- Team members can delegate a task by Teams message or email and keep working. The agent carries on with the task in between.
- The agent works with other agents, tools and services using its own approved credentials and scoped permissions, not any individual user’s or maker’s credentials.
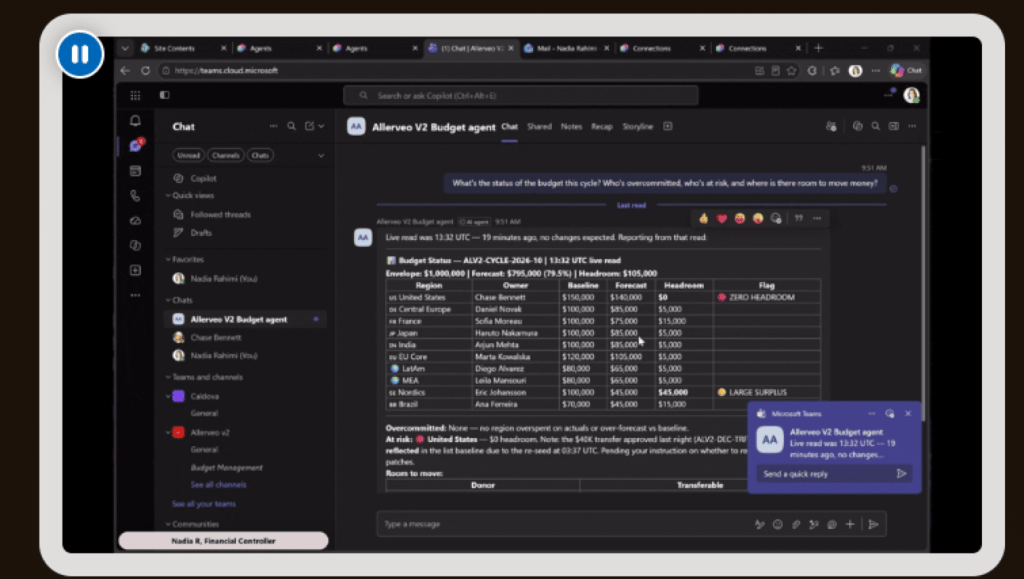
Why does this matter? In the previous post about the SharePoint knowledge base, Autopilot uploaded a meeting transcript “As you” after the user approved it. With agent accounts, the agent acts as itself.
That speaks directly to one of the points in From Answers to Actions with Work IQ: you need to be able to tell “the person did it” from “an agent did it.” Microsoft says work can now be attributed to the agent, while the process owner keeps control of its scope. That improves observability and traceability.
Admins can scope access, apply extra controls and manage the agent’s lifecycle. Microsoft says further access policies, quality and cost management, and lifecycle controls for these agents are planned for the coming months.
Business process memory – what one person teaches, everyone benefits from
Recurring processes have their quirks. “This cost center always reports late.” “Legal wants to see contracts over a certain value.” Today that knowledge sits in someone’s head, and it has to be explained again every time.
Business process memory lets the agent carry users’ preferences and process context into each new cycle. When one person points out a quirk to the agent, it becomes shared knowledge that everyone else benefits from. People need to repeat less every time they hand work to the agent.
Makers stay in control. Through the agent’s instructions, they set how the retained context is used and which business records and policies are authoritative.
This pairs nicely with the SharePoint knowledge base:
- The knowledge base is the team’s memory: what we know.
- Business process memory is the process’s memory: how this work runs here.
Both address the same old problem: the person who knows leaves, and part of the memory leaves with them.
Agent refinements – coming next
Over the coming months, Microsoft plans to roll out agent refinements. These use the agent’s own activity to suggest improvements to the maker, who can review, test and apply them:
- turn stable, repeated steps into workflows
- capture reusable approaches as skills
- point out recurring ambiguity in the instructions
- suggest a better-suited model for the task
That is a smart loop: the agent helps its maker improve both quality and cost.
What it looks like in practice
Microsoft’s example is a budget management agent built by a finance lead:
- Every Tuesday the agent prepares for the weekly review. Using its own credentials, it gathers planning records, compares forecasts with the explanations submitted, and asks budget owners about unexplained changes.
- The finance team adds context by @mentioning the agent in Teams or replying in Outlook.
- The agent writes a concise summary of the figures, explanations and gaps, and escalates decisions to finance.
- People decide whether to revise the forecast, ask for more information or approve the plan.
- In the next cycles the agent carries forward the review requirements and open questions.
The team spends less time piecing together what happened and keeps full authority over allocations and spending.
Early customers are already using these capabilities. At Ooredoo Qatar, an executive business-case review agent works across Outlook, Teams and Word. It reviews incoming proposals against company policy and precedent and prepares decision-ready briefs for executives.
Agent 365 – where the agent gets its identity and governance
If an agent is going to work like a colleague, it also needs to be managed like one. That is the role of Microsoft Agent 365, the control plane for agents. It has been generally available for the Commercial segment since May 1, 2026, and it is built around three things: observe, govern and secure the agents in an organization.
For agent accounts, Agent 365 is not an optional add-on in the background. Agent 365 provisions and governs the agent accounts, giving admins the same kind of visibility and control they have over user accounts.
What the agent gets
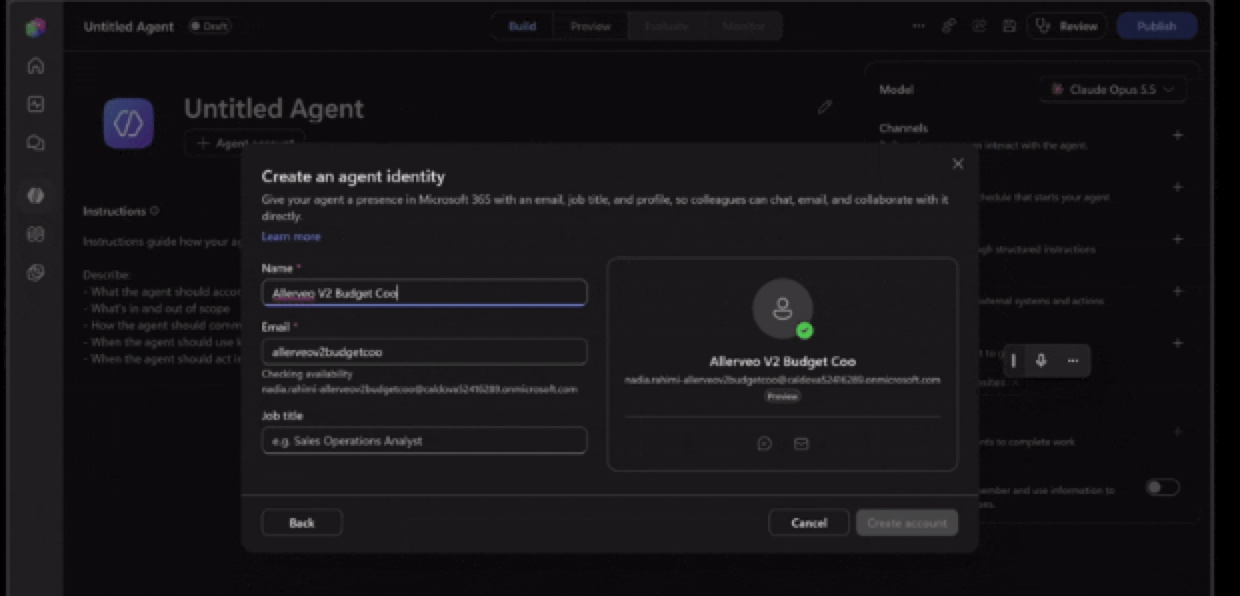
When a Copilot Studio agent with an account is published, it is provisioned with:
- its own mailbox, so it can send and receive email and be added to distribution lists
- a presence in Teams and in the organization’s directory, so people can find and @mention it like a colleague
- its own Microsoft Entra account and Entra Agent ID, so admins can govern and audit it like any other identity
A nice detail: the agent’s email address uses the maker’s alias as a prefix, and the agent reports to the maker. Just like a new hire, the agent has a manager. In this preview, the prefix and the reporting relationship can’t be changed, and the email address is fixed once the agent is published, so plan the agent’s identity before publishing.
What admins get
Copilot Studio agents plug into Agent 365 automatically, with no manual registration or SDK work:
- Registry: agents appear in the agent registry in the Microsoft 365 admin center with their name, publisher, connectors and environment details.
- Observability: agent and tool invocations flow automatically to the Microsoft 365 admin center, Microsoft Defender and Microsoft Purview.
- Governance: lifecycle management, access control and compliance across Microsoft 365 admin center, Microsoft Entra and Microsoft Purview, including Conditional Access policies that target the agent’s identity.
This is also where the pro-code point from the beginning shows. Pro-code agents need their identity set up manually. Copilot Studio creates the agent identity automatically and connects it to Agent 365 governance.
Good to know before designing a process
This is a preview, and the current limitations are worth reading before choosing the first process:
- Protected documents are off-limits. Agents with an account can’t read documents protected with labels such as Confidential or Internal Only. Compare that to the previous post, where Autopilot, acting as the user, kept the “Confidential \ Internal Only” label on the transcript it uploaded. An agent with its own account works differently from an agent acting as you.
- Memory is shared, with no privacy boundary between users. Anything shared with the agent can be summarized and used in responses to other users, even users who don’t have access to the original file or chat. There is no opt-out in this preview. This is the most important design point. The agent’s People card and first conversation tell users about it, but the process owner should make it clear up front what is OK to share with the agent.
- Internal only. The agent doesn’t respond to anyone outside the tenant.
- New documents, not co-authoring. The agent can generate new documents but can’t yet edit existing ones through co-authoring or make targeted edits from a comment.
- Email audience is limited to conversations with up to 250 people.
- EEA note: agent accounts are available in the European Economic Area, but the agent appears in Teams only if the tenant also licenses Teams separately.
What this means
The agent is becoming a colleague, not just a tool. It has an identity, a manager, a place in Teams and Outlook, memory and a schedule. That makes it easier to use, and it also makes it something that needs to be managed like a colleague.
A few questions to sort out before the first production process:
- Who owns the agent? A process owner, not just the maker who built it, even though the agent reports to the maker in the directory.
- What does the agent’s account have access to, and who reviews that access when the process changes?
- What may be shared with the agent? Shared memory is shared knowledge, and it can also hold shared mistakes or information that shouldn’t spread across the team.
- Where does the agent escalate, and to whom? The budget example only works because the decisions stay with finance.
- What happens when the agent is retired? Lifecycle now matters for agents as much as for people, and so does freeing up its license.
The three questions from the Work IQ post still apply: Is it allowed? Is it allowed for an agent? Does a human need to approve this specific action? The difference now is that the agent itself is the identity being asked.
Availability
These features are rolling out now through the Frontier program, with more capabilities coming soon. Agent refinements and additional admin controls are planned for the coming months. Agent accounts require Frontier enrollment, a maker license with Agent 365 (Microsoft 365 E5 + Agent 365 add-on, or Microsoft 365 E7), and a Microsoft 365 Frontier for AI Teammates license per agent, with usage billed in Copilot Credits.
Start with one process
Microsoft’s advice matches mine: start with one shared business process. Pick one that recurs, has clear decision points, and currently relies on a few people remembering how it works. In this preview, also pick one where the content isn’t protected and the team is comfortable sharing it with the agent.
The previous posts covered how AI moves from answering to acting, and how teams gain a memory curated by AI. This step gives the work itself an owner that doesn’t forget, doesn’t go on holiday, and starts on time, without waiting for a prompt. People stay in the driver’s seat.
Which shared process in your organization would you hand to an agent first?
Previously in this series: From Answers to Actions with Work IQ and SharePoint Knowledge Base – Team Memory, Curated by AI.
Sources and further reading
- Microsoft Copilot Blog – Delegate shared business processes to agents that are more persistent and proactive with Microsoft Copilot Studio
- Microsoft Learn – Give your agent an account (Frontier)
- Microsoft Learn – Overview of Microsoft Agent 365
- Microsoft Learn – Build agents with Copilot Studio and Agent 365

Pennsylvania, USA
This week, we discuss AI yes/no deciders, the SaaS apocalypse, Bending Spoons, and Oxide's funding. Plus, why Google Docs still has no dark mode.
Watch the YouTube Live Recording of Episode 594
Runner-up Titles
- Lightweight Mark Zuckerberg
- I'm on a mailing list
- It respects the dark mode
- You can't be Greasemonkeying your way through life
- What are the optics of AI?
- I was getting into my groove
- Is it worth \$7.5 billion dollars
- The ArtCrafting people
- That is the SaaSpocalypse
- You should see the stuff I make in my bathtub
- Not everything has to be acquired
- The software industry is becoming the CPG industry
- The floor has fallen out of the software industry
- Brand is king
- Horse shampoo in the human shampoo section
- I'm doing real work, I need a black background
- It felt like the sun
- The devil's stream
Rundown
- Jev / TypeSafe: a \$7.5B decision model with no text output
- Andreessen Horowitz Backs Jev Maker at \$7.5 Billion Value
- Understanding Jev, the new model everyone is talking about
- TypeSafe AI Raises \$40 Million Seed Funding At \$200 Million Valuation
- Workday is using TypeSafe's Jev to build user interfaces on the fly
- Andrej Karpathy says only 5,000 people have seen what AI can really do
- Andreessen Horowitz Backs Jev Maker at \$7.5 Billion Value
- "Software is over": AI clones of Adobe and Office, and what open source is becoming
- “Software is over”: AI developer takes aim at Adobe with open source clones
- Creator of free Adobe clones unveils open-source Microsoft Office replacements
- Open Source as We Know It Is Dead
- software doesn't need to be readable anymore. it needs to be explainable.
- Bending Spoons Deploys AI to Overhaul Acquired Software Companies
- “Software is over”: AI developer takes aim at Adobe with open source clones
- Neocloud money: backlog, concentration and the bond market
- AI computing startup Lambda to raise \$4B ahead of planned IPO
- Axe Compute rings Nasdaq bell with \$3.45B neocloud GPU backlog
- Amazon in Talks to Buy AI Startup Decart for Around \$7 Billion
- Compute constraints help Oxide hit \$6B
- Oxide raises \$445M Series D
- IMF cites AI slowdown, spiking yields as looming global market risks
- AI computing startup Lambda to raise \$4B ahead of planned IPO
Relevant to your Interests
- Meta releases its first frontier model, Muse Wonder
- Claude now works in Google Docs, Sheets, and Slides
- Introducing the Anthropic Cyber Mission
- AWS AgentCore security undone by prompt requesting credentials
- ComfortDelGro to pull workloads back from public cloud
- Broadcom introduces VMware HyperArmor
- 11:11 Systems acquires select IBM VMware cloud customers
- CME Group announces cloud migration milestones
- Redesigning source control at Anthropic
- Netflix Lays Off 6% of Employees, Elimination About 1,000 Jobs in Biggest Cutbacks to
- Memphis City Council meeting erupts into chaos over Musk data centers
- Conservation group calls moratorium on AI data centers on US public lands
- Amazon responds to data center backlash, says it no longer uses NDAs
- Oracle's AI data center push hits a power bottleneck
Conferences
- DevOpsDays Istanbul, Oct 24th, 2026, Coté keynoting.
- VMware User Group, Orlando, Oct 20-22, 2026
- VMware Explore London, Nov 18-19, 2006, Coté speaking.
- Cloud Native Denmark, Nov 19th, 2026, Coté keynoting, Discount Code: CSVFTW
- Build Stuff, Dec 2-4, 2026, Vilnius, Lithuania. Coté speaking.
- cfgmgmtcamp, Ghent, Belgium, February 1-3, 2027
- SCALE 24x Pasadena, CA, April 1-4, 2027
SDT News & Community
- Join our Slack community
- Email the show: questions@softwaredefinedtalk.com
- Free stickers: Email your address to stickers@softwaredefinedtalk.com
- Follow us on social media: Twitter, Threads, Mastodon, LinkedIn, BlueSky
- Watch us on: Twitch, YouTube, Instagram, TikTok
- Book offer: Use code SDT for \$20 off "Digital WTF" by Coté
- Sponsor the show
- Sponsor more podcasts with Failover Media
Recommendations
- Brandon: YOU CAN SEE EVERYTHING Official Trailer
- Matt: What I Talk About When I Talk About Running
- Coté: FileRouter
Edited and produced with PodEditor, the native Mac podcast editor.
Download audio: https://aphid.fireside.fm/d/1437767933/9b74150b-3553-49dc-8332-f89bbbba9f92/bf37b187-8b2c-46f1-833f-0001038d2cb5.mp3
Pennsylvania, USA
If you have ever tried to export a SQL Server database to a .bacpac file with sqlpackage, you have most likely run into the dreaded SQL71627 error, complaining about a Windows user or login. I ran into it myself a few years ago, and the only workaround was to drop the offending users from the database (or a copy of it) before running the export.
With sqlpackage 170.6.28-preview, that workaround is no longer needed. The Export action has two new properties that let you remove objects that are not compatible with Azure SQL Database while exporting, and write a report of what was removed.
.dacpac vs .bacpac
Before looking at the new options, a quick recap of the two file types, as they are often confused.
A .dacpac file contains the schema of a database - tables, views, procedures, users, permissions and so on - described in a model.xml file. You get a .dacpac by building a SQL Database project, or by running sqlpackage /a:Extract against a live database. You deploy it with sqlpackage /a:Publish, which compares the .dacpac with the target database and generates an incremental script that brings the target up to date. The target can be a new or an existing database, and the existing data in the target is kept. A .dacpac can optionally contain table data as well (/p:ExtractAllTableData=true), but it is normally used for schema only.
A .bacpac file contains both the schema and the data from all tables in the database. You create it with sqlpackage /a:Export and restore it with sqlpackage /a:Import, which always creates a new database (or imports into an empty one). Think of it as a logical, portable backup. Unlike a native .bak backup, it can be restored to a different SQL Server version and to Azure SQL Database.
Both are just zip files, so you can rename them to .zip and have a look inside. A .bacpac has a Data folder with the table data in BCP format next to the model.xml file.
Microsoft has more details in the data-tier applications documentation.
Why the export fails
The .bacpac format was designed for moving databases to and from Azure SQL Database. For that reason, the Export action always validates the schema against Azure SQL Database, even if you plan to import the .bacpac to another SQL Server instance. Any object that is not supported in Azure SQL Database makes the export fail, and the most common offenders are Windows users and logins.
Here is an export of a LocalDB database with a Windows user:
sqlpackage /a:Export /scs:"Data Source=(localdb)\mssqllocaldb;Initial Catalog=TestBed3;Integrated Security=false;Encrypt=false" /tf:TestBed.bacpac

Connecting to database 'TestBed3' on server '(localdb)\mssqllocaldb'.
Extracting schema
Extracting schema from database
Resolving references in schema model
Validating schema model
Validating schema model for data package
Validating schema
*** Error exporting database:One or more unsupported elements were found in the schema used as part of a data package.
Error SQL71627: The element User: [winadmin] has property AuthenticationType set to a value that is not supported in Microsoft Azure SQL Database v12.
Error SQL71627: The element Login: [MYPC\Administrator] has property IsMappedToWindowsLogin set to a value that is not supported in Microsoft Azure SQL Database v12.
The DacFx issue SqlPackage - option to skip Windows logins (microsoft/DacFx#426) was originally reported for a SQL Server connected to Azure Arc, where the export failed on NT AUTHORITY\SYSTEM. But it is not an Azure Arc issue - any database with a Windows authenticated user will fail in the same way.
The new options
sqlpackage 170.6.28-preview adds these two properties to the Export action:
/p:ExcludePlatformIncompatibleObjects=({None|SqlAzureV12} 'None')

Specifies the target platform whose incompatible objects should be excluded from the exported package and included in the compatibility report. Use None to disable exclusion

/p:CompatibilityReportPath=(STRING)

Specifies the path for the JSON Azure compatibility report. When not specified, no JSON report file is written.
The default for ExcludePlatformIncompatibleObjects is None, so the existing behaviour does not change unless you opt in. Set it to SqlAzureV12 to have incompatible objects removed from the exported package. The source database is not modified.
Running the same export again with the new options:
sqlpackage /a:Export /scs:"Data Source=(localdb)\mssqllocaldb;Initial Catalog=TestBed3;Integrated Security=false;Encrypt=false" /tf:TestBed.bacpac /p:ExcludePlatformIncompatibleObjects=SqlAzureV12 /p:CompatibilityReportPath=testbed3.json

Connecting to database 'TestBed3' on server '(localdb)\mssqllocaldb'.
Extracting schema
Extracting schema from database
Resolving references in schema model
Validating schema model
Validating schema model for data package
Validating schema
Prune Azure SQL Database incompatible objects
Processing tables for data extraction
Exporting data from database
Exporting data
Processing Export.
Processing Table '[dbo].[Artist]'.
Processing Table '[dbo].[PlaylistTrack]'.
Processing Table '[dbo].[InvoiceLine]'.
Processing Table '[dbo].[Customer]'.
Processing Table '[dbo].[Employee]'.
Processing Table '[dbo].[Track]'.
Processing Table '[dbo].[MediaType]'.
Processing Table '[dbo].[Genre]'.
Processing Table '[dbo].[Playlist]'.
Processing Table '[dbo].[Invoice]'.
Processing Table '[dbo].[Album]'.
Processing Table '[sqlproj].[DeploymentHistory]'.
Azure Compatibility Report:
Excluded objects: 3
Warnings: 2

Successfully exported database and saved it to file 'TestBed.bacpac'.
Notice the new "Prune Azure SQL Database incompatible objects" step, and the short summary at the end.
The compatibility report
If you specify CompatibilityReportPath, you also get a JSON file with the details. This is the report from the export above:
{
  "exportDate": "2026-10-16T07:59:27.1555006Z",
  "sourceDatabaseName": "TestBed3",
  "sourceServerVersion": "Microsoft SQL Server 2025 (RTM-CU8-GDR) (KB5122769) - 17.0.4085.5 (X64) \n\tAug 26 2026 17:29:26 \n\tCopyright (C) 2025 Microsoft Corporation\n\tExpress Edition (64-bit) on Windows 10 Enterprise 10.0 \u003CX64\u003E (Build 26200: ) (Hypervisor)\n",
  "targetPlatform": "AzureSqlDatabase",
  "summary": {
	"totalObjectsProcessed": 257,
	"objectsExcluded": 3,
	"warningsGenerated": 2
  },
  "excludedObjects": [
	{
	  "objectType": "SqlLogin",
	  "schemaName": null,
	  "objectName": "MYPC\\Administrator",
	  "excludedBecause": "DirectlyUnsupported",
	  "reason": "Windows authentication logins are not supported in Azure SQL Database.",
	  "recommendation": "Create a contained database user or use Microsoft Entra authentication.",
	  "warningCode": "ASDB_WINDOWS_LOGIN",
	  "dependsOn": []
	},
	{
	  "objectType": "SqlUser",
	  "schemaName": null,
	  "objectName": "winadmin",
	  "excludedBecause": "DirectlyUnsupported",
	  "reason": "Windows-authenticated database users are not supported in Azure SQL Database.",
	  "recommendation": "Create a contained database user or use Microsoft Entra authentication.",
	  "warningCode": "ASDB_WINDOWS_USER",
	  "dependsOn": []
	},
	{
	  "objectType": "SqlPermissionStatement",
	  "schemaName": "Grant.Connect.Database",
	  "objectName": "dbo",
	  "excludedBecause": "DependsOnExcludedObject",
	  "reason": "Windows authentication logins are not supported in Azure SQL Database.",
	  "recommendation": "Create a contained database user or use Microsoft Entra authentication.",
	  "warningCode": "ASDB_WINDOWS_LOGIN",
	  "dependsOn": [
		"MYPC\\Administrator",
		"winadmin"
	  ]
	}
  ],
  "warnings": [
	{
	  "objectType": "SqlDatabaseOptions",
	  "schemaName": null,
	  "objectName": null,
	  "warningCode": "SqlDatabaseOptions.IsTornPageProtectionOn",
	  "message": "Property \u0027IsTornPageProtectionOn\u0027 was reset to its target-platform default. Property is not supported on the target platform.",
	  "recommendation": "Review the Azure SQL Database compatibility report."
	},
	{
	  "objectType": "SqlDatabaseOptions",
	  "schemaName": null,
	  "objectName": null,
	  "warningCode": "SqlDatabaseOptions.PageVerifyMode",
	  "message": "Property \u0027PageVerifyMode\u0027 was reset to its target-platform default. Property is not supported on the target platform.",
	  "recommendation": "Review the Azure SQL Database compatibility report."
	}
  ]
}
A few things worth noting:
excludedObjectslists everything that was left out of the .bacpac. TheexcludedBecausevalue tells you if the object itself is unsupported (DirectlyUnsupported), or if it was removed because it depends on an excluded object (DependsOnExcludedObject). In this case theGRANT CONNECTpermission for the Windows user was removed as well, as it would be invalid without the user.- Each entry has a
reasonand arecommendation, so the report doubles as a to-do list for setting up access in the new database, for example with Microsoft Entra authentication or contained database users. warningslists properties that were not removed, but reset to the Azure SQL Database default value - here two database options related to page verification.
The report is a good thing to keep with the .bacpac file, so you know exactly what is missing after the import.
Getting the preview
The feature is in the 170.6.28-preview release of sqlpackage. If you use the .NET tool, you can install or update to the preview like this:
dotnet tool install -g microsoft.sqlpackage --version 170.6.28-preview
Summary
Exporting a database with Windows users to a .bacpac no longer requires you to clean up the database first. Add /p:ExcludePlatformIncompatibleObjects=SqlAzureV12 to the Export command to leave out objects that Azure SQL Database does not support, and add /p:CompatibilityReportPath to get a JSON report of what was excluded and why.
As this is a preview, please give it a try and report any issues or feedback in the DacFx GitHub repository.
Pennsylvania, USA

PowerToys Preview v0.102.2883.0
This is a preview-channel build for the PowerToys 0.102 release train, produced from the stable branch. It follows v0.102.2862.0; these notes cover changes since that preview, not the complete 0.102 versus 0.101 changelog. This is not the final stable release.
Installer Hashes
| Description | Filename | sha256 hash |
|---|---|---|
| Per user - x64 | PowerToysUserSetup-0.102.2883.0-x64.exe | 8F76B417BD374AA75557DF8CE4EE28430D5F0B734E94B9E91FFE4DA0579AA52F |
| Per user - ARM64 | PowerToysUserSetup-0.102.2883.0-arm64.exe | F739926D12AA251D683912B88FD1EA00B3A864089745A49A53D4F3EDFD5E2FCD |
| Machine wide - x64 | PowerToysSetup-0.102.2883.0-x64.exe | 8E7D8608CE97AF984E0E0A3825EA570DD2708C4410F625C75FFC25065C33F3D2 |
| Machine wide - ARM64 | PowerToysSetup-0.102.2883.0-arm64.exe | 9F7D98587FCE90EE4075018455E758E1A33E48ED3B2FBC864D508E6B52DFC26E |
Highlights
- ZoomIt: Added opt-in offline snip dictation for pasting screenshots together with transcribed speech.
- Peek: Added plain-text fallback previews and command-line support for multiple files and folders.
- Keyboard Manager: Added searchable key selection for empty remaps in the new editor and limited recording to the foreground editor.
- Command Palette: Continued loading results in underfilled views and when keyboard navigation reaches the loaded end of a list.
- Command Palette: Fixed in-place Adaptive Card updates in release builds and enabled custom elements to refresh without rebuilding the card.
- Command Palette: Avoided repeated writes of unchanged provider and fallback settings during startup.
- Settings: Added an interactive animated welcome scene and fixed memory growth when navigating between Home and General.
- General: Prevented startup and read-only Settings refreshes from overwriting existing preferences.
- CursorHide: Refreshed the former Auto Hide Cursor branding, icon, and behavior controls in Settings.
Advanced Paste
- Fixed the CLI root --version option to print the executable version and exit without requiring a subcommand in #51298 by @MuyuanMS
Command Palette
- Fixed Adaptive Cards updating in place in release builds and enabled custom elements to refresh without rebuilding the entire card in #51204
- Loaded additional result batches when the first list or grid page does not fill the window, so more items remain accessible without a scrollbar in #51285 by @jiripolasek
- Loaded the next result batch when keyboard navigation reaches the end of the current list, preserving selection until loading completes in #51287 by @jiripolasek
- Fixed Ctrl+Enter targeting the wrong command in context-menu submenus and delayed the initial highlight until navigation or filtering in #51290 by @jiripolasek
- Avoided repeatedly saving unchanged provider and fallback settings during startup in #51353
CursorHide
- Renamed Auto Hide Cursor to CursorHide in Settings and refreshed its icon, behavior controls, and new-feature indicators in #51123 by @Copilot and @LegendaryBlair
General
- Prevented startup and read-only Settings refreshes from overwriting preferences with partially initialized or stale module states in #51115 by @LegendaryBlair and @Copilot
Keyboard Manager
- Added searchable key selection for empty remaps in the new editor, limited recording to the foreground editor, and restored Tab navigation while recording in #51150 by @Copilot
Peek
- Added command-line previews for multiple files and folders, with improved relative-path handling and argument validation in #49724 by @daverayment
- Added plain-text previews for text files with otherwise unsupported extensions instead of showing only file information in #50020 by @eglavin and @claude
Settings
- Added an interactive animated welcome scene featuring PowerToys module icons in #50873 by @Copilot
- Fixed retained pages and view models that caused memory use to grow when navigating between Home and General settings in #51060 by @dotMorten and @Copilot
ZoomIt
- Added opt-in offline snip dictation so a screenshot and its spoken description can be transcribed and pasted together in #51286 by @MarioHewardt, @markrussinovich, @Copilot, and @foxmsft
Development
- Made new Windows platform-compatibility analyzer violations fail builds so unsupported API calls are caught earlier in #51063 by @Copilot
- Updated outdated third-party launcher plugin and author links in #51126 by @karan5028ji and @LegendaryBlair
- Removed an obsolete Settings screenshot reference from the module project-template documentation in #51334 by @mmustafasenoglu
- Standardized spacing before comments in module UI tests in #51264
- Reused JSON serializer options in Advanced Paste UI tests in #51280
- Replaced broad message passing with explicit Command Palette control and view-model ownership to support independent navigation surfaces in #51038
- Extracted Command Palette page creation and initialization into a shared navigation service while preserving navigation behavior in #51091 by @Copilot
- Removed the superseded Toolkit-specific neutral-language workaround while retaining shared official-build assembly metadata generation in #51291 by @LegendaryBlair and @Copilot
- Pinned the Command Palette extension SDK build version and prepared its signing runtime for more predictable release builds in #51326 by @LegendaryBlair and @Copilot
- Made Command Palette Extension Gallery tests use deterministic synchronization to avoid intermittent ordering failures in #51340 by @foxmsft
- Kept Command Palette test page contexts alive through execution and cleanup to prevent intermittent view-model test failures in #51355 by @jiripolasek
- Aligned multiline argument formatting across module UI tests without changing test behavior in #51257
- Normalized FancyZones UI-test file endings for consistent analyzer compliance in #51258
- Split FancyZones and File Locksmith UI-test helper types into matching source files in #51259
- Ordered System using directives consistently in FancyZones UI tests in #51262
- Normalized split-argument layout in FancyZones, Advanced Paste, and Environment Variables UI tests in #51265
- Removed unnecessary parentheses from FancyZones UI tests in #51267
- Aligned initializer indentation in FancyZones and Mouse Utilities UI tests in #51268
- Removed redundant blank lines from FancyZones UI tests in #51272
- Added consent-aware command and result telemetry for the Light Switch and PowerDisplay CLIs without changing their output or exit codes in #51315
- Resolved possible-null dereference warnings in Advanced Paste and Mouse Utilities UI tests in #51274
- Made Peek UI-test formatting use explicit format providers for consistent behavior across locales in #51260
- Normalized closing-brace spacing in Peek UI tests in #51273
- Resolved nullable-argument warnings in Peek UI tests in #51275
- Aligned nullable argument types in Peek UI tests in #51276
- Used direct indexing for indexable collections in Peek UI tests in #51278
- Reused constant argument arrays in Peek UI tests in #51279
- Aligned PowerRename UI-test comment spacing with analyzer requirements in #51263
- Removed a duplicate shared-suppression source entry from the PowerRename UI-test project in #51282
- Resolved reserved-keyword naming warnings in Screen Ruler UI tests in #51277
- Aligned Settings UI-test parameter names with analyzer conventions in #51271
- Made culture-sensitive operations explicit in Workspaces UI tests in #51261
- Aligned Workspaces UI-test parameter-list formatting with analyzer requirements in #51266
- Standardized spacing between Workspaces UI-test members in #51269
- Kept cleanup exceptions out of finally clauses in Workspaces UI tests in #51281
- Placed readonly fields consistently in ZoomIt UI tests in #51270
Changes needing final review
- Restored strict resource-language, identifier-naming, and MVVM build diagnostics in direct stable commit ce7edd480bc6, reapplying the exact change from #51065 after the official-build metadata fixes by @LegendaryBlair and @Copilot. This direct reapplication has no separate PR.
Pennsylvania, USA
Next Page of Stories