Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
165381 stories
·
33 followers

Daily Reading List – November 19, 2026 (#913)

1 Share

Everybody is going through something, so I appreciated a couple of items in today’s queue related to resilience, and dealing with change.

[article] When AI-Generated Data Becomes Tomorrow’s Ground Truth. Are we tracking decision lineage, and respecting that answers start carrying authority? Food for thought.

[blog] Introducing Tool Retrieval in the Gemini API. I’m glad we’re supporting this pattern now. Defer tool loading, and the model grabs what it needs when it needs it. No more passing all the tool metadata with every prompt.

[blog] Building always-on agents. It’s a different set of considerations. When agents are stateful, proactive, and event-driven, you design a specific architecture. Good post from Anthropic.

[blog] Spring Boot 4 + Java 25 on Cloud Run: 62% faster cold starts. Java can be fast, but you have to do it on purpose. This post shows how some optimizations following a version upgrade shaved a lot of startup time.

[article] Replit’s agent swarms built an app monitoring platform in 2 days on a $3K budget. Now, it’s offering them to customers. Swarms are big right now. I wonder how much of this “provide light direction and let the agent figure it out” will play out the way we think.

[blog] Scaling massive AI/ML workloads with IPv6 on Google Kubernetes Engine clusters. We’re still getting by with IPv4, 15+ years after we “ran out.” But it’s great that IPv6 support is coming to Kubernetes here.

[blog] How to Bounce Back After Setbacks. What story are you telling yourself when things go wrong? Is it oriented around growth? That story matters.

[blog] Building an agentic stack in Envoy: routing models, tokens, and MCP. Developers may not appreciate components like Envoy, but that’s ok. It’s an increasingly-important part of the platforms we’re using.

[blog] Building the Agent Host Protocol for sessions that continue across devices. GitHub wanted a way to decouple the “one integration per client” mode for agents. Hence, this new protocol.

[blog] AI Code Review: Spend Human Attention Where It Matters. Being overly trusting is a mistake, whether it’s human-led or agent-led code.

[article] Our Favorite Management Tips on Managing Change Fatigue. You won’t see the rate of change slow down. But we can become more resilient, and take command in certain ways.

[blog] Sashiko: Lessons from building an agentic code review system for Linux. Here’s some very cool work we did for the Linux project that results in faster patching and safer releases.

Want to get this update sent to you every day? Subscribe to my RSS feed or subscribe via email below:


Read the whole story
alvinashcraft
35 seconds ago
reply
Pennsylvania, USA
Share this story
Delete

Azure DevOps integration with the GitHub Copilot app (public preview)

1 Share

We’re excited to announce the public preview of Azure DevOps integration in the Copilot app. You can now start agent sessions that work directly with your Azure DevOps repositories to create branches, make code changes, commit changes, and open pull requests. This brings GitHub Copilot’s coding agents to teams using Azure DevOps repositories.

What is the Copilot app?

The GitHub Copilot app is a standalone desktop application that lets developers delegate coding tasks to AI agents. You can ask Copilot to explore a codebase, implement changes, fix bugs, and create pull requests, all from one place.

The app also lets you manage multiple agent sessions and review code changes in one place. With Azure DevOps integration, you can now use these capabilities with repositories hosted in Azure Repos.

Using the Copilot app with Azure DevOps

The Azure DevOps integration lets you connect Azure Repos repositories to the Copilot app and delegate coding tasks to AI agents. Agents can create branches, make code changes, commit changes, and open pull requests. Multiple agent sessions can also run in parallel, allowing different tasks to progress at the same time.

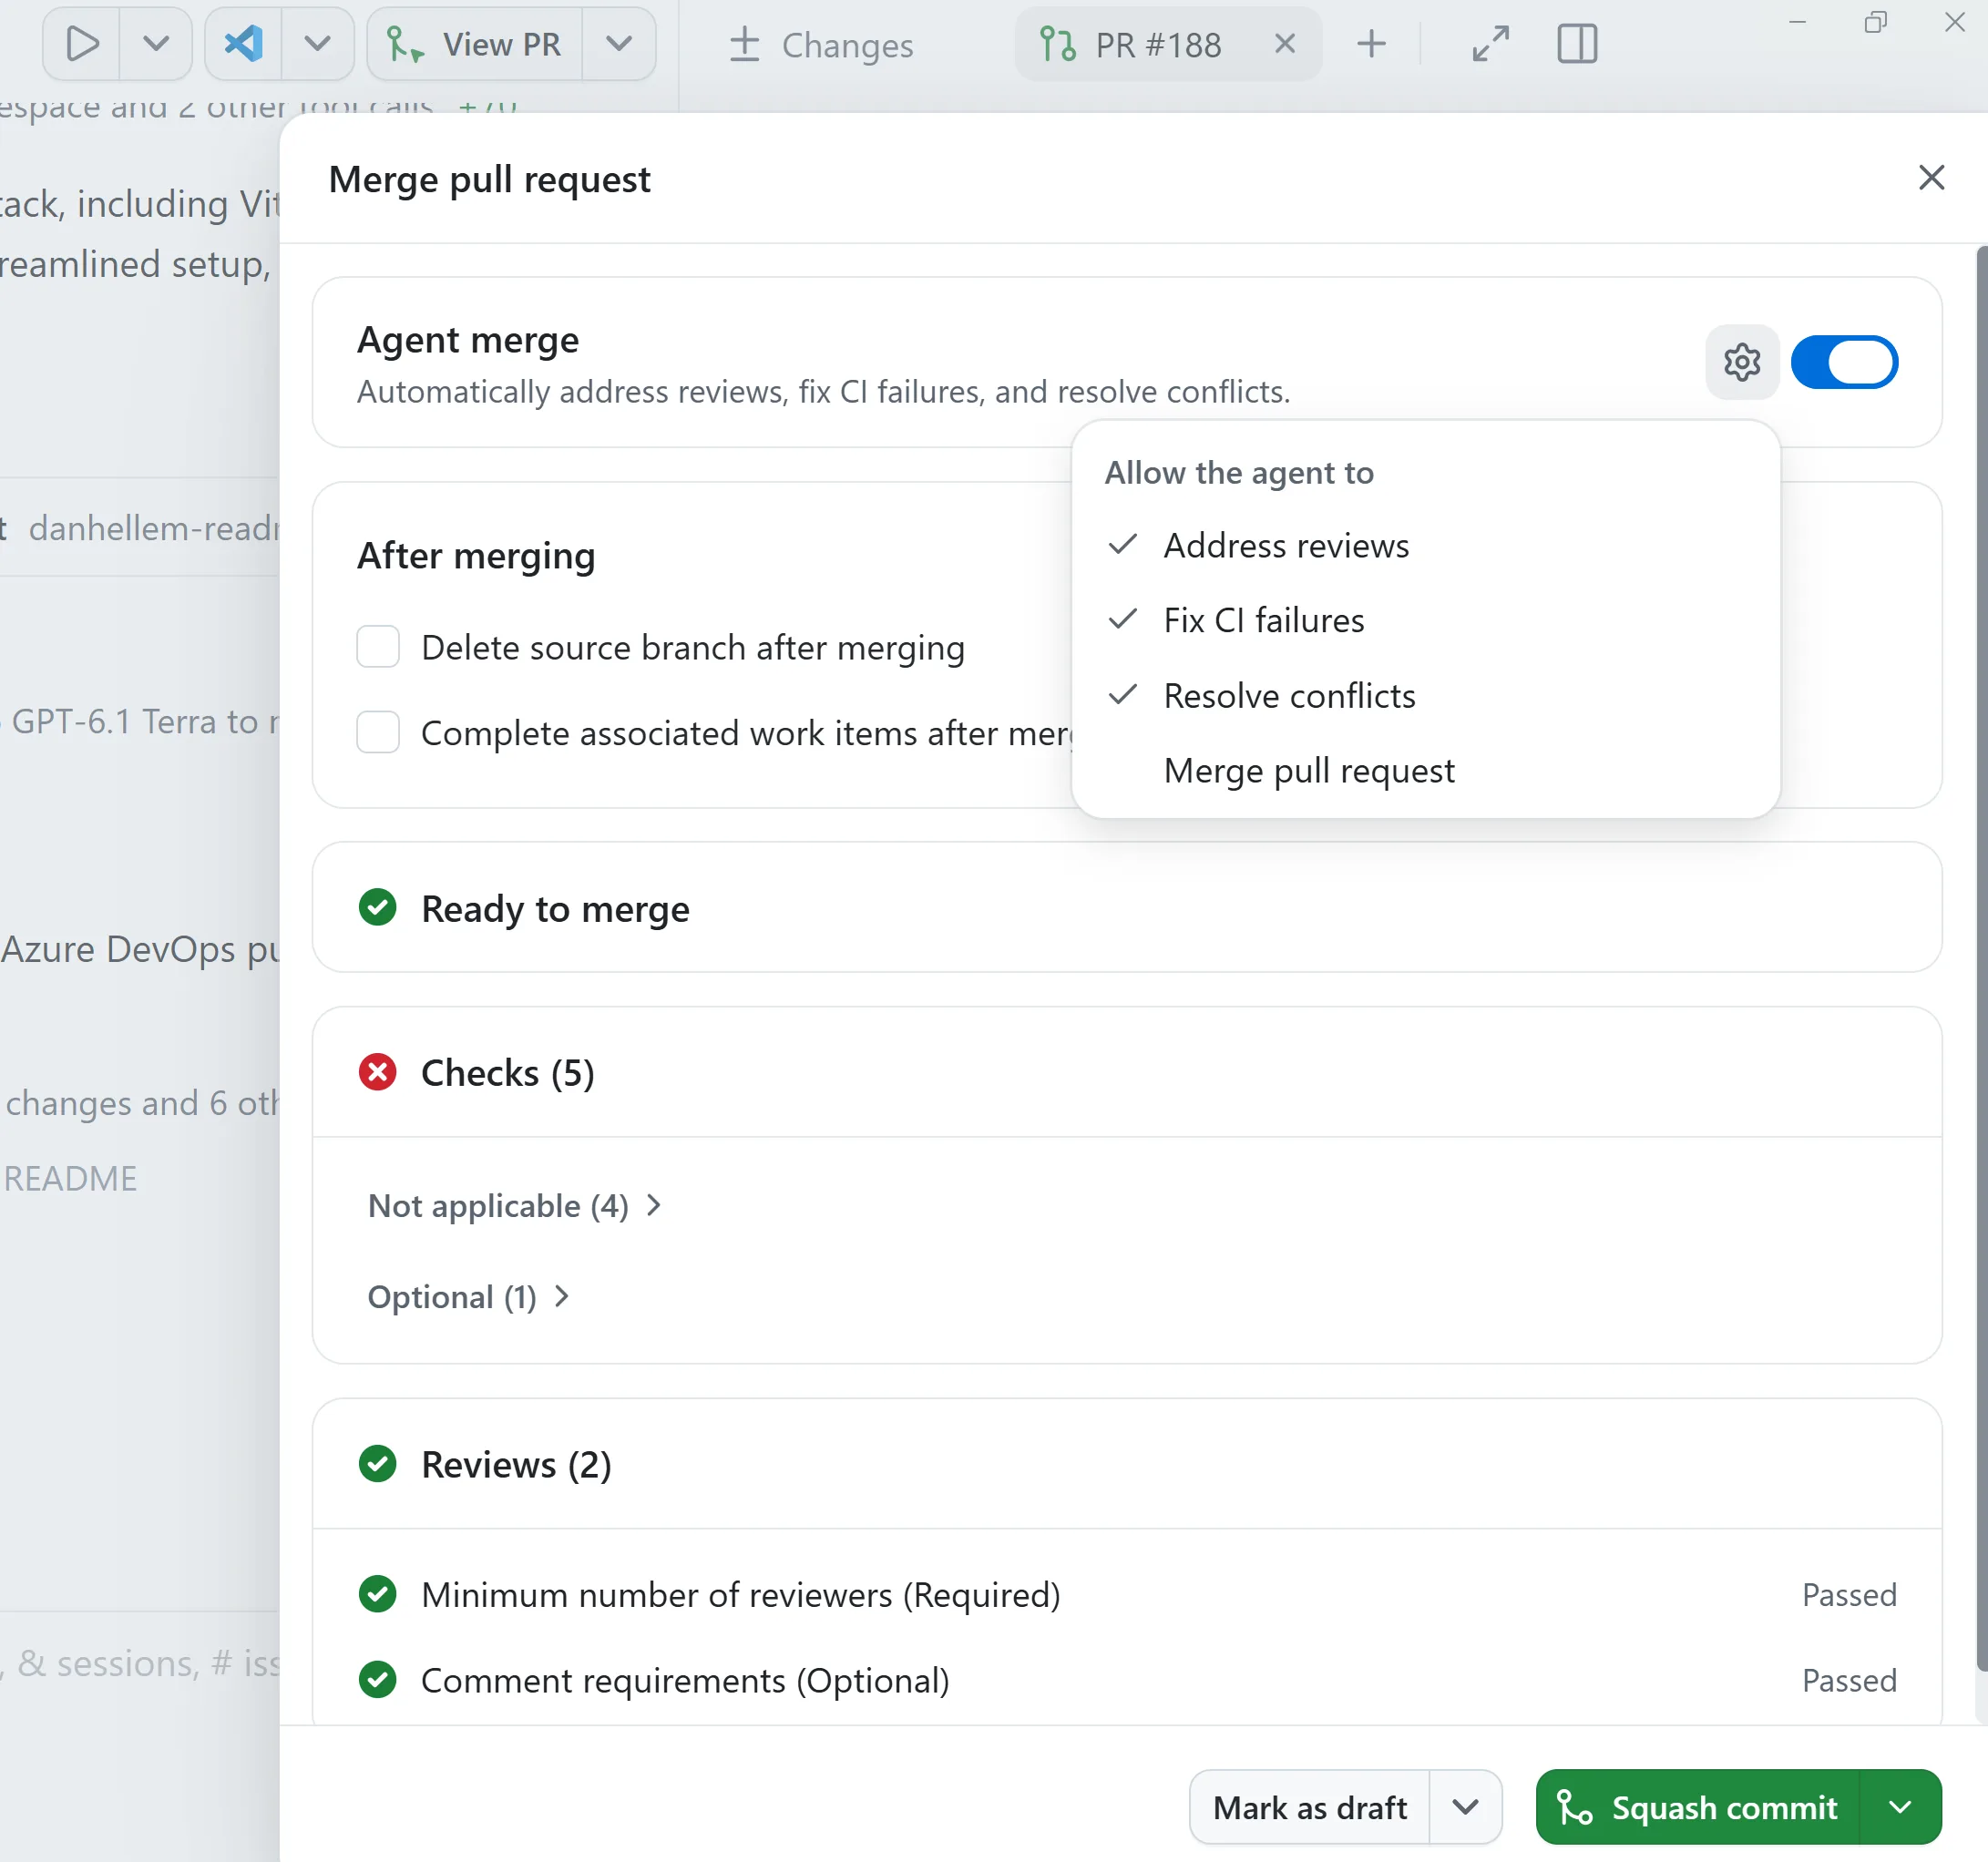
The Copilot app also provides a place to review code, add comments, and manage pull requests. With Agent Merge, agents can monitor pull requests, address review comments, resolve CI issues, and automatically merge changes when they’re ready.

Enable Azure DevOps integration

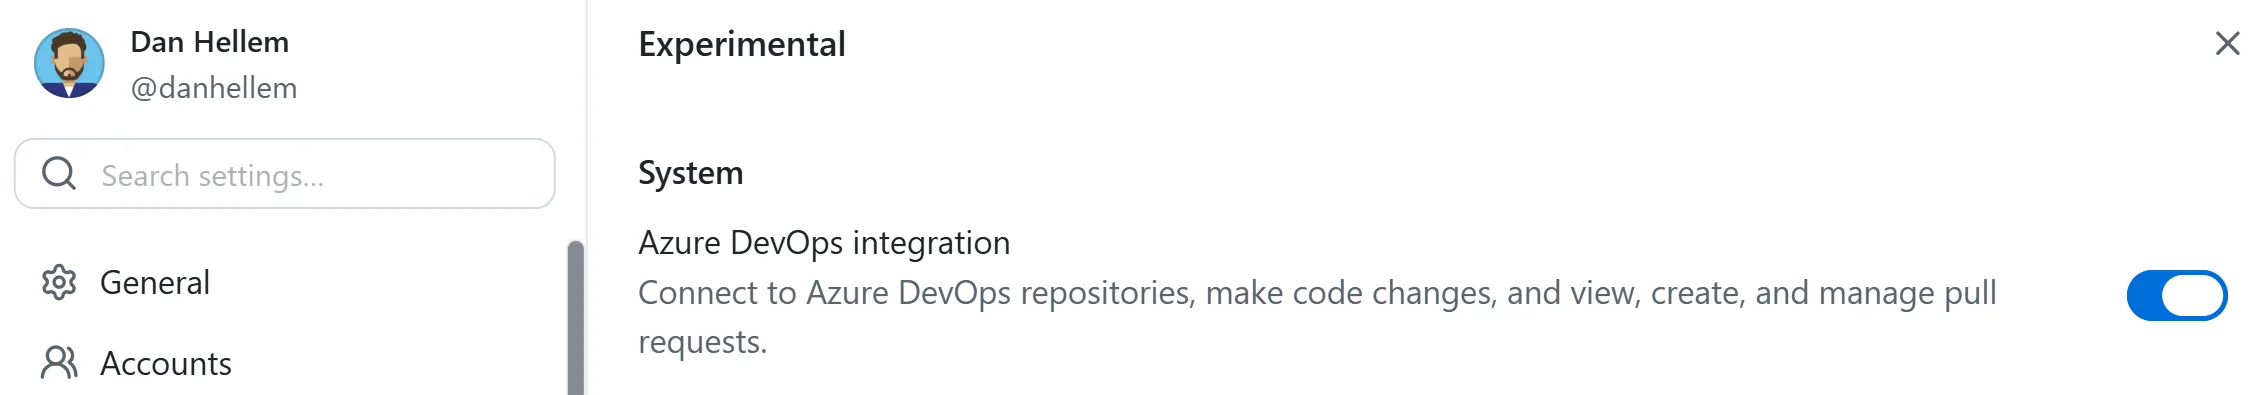
To enable the Azure DevOps integration, go to Settings > Experimental, and look for Azure DevOps integration, and enable the integration.

enable azure devops

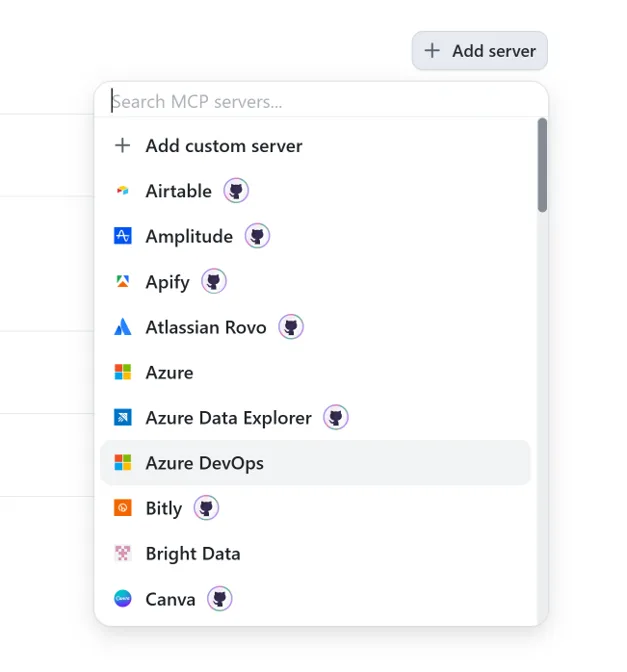
We also recommend enabling the Azure DevOps Remote MCP Server. To set it up, go to Customize > Installed, select Add server, and choose Azure DevOps. You can optionally enter your Azure DevOps organization name.

Add Azure DevOps Remote MCP Server

Getting started

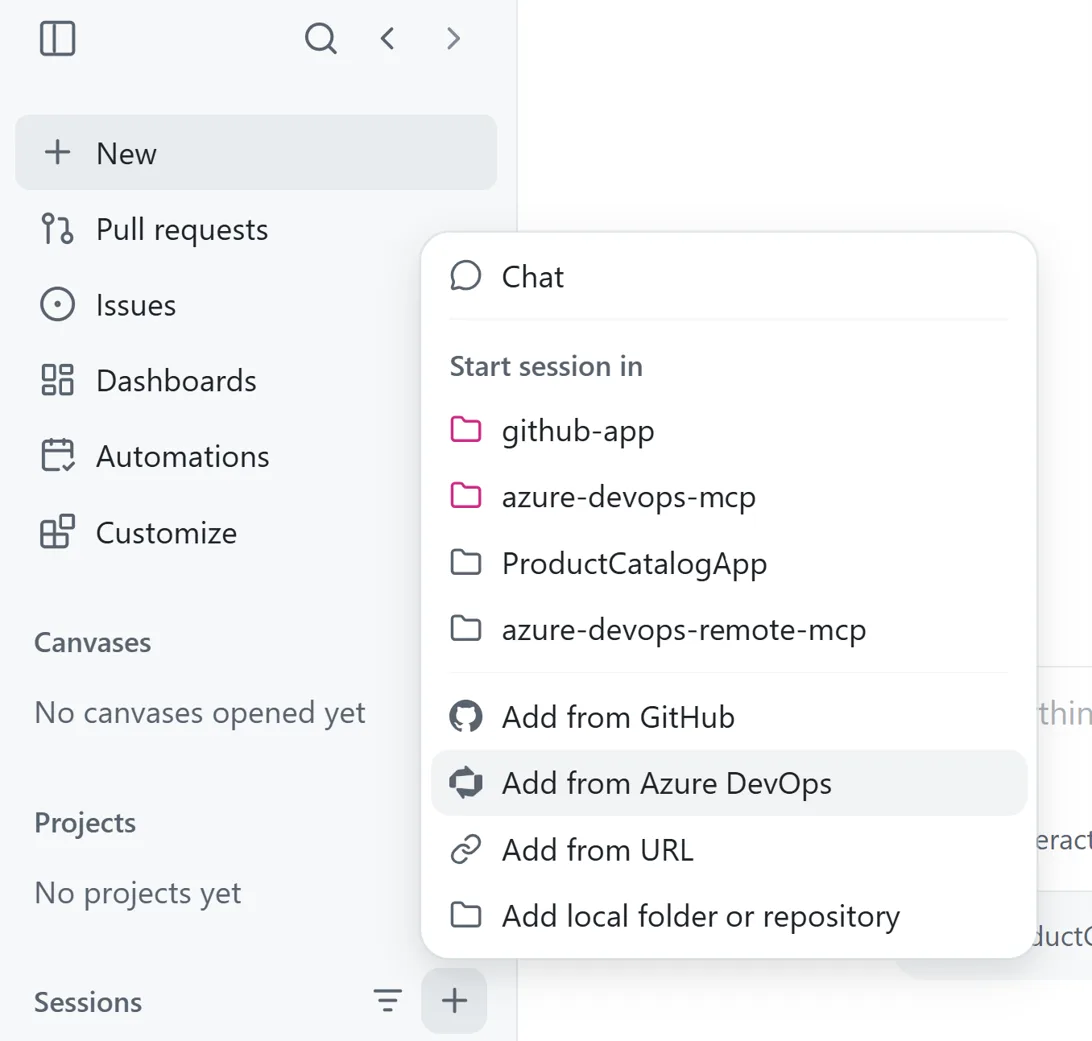
To get started, create a new session, select Add from Azure DevOps, and choose the repository you want to work with.

Select an Azure DevOps repository in the Copilot app

Once connected, you can ask Copilot questions about your repository or give an agent a coding task.

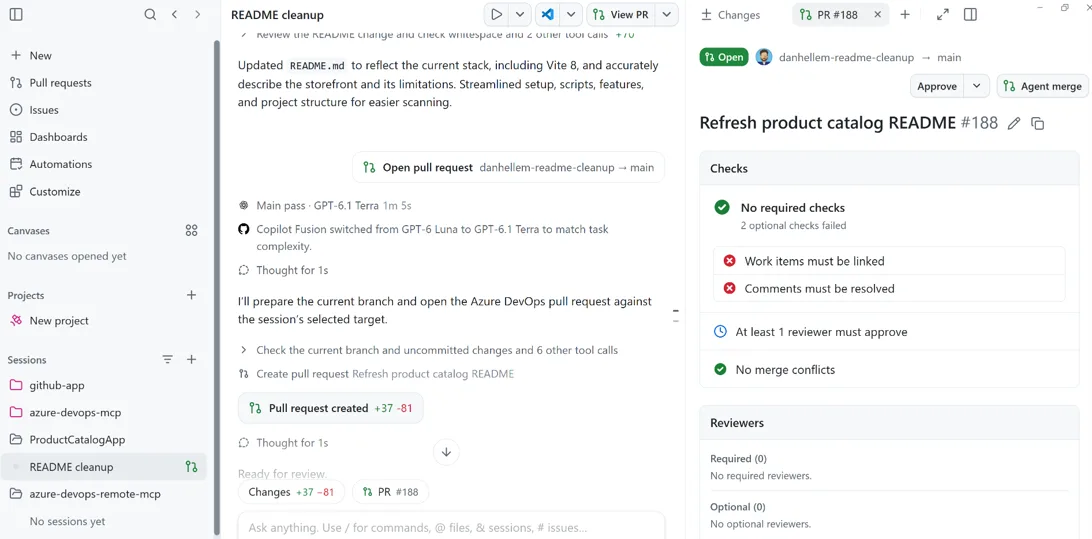
After the agent completes its work, you can review the changes and manage the pull request directly in the Copilot app.

Review pull request changes in the Copilot app

You can also enable Agent Merge on a pull request to monitor its progress, address review comments, resolve CI issues, and merge it when everything is ready.

Manage pull requests with Agent Merge

What’s next

This is an important step forward for teams using Azure DevOps who want to take advantage of GitHub Copilot. Throughout the public preview, we’ll continue to address existing gaps and expand support for Azure DevOps. Planned improvements include the ability to view and open work items, start coding sessions directly from work items, and Projects support.

We encourage you to try out the integration and share your feedback. If you encounter issues or have suggestions, please let us know by opening an issue in the Copilot app GitHub repository.

The post Azure DevOps integration with the GitHub Copilot app (public preview) appeared first on Azure DevOps Blog.

Read the whole story
alvinashcraft
41 seconds ago
reply
Pennsylvania, USA
Share this story
Delete

v2026.11.6

1 Share

OpenClaw 2026.11.6

Read the whole story
alvinashcraft
55 seconds ago
reply
Pennsylvania, USA
Share this story
Delete

Token fraud is here and it’s BAD (YouTube)

1 Share

Token fraud is here and it’s BAD (YouTube)

Claire Vo runs ChatPRD, an AI platform that helps product managers "turn an idea into a spec". The product has been live since the GPT-4 era, and Claire has been building it in public for much of that time.

In this YouTube video (see also the accompanying Twitter post) Claire describes the flood of token fraud she has seen from groups abusing the product's free trial, sometimes just to get free AI usage but often to resell tokens or run other commercial enterprises on top of the ChatPRD agent.

I am funding a international Roblox and Fortnite map studio. They run a loop of free trials and promo codes and then tunnel to my agent and use it to build Roblox and Fortnite maps.

Apparently one of the common prompts Claire saw running through her agent involved SVGs of pelicans riding bicycles! Presumably the token scammers are using that to help sniff the underlying models - different model families have a definite signature, and I've used it like this in the past to try and guess the identity of stealth preview models on platforms like OpenRouter.

Claire is winding down her free trials entirely, which sadly looks like the right decision in the face of this abuse.

Tags: youtube, ai, generative-ai, llms, pelican-riding-a-bicycle, ai-misuse

Read the whole story
alvinashcraft
1 minute ago
reply
Pennsylvania, USA
Share this story
Delete

PostgreSQL 19 Released

1 Share

PostgreSQL 19 Released

Most years PostgreSQL ships a new release in September, but this year's release came two months later thanks mainly to the flurry of issues that the PostgreSQL team needed to address as part of the ongoing AI-reported vulnerability apocalypse.

This release was definitely worth the wait. My favorite new feature is this one:

For applications that send reads to standbys, PostgreSQL 19 adds "read-your-writes" consistency with the new WAIT FOR LSN command. A session on a standby can use WAIT FOR LSN to wait until the standby has replayed the write-ahead log (WAL) up to a specific log sequence number (LSN) before running a query, so the application can read data it just wrote on the primary.

In practice, that looks like this:

UPDATE movie SET genre = 'Dramatic' WHERE genre = 'Drama';
SELECT pg_current_wal_insert_lsn();

That returns a value like 0/0306EE20. Store that somewhere (a signed cookie would work) such that on a subsequent request your application can do:

WAIT FOR LSN '0/0306EE20' WITH (TIMEOUT '0.1s');
SELECT * FROM movie WHERE genre = 'Drama';

The timeout is optional - if you provide one you'll get an error if the replica you are talking to doesn't catch up within the specified time.

I first encountered this pattern in Wikipedia, which has a hand-rolled version of this built against MySQL replication:

In addition to this, MediaWiki attempts to ensure that the user sees events occurring on the wiki in chronological order. A few seconds of lag can be tolerated, as long as the user sees a consistent picture from subsequent requests. This is done by saving the primary binlog position in the session, and then at the start of each request, waiting for the replica to catch up to that position before doing any reads from it.

Here's the relevant MediaWiki code, which these days uses MySQL's WAIT_FOR_EXECUTED_GTID_SET() function and falls back to SOURCE_POS_WAIT().

Via Lobste.rs

Tags: mysql, postgresql, replication, scaling, wikipedia, ai-security-research

Read the whole story
alvinashcraft
1 minute ago
reply
Pennsylvania, USA
Share this story
Delete

Build trusted autonomous agents for your team with Microsoft Foundry

1 Share

A new kind of agent can work alongside your team in Microsoft 365, with its own identity, permissions, and a manager accountable for its work.  

Enterprises are all-in on AI agents, but the ROI hasn’t followed. What’s holding those agents back isn’t capability. Today’s agents can do remarkable work on their own. They can start on a bug as soon as it’s assigned, turn a finished design into a working app, learn a task by watching you do it once, and spend the night researching and testing ideas so results are waiting by morning. 

The gap shows up when you ask one of those agents to work with your team. Today, unless an agent has an account of its own, the only way it can work in Outlook or Teams is with your permissions. That works for a personal assistant, but it breaks down in two common scenarios: 

  • No user is signed in. An agent triggered by an event has no signed-in user to act for, so it either can’t take Microsoft 365 actions at all or has to hold on to someone’s credentials to do it. 
  • Group settings. In a group chat, the agent must guess on whose behalf to act, and there’s no right answer. Whoever it picks, that person’s permissions apply to the whole thread: actions get attributed to someone who didn’t ask, and members can see content they don’t have access to. 

So most agents stay single-player: one user, one agent, one private conversation. But enterprise work rarely happens alone. Shipping a feature, launching a campaign, closing a deal, or leading a workstream happens across teams, meetings, documents, channels, SharePoint sites, and group chats. Agents won’t deliver business value until they can work there, safely.

A trusted member of your team

Foundry now lets you build agents that bring that autonomy to the enterprise. Each one works under its own identity as a named member of your organization, in a standing role rather than performing one request at a time. 

You may have seen Autopilot in Microsoft 365 Copilot. These agents are the same type: Autopilot comes out of the box, and in Foundry you build your own.

What makes them trustworthy is identity and the governance controls that come with it. Identity is what makes any actor in an enterprise governable, because every action traces back to it. It’s how an organization answers three questions: who took this action, were they authorized to, and can we prove it afterward? An agent you build in Foundry is a member of your organization in the ways that count:

  • Its own identity. It acts as itself and never borrows anyone’s credentials. Every Foundry agent has a Microsoft Entra agent identity, and these agents also have an Entra agent user account that lets them perform Microsoft 365 actions as themselves.
  • Its own access. You grant it permissions the same way you would a person.
  • Its own manager and place in the org. It has an accountable manager, and its spot in the org chart shows everyone who that is. It also has its own email, calendar, OneDrive, and Teams presence, like any colleague.
  • Its own audit trail. Every action is attributed to the agent, not to whoever happened to be in the conversation.

Build it once, hire it across your organization  

You don’t build this kind of agent directly. You build an agent-as-a-service: a blueprint that people then use to create their own instances. The blueprint is a template that defines what the agent can do, such as the APIs it can call and the MCP tools it can access. You write custom code to shape that behavior, like when it responds, and deploy it as a Foundry hosted agent. Once the published blueprint is approved by an admin, your entire organization benefits: each approved person in your org hires their own instance, with its own identity, agent user account, and access to their resources.

Capability and access are separate

A blueprint never grants access to any specific team’s business resources. Say I build a release captain tailored to my company’s release process. It knows how to update Azure DevOps work items and write to SharePoint, but each manager decides which Azure DevOps project and which SharePoint site their instance can reach.

without with blueprints light v2 image The benefits of build, the simplicity of buy 

Foundry gives you the benefits of building an agent with the simplicity of buying one. 

The benefits of building one 

  • Built for your process. You build a blueprint specific to your company’s business processes.
  • You own your IP. Every time your agents work, they create intelligence. The business process your blueprint encodes and the learning loop it builds are both yours.
  • Complete control and visibility under the hood. These agents act on their own across your organization, so you get granular control of how they behave, down to whether one responds to a given message. 

The simplicity of buying one 

Once your blueprint is approved, your whole company can use it as easily as software you bought. It’s hired, governed, and managed exactly like employees, through the same Entra and Agent 365 controls your admins already use. 

foundry build buy light v2 imageBuilt on enterprise primitives, extended for what’s different 

What it reuses. Everything above runs on primitives enterprises already manage: Entra for identity, the access controls your admins already use, the places your people already work, and Agent 365 for governance.  

What it adds. There’s an important catch. Just because an agent can operate like a user doesn’t mean it has the same incentives, judgment, or failure modes. We gave it a user identity so we could govern it like an employee, not because it is one. 

It has no stakes of its own, so the consequences that shape how people behave don’t shape it, and accountability has to sit with the people around it. It doesn’t notice when it’s past what it knows, so it keeps going, confidently, where a person would stop and ask. And where a thousand employees make a thousand different mistakes that partly cancel out, a thousand copies of one autopilot share the same blind spots and fail together. 

That’s why we’ve built controls people never needed. Every one of these agents is an instance of a blueprint, so one kill switch can disable an entire class of agents in one action, and Agent 365 gives you a full control plane for managing your fleet.

Reusing what we have is what lets this scale. Extending it for what’s different is what makes it safe.

This is happening now 

Organizations already have these agents in production today. We have seen Autopilots fall into three types, which differ in who they serve.

  • Personal: works for one person, as an isolated instance created and used by that person only.
  • Team: works for a team. It lives where the team works, holds context the whole team shares, and coordinates across people instead of serving one at a time.
  • Organization-wide: provides a centrally managed capability available to everyone in the organization, typically as one production instance per business process.

Nous Research 

The Hermes Agent is getting a new capability powered by Microsoft Foundry: it can now work as an AI coworker with its own Microsoft 365 account, managed like any other member of your staff.  

Nous Research knows the hard part of bringing agents into an organization today is doing it securely, in a way admins trust. So the idea is simple: each Hermes agent gets its own work account, complete with email, a cloud drive, a calendar, a chat profile, and a manager, and joins the company much as a new hire would. IT governs it with the tools it already uses for staff, and employees work with it as they would any colleague, by sending it a message or sharing a folder. With nothing new to build or learn, adoption takes care of itself. 

Companies will soon be able to get Hermes two ways: Hermes Business or Hermes Enterprise. Hermes Business is a SaaS agent that Nous hosts, and Hermes Enterprise is self-hosted in the company’s own Azure tenant as Foundry hosted agents, with a control plane that governs them. Both give every member of a team a self-improving agent, and the skills one agent learns are shared with everyone else’s. To self-host today, you can get started with Nous’s open-source cookbook on GitHub.

“Hermes Enterprise is the agent platform a company can fully own: it writes its own skills as people work, so the know-how compounds inside your tenant. Hosted agents on Microsoft Foundry give that agent its own identity and a place to run around the clock while giving you the freedom to use any model provider.”

Jeffrey Quesnelle, Co-Founder & CTO, Nous Research

Microsoft  

An auto-approval path for any Microsoft employee. Because it runs on infrastructure we already trust, any Microsoft employee can build their own agent like this and deploy it inside Microsoft today. If it stays within the bounds we developed with Microsoft IT, it’s approved automatically: no reviews, no waiting. 

Meet Office of Amanda, my AI chief of staff, running in production at Microsoft. It takes the follow-ups and coordination off my plate so I can spend my time on the work that needs me. It acts for me, not as me. I give it access to my calendar and mailbox the same way I would a human assistant: through the Exchange delegation permissions that already exist. I can add it to security groups and Microsoft 365 groups, assign it access packages, and share documents with it. When it sends an email, it sends it as itself, under its own identity, with its own audit trail.

Office of Amanda is one of more than 30 blueprints Microsoft employees have already built on Foundry.officeofamandaorgchart image

What comes next 

Giving agents their own identity gets them out of single-player mode and into the places enterprise work actually happens. That’s the first step.

Now we’re also rethinking the work itself. What should agents take on? Where should human judgment stay? And how do humans and agents work as one team? Nobody has the answer yet, but we’re building to find out, and we want you building with us.

Get Started

The post Build trusted autonomous agents for your team with Microsoft Foundry appeared first on Microsoft Foundry Blog.

Read the whole story
alvinashcraft
1 minute ago
reply
Pennsylvania, USA
Share this story
Delete
Next Page of Stories