Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
161225 stories
·
33 followers

Gemini Live audio

1 Share

Tool: Gemini Live audio

Google released Gemini 3.8 Live and 3.8 Live Extended Thinking today - two new speech-to-speech models that are a similar shape to OpenAI's GPT-Live family.

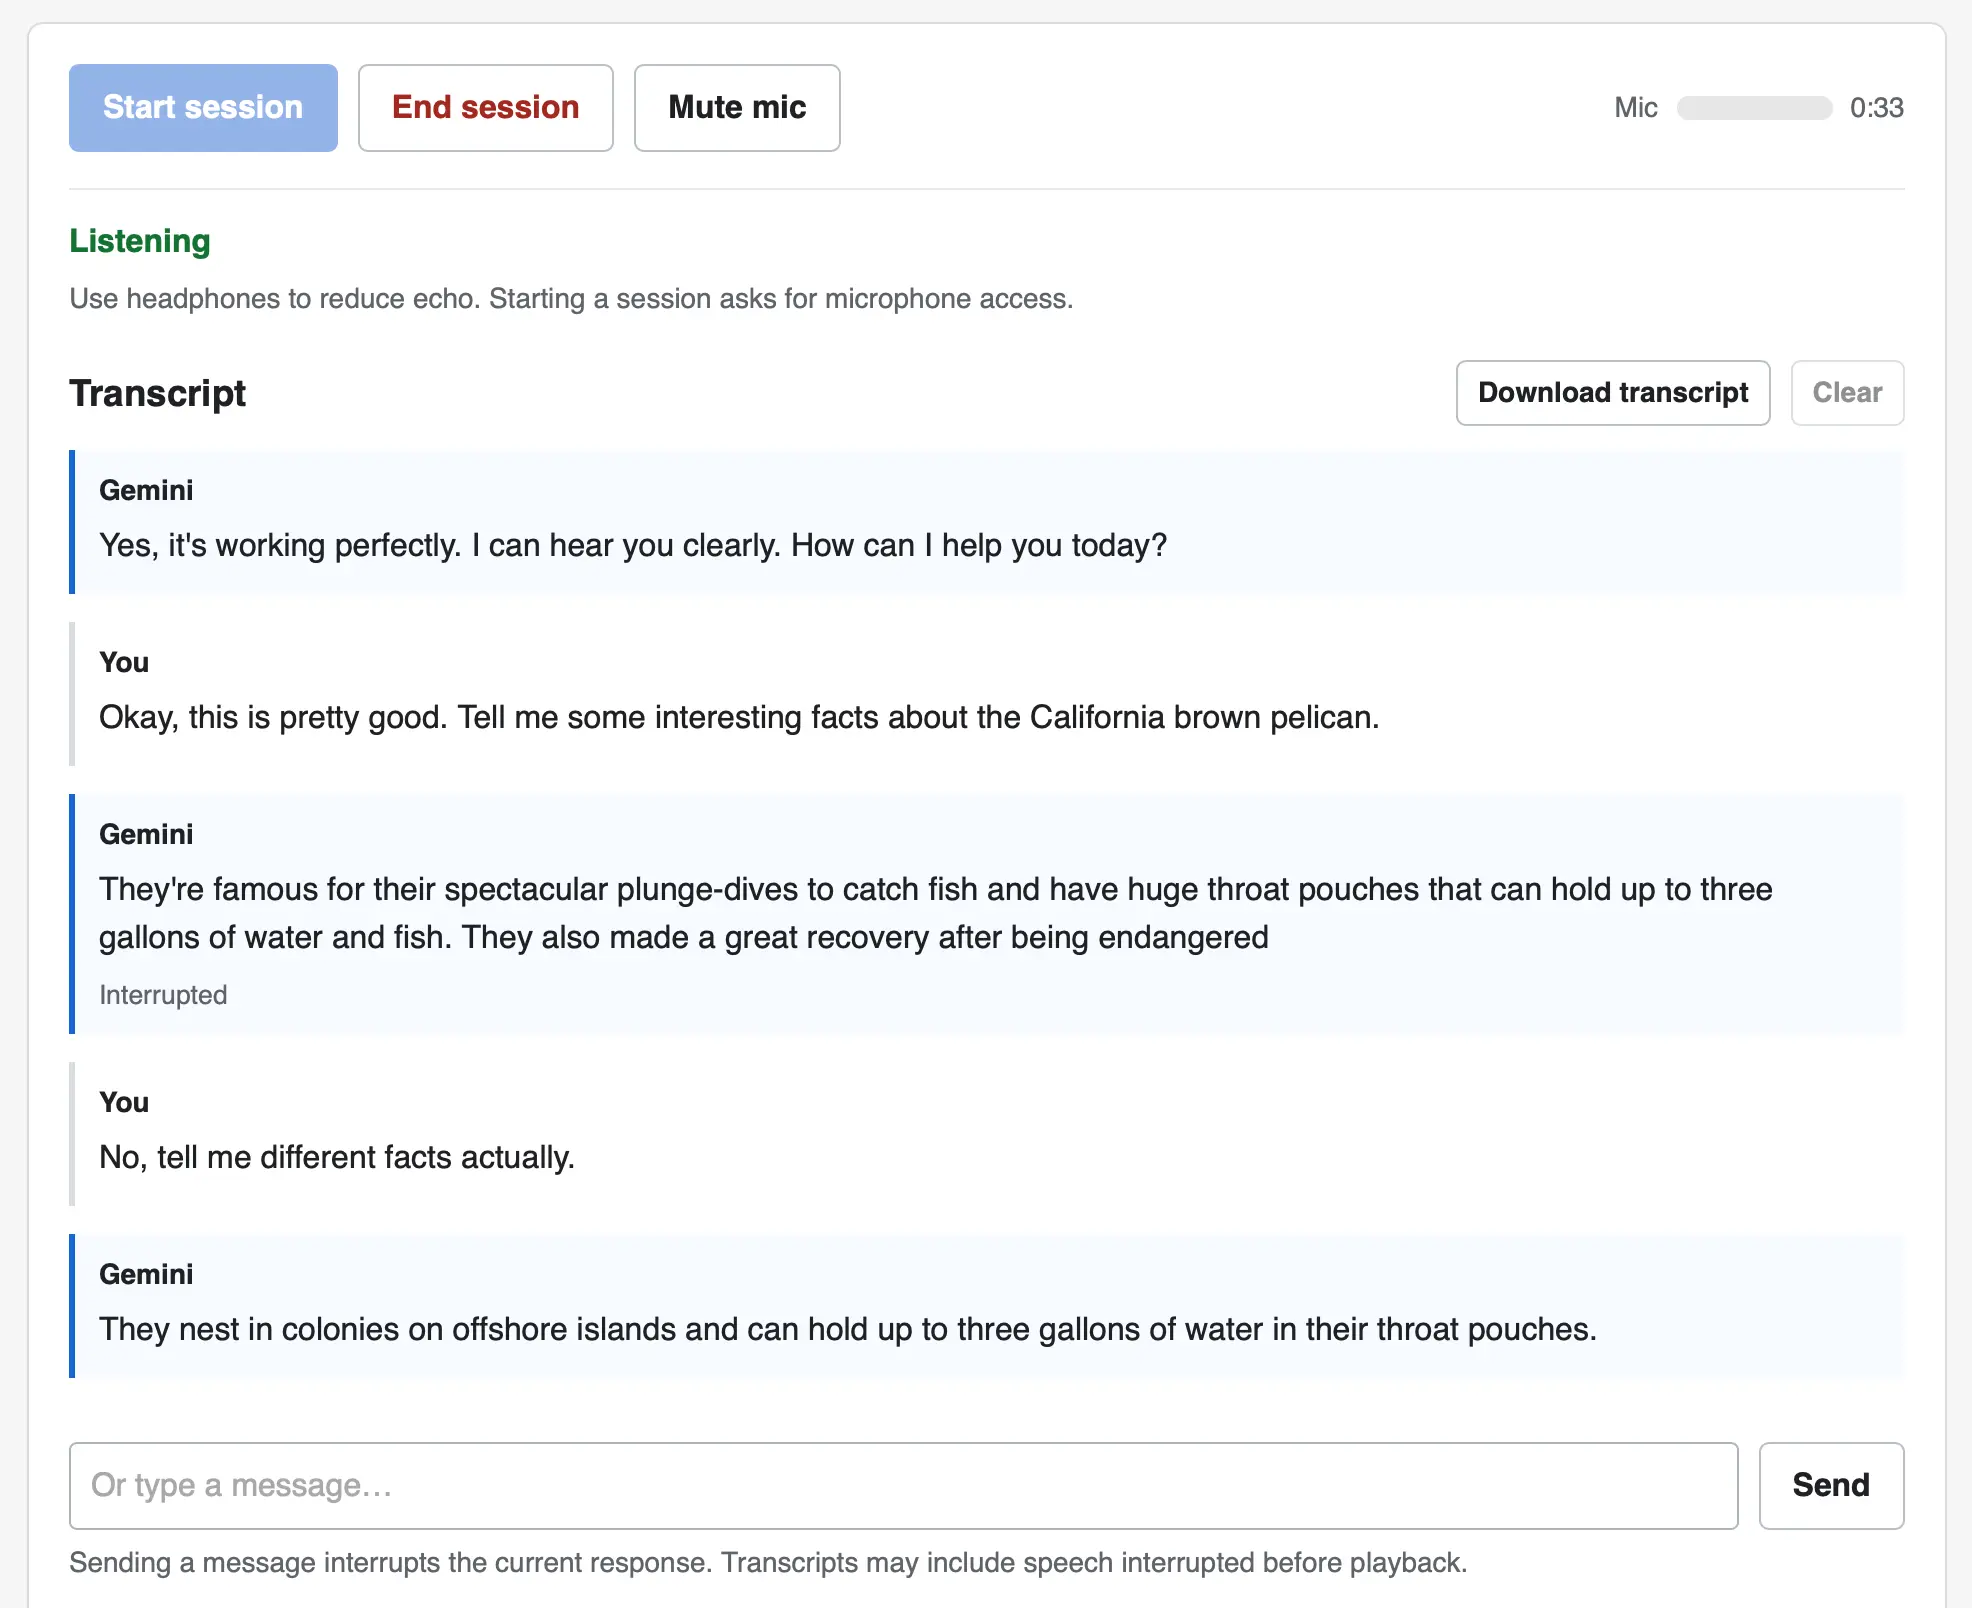
I pointed GPT-6 Astra Extra High at the documentation and had it build me this web UI for trying out the new models. You can select a model and voice preset, enter an optional system prompt and then start a voice conversation through your browser, including the ability to interrupt the model while it is talking.

Screenshot of a voice chat web interface with a transcript. Top buttons: Start session, End session, Mute mic, plus a Mic level meter and a timer showing 0:33. Status: Listening. Use headphones to reduce echo. Starting a session asks for microphone access. Transcript (with Download transcript and Clear buttons). Gemini: Yes, it's working perfectly. I can hear you clearly. How can I help you today? You: Okay, this is pretty good. Tell me some interesting facts about the California brown pelican. Gemini: They're famous for their spectacular plunge-dives to catch fish and have huge throat pouches that can hold up to three gallons of water and fish. They also made a great recovery after being endangered — marked as Interrupted. You: No, tell me different facts actually. Gemini: They nest in colonies on offshore islands and can hold up to three gallons of water in their throat pouches. At the bottom is a text input reading Or type a message… with a Send button, and the note: Sending a message interrupts the current response. Transcripts may include speech interrupted before playback.

The implementation uses no libraries. It connects to the wss://generativelanguage.googleapis.com/ws/google.ai.generativelanguage.v1alpha.GenerativeService.BidiGenerateContent?key=... WebSocket endpoint and uses a Web Audio API AudioContext for both capture and playback.

Here's the Gemini Live tutorial for getting started with that WebSockets API.

Tags: google, tools, websockets, generative-ai, llms, gemini, llm-release, speech-to-text

Read the whole story
alvinashcraft
3 minutes ago
reply
Pennsylvania, USA
Share this story
Delete

Managing apps built in Copilot Studio

1 Share

Last week we announced app building in Copilot Studio and Copilot Cowork. Makers can now describe business outcomes and produce full-stack apps with built-in source control, deployment stages, and version isolation—all on Microsoft-hosted infrastructure that requires no infrastructure provisioning, hosting configuration, or deployment pipeline.

With those capabilities built in, your administrative scope is narrower and more familiar. Apps are created in the maker's personal developer environment following the environment routing policies you already have. That means things like connector permissions and data policies apply to an app both while it is being built and after it is published. Apps also access connected data on behalf of the signed-in user, which means publishing or sharing an app never grants anyone access to data they could not already reach.

With these new capabilities, there are three things that every admin should be thinking about:

  1. Review your app estate
  2. Control cost with credit caps
  3. Choose where makers can build apps

Review your app estate

Published apps are inventoried in the Microsoft 365 admin center. Each app shows:

  • Who built it
  • Its lifecycle state
  • Which data sources and connectors it uses
  • Which policies apply to it
  • Usage and operational metrics

From the same experience, you can also block or disable a published app, remove a connector, bring an app back within policy, control whether it can be shared, and retire apps that are no longer used.

Control cost with credit caps

Building and running apps are both charged through Copilot Credits usage-based billing, and are metered as two separate services. This distinction lets you manage maker cost and app runtime cost independently. Build consumption varies with the language model used, the complexity of the app, and how much iteration is involved. Runtime consumption, on the other hand, varies with the volume and complexity of the tasks the app processes.

At runtime, if the user holds a Power Apps Premium license, usage is included within existing request limits. Beyond those limits, or without a license, usage bills through Copilot Credits. You can learn more by reviewing the Copilot Credits licensing guide.

As an admin, you can define credit cap policies to manage your costs. For both maker and runtime usage, caps are set per user, and the controls are managed through usage-based billing. For makers, think of a cap as a per-user budget: you can set the same budget for everyone, or different budgets for groups of users, such as departments that carry separate budgets of their own.

Choose where makers can build apps

By default, app creation is available to all users in both Copilot Studio and Copilot Cowork. However, you may want to limit where people can build apps. To do so: In the Microsoft 365 admin center, navigate to Apps, then Overview, and find ‘Choose where people can make apps’.

Two paths appear:

  • Copilot Studio, where makers build directly, which is on by default and recommended
  • Copilot Cowork, where people create apps through chat, with availability managed by your organization's participation in the Frontier program

Note that turning a path off prevents new apps being created that way. However, apps that are already published through that path will continue to run.

Key takeaways for managing apps built in Copilot Studio

  • The Microsoft 365 admin center is the one place to review the app estate, adjust app policies, and decide which creation paths stay open.
  • Set credit caps as per-user budgets today, uniformly or by group, and plan for environment-level caps as project budgets when they arrive.
  • Decide who is accountable for overseeing published apps before makers start publishing, as you would for any other application estate.

Go to the Microsoft 365 admin center

Read the whole story
alvinashcraft
9 minutes ago
reply
Pennsylvania, USA
Share this story
Delete

Introducing Foundry Dev Pack: One Command to Start Building

1 Share

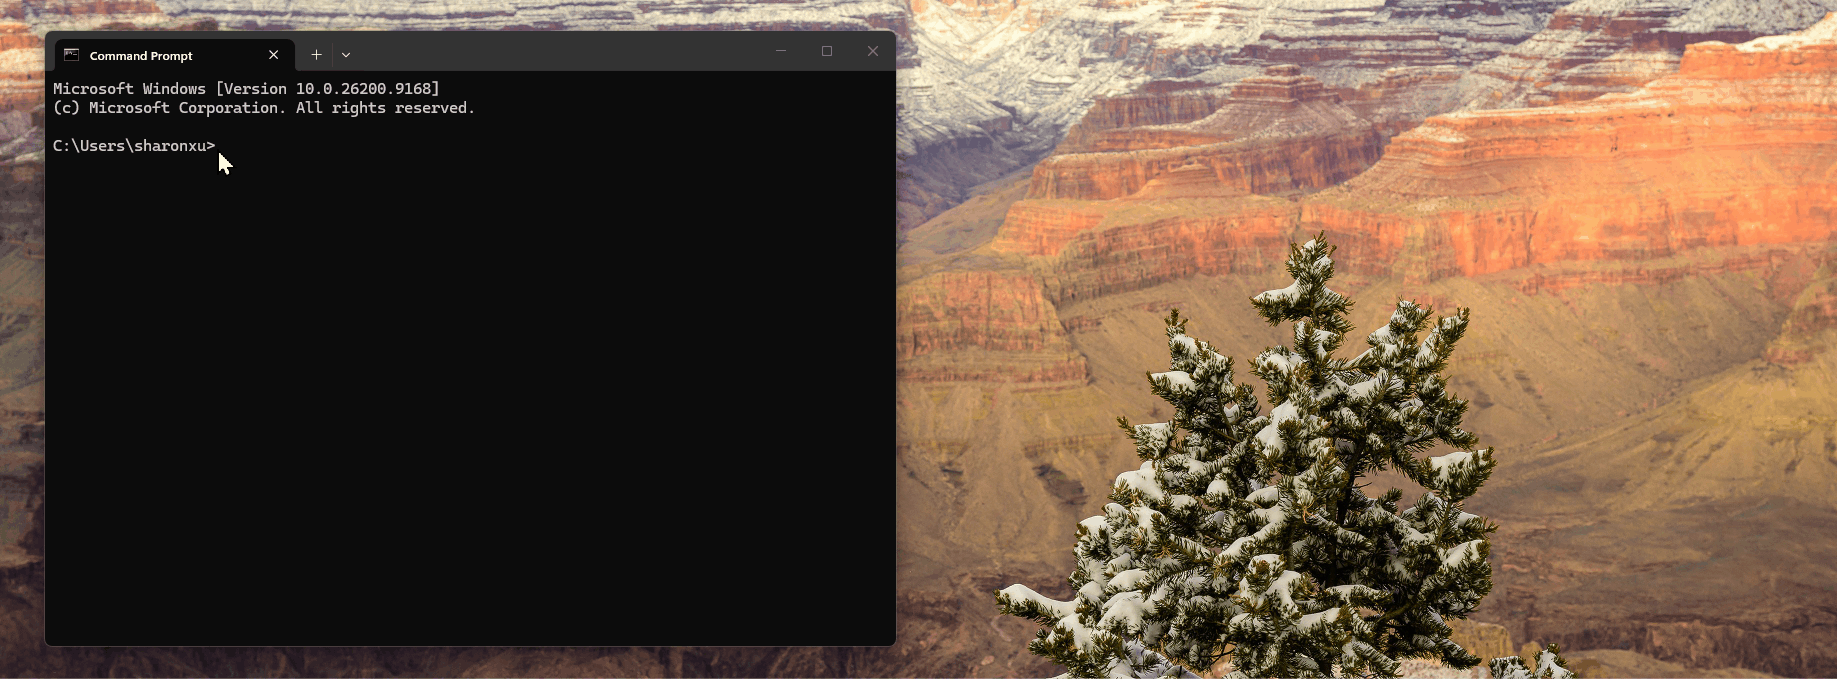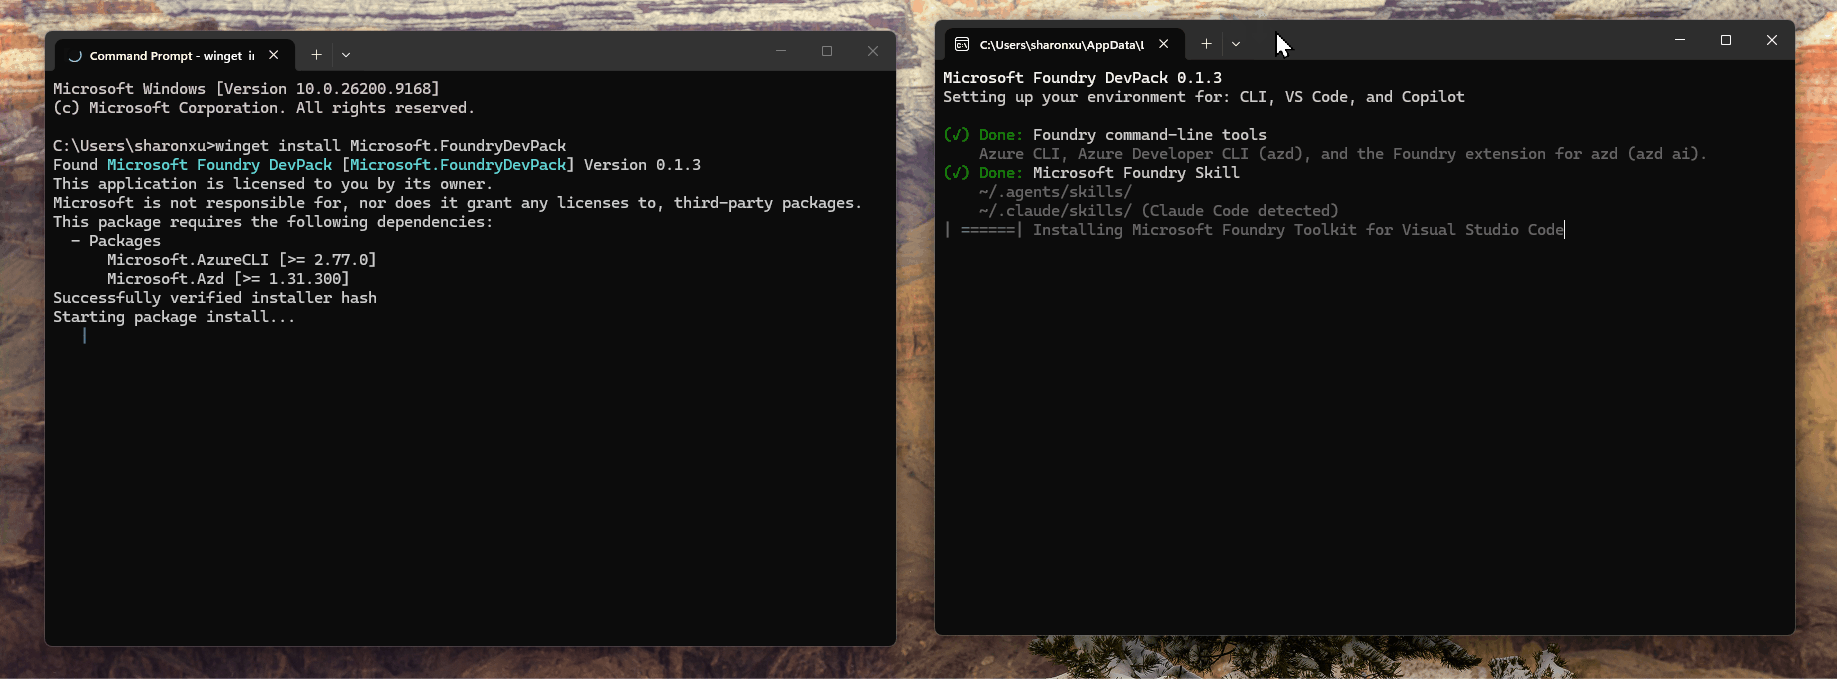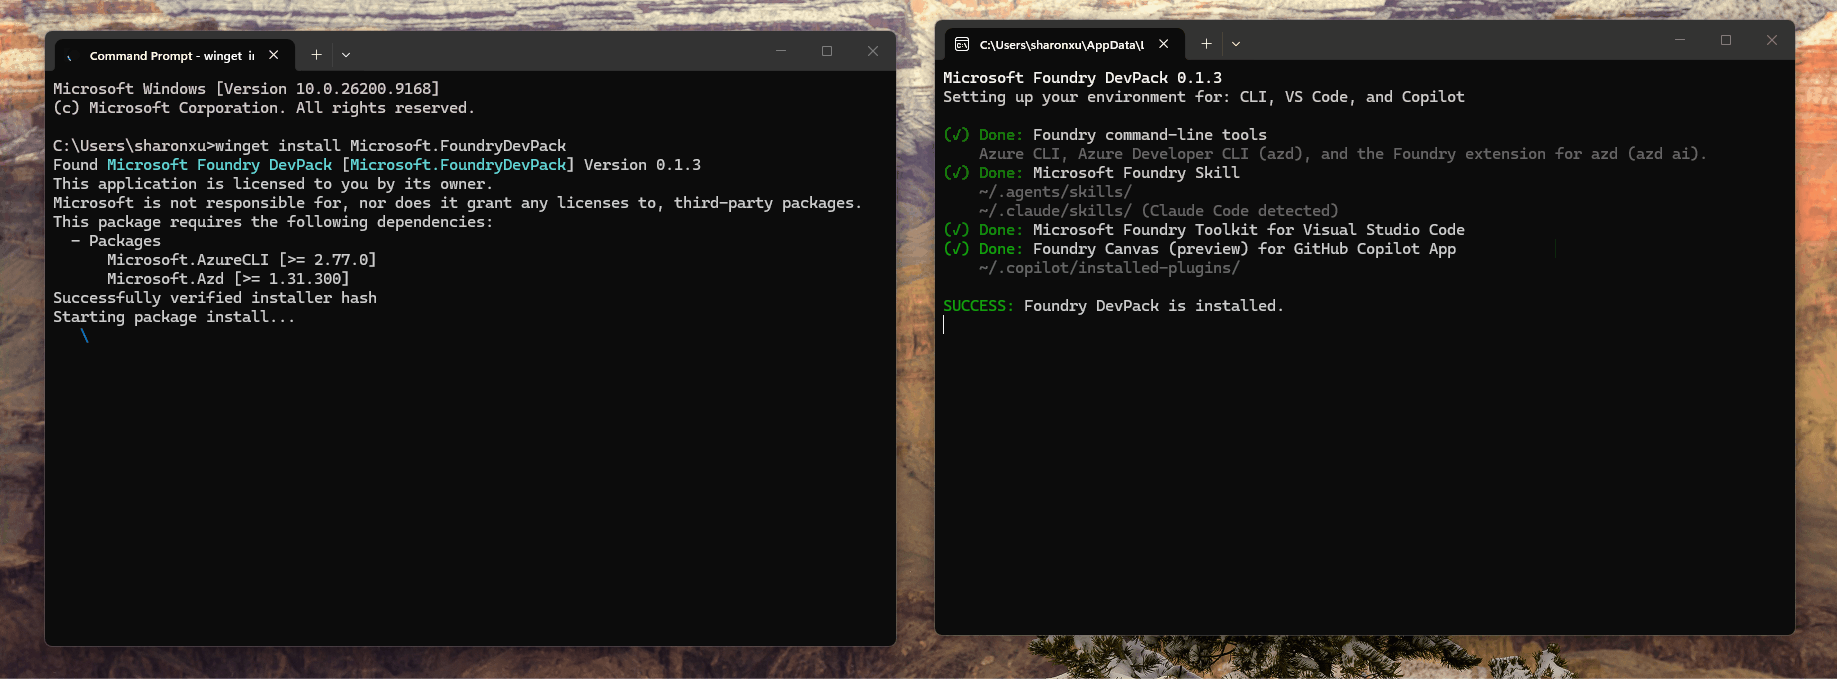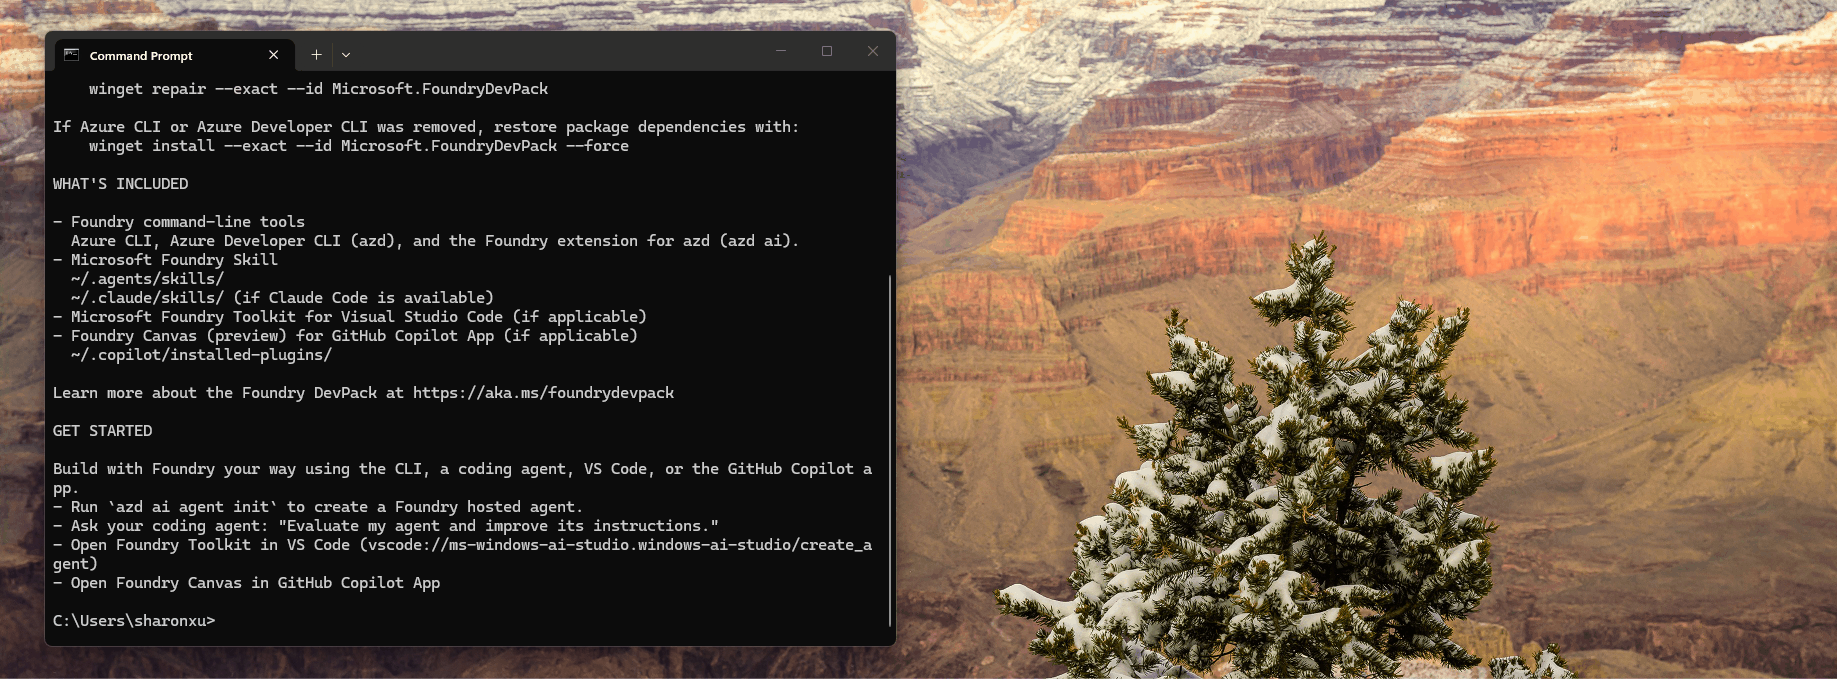
Setting up your Microsoft Foundry environment just got a lot simpler. We launched Foundry Dev Pack to consolidate initial installation steps into a single setup process.

The Foundry Dev Pack is an all-in-one installer that prepares your machine for Foundry development by installing the tools that you’ll need across your terminal, IDE, or coding agents.

Foundry Dev Pack

Depending on your environment, the Dev Pack can install:

  • Foundry Command Line Tools

Scaffold, deploy, evaluate, and automate from the terminal. Includes Azure CLI (az), Azure Developer CLI (azd) and the Microsoft Foundry Extension for azd.

Give coding agents reusable guidance for Foundry workflows.

Build, test, evaluate, and deploy from the VS Code editor. Installed only if VS Code is present.

Design and deploy hosted agents from a guided canvas. Installed only if GitHub Copilot App is present.

Whether you prefer the terminal, VS Code, or a coding agent, Foundry Dev Pack supports them all and gives you one place to start building. For more details, see our docs.

Get Started

Install Foundry Dev Pack using the command for your operating system:

Windows

winget install Microsoft.FoundryDevPack

macOS

brew install --cask microsoft/foundry/devpack && foundry-devpack install

Linux

curl -fsSL https://aka.ms/foundry-devpack-install.sh | bash

Build an Agent

To begin building your first agent, follow this quickstart, or choose one of the following tools:

  • CLI

Run azd ai agent init to create your first agent from a template.

  • VS Code

Look for the Foundry extension in the left Activity Bar to explore templates or create a custom agent.

  • Coding Agent

Leverage the Foundry skill by asking your coding agent:

Create my Foundry hosted agent end to end.

Welcome to a simpler way to develop with Microsoft Foundry!

The post Introducing Foundry Dev Pack: One Command to Start Building appeared first on Microsoft Foundry Blog.

Read the whole story
alvinashcraft
10 minutes ago
reply
Pennsylvania, USA
Share this story
Delete

Adopting the software factory model: crawl, walk, run

1 Share
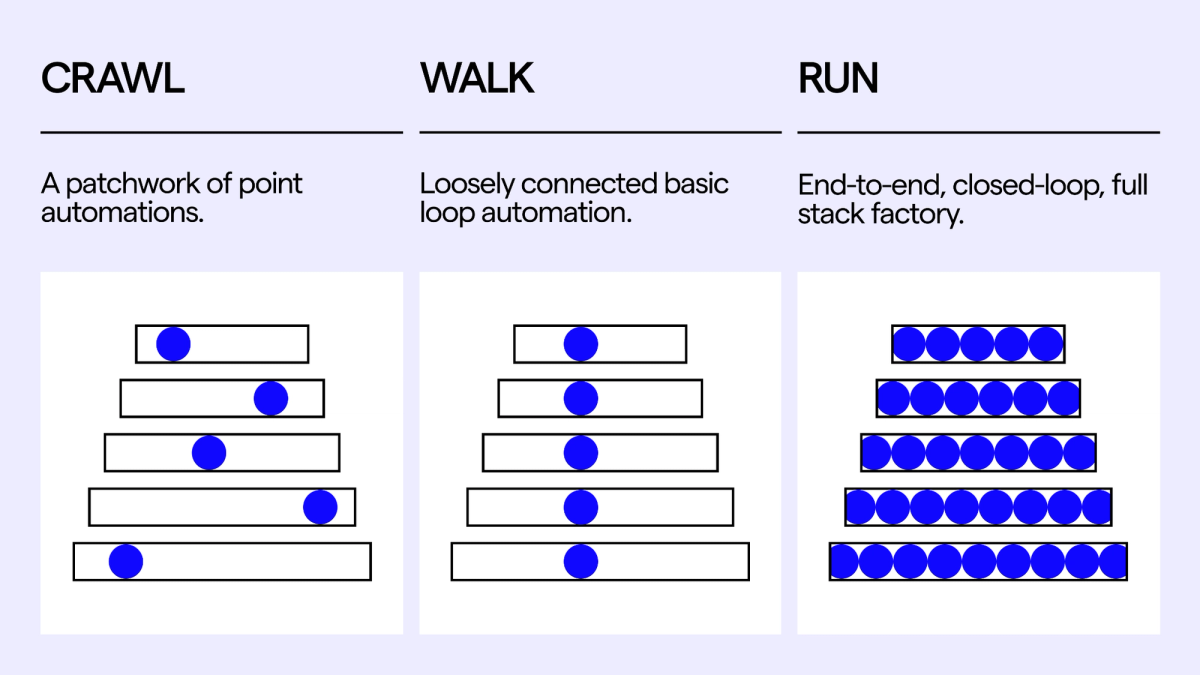
A crawl, walk, run path for adopting the software factory model: start with point automations, stand up an end-to-end cloud development loop, then scale to a closed-loop factory stack.

Read the whole story
alvinashcraft
10 minutes ago
reply
Pennsylvania, USA
Share this story
Delete

MCP for Project Management: Give Your Project Manager Superpowers

1 Share

Your development team is two weeks away from a major release.

There are hundreds of tickets in the backlog. A few high priority issues have not been updated. One critical task still does not have an owner. And someone just asked you for a status update.

Sound familiar?

The frustrating part is that the answers are probably already there. They are just scattered across tickets, comments, commits, repositories, reviews, and conversations. So you start digging.

This is where I think MCP for project management gets genuinely interesting. Not because we need an AI project manager. We do not. But give AI the right project context, and suddenly it can become a pretty useful sidekick. And that is where MCP comes in.

In Short

MCP can give AI controlled access to the context behind a software project, including tickets, milestones, development activity, and more. Instead of simply generating content, AI can help project managers find what matters, spot things that need attention, and spend less time chasing information.

Think of it less as replacing your project manager and more as giving them a new set of superpowers.

How Does MCP for Project Management Work?

MCP, or Model Context Protocol, provides a standardized way for AI applications to connect with external tools and data. That sounds technical. The practical version is much simpler.

An AI assistant normally knows what you tell it. Connect it to your project environment through MCP, with the appropriate permissions, and it can potentially understand things like tickets, priorities, assignments, milestones, comments, and development activity.

That changes the conversation. Without project context, you can ask AI:

“Write me a project status report.”

With project context, you can ask:

“What should I be worried about before Friday?”

That second question is much more interesting.

Superpower #1: Finding Things Without the Treasure Hunt

Project managers spend a lot of time just finding information. What is blocking the release? Which high priority tickets have not moved? What still needs an owner? What changed since yesterday?

Answering those questions can mean bouncing between screens, checking tickets, reading comments, messaging developers, and piecing everything together yourself. With MCP, an AI assistant could potentially do much of that first pass for you.

You might ask:

“Show me high priority work in this milestone that has not been updated recently and flag anything without an owner.”

You still decide what matters. You just do not have to spend half an hour finding it first. That is a superpower I would happily take.

Superpower #2: Seeing Trouble Before It Becomes a Fire

Most software project problems do not suddenly appear on release day. There are usually warning signs.

A dependency has not been resolved. A critical ticket has not moved. Something important does not have an owner. A milestone is getting closer, but the work underneath it is not. Individually, those things are easy to miss.

AI with access to project context could help surface those patterns earlier and essentially say, “You might want to look at this.”

That does not mean AI decides whether a project is in trouble. The project manager still brings the experience, judgment, and knowledge of the team. AI just gives them better peripheral vision.

Superpower #3: Seeing Beyond the Ticket

This is where MCP gets particularly interesting for software teams. A software project does not actually live inside a project management board. It lives across tickets, code, commits, reviews, repositories, conversations, and the people doing the work.

A ticket might say In Progress. Okay. But what is actually happening?

Has code been committed? Is there a review underway? Has development activity stopped? Is the ticket connected to the work you expected?

The more of that context an AI assistant can understand, the more useful its answers can become. This is also why connecting project management and source code matters.

Assembla brings project management together with Git, SVN, and Perforce workflows, allowing development activity and project work to live closer together. MCP opens up an interesting next step: making more of that connected context understandable and useful to AI.

Every Superpower Needs Guardrails

Yes, I went there.

Giving AI access to project information does not mean giving it the keys to everything. There is a big difference between an AI assistant that can read, recommend, prepare, and execute. Those should not automatically be treated as the same level of permission.

Maybe an AI assistant can read tickets and identify a potential blocker. Maybe it can recommend changing a priority. Maybe it can prepare an update for approval. Actually changing project data is another step.

The right model depends on the team, but the principle is simple: give AI enough access to be useful, not unlimited access just because you can. Permissions, auditability, and human oversight still matter.

The Real Superpower Is More Time to Think

For me, this is the bigger point. The best project managers are not valuable because they are good at clicking through tickets. They are valuable because they understand priorities, people, dependencies, tradeoffs, and what needs to happen next.

Every hour spent assembling status reports or hunting through stale tickets is an hour that is not being spent on those things.

If MCP can remove some of that administrative work, surface important information sooner, and make project context easier to understand, that is where the real value is.

Not replacing the project manager. Giving the project manager more time to actually manage the project.

AI Does Not Need to Be the Hero

There is a temptation with AI to make the technology the star of everything. I think that is backwards.

MCP does not suddenly make AI capable of running your software project while everyone goes for coffee. What it can do is give AI access to better context. And better context can help the person already responsible for the project make faster, better informed decisions.

That is a much more realistic and useful vision of AI in project management.

Assembla is exploring how MCP powered capabilities can connect AI more closely with project and development workflows while keeping teams in control.

Because ultimately, the project manager is still the hero. MCP just gives them a few more superpowers.

FAQs

What is MCP in project management?

MCP, or Model Context Protocol, can connect AI applications with project management tools and data, giving AI access to relevant project context within the permissions a team allows.

Can AI update project tickets through MCP?

Potentially, yes. What an AI assistant can read or change depends on the MCP implementation and the permissions provided to it. Teams can choose to keep AI read only or allow specific actions.

Does MCP replace project managers?

No. MCP can help AI handle information gathering, routine analysis, and administrative tasks. Prioritization, judgment, communication, and leadership still belong to the project manager.

Read the whole story
alvinashcraft
14 minutes ago
reply
Pennsylvania, USA
Share this story
Delete

1.0.85

1 Share

2026-09-16

  • Vim mode is now available to everyone. Turn it on with /vim or by setting editorMode to vim for modal editing in the composer, with the current mode shown while you type.
  • Add /settings options to opt in to context management tools for agents and subagents
  • Set transcriptView to "concise" to group tool activity into expandable work summaries.
  • Add /config to open a sidebar configuration screen in the CLI
  • Add /sandbox Network host allow/deny rules without replacing your configured upstream proxy
  • Add session and memory import commands for the semantic JSONL interchange format
  • Add copilot instruction list and copilot lsp list, replacing copilot plugins list --kind instruction and --kind lsp
  • Add --json to copilot plugin list, copilot plugin marketplace list and copilot plugin marketplace browse
  • Add enable and disable to copilot plugin, copilot mcp and copilot skill, replacing copilot plugins enable/disable --plugin|--mcp|--skill
  • Add support for GPT-6 Astra
  • Managed sandbox sessions can now be disabled for the rest of the session from an approved bypass prompt.
  • --add-dir rejects non-directory and inaccessible paths uniformly and aborts startup before session initialization
  • Streamer mode masks internal model names in /model, the footer, and startup diagnostics without restarting model initialization on toggles
  • Fixed the one-command sandbox bypass on Windows: when the sandbox container refuses a policy-blocked write for want of a privilege, approving the bypass now runs the command instead of stopping after the permissive retry, so it no longer takes disabling the sandbox for the whole session
  • Respect terminal color themes even when palettes are incomplete
  • Failed new-session handoffs stop unused clients from polling and preserve the current session, schedules, and unsent prompt.
  • Earlier messages remain visible when switching back to a background session with frequent hooks.
  • End and Ctrl+E move the cursor to the true end of a wrapped line, so typing or Ctrl+K no longer edits one character early inside a long word or URL. On such a line the landing spot is the wrap boundary, so pressing End or Ctrl+E again advances to the end of the next visual row
  • --share=~/notes.md now writes the exported session to your home directory instead of creating a folder named ~ in the current directory
  • Modified chords such as Ctrl+X, Alt+X or capital X no longer trigger the /tasks letter shortcuts; only unmodified a, f, x, r, b, j and k respond. Enter, Escape, the arrow keys and Ctrl+G / Ctrl+P / Ctrl+N are unaffected
  • Scheduled prompts show an error when they fail at runtime
  • CLI retries image prompts without images when providers reject image-limit requests
  • Authenticated model lists refresh after startup auth hydration
  • MCP servers no longer fail to load when the CLI is connected to a running IDE. The in-process IDE bridge was rejected by config validation, which failed the plugin reload and restricted the session
  • copilot init now removes the .github directory it created when the run exits without writing an instructions file.
  • MCP turns continue even if tool list refresh fails after a tool change
  • MCP servers keep correct workspace source labels after trusting a folder
  • An editor or shell that leaves mouse tracking on no longer leaves your terminal reporting clicks, during the session or after the CLI exits
  • The /permissions picker marks Allow all when --allow-all-tools, --allow-all-paths and --allow-all-urls are all set
  • Resumed sessions show completed reasoning as Thought instead of Thinking…
  • copilot --help describes the --no-* options again, and --no-auto-update says it runs the version bundled in the binary. --no-auto-login and --no-sandbox stay supported but remain hidden from help, as they were before the clap port
  • Restore keyboard input and screen output on macOS and Linux when you return from an external editor that reset the terminal
  • Model lists refresh after signing in, switching accounts, or signing out
  • Fixed the thinking shape sent to Claude models classified as adaptive-only: they now stay adaptive instead of failing (turning thinking off lowers reasoning effort instead), and reasoning effort is capped at high whenever thinking is disabled
  • Run sessionEnd hooks when /clear closes an interactive session
  • Plugin agents expand ${PLUGIN_ROOT} placeholders in mcp-servers frontmatter
  • Skills from directories added with --add-dir are no longer missing when a skills load races the directory registration
  • A relative --additional-mcp-config @<file> path now resolves against the session working directory under --resume=<id> and --worktree instead of the launch directory, and ~/ expands.
  • Windows sandbox denials of loopback and local network access prompt to re-run the command outside the sandbox
  • Approved sandbox retries are labeled sandbox relaxed while network policy stays enforced, or sandbox bypassed when fully unsandboxed; failed bypasses explain that host permissions still apply
  • Cancelling an MCP tool call now notifies the MCP server and cleanly ends the turn.
  • Scrolling the wheel with mouse capture off no longer walks backwards through prompt history in terminals that report DEC private mode 1007 (alternate scroll), such as Ghostty
  • MCP OAuth requests additional scopes when needed and retries the tool call
  • Changing reasoning effort now takes effect before the next logical request in an active turn, while retries keep their original effort
  • Automatic compaction now saves a checkpoint that appears in /session checkpoints
  • Windows CLI artifacts run without requiring the Visual C++ Redistributable
  • Keep terminal theme colors consistent at startup and during live appearance changes
  • Interactive mode submits startup prompts even when model discovery is still loading.
  • MCP tools with boolean property or array-item schemas work with Gemini instead of causing a 400 error
  • An enterprise-managed sandbox policy delivered by MDM or a managed settings file no longer discards sandbox.allowBypass, so bypass prompts and /sandbox disable work as the policy intends
  • The managed sandbox startup notice no longer says sandboxing can't be turned off when your organization's policy allows a session opt-out; it names /sandbox disable instead
  • Viewing or attaching an image in a format the model cannot read, such as BMP or TIFF, no longer leaves the session unable to send any further message; the image is now reported as an unsupported format that you can convert to PNG, JPEG, WebP or GIF
  • The YOLO status indicator reflects the active session after switching sessions
  • Computer Use now stays in sync across /computer and whole-plugin /plugin toggles.
  • Pressing Enter in the Sessions tab now foregrounds the highlighted session, even when a background refresh rebuilds the list at that moment, instead of sometimes opening a different session
  • Indexed search on Windows prevents new disk-space leaks when updating indexes
  • Keep long /ask responses visible after generation completes
  • When session history is truncated or compacted just as a turn finishes, the "Working" indicator now clears instead of staying up for the rest of the session
  • COPILOT_ALLOW_ALL no longer refuses to start the CLI on values such as 1, 0, yes or an empty string, and falsey values now disable automatic tool approval instead of enabling it
  • Subagent launches honor explicit model, reasoning effort, and context tier preferences from applicable global and custom instructions
  • A failed command whose EPERM or EACCES diagnostic names a sandbox-blocked path now offers to run outside the sandbox, even when the command line never named that path
  • A write blocked by a read-only sandbox path, and a Node or Go network failure blocked by the sandbox, are now recognized as sandbox denials instead of surfacing as raw errors
  • Report in-memory MCP servers as memory instead of local in copilot mcp list
  • /compact no longer reports an empty model response when a valid summary was returned
  • Streaming responses preserve message chunk ordering before final output.
  • Retry responses keep the correct streamed message and reasoning after mid-stream model failures
  • Workspace .mcp.json servers load correctly after trusting a folder on startup
  • When image-heavy requests exceed model limits, user-provided images are prioritized over tool-generated images, newer messages are kept first, and the CLI reports any removals.
  • Plugin-contributed agents discovered by the CLI can now be selected and run.
  • Fixed same-turn MCP tool-list refresh after received change notifications, including modern subscription-based servers.
  • The remote session timeline entry now advertises ctrl+o to show or hide the QR code, matching the key that actually toggles it
  • Show when sandboxing is only enabled for the current session in /sandbox status and settings.
  • Interactive --yolo startup remains available before authentication when no managed policy evidence is present
  • Indexed search shows when enabled, works on Windows ReFS volumes, supports explicit cloud-sync overrides, and keeps refreshing on Linux when native file watches are exhausted.
  • /copy includes task completion messages when available
  • OAuth-authenticated MCP servers connect reliably during session startup
  • ctrl+h no longer deletes a whole word in tmux, screen, and remote sessions that carry a Windows Terminal WT_SESSION from elsewhere. As an accepted tradeoff, ctrl+backspace now deletes a single character in those sessions — including a genuinely local Windows tmux or screen pane — where ctrl+w still deletes a word
  • MCP servers now see the same copilot-cli client identity when you add a server and when a session connects, carrying the shipped CLI version instead of 0.0.0
  • Interactive mode starts and submits the initial prompt when using --auth-token-env
  • Use /settings taskbarPresence false to disable Windows taskbar session status. Loader-managed sessions restart immediately; standalone sessions require a manual restart.
  • Pressing Escape once cancels MCP inference approval prompts once
  • MCP reload summary shows servers still starting after timeout
  • Initial prompts start immediately for Entra-authenticated sessions while token refresh runs in the background.
  • Choosing approve-for-location now persists tool approval to avoid repeat prompts
  • Large sessions resume without freezing the interface during context token counting
  • Configured hooks keep running after an extension restarts instead of silently stopping and later denying every tool call; the extension's own callback hooks resume once it re-registers
  • The allowManagedHooksOnly policy now also blocks extension-registered preToolUse, postToolUse and postToolUseFailure callbacks, which previously bypassed the managed-only lockdown that every other hook event already applied
  • A PowerShell write the sandbox blocks offers to run the command outside the sandbox
  • When you have more than one GitHub account in your credential store, a sandboxed gh command now acts as the account gh is logged in as instead of an arbitrary one.
  • The /rubber-duck command is hidden after a model refresh removes its compatible critic
  • Sandboxed runs now use relocated developer-tool caches from env vars and tool config files
  • On Windows, a sandboxed command that runs git without naming it — a hook, a build tool, or an npm install that clones over HTTPS — no longer dies inside the credential helper's MSYS2 shell.
  • Reduce metadata scanning time for large local session histories, with increased thread and memory use
  • Pause and resume Agent Factory runs from the /factories dialog
  • Apply managed Edit and Write rules to recognized native shell redirections and supported in-place sed operations
  • Show active scheduled prompts in the CLI footer by default
  • Use /worktree, /move, and --worktree without enabling experimental mode
  • Make /collect-debug-logs and --collect-debug-logs available to all users
  • /sandbox disable turns the sandbox off for the current session when your organization's policy allows bypass
  • Shell completions are generated from the same grammar the CLI parses with, so copilot <TAB> offers root flags alongside subcommands and each subcommand offers only its own options
  • Command-line parsing moved from Commander to a Rust grammar; error and help wording changed, copilot login --host now works, and --max-autopilot-continues no longer accepts scientific notation
  • Show /sandbox filesystem paths as absolute paths; typing ~/path still expands to your home directory
  • Move the /sandbox Filesystem paths into their own list, opened from a Paths row
  • Show trust status, tier, and eligibility details for online resource catalogue results
  • /usage shows per-model AI Credit consumption in usage breakdowns
  • Improve /sandbox guidance and show /sandbox policy in command help
  • On supported Windows sandbox policies, interactive shell commands now record blocked accesses. One approved escalation retries with file and process restrictions recording instead of blocking while network policy remains active, then falls back to the disclosed full bypass only if still blocked
  • Speed up startup when resuming an existing local session by its exact UUID with --resume
  • Replace copilot plugins install --skill [--scope project] with copilot skill add [--project]; the --scope spelling is gone
  • Remove the cross-kind --kind, --scope, --mcp and --skill flags from copilot plugins; use copilot mcp and copilot skill
  • copilot plugins list --json now emits a flat array of plugins instead of the cross-kind { plugins, errors } object; scripts reading .plugins must be updated
  • copilot plugins list is now an alias of copilot plugin list and reports only plugins, no longer MCP servers, skills, instructions or LSP servers
Read the whole story
alvinashcraft
15 minutes ago
reply
Pennsylvania, USA
Share this story
Delete
Next Page of Stories