 Log in


Episode 930
Matthew Renze on Best Practices When Working With AI Agents
Matthew Renze does AI consulting while pursuing a doctorate in AI. He describes things to consider when build AI Agents and when using AI Agents.

|
Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
|
Episode 930
Matthew Renze on Best Practices When Working With AI Agents
Matthew Renze does AI consulting while pursuing a doctorate in AI. He describes things to consider when build AI Agents and when using AI Agents.


About a year ago, Google shipped the first version of the Antigravity IDE. It was basically an agent-centric VS Code fork. Fine tool, fine models underneath. Nothing world-beating, but certainly useful. Back in May, the product rebooted with Antigravity 2.0, an agent-first experience that pushed the IDE to the background, and focused on the desktop app and CLI experience. Better tool, better models. It didn’t leapfrog competition, but put Google in the game. Here in November of 2026, it’s a different story. The product caught up with competitors in key areas, innovated in a few others, and is powered by legitimately good coding models. It’s worth a second (third, fourth) look!
Disclaimer: I work at Google and use Antigravity every day, alongside tens of thousands of coworkers. I do so because I prefer to use what I ask developers to use! While I use an internal version of Antigravity for day to day work, I also use my personal Google AI Pro subscription so that my developer experience often feels like that of a “regular” user. I’ve done my best to deliver a fair assessment below, but please point out any mistakes I make about the landscape.
Over the last 90 days (August 19 – November 17, 2026), no other leading AI developer tool shipped as many net-new capabilities as the Google Antigravity team did. To be sure, everybody has been shipping a ton in this space. Across all surfaces (Antigravity App, CLI, IDE, SDK, IDE extensions) we delivered 150 versioned releases, and 900+ public changelog items. Claude Code delivered ~84 CLI releases with hundreds of total items, Microsoft dropped dozens of features as part of this GitHub Universe window, Devin had ~58 tracked releases, OpenCode delivered about 65 tagged releases, and OpenAI Codex had about 40 shipping events.
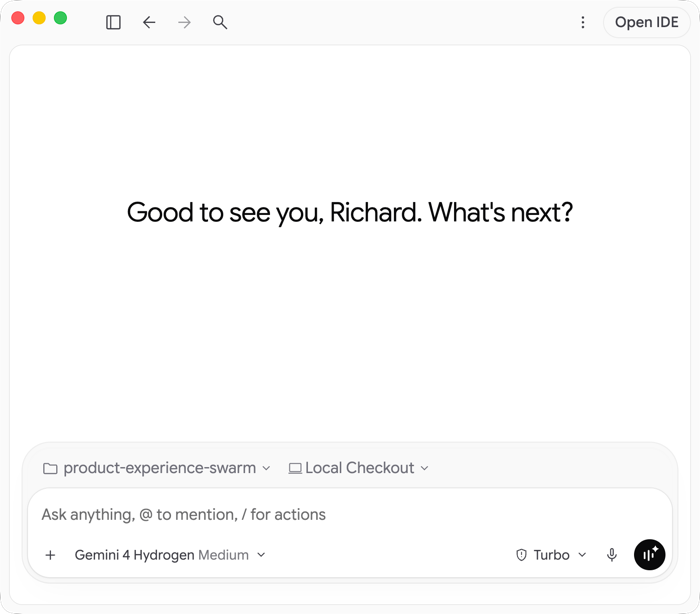
Now you might say “sure, you shipped a lot of features because you were behind on functionality others already had.” True. We still needed to ship them, though! Let’s look at those items first.
Over the past 90 days, Antigravity added a lot of features already present in other great AI tools.
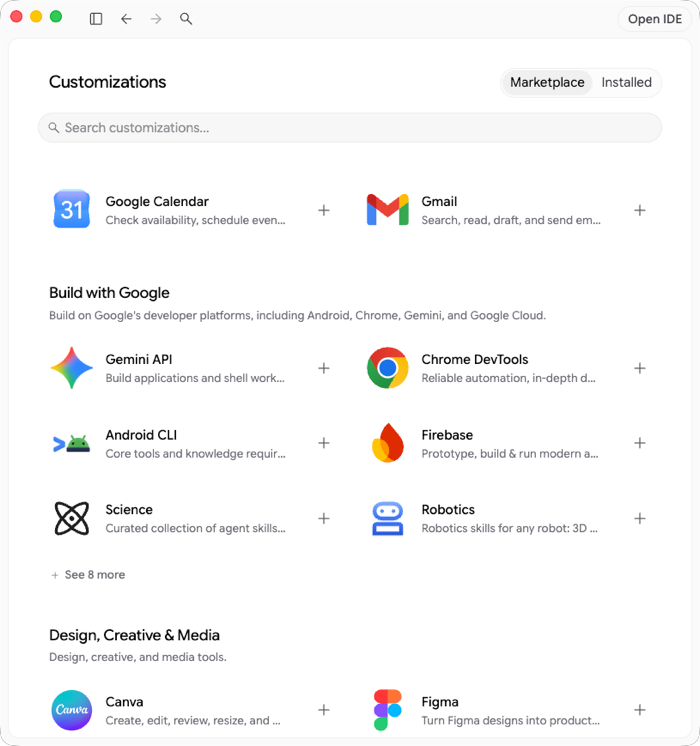
Plugin / skill / MCP marketplace. You want an easy way to find and install useful plugins. OpenAI Codex, Claude Code and others have this. We’ve added a helpful “customizations” experience for discovery and management of these extensions.
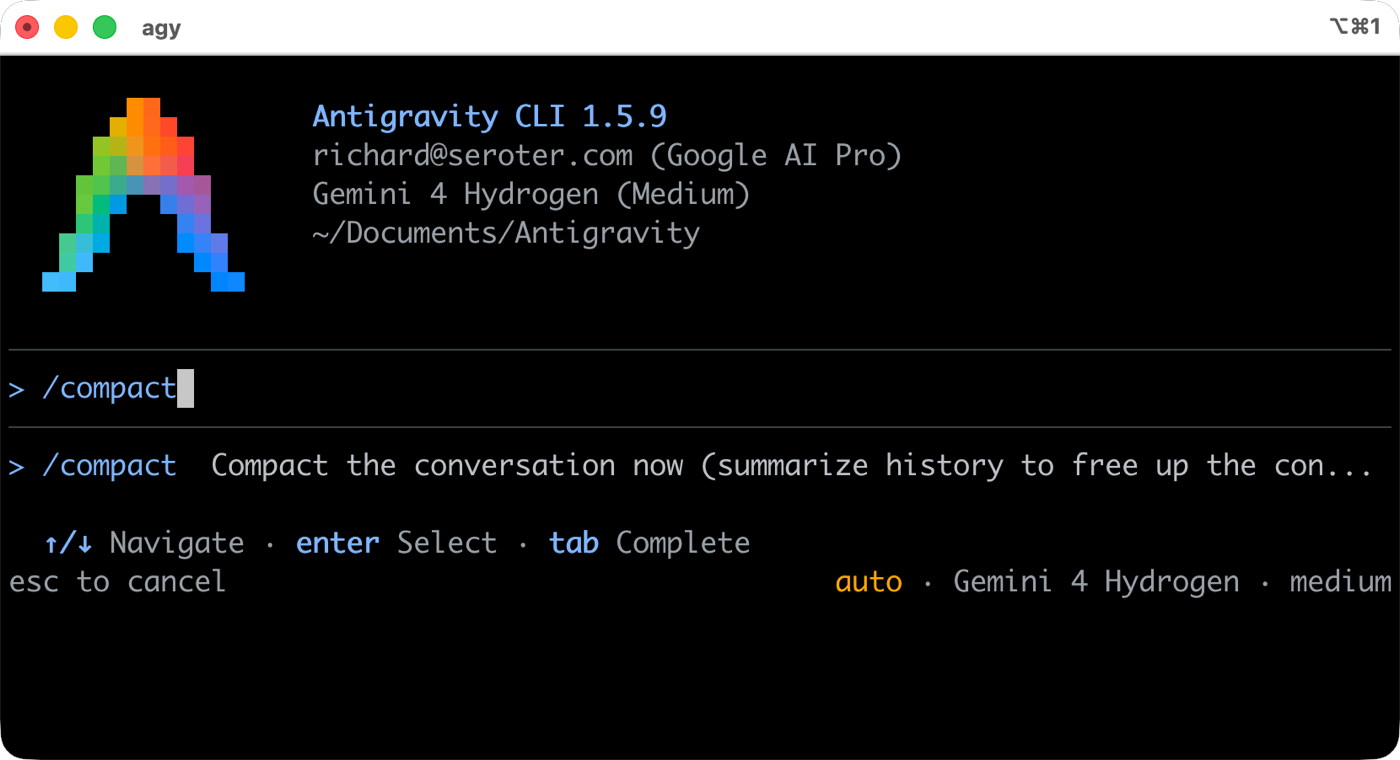
Manual context compaction. Claude, Cline, and OpenCode have this. Now you can do an on-demand summarization with Antigravity. We also doubled the automatic context checkpoint from 256k to 512k tokens, which is unique.
Lifecycle hooks. Anthropic invented this taxonomy and now we have these plugin lifecycle hooks for PreToolUse, PostToolUse, Stop, SessionStart events.
Consolidating on AGENTS.md and directory-scoped rules. Instead of proprietary frontmatter-only rule files, we’ve changed (alongside Cursor, Claude Code, Codex) towards AGENTS.md with parent directory traversal.
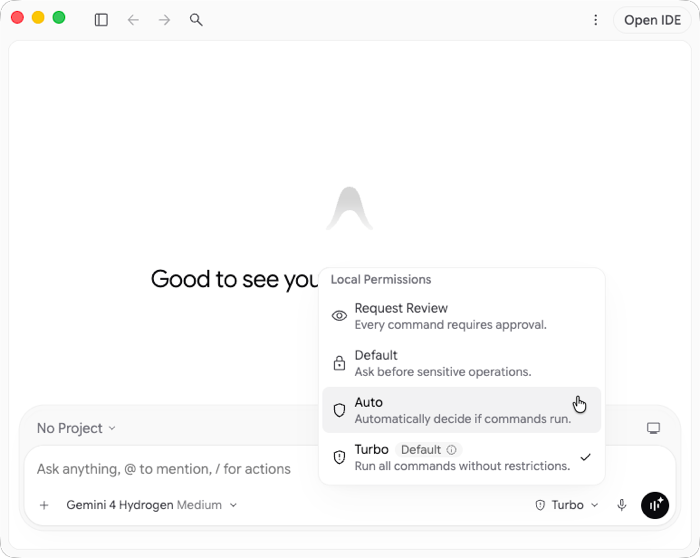
Default “auto mode.” How much do you want to be interrupted to provide feedback on harness decisions? Other tools offered an auto permission mode, and we’ve added to the existing “turbo”, “request review”, and “default” options.
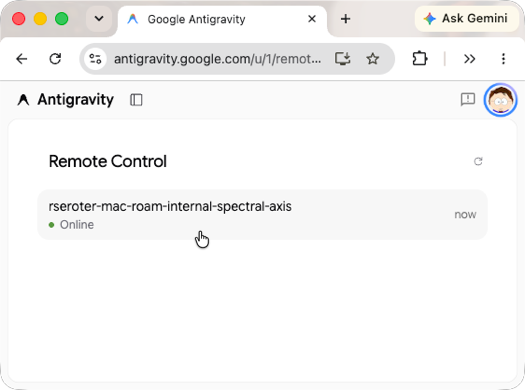
Remote control of a local terminal. Drive your laptop session from a phone. Claude Code popularized this, and now you can steer your machine from anywhere.
Side-channel questions and mid-turn steering. Claude Code and Copilot offer /btw for tangential questions. Antigravity now has that too, with a good experience where you can also pick which model answers the question. You can also add relevant questions mid-stream and immediately send those updates to the main trajectory.
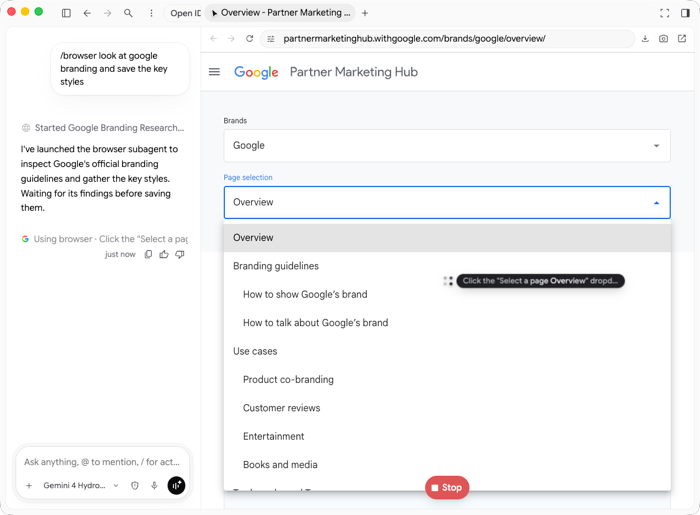
Autonomous browser use. We’ve had browser use in the past, as did most tools, but we removed it. We’ve since updated that, and now have a rich /browser experience for opening web pages, interacting with running apps, inspecting errors, taking screenshots, and more.
Raw key auth and bidirectional stream/json piping. Like Aider, OpenCode, and Claude Code, you can now stream JSON out for better Unix piping. And we’ve added API key as a CLI parameter for non-interactive scenarios. All of this helps background workers.
Besides adding functionality that everyone else has, the Antigravity team recently introduced a set of relatively unique features for those building with AI.
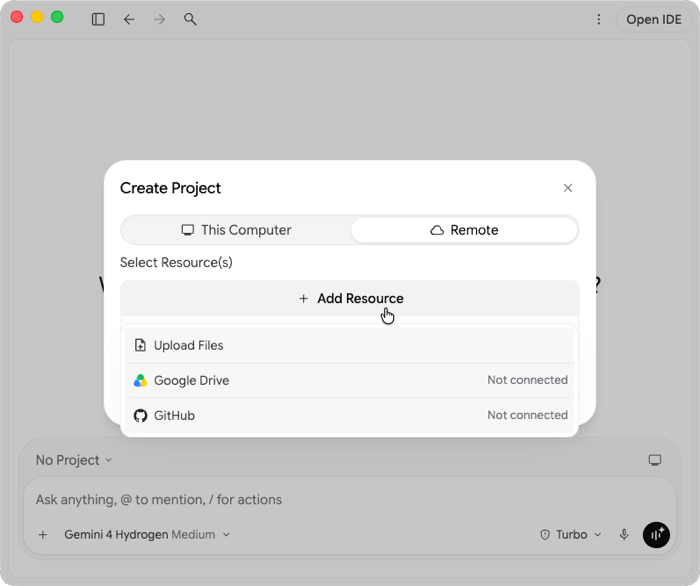
Remote cloud agents. Keep executing even when the laptop closes. Remote Agents run in a persistent cloud VM attached to GitHub repos or Google Drive folders. Access this from anywhere.
Gemini 4 Argon, Carbon, Hydrogen, and Orchestrator. Objectively, the Gemini 4 models are strong coding models. In both benchmarks and real-world usage, developers are increasingly leaning on them. Antigravity also added support for Claude Sonnet 5.5 and Opus 5.5. Note different access based on subscription tier.
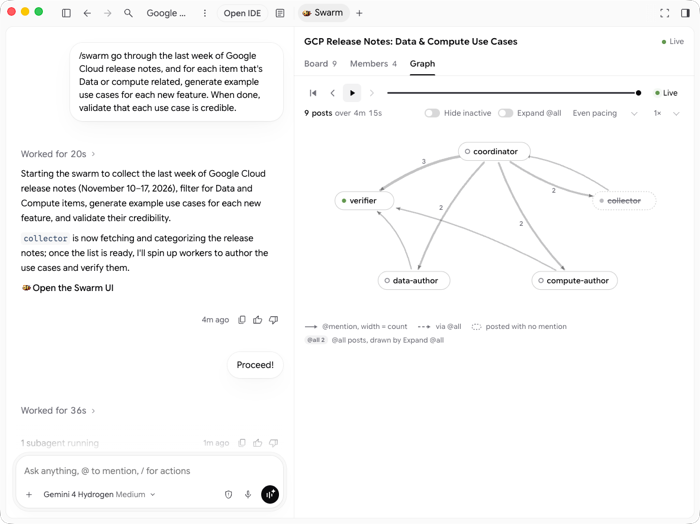
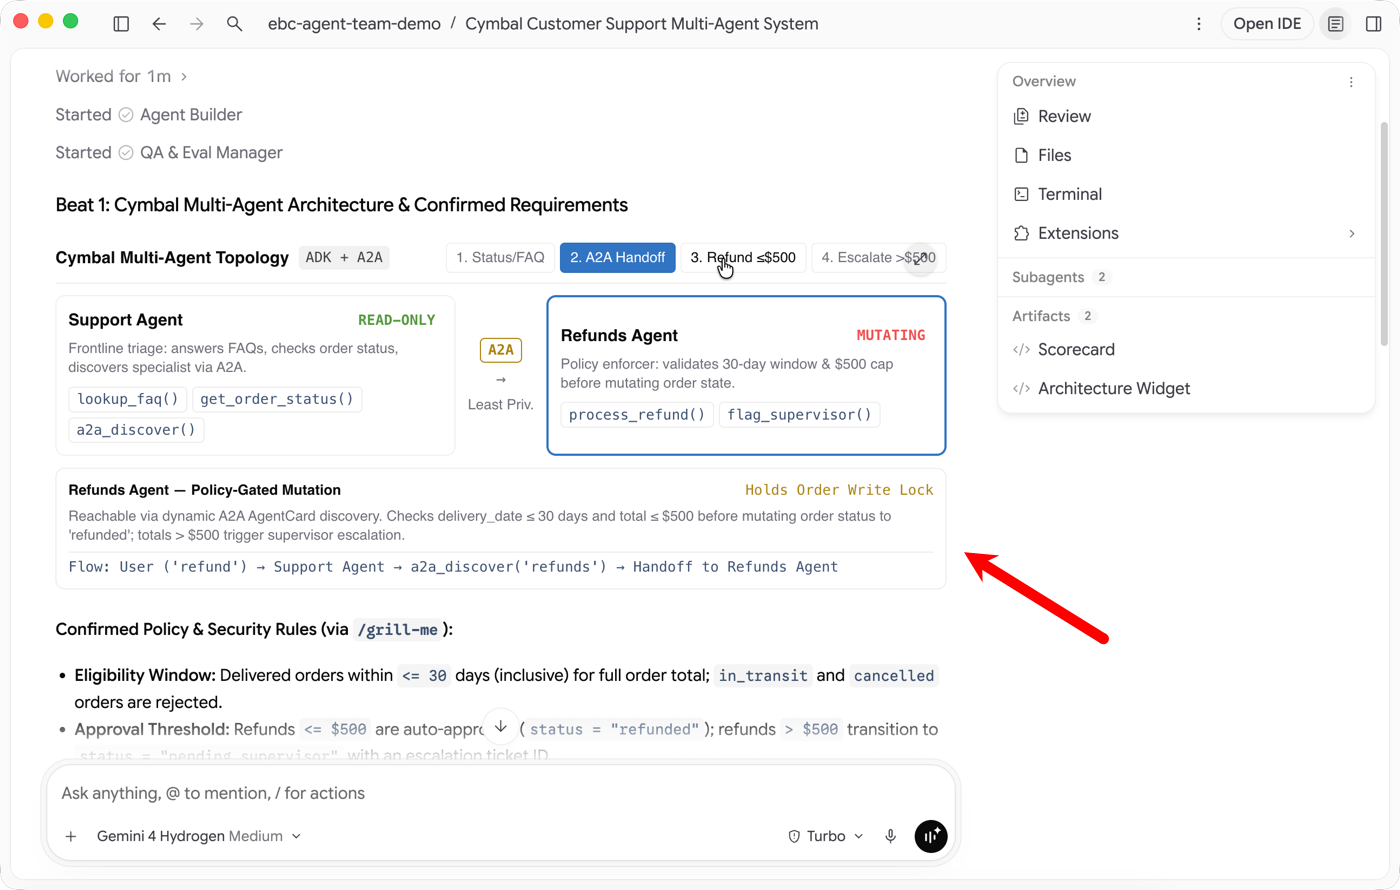
Shared-board agent swarms. /swarm mode is pretty awesome. Run a team of named agents that work in parallel and share a message board. Easy to start, and the visualizations make it easy to see what’s going on.
Zero-install dynamic Python workflows. This one is brand new. The Antigravity agent writes a runs a Python script that creates a predictable control flow for your agents.
Full-duplex Gemini Live voice. Unlike others that offer a audio recording as input, Google Antigravity ALSO supports an ongoing two-way conversation with the agent. Pairing this with remote agents and on-the-go work feels compelling.
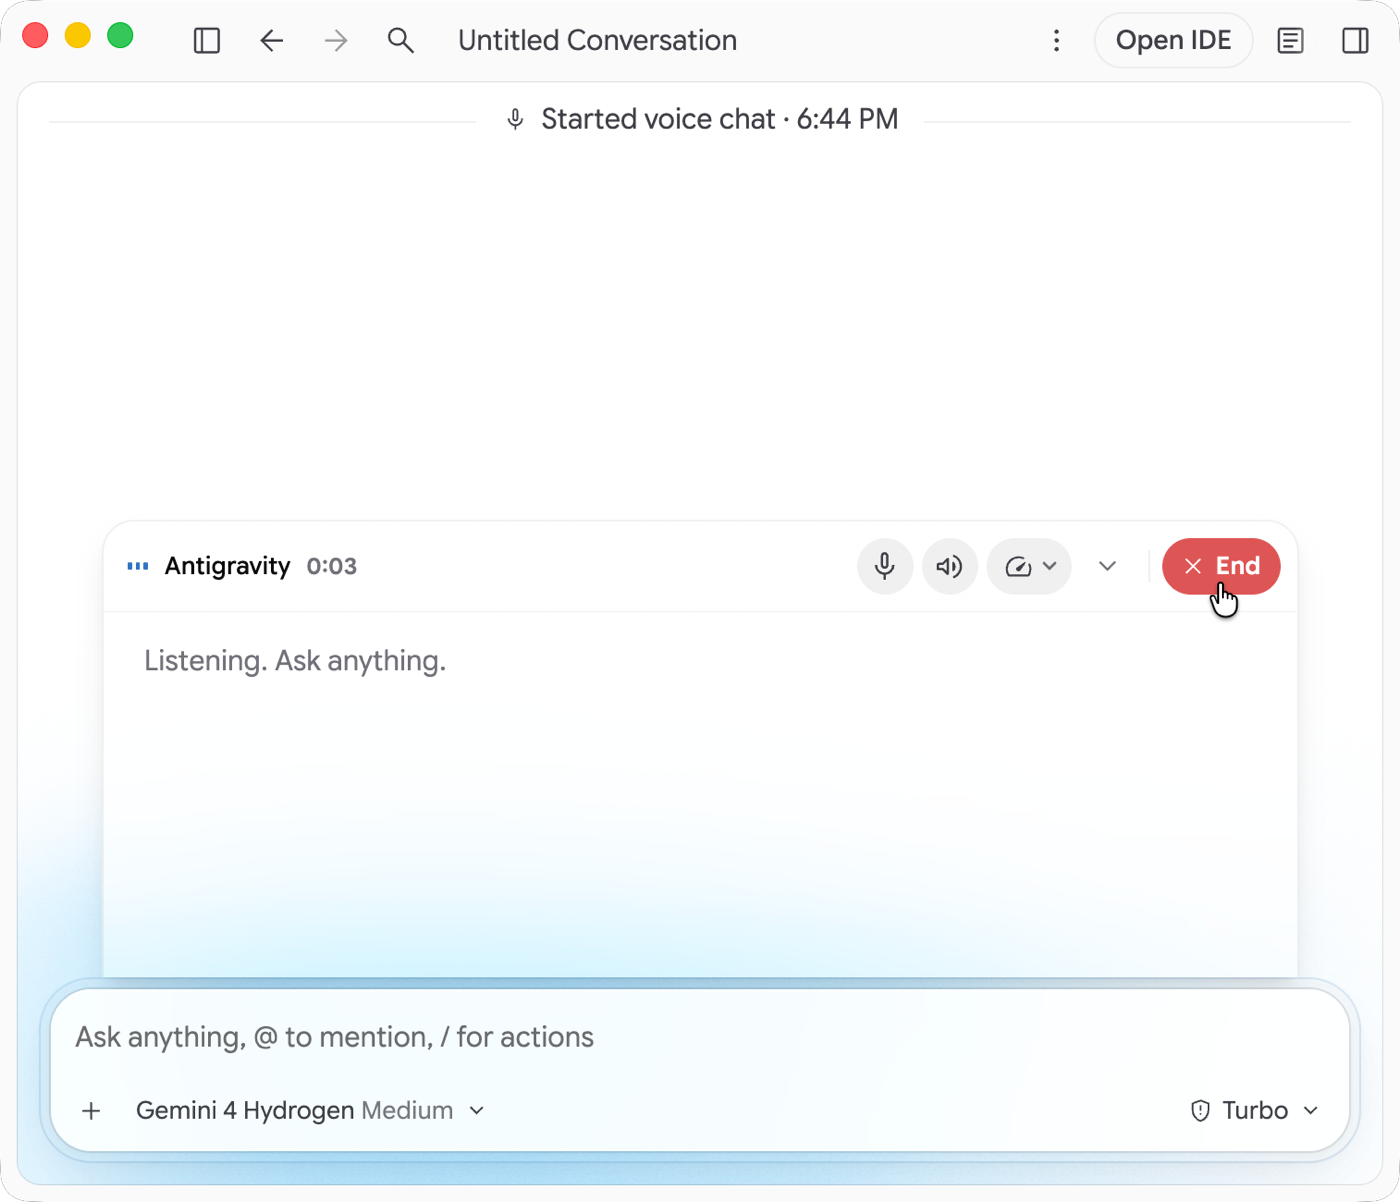
Direct subagent messaging. With the Antigravity CLI, you can DM a subagent directly from the main conversation. We’ve made a lot of investment in making multi-agent feel natural.
Generative interfaces in the main chat. Ask the agent to create interactive widgets for the output.
Unmatched surface breadth and usable $0 tier. Use a desktop app, IDE, CLI, IDE extensions (for VS Code, Visual Studio, Eclipse, JetBrains, Zed, XCode), and an SDK. It’s all available in the free tier, as well as paid tiers. The paid tiers give you access to more up-to-date models, more quota, and more functionality (e.g. multi-agent teamwork, remote control).
Sure, many individuals don’t care about “enterprise” features. But millions of developers want to use rad agentic tools at work, so these capabilities matter. Many vendors are chasing the same set of functionality, as it’s required for winning businesses at scale.
Seat bundling and consumption flexibility. Antigravity usage is now included with Gemini Enterprise Standard and Plus seats. Or, get it seat-free with Gemini Enterprise pay-as-you-go.
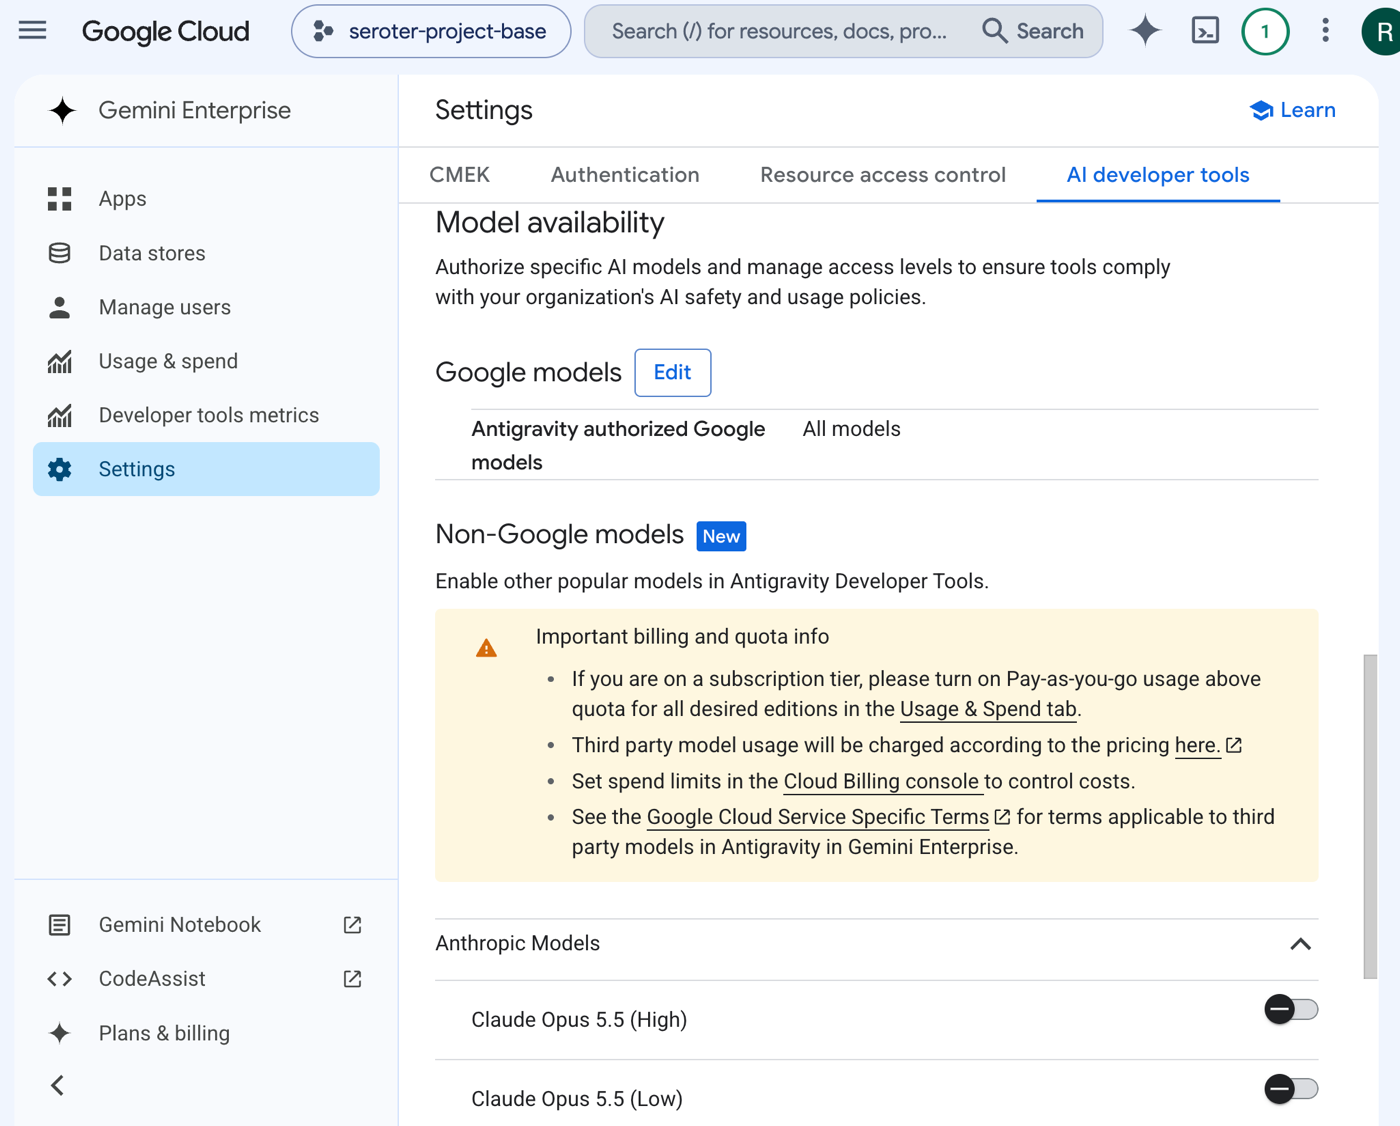
Multi-vendor frontier model governance. Gemini Enterprise admins can enable (or disable) developer access to frontier models from Anthropic and Google. All this on one bill, with the same Google Cloud Terms of Service and IAM perimeter.
Pooled quotas with per-user caps. The individual user quota is pooled together so that the whole team can tap into it. But we’ve also got controls to prevent one user from chewing it all up.
Granular harness, browser, MCP and plugin guardrails. Set up policies to centrally govern MCP server allowlists, plugin/marketplace access, browser rules, and more.
None of these AI developer products are “done” and we have room to improve ourselves. Many of these items are present in other products, and our Antigravity team is going to keep quickly closing gaps while adding novel features.
OS-level desktop computer use. Claude Desktop, Codex Desktop, GitHub Copilot App all work with more than sandboxed browser tabs.
Autonomous PR merge and inbound chatops triggers. Antigravity doesn’t have the autonomous PR closure like Copilot’s “Agent Merge” and lacks the @ mentions cloud triggers inside Slack, Teams, or Jira threads.
Ambient memory. Memory remains manual (/learn triggers reflection) versus nightly auto-consolidation (like Devin’s dreaming).
Google Antigravity is faster, more usable, with better functionality, and backed by better models than ever before. It’s genuinely fun to use for coding, research, content creation, and tons of other tech and non-tech use cases.

Over the last few months I’ve worked with a lot of teams taking a hosted agent from pilot to production. A working demo is only the start. The questions that decide whether it ships come next: Will the subnet hold up when usage takes off? Can the agent call internal services that use our own certificates? Where exactly can it connect, and who decides? Can it run on the Azure Kubernetes Service (AKS) clusters we already operate? And what happens when a two-hour job gets interrupted?
At Microsoft Ignite 2026, we’re announcing a solution to each of these challenges for hosted agents in Foundry Agent Service. Below you’ll find what’s new, what you can use today, and what’s still to come. The egress and private CA updates apply to managed hosted agents, the ones Foundry runs for you; BYO-AKS support will be documented separately.
| What’s new | What it means for you | Status |
|---|---|---|
| Shared subnet IPs | Run many more sessions from the same subnet; your session quota still applies | Generally available (GA) |
| Private CA trust | Call internal services that use your company’s certificates, with certificate checks still on | Public preview |
| Network egress controls | One place to decide where an agent can connect, enforced outside the agent | Generally available (GA) |
| Azure Policy governance for egress | Admins require compliant egress settings across a subscription or resource group | Public preview, starting in three regions |
| Deploy hosted agents to your own AKS clusters | Foundry’s agent runtime on your own AKS cluster | Public preview targeted for early December |
| Long-running resilient execution | Opt-in recovery for long jobs after a crash or redeploy | Generally available |
| Configurable idle timeout | Sessions can wait from 2 minutes to 4 hours between requests | Generally available |
| Memory snapshots | Faster cold starts for agents with heavy startup | Public preview |
| A2A passthrough | Host your A2A v1.0 agent on Foundry with a small Python adapter | Public preview |
If you run hosted agents in your own virtual network, each session used to take its own IP address from your delegated subnet. A /24 topped out at about 250 concurrent sessions, and teams with a tight IP plan hit that wall fast.
Hosted agent sessions now share subnet IP addresses. Each session still runs in its own VM-isolated sandbox. What changes is how far your subnet goes: our planning estimate for a /24 is now about 60,000 concurrent sessions, and even a /27, the smallest supported size, is planned for about 7,500. IP sharing is on for everyone, with no request needed.
These are planning estimates, not guarantees, and we still recommend a /24 or larger for production so there’s room for upgrades and maintenance. For most teams, your regional session quota is now the practical ceiling: by default 2,000 or 1,000 concurrent sessions per subscription, depending on the region. You can ask for more through a support request.
Status: Generally available now. See subnet size and concurrent sessions.
Internal MCP servers, APIs and model gateways often use certificates from a private certificate authority (CA). Agents didn’t trust them, so calls failed, and the tempting fix was turning off certificate checks. Security teams don’t like that fix, for good reason.
Now you register your CA once on the Foundry resource. The CA certificate lives in Azure Key Vault, and every project in the resource picks it up. Certificate and hostname checks stay on, public CAs stay trusted, and you don’t bake CA files into container images or recreate project capability hosts.
Trust covers two paths. Tools, toolboxes and bring-your-own-model gateways use your CA in projects on your own virtual network, usually within a minute of the update. Hosted agent code that calls internal services directly trusts your CA in new sessions. The docs list what isn’t covered yet, such as remote builds and mutual TLS.
Status: Public preview. See Connect agents to services that use a private certificate authority.
A tool list isn’t a network boundary. Agent code can start a subprocess, a library can follow a redirect, and generated code can call anything. Security teams want one place to say “these hosts, nothing else.”
Network egress controls for hosted agents are now generally available. You attach an ordered list of rules to an agent: allow or deny hosts, add headers on the way out, or send traffic through your own gateway. Foundry enforces the rules outside the agent’s sandbox, before requests reach their destination, so they don’t depend on the agent’s code behaving. If a policy can’t be evaluated, the request is denied. Egress controls add to your own network controls, like Azure Firewall; they don’t replace them.
If security review is what’s holding your agent back, start here. Turn on Audit mode with a default of deny. In Audit mode, Foundry logs every request it would have blocked but lets it through. Header changes and rewrites still apply, so test them in a non-production environment first. Run representative tasks, review the destinations you see, and refine the allowlist. Then switch to Enforce and deploy a new agent version, since running sessions keep the policy they started with. Your security team reviews a list built from real traffic instead of a guess.
Admins get a central check too. With Azure Policy governance (public preview), you assign policy at a scope such as a subscription or resource group, and Azure Policy checks that egress settings and new hosted agent versions follow your rules, like Enforce mode, a default of deny, and only approved destinations. Start in Audit to see what doesn’t comply, then switch to Deny to block noncompliant changes. Sessions that are already running keep going uninterrupted. The governance preview starts in Canada Central, Spain Central and Korea Central.
Above Security runs its AI investigative agents on hosted agents inside its own network:
“Insider risk is an investigation problem, not a policy problem, and Microsoft Foundry gives our AI investigative agents a secure home on Azure. With hosted agents in Foundry Agent Service running inside our own network and Claude served natively through Foundry, we can bring our agents to Azure customers without rewriting them.”
Amir Boldo, CPTO & Co-founder, Above Security
Status: Egress controls are generally available (GA). Azure Policy governance is in public preview. See Add guardrails to a hosted agent and Govern hosted agent egress with Azure Policy.
With this new deployment option, Foundry runs the agent runtime on your Azure Kubernetes Service (AKS) cluster. You build, deploy and call agents through Foundry the same way you do today, with the same APIs, azd flow and endpoint. Each session runs as its own pod in a lightweight VM (AKS pod sandboxing), so sessions stay isolated from each other. Your networking, container registry, policies and capacity stay yours.
Managed Hosted Agents are the best fit when you want Foundry to operate the hosting infrastructure for you. The option to BYO-AKS is designed for organizations that already operate AKS as a platform or need agent workloads to run within an infrastructure, network or compliance boundary they manage. It gives customers a choice of operating model without changing how developers work with agents in Foundry.
Your platform team controls the cluster capacity and scaling, network configuration, container supply chain, storage settings and infrastructure monitoring. You can apply existing virtual networks, private connectivity, DNS, routing, firewall and egress controls; choose node pools and registry integrations; and use your established storage and observability practices.
Responsibility is shared. Foundry manages the agent lifecycle and the Foundry-managed integration components. You operate the AKS cluster and its supporting resources, such as networking, node pools and storage.
OctopusOS runs on hosted agents today and sees the AKS deployment as the way to extend into its customers’ own environments:
“At OctopusOS, our customers – like accounting firms handling sensitive client data – need agents to run where their data and compliance boundaries are. Foundry Agent Service already gives us a managed, governed agent runtime; bringing our own AKS lets us extend that same experience into customer-controlled environments without rebuilding our platform.”
Ran Tao, CEO & Founder, OctopusOS
Status: Public preview is targeted for early December. Sign up now and tell us what you need.
With resilient execution, agents that opt in can recover long jobs after a crash, restart or redeploy instead of starting over, and reconnecting clients can pick up the streamed output. Recovery reruns your handler, so save progress as you go and make sure actions like sending an email aren’t repeated.
Sessions can also wait longer between requests. You can set the idle timeout per agent version from 2 minutes to 4 hours (15 minutes by default). Without memory snapshots, session files survive idle periods, and a session is deleted after 30 days of inactivity.
For full workflow orchestration, we’re working with Temporal. Customers who want to combine Temporal’s durable workflows with hosted agents can contact Temporal for early access to the integration. Public preview is planned for early 2027.
Status: Resilient execution and configurable idle timeout are generally available (GA). See Resilience for long-running hosted agents.
Cold starts add up when every new session imports the same libraries and loads the same data. With memory snapshots, Foundry captures your agent once it’s ready and restores that state for new sessions, so they skip repeated startup work. You turn it on per agent version, in Python or .NET.
One catch: a snapshot restores your agent’s ready-to-run starting point, not a running session. Memory and local files, including $HOME, don’t survive an idle period in snapshot sessions, so keep state you need later in external storage, or leave snapshots off.
Status: Public preview. See Enable memory snapshots for hosted agents.
If you already built an Agent2Agent (A2A) v1.0 agent, you can now host it on Foundry with A2A passthrough (preview) and keep your own message and task logic. A small Python adapter wraps your existing agent card and handler, and Foundry handles the endpoint, authentication and compute. The preview supports JSON-RPC, without streaming or push notifications for now, and works in all supported Foundry regions with no enrollment.
Status: Public preview. See Host an A2A-native agent.
If you’re attending Microsoft Ignite 2026, or watching on-demand content later, be sure to check out these sessions:
What still keeps your hosted agent out of production? Tell us in the comments what you’re trying to run and what’s blocking it. Most of what’s in this post started as exactly that kind of feedback.
The post Hosted agents in Foundry Agent Service at Ignite 2026: from pilot to production inside your enterprise boundaries appeared first on Microsoft Foundry Blog.
Much of the work that keeps a business running still happens in a browser: internal portals, vendor consoles and legacy apps with no API. The Browser Automation tool in Foundry Agent Service, powered by Azure Playwright Workspaces, is now generally available. It gives every Foundry agent secure, scalable browsers with isolated sessions, and includes the following capabilities:
This Ignite, the Browser automation tool is enabled with additional features for your agentic automation workloads
Our sample agent’s task is clear – Process 15 invoices, validate them against the rules, flag anomalies in Excel, and enter the validated invoices into the expense portal. That’s a multi-app task, and the agent hits the ground running with Browser automation tool in its toolbox.
Browser automation tool offers a larger set of MCP tools built for browser work, so agents can choose the right level of control for each step of a workflow. Step-by-step tools cover the full range of interactions: opening and reading pages, taking accessibility snapshots, clicking, typing, completing forms, selecting options, handling dialogs, managing tabs, uploading files, and capturing screenshots, console messages and network requests. For multistep sequences, agents can batch actions with the run-code tool. It runs one Playwright script for the whole sequence instead of a long chain of snapshot, click and type calls. We understand efficiency matters and hence recommend batched scripts for repetitive flows, and step-by-step tools for unfamiliar pages and flows with dialogs, where checking the page at each step pays off and LLM is an enabler. Because scripts can run any code, the run-code tools stay opt-in and should be enabled only for reviewed scenarios. Learn more
Browser workflows sometimes reach an unexpected page state, an ambiguous choice, or a step that needs human judgement. Live View shows the agent’s browser in headed mode in real time, so developers and operators can watch it work and see exactly how it performs each action. With Take control, a person can step in to steer the browser, for example to complete a sign-in (as seen in the demo above), give an approval or recover from an unexpected dialog. They can then hand control back and let the agent continue from where it left off. This keeps people in the loop for high-impact actions without giving up the speed of automation.
When you need to know what an agent did, session recordings let you replay its browser sessions for debugging, auditing and compliance reviews. Recording is opt-in, and recordings are stored in your own storage account, so storage role-based access control decides who can view them. Activity logs and billing observability are also available, giving you a complete record of browser activity across your workloads.
{
"tags": null,
"location": null,
"id": "/subscriptions/<subscription-id>/resourceGroups/<resource- group>/providers/Microsoft.CognitiveServices/accounts/<resource-name>/projects/proj-default/connections/browserautomation_<string>",
"name": "<string>",
"type": "Microsoft.CognitiveServices/accounts/projects/connections",
"properties":
{
"authType": "ApiKey",
"credentials": {
"key": "<API_KEY>"
},
"group": "ServicesAndApps",
"category": "PlaywrightWorkspace",
"target": "https://<region-name>.mcp.playwright.microsoft.com/playwrightworkspaces/<playwright workspace -id>/mcp",
"metadata":
{
"resourceId": ""/subscriptions/<subscription-id>/resourceGroups/<resource-group>/providers/Microsoft.ManagedIdentity/userAssignedIdentities/<identity-name>",
"enableRecording": "false"
}
},
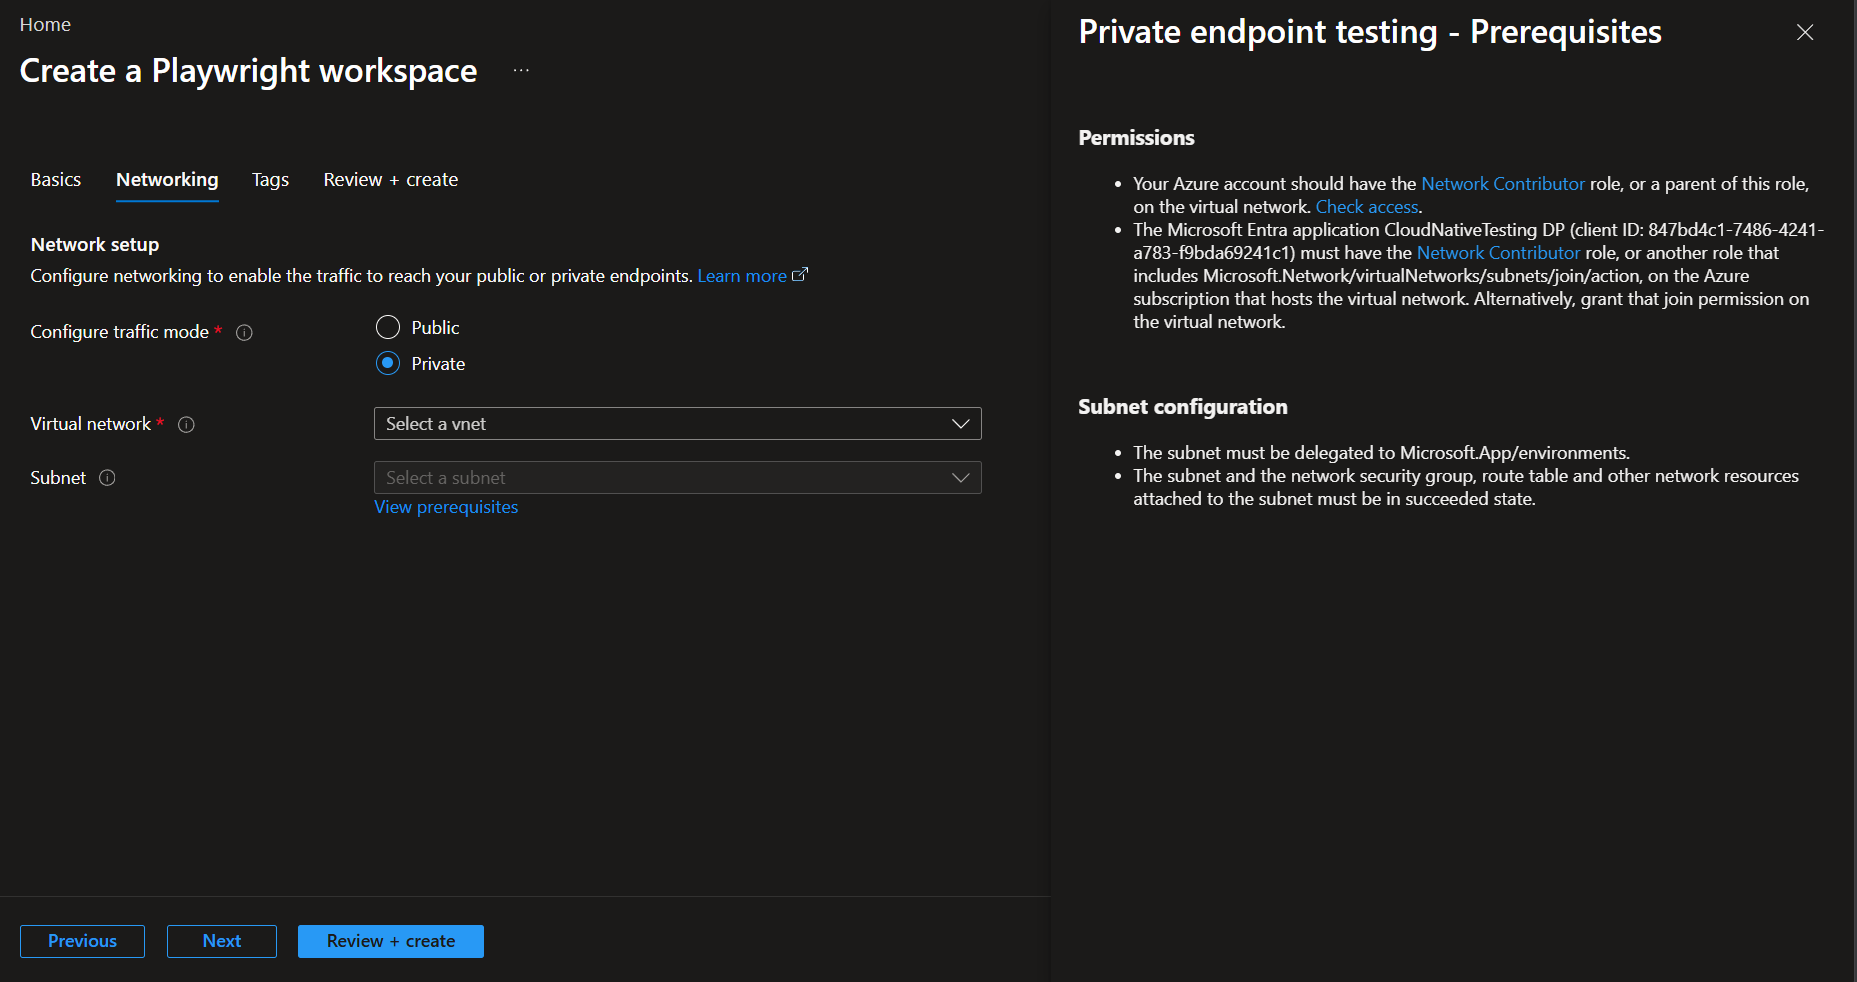
}Many of the most valuable enterprise workflows run on applications that aren’t on the public internet, such as internal portals, admin consoles and line-of-business systems. With VNet injection, now in preview, you can link your own virtual network and subnet directly to your Playwright Workspace. Cloud browsers can then reach applications and endpoints hosted inside that private network. The integration uses a dedicated delegated subnet, so you can set network boundaries and control browser egress with the networking policies you already apply to the subnet. Your agents can automate private applications while network access stays within your organization’s security requirements.
Enterprises often need precise control over how browser traffic leaves their environment. With browser proxy, now in preview, you can bring your own proxy and route cloud-browser traffic through your existing proxy infrastructure to meet your organization’s access-control requirements. Configurable proxy pools support domain-based routing, so traffic can go through different proxies depending on the destination. Proxy credentials are handled through Azure Key Vault and managed identities, which keeps secrets out of your automation code. You can easily set priorities for your proxies too. When a request matches more than one rule, the rule with highest priority decides which proxy handles it, so routing stays predictable even as your rules grow. Together, these features give you greater control over how your agents’ browsers connect to the web.
az rest --method put \
  --url "<api-base-endpoint>/proxy-configs/<config-id>?api-version=2026-11-01-preview" \
  --resource "https://management.core.windows.net/" \
  --body '{
    "name": "my-proxy-config",
    "description": "Corporate and EU routing",
    "keyVaultReferenceIdentity": {
      "type": "UserAssigned",
      "resourceId": "/subscriptions/<subscription-id>/resourceGroups/<resource-group>/providers/Microsoft.ManagedIdentity/userAssignedIdentities/<identity-name>"
    },
    "proxyPool": {
      "default-proxy": {
        "server": "http://your-default-proxy-hostname:8080"
      },
      "eu-route": {
        "server": "http://your-eu-proxy-hostname:8080",
        "pattern": ["*.eu.company.com", "eu.company.com"],
        "priority": 1,
        "credentials": {
          "usernameSecretUri": "https://<vault-name>.vault.azure.net/secrets/eu-proxy-username",
          "passwordSecretUri": "https://<vault-name>.vault.azure.net/secrets/eu-proxy-password"
        }
      },
      "corp-route": {
        "server": "http://your-corp-proxy-hostname:8080",
        "pattern": ["*.company.com", "company.com"],
        "priority": 2
      }
    },
    "bypass": ["status.company.com", "*.blob.core.windows.net"]
}'Long-running and repeated workflows shouldn’t have to sign in from scratch every time. With profile reuse, now in preview, browser profiles keep authentication, cookies and browser state between sessions, so agents skip repeated logins and setup steps. This makes multistep and long-running workflows faster. Profiles are kept in encrypted storage and governed by workspace-level role-based access control, so only authorized identities can use a saved browser state.
az rest --method patch \
--resource "https://management.core.windows.net/" \
--url "https://<region>.api.playwright.microsoft.com/playwrightworkspaces/<workspaceId>/browser-sessions/<saveSessionId>?api-version=2026-12-01-preview" \
--headers "Content-Type=application/merge-patch+json" "x-ms-mcp-call=true" \
--body '{
    "browserType": "Chromium",
    "operatingSystem": "Linux",
    "protocol": "MCP",
    "browserProfile": {
      "id": "<profileId>",
      "saveChanges": true
    }
  }'
Agents often need credentials to sign in to the websites they automate, and those credentials should never reach the model or your application code. With secret management, now in preview, you keep secrets in your own Azure Key Vault and pass them directly to the browser. The secret is read on the server side, inside the Playwright Workspaces remote MCP server, so neither your application code nor the model ever receives the value. You can bind each secret to a domain allowlist, which stops a malicious site from capturing it. Secret URIs are versionless, so when you rotate a secret in Key Vault, the change is picked up automatically.
Many public websites are protected by CAPTCHAs and web application firewalls that block automated traffic. Our focus is secure, responsible, enterprise-grade automation, not getting around a website’s security controls.
Web bot Auth (based on IETF draft) enables AI agents to cryptographically sign their HTTP requests which can help in verifying the agent’s identity for public website research tasks. We are enabling Web Bot Auth for customers by primarily 2 methods – customer self-registration OR Microsoft platform registration (via selected bot management providers like Akamai, Cloudflare, and F5). Complete this form to express interest in Microsoft platform registration.
PATCH
https://management.azure.com/subscriptions/{subscriptionId}/resourceGroups/{resourceGroupName}/providers/Microsoft.LoadTestService/playwrightWorkspaces/{workspaceName}?api-version=2026-11-10-preview
Authorization: Bearer {{AAD Token}}
Content-Type: application/json

{
  "properties": {
    "webBotAuth": {
      "status": "Enabled",
      "signingKey": "Workspace"
    }
  }
}To get started, create a Playwright Workspace, connect Browser automation tool to a toolbox in Microsoft Foundry, and add the toolbox to your agent. Then enable the capabilities your scenario needs. Preview capabilities are subject to change, so review their documentation before using them in production. These resources will help:
With these capabilities, your agents can reach private applications, use your network’s controls, sign in safely, carry state between sessions, and leave a full audit trail.
The post Browser Automation Tool in Microsoft Foundry : Ignite’26 Announcements appeared first on Microsoft Foundry Blog.
Your next agent can start wherever you like to build: in your editor, at the terminal, or with your favorite coding agent. At Microsoft Ignite, we’re making that first step easier: the Foundry Dev Pack (aka.ms/foundrydevpack) is now generally available, bringing the Microsoft Foundry developer tools to your machine in a single install. Move from setup to building, debugging, evaluating, and deploying agents in the environment you already know.
The Dev Pack combines the Foundry CLI (azd ai) and Microsoft Foundry Skill, and installs the Foundry Toolkit for VS Code and Foundry plugin for the GitHub Copilot app when those apps are present. It builds on a major milestone from November 5: the Foundry CLI reached general availability. Together, these tools give you more ways to move from an idea to an agent you can test and ship more efficiently.
With a single command, the Foundry Dev Pack sets up your development environment so you can start building Foundry agents wherever you prefer to work.
| Tool | Where you work | Best for |
|---|---|---|
| Foundry Toolkit for VS Code | Editor | A visual, repository-centered workflow with familiar VS Code debugging |
Foundry CLI (azd ai) |
Terminal, scripts, CI/CD | CLI-focused developers, platform engineers, and teams automating deployment |
| Foundry plugin for the GitHub Copilot app | Desktop app | Guided design choices without losing access to the generated code |
| Microsoft Foundry Skill | Any compatible coding agent | Developers using GitHub Copilot, Claude Code, Cursor, or another compatible coding agent |
Mix and match as you build. The tools share project files, so you can scaffold in one, debug in another, and deploy from whichever environment fits your workflow.
Keep your agent-building loop moving without leaving the editor. The Foundry Toolkit for VS Code brings together the richest feature set of the developer tools with a visual workflow and tight GitHub Copilot integration.

Learn more in the Foundry Toolkit documentation.
azd ai)
Prefer the terminal? The Foundry CLI turns agent development and deployment into repeatable commands and project configuration in azure.yaml. Take the same workflow from your laptop to scripts and CI/CD pipelines, and customize infrastructure with Bicep or Terraform when you need to. Target environments and cost-bearing actions stay explicit and reviewable.
Here’s the inner loop with the basic Python Agent Framework sample. Before you begin, install Azure Developer CLI 1.37.0 or later, a current uv release, and Python 3.13 or later.
azd auth login

# Scaffold the sample into an empty folder, then review the source and azure.yaml
azd ai agent init \
  --template https://github.com/microsoft-foundry/foundry-samples/blob/main/samples/python/hosted-agents/agent-framework/responses/01-basic/azure.yaml \
  --deploy-mode code \
  --src .

# Confirm tenant, subscription, project, region, model, and quota
azd provision

# Run and invoke locally
azd ai agent run
azd ai agent invoke --local "Write a haiku about deploying cloud applications."

# Deploy from the same project
azd deploy
From there, azd ai agent monitor --follow streams logs, azd ai agent doctor diagnoses setup and permission issues, and azd pipeline config sets up GitHub Actions or Azure DevOps. For the full walkthrough, including evaluations and CI/CD, read the azd ai GA announcement.
Turn an idea into a project you can inspect and shape. In the GitHub Copilot app, Microsoft Foundry Canvas opens a guided, project-aware experience alongside your chat:
Your choices produce code and configuration that you can inspect and edit.

Learn more about Microsoft Foundry Canvas.
Bring Foundry expertise to the coding agent you already use. The Microsoft Foundry Skill provides reusable workflows for creating, deploying, evaluating, and troubleshooting Foundry agents across compatible hosts, including GitHub Copilot, Claude Code, Cursor, and other coding-agent hosts.
The skill guides coding agents to use tools such as az, azd, MCP tools, and your repository scripts when needed. With Foundry-specific knowledge and deterministic command-line workflows built in, the skill helps agents avoid broad web searches and repeated trial and error—so they can make progress with fewer tokens and faster iteration. You stay in control: review the agent’s plans, file changes, commands, and cost-bearing actions before they run.
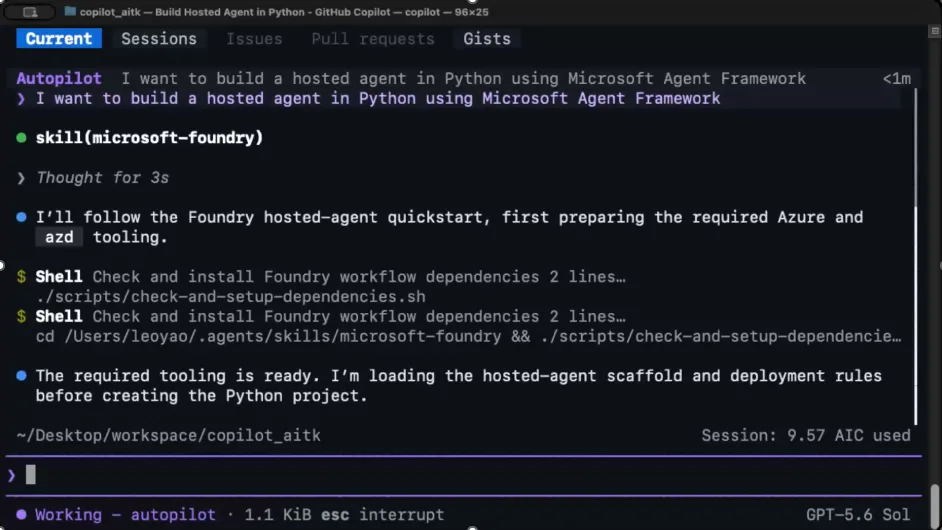
Learn more: Microsoft Foundry Skill documentation
Ready to get your machine set up? The Foundry Dev Pack is the recommended, repeatable way to prepare for Microsoft Foundry. One install brings in the tools you need:
azd ai)
Install for your operating system:
Windows
winget install Microsoft.FoundryDevPack
macOS
brew install --cask microsoft/foundry/devpack && foundry-devpack install
Linux
curl -fsSL https://aka.ms/foundry-devpack-install.sh | bash
You can use the Dev Pack’s install commands in onboarding docs, dev containers, and machine setup scripts so your team can get started with a consistent toolset.
Install the Foundry Dev Pack, then follow the hosted-agent quickstart to take an agent from project setup through local testing and deployment. Prefer to see the tools in action first? Check out these Microsoft Ignite sessions:
The post The Foundry Dev Pack is here: build Foundry agents your way appeared first on Microsoft Foundry Blog.
Your customers don’t judge agents by how well they demo. They judge them by whether the work gets done: the case resolved, the report delivered, the follow-up sent. That takes more than a model. It takes the right context and tools, a runtime that holds up under real demand, and a way to keep improving once real users put agents to work. At Ignite 2026, Foundry Agent Service delivers new capabilities to get you there across the agent lifecycle: Build, Deploy, and Operate.
Build more capable agents faster with the managed Microsoft Copilot harness, real-time voice, and richer tool connections. Deploy them at scale with enterprise controls, and bring them into Microsoft 365 where people already work. Operate them with confidence by turning production evidence into validated improvements. Here’s what’s new, and how each capability helps you move from idea to impact.
The Microsoft Copilot harness, in public preview, gives developers a fully managed way to build prompt agents that reason, use tools, and complete complex, long-running tasks. Microsoft runs the agent loop and sandbox; you bring the knowledge, reusable skills, and connected tools that make the agent yours. Instead of rebuilding execution machinery, your team can focus on the agent’s expertise and results.
Author Copilot harness agents in the Foundry UI, the GitHub Copilot app, the Foundry CLI (azd ai), or the Foundry Toolkit for VS Code, and keep agent definitions in source control alongside your application code. [Read what’s new in Foundry dev tools →]
You can choose the right starting point for your application: author a prompt agent using the Microsoft Copilot harness, or bring your own code and orchestration through hosted agents. Foundry Agent Service supports those choices without requiring every team to use the same framework or take the same approach to agent logic.
Talking to AI should feel as natural as talking to a person. Voice agents in Foundry Agent Service are now generally available, giving organizations an enterprise-grade way to add real-time voice to their agents. That covers serving customers, supporting employees, and powering in-car and in-app assistants.
Thousands of customers have adopted voice agents since public preview, across customer service, automotive, education, HR and public services. [Read what’s new in Azure Speech in Foundry Tools→]
At Ignite, we’re expanding how Foundry agents connect to tools, business context, and other agents. Work IQ and Fabric IQ integrations, in preview, bring Microsoft 365 context and Fabric data into agent workflows. Web Search powered by Web IQ is generally available for prompt agents, with Toolbox support coming soon, while the generally available A2A tool connects Foundry and external agents. Toolboxes make these capabilities reusable through a managed MCP endpoint, with expanded skills support, a monitoring dashboard, and preview tool policies.
Computer use and browser automation are now generally available for tasks that require an application interface rather than an API. Browser automation combines isolated browser sessions with Live View and Take control for human oversight, session recordings in customer-owned storage, and preview access to applications behind private virtual networks. [Read what’s new in tools and toolboxes in Foundry →]
Hosted agents let you bring your application code and orchestration to a managed runtime. At Ignite, we’re expanding scale, enterprise controls, and deployment choice:
[Read what’s new in hosted agents →]
One powerful publishing pattern is creating autonomous, always-on agents in Microsoft 365. Supported hosted agents get their own Entra Agent ID, email address, Microsoft Teams presence, and place in the org chart, so they can start conversations, work on shared files, and follow up on action items alongside people.
Foundry is integrating with Microsoft 365 Resources for Agents, which equips supported agents with their own secured Microsoft 365 resources, including a standalone mailbox, calendar, and OneDrive workspace for file storage. These capabilities will be made available to supported agents across the Microsoft portfolio.
The result: agents that work where people already collaborate, while administrators keep control of access and availability through Microsoft Entra and Agent 365, subject to tenant controls.
Production readiness means understanding how agents behave after deployment, and using that evidence to improve them. At Ignite, we’re connecting production insights, expert feedback, and optimization through continuous improvement in Foundry:
Every improvement should be validated before release and monitored afterward. For the full continuous improvement story, see Tina Schuchman’s blog.
“For us, agent quality is paramount and must be measurable. We can now connect tracing and evaluation so we can diagnose failures, measure quality against expert-validated answers, and continuously improve the agent. Data protection is equally fundamental: session isolation and private networking provide key controls. Together, these capabilities give us a more systematic way to keep improving the agent based on our in-house intelligence while leveraging our existing strong data controls.”
— Rasmus S Andersen, Associate Director, Products and AI, FounData, Novo
Whether you are authoring a harness agent with the Foundry CLI (azd ai) or the Foundry Toolkit for VS Code, scaling a hosted application, or improving an agent already in production, these updates expand what you can do with Foundry Agent Service. Start with the authoring and deployment path that fits your application, connect the tools it needs, and use production evidence to guide what comes next.
If you’re attending Microsoft Ignite 2026, or watching on-demand content later, be sure to check out these sessions:
The post What’s new in Foundry Agent Service at Ignite 2026 appeared first on Microsoft Foundry Blog.

