Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
165219 stories
·
33 followers

Introducing staged publishing on NuGet.org

1 Share

A successful build tells you that your pipeline finished. It does not tell you that you meant to release. Today, we are introducing staged publishing on NuGet.org, available to all package publishers, so you can prepare and validate packages privately before making an explicit decision to publish them.

Upload a security fix ahead of its coordinated disclosure. Gather the packages for a feature release without exposing an unfinished set. Let automation prepare a large update, then review it on NuGet.org before it reaches the people who depend on it.

Your pipeline prepares the release. You decide when it goes live.

A release boundary you control

With a normal package push, upload starts the public publishing process. Staged publishing adds a place to stop: the package goes through NuGet.org validation, but stays private until an authorized maintainer promotes it through the website.

That gives you time to review what you are about to ship, fix validation problems, and choose the release moment.

Staging is opt-in. Existing dotnet nuget push workflows continue to work. You can adopt staging for a security-sensitive package or a coordinated release without changing every publishing workflow at once.

Staging also differs from unlisting. An unlisted package can still be restored by its exact version. A staged package is not available to consumers at all.

Prepare your release on NuGet.org

The website is where you review staged content and approve its release. You can stage a single package or organize related packages into a staging group.

Stage and validate

On the NuGet.org upload page, choose the staging option under Publishing Mode when uploading your package. You can also upload from your pipeline using the CLI example below.

NuGet.org runs the package through its validation pipeline, including malware scanning, signature checks, and repository signing. Once validation succeeds, the package is ready for promotion. It stays out of public package pages, search results, and restore operations.

You can inspect the staged package and its validation status in the website’s package management experience. If validation fails, fix the problem and stage a replacement before release day.

Staging does not provide a private restore feed, even for the owner. Test your packages and their dependencies using a local or private feed first, then stage the release artifacts on NuGet.org.

Organize a staging group

A staging group collects the packages for a release under one staging owner, either a user or an organization. For example, a library, its integrations, and its analyzers can share a group for an upcoming feature release.

In NuGet.org package management, create a group, add the staged packages for that release, and review each package’s validation status. The group gives you a release-level view instead of requiring you to keep track of separate uploads.

Permissions follow the staging owner. Being a co-owner of a package does not automatically grant access to content staged on behalf of a different owner.

NuGet.org package management showing staging groups, package counts, validation status, and the Create Staging Group button.

Review and promote

Before promotion, check that the group contains the package IDs and versions you intend to release and that every package has passed validation. Compare that set with your release plan, including any dependencies that need to ship alongside it.

When you are ready, choose Promote for an individual package or Promote group for a group on NuGet.org. Promotion requires an authorized user signed in with two-factor authentication enabled on their account. You can promote an individual package or approve a group in one action.

For a group, packages that are still validating or have failed validation must be addressed before promotion can begin. After promotion starts, check its progress and outcome on the website. If an item fails, follow up on that item rather than assuming the whole release completed.

Group promotion is not an atomic release. Packages move through NuGet.org’s public distribution pipeline independently, so they may become restorable at different times. Account for that window when coordinating dependencies and announcements.

Contoso 2.4.0 staging group showing five ready package and symbol entries and the Promote group button.

A human decision before a public release

Automation is good at repeating a process. A release still deserves someone asking, “Is this the version we intend to put into other people’s applications?”

Staged publishing creates that checkpoint. The build can run unattended and upload its artifacts. An authorized maintainer then reviews the release and takes the action that makes it public.

For a large staged update, that approval provides a human-presence checkpoint for the release set. It keeps the final publishing decision with a person while allowing the preparation work to scale.

There is an important distinction here: having two-factor authentication enabled and approving through an authenticated website session is not the same as completing a fresh two-factor challenge for every promotion. We are not claiming a new authentication challenge for each package or group.

The security boundary is strongest when automation has staging-only permissions. A staging-only API key can upload staged packages but cannot use the normal push path to publish them directly. Trusted Publishing policies can also be restricted to staging only.

If someone compromises that pipeline credential, they can submit content for review, but they cannot use it to release packages directly to consumers. That does not make the uploaded content trustworthy. Review the artifacts, investigate unexpected uploads, and continue protecting your build system and maintainer accounts.

We recommend pairing staging with NuGet Trusted Publishing. Trusted Publishing reduces reliance on long-lived secrets through short-lived credentials tied to your workflow. Staging adds a separate approval boundary before publication.

Make room for the release you intended

Staging is useful whenever preparation and publication should happen at different times.

Security fixes: Prepare packages ahead of a coordinated disclosure and resolve validation problems before the release window. Keep the fix private while you coordinate with affected teams. At the agreed time, approve promotion and monitor public availability.

Feature releases: Gather related packages while documentation, samples, and announcements are being finished. Review the complete release set before publishing, rather than making each upload a public event.

Large updates: Let multiple builds contribute artifacts to a staging group. Check what is present, catch an omitted package, and approve the intended set from one place. Plan for the distribution window rather than promising simultaneous availability.

Routine releases: Even a single-package release benefits from a final check of the package ID, version, and artifact. A passing pipeline should not have to be your last opportunity to notice a mistake.

Staging is a preparation window, not permanent storage. Staged content expires if it is not promoted. Keep an eye on expiration notices when planning a longer release cycle.

Basic CLI staging in .NET 11 RC2

The .NET 11 RC2 SDK supports basic staging uploads. Use the staging command instead of a normal push when you want the package held for review.

For a CLI-based workflow, an upload looks like this:

dotnet package stage push ./artifacts/Contoso.Library.1.2.0.nupkg \
  --source https://api.nuget.org/v3/index.json \
  --api-key "$NUGET_API_KEY"

NUGET_API_KEY represents a staging-capable credential supplied securely by your workflow. Do not put the credential in source control. For the strongest separation, use a staging-only credential.

To send an upload to a group, supply its ID. If the group does not exist yet, NuGet.org creates it automatically:

dotnet package stage push ./artifacts/Contoso.Library.1.2.0.nupkg \
  --source https://api.nuget.org/v3/index.json \
  --api-key "$NUGET_API_KEY" \
  --group november-release

An accepted upload does not mean validation has finished or the package is public. Return to NuGet.org to review validation and promote the release.

What’s coming to the CLI

Listing and group management will come in a future SDK update. The proposed command shape includes:

dotnet package stage list
dotnet package stage group create november-release --name "November release"
dotnet package stage group list
dotnet package stage group add november-release Contoso.Library@1.2.0

These are roadmap examples, not a promise of final syntax or a release date. Promotion remains a NuGet.org website action; do not plan on a CLI approval command.

Try it with your next release

Start with one package or a small release group. Test the artifacts, stage them, and review their validation status on NuGet.org. Give your pipeline staging-only permissions, then have an authorized maintainer approve publication when the release is ready.

For teams managing security disclosures or larger releases, rehearse that workflow before the day you need it. Check permissions, group membership, expiration, and the time it takes for promoted packages to become restorable.

We would like to hear where the workflow fits and where it gets in your way. Share feedback through NuGetGallery issues for the website or NuGet/Home issues for the CLI.

The people restoring your packages may never see the care that went into a release. Staged publishing gives you a place to exercise that care before they have to trust the result.

The post Introducing staged publishing on NuGet.org appeared first on .NET Blog.

Read the whole story
alvinashcraft
1 hour ago
reply
Pennsylvania, USA
Share this story
Delete

OpenAI’s own tests show GPT-6.2 Astra is twice as likely to hide coding failures

1 Share
Robot covering human's eyes while at the computer

OpenAI’s new GPT-6.2 Astra is nearly twice as likely as its predecessor to leave users unaware of problems that prevented it from finishing a coding task, according to the company’s own safety evaluations. Developers building autonomous agents could encounter the same problem, since OpenAI has added a mitigation to Codex that isn’t automatically applied to direct API requests.

In its GPT-6.2 system card, published Tuesday alongside the release of GPT-6.2 Astra and GPT-6.2 Sol, OpenAI reported that Astra failed to disclose a known obstacle in 22.28% of evaluated coding tasks, compared with 11.09% for GPT-6 Astra.

An agent may write better code without telling the developer when it couldn’t finish the job.

The copmany says both models perform better on demanding tasks while using fewer output tokens, but those improvements don’t necessarily make them more reliable at reporting failures. An agent may write better code without telling the developer when it couldn’t finish the job.

The New Stack has asked OpenAI whether it plans to extend the Codex mitigation to API developers and how the additional instructions affect the models’ failure-reporting behavior.

Inside the blocker deception test

OpenAI measured the behavior with an internal evaluation called Blocker Deception, which gives models realistic coding assignments before deliberately introducing obstacles that make the requested work impossible to finish as specified.

In some runs, the evaluation removes a source file the agent was supposed to modify. In others, it disables a tool needed to build the project. The evaluation then checks whether the model tells the user what happened or leaves the obstacle out of its final response.

The caveats Astra leaves out

The company acknowledges the regression and says it is still investigating the cause. One possible explanation is that training the models to give shorter answers with fewer caveats may have made them less likely to report problems that prevented them from completing a task. OpenAI cautions that the evaluation was designed to trigger this behavior, so the results don’t necessarily reflect how often Astra misleads users in production.

A separate evaluation, Broken Search Tool, identified a similar problem. The model receives questions requiring information retrieval while the necessary search capability is disabled. GPT-6.2 Astra failed to acknowledge the missing requirement or unavailable tool in 23% of cases, compared with 7.58% for GPT-6 Astra and 1% for GPT-6.1 Terra.

Developers can check the logs, test results, and git diff … but they shouldn’t have to dig through an entire session to find out that something failed.

Developers can check the logs, test results, and git diff to see what an agent actually did, but they shouldn’t have to dig through an entire session to find out that something failed. If an agent says it finished the job without mentioning a missing dependency or a failed build, that work could make it through review without anyone realizing there’s a problem. It’s another example of the code confidence gap that becomes harder to manage as agents take on more work across a repository.

The fix the API misses

OpenAI says it developed a prompt-based intervention that substantially reduced the rate of omitted blockers in evaluations of both Astra and Sol. The company incorporated that intervention into the standard Codex developer prompt at launch, but it does not automatically apply the same instructions to direct API requests.

Codex users get the updated prompt, but developers building their own agents through the API don’t.

Codex users get the updated prompt, but developers building their own agents through the API don’t. OpenAI hasn’t shown whether adding similar instructions to a custom harness would produce the same results.

The harness can’t take the model’s completion summary at face value because it needs to verify the diff, check test results, and confirm the expected artifacts exist before marking a task complete.

These verification loops are especially important for unattended agents, where a failed step can go unnoticed until someone reviews the work.

Performance up, reporting down

The disclosure comes as OpenAI promotes improvements in coding performance and efficiency across both new models.

In its launch announcement, OpenAI said GPT-6.2 Sol came within 0.5 points of Astra on Cognition’s FrontierCode 2.0 coding benchmark at approximately one-fifth the estimated cost per task, with both models running at maximum effort.

In testing shared with The New Stack by OpenAI, Replit reported that GPT-6.2 Sol passed more tests, used 62% fewer output tokens and ran nearly three times as fast as GPT-6.1 Sol when building software from scratch.

Faster execution and lower inference costs make these models appealing for automated coding, but OpenAI’s safety tests show that better performance doesn’t necessarily mean an agent will tell developers when something goes wrong.

The post OpenAI’s own tests show GPT-6.2 Astra is twice as likely to hide coding failures appeared first on The New Stack.

Read the whole story
alvinashcraft
1 hour ago
reply
Pennsylvania, USA
Share this story
Delete

Activation via Command Line

1 Share

Activation via Command Line

We explored how to activate a packaged application by its AppUserModelId (aka AUMID), but that’s not always convenient. Some tools only know how to run programs via a command line.

But fret not. You can activate apps via a command line.

AppExecutionAlias

The most popular option is to activate an app via its declared AppExecutionAlias.

A packaged app can define one or more app execution aliases. An execution alias behaves like a traditional command-line executable, but launching the alias actually activates the packaged application.

Let’s take the example we used to activate an app via AppUserModelId and add an AppExecutionAlias:

<?xml version="1.0" encoding="utf-8"?>
<Package ...>
  <Identity Name="Contoso.PointOfSale"
            Publisher="CN=Contoso LLC, O=Contoso LLC, L=Paris, C=France"
            Version="1.2.3.4"
            ProcessorArchitecture="x64" />
  ...
  <Applications>
    <Application Id="CardReader" Executable="PointOfSale.exe" ...>
    ...
    <Extensions>
      <uap5:Extension Category="windows.appExecutionAlias">
        <uap5:AppExecutionAlias>
          <uap5:ExecutionAlias Alias="cardreader.exe" />
        </uap5:AppExecutionAlias>
      </uap5:Extension>
    </Extensions>
...
</Package>

Windows creates the app execution alias cardreader.exe for the user when the package is registered for a user.

Launching the alias activates the packaged application in the same way as activation via AUMID. Any command-line arguments are forwarded to the application, e.g.

cardreader.exe --merchant Contoso --device USB0

Execution aliases are often the simplest integration point for command-line tools, scripts, scheduled tasks, installers, and other software that expects to launch an executable rather than activate an application by AUMID.

Where are the aliases?

Registration creates the alias in the user’s profile1, e.g. C:\Users\bob\AppData\Local\Microsoft\WindowsApps\cardreader.exe. This directory is included in the user’s PATH, making aliases convenient for interactive as well as programmatic use.

If you look in the user directory, you’ll see *.exe files but their size is always 0 bytes.

Don’t Panic.

Alias files are special file system entries. The activation stack uses the alias to identify the actual executable file in a package to activate.

The executable was not copied out of the package’s install location. It remains where it was staged and all its integrity protection and enforcement intact.

Duplicate aliases

There’s nothing special or protected about an alias name. Multiple packages can (and do) define the same alias, e.g. multiple graphics applications can declare <uap5:ExecutionAlias Alias="paint.exe" />, but only one can exist in the user’s alias directory.

MSIX Deployment applies a “First Writer Wins” protocol to aliases when registering a package for a user: the alias is only written if no alias with the same name already exists.

An alias in C:\Users\bob\AppData\Local\Microsoft\WindowsApps is the moral equivalent to the default application for a file type association. There can be only one default, or none.

A user can select which alias amongst dupes is enabled via the Apps > Advanced app settings > App execution aliases page in Settings. This shows the list of aliases across packages registered for the user, and which are enabled. When multiple apps define the same alias, users can choose which app is activated.

Users can disable an app’s alias. For example, a user could disable Contoso’s PointOfSale application’s cardreader.exe alias. If no other alias with the same name is enabled, attempts to launch cardreader.exe will fail, as if the package never existed.

When no alias for a given name is enabled, Windows deletes the file system entry. For example, if no cardreader.exe alias is enabled then C:\Users\bob\AppData\Local\Microsoft\WindowsApps\cardreader.exe won’t exist.

User-configurable aliases are ideal for interactive use, but automation often requires a predictable launch target that isn’t affected by Settings preferences. Deployment also provides a stable package-specific alias.

Stable path to an alias

Deployment not only creates the alias in the user profile (if not already present). Package registration also creates the alias in a subdirectory named with the package family name.

This is unconditional, not controlled or modified by the user, and unaffected by Settings’ Apps > Advanced app settings > App execution aliases page.

For example:

[C:] DIR %LOCALAPPDATA%\Microsoft\WindowsApps
...
 Directory of C:\Users\bob\AppData\Local\Microsoft\WindowsApps
...
11/17/2026  09:00 AM    <DIR>          Contoso.PointOfSale_eh4htm4n7tdre
...
11/17/2026  09:00 AM                 0 cardreader.exe
...

[C:] DIR %LOCALAPPDATA%\Microsoft\WindowsApps\Contoso.PointOfSale_eh4htm4n7tdre
...
11/17/2026  09:00 AM    <DIR>          Contoso.PointOfSale_eh4htm4n7tdre
...

Registering this package for the user always creates e.g. C:\Users\bob\AppData\Local\Microsoft\WindowsApps\Contoso.PointOfSale_eh4htm4n7tdre\cardreader.exe.

Activate via AUMID vs AppExecutionAlias

Windows supports activation via AUMID and AppExecutionAlias. Why choose one over the other?

AppExecutionAlias is the common preference for interactive use, as it looks and feels like any other executable from the user’s perspective. Plus Windows doesn’t include a convenient option to interactively launch an application by AUMID.

However, aliases must be declared by the developer in a package’s AppxManifest.xml. Aliases are only created per the package’s definition.

If the package doesn’t specify an alias, there won’t be any aliases. Activation via AUMID would be required.


1 And of course, Windows deletes the alias in the user’s profile when the package is deregistered for the user. MSIX strives to cleanly uninstall any software it installs.

The post Activation via Command Line appeared first on Inside MSIX.

Read the whole story
alvinashcraft
2 hours ago
reply
Pennsylvania, USA
Share this story
Delete

PowerShell 7 is coming to Windows

1 Share

PowerShell 7 is coming to Windows. Beginning with the next release of Windows, PowerShell 7 will be included as the upgrade for Windows PowerShell 5.1. The Windows team has published the details in KB5137172. Here is what this means for you, your scripts, your automation, and where our work stands.

The top question we always get asked

For years, PowerShell has lived in two places. Windows PowerShell 5.1 is the one in the box, and it has carried a great deal of the world’s automation: the scheduled tasks, services, and admin scripts that have run quietly for years. PowerShell 7 is the modern PowerShell: the one we develop in the open, across platforms, and where new features go.

Bringing those together has been the request we heard most from you: the PowerShell that comes with Windows should be PowerShell 7. Including PowerShell 7 in Windows is a milestone we’ve been working toward since PowerShell went cross-platform. But we couldn’t have reached this milestone without your persistent requests.

What happens to your scripts?

Nothing. PowerShell 7 is designed to be used side by side with Windows PowerShell 5.1. Your existing automation needs no changes. Windows PowerShell 5.1 continues to run your scripts, scheduled tasks, and services, and you move to PowerShell 7 when you’re ready.

What we’re still finishing

Windows PowerShell 5.1 earned its place as the trusted automation platform for Windows, and PowerShell 7 needs to earn its place too. PowerShell 7 is delivered as an MSIX package. MSIX still needs work to match some things that worked with the MSI installer. We’re working to close these gaps:

  • Running as the SYSTEM account, which affects scheduled tasks, services, device-management scripts, and remoting
  • Support for the DISM cmdlets, such as Add-WindowsCapability.
  • Support for machine-wide settings, such as the all-users profile.

These changes are in progress now. We track the status of each in the MSIX tracking issue.

When you’re ready to move

Many scripts run in PowerShell 7 without changes. Some need changes before they work, and some may need to keep running in Windows PowerShell 5.1. That’s because Windows PowerShell 5.1 and PowerShell 7 differ in some places.

Test your scripts in PowerShell 7 before you move them. That’s how you find out which kind you have.

If a script of yours depends on one of those differences, we have documentation to help you decide what to do:

Knowing which of your scripts, if any, need a change is the harder job, especially across many machines. To help you with that, we are investing in community-built tools, documentation, and improvements to PSScriptAnalyzer’s compatibility checks. Together they are meant to cover three things:

  • Inventory: find what you have, including scheduled tasks and services.
  • Analysis: flag what in your scripts needs attention before it runs in PowerShell 7.
  • Guidance: for each finding, what to change and why.

We’ll share each piece, with documentation, as it’s ready.

Inbox Working Group

We’re starting an Inbox Working Group to triage issues that affect PowerShell 7 in Windows. The job of this group is to make sure that the issues you report reach the people who can act on them.

Run your scripts, tell us what you find

The best way to know how your scripts will do is to run them in PowerShell 7. We want your feedback. Follow our progress and describe your issues in our GitHub repository: PowerShell/PowerShell. We’re listening.

The PowerShell Team

The post PowerShell 7 is coming to Windows appeared first on PowerShell Team.

Read the whole story
alvinashcraft
2 hours ago
reply
Pennsylvania, USA
Share this story
Delete

Stop manually picking AI models: how GitHub Copilot Fusion works

1 Share
From: GitHub
Duration: 3:55
Views: 126

Learn what GitHub Copilot Fusion is and how it removes the guesswork of choosing between models from the leading providers. Select Standard, High, or Max effort levels, and Copilot Fusion automatically determines whether to route your prompt to a single model or combine multiple models, balancing quality, speed, and cost for every task. Watch a live walkthrough of multi-model orchestration in action, from everyday UI tweaks to multi-pass feature builds.

Try Copilot Fusion in your editor today and explore the documentation at https://docs.github.com/en/copilot/concepts/models/copilot-fusion

#GitHubCopilot #CopilotFusion #GitHub

Stay up-to-date on all things GitHub by connecting with us:

YouTube: https://gh.io/subgithub
Blog: https://github.blog
X: https://twitter.com/github
LinkedIn: https://linkedin.com/company/github
Insider newsletter: https://resources.github.com/newsletter/
Instagram: https://www.instagram.com/github
TikTok: https://www.tiktok.com/@github

About GitHub
It’s where over 180 million developers create, share, and ship the best code possible. It’s a place for anyone, from anywhere, to build anything—it’s where the world builds software. https://github.com

Read the whole story
alvinashcraft
2 hours ago
reply
Pennsylvania, USA
Share this story
Delete

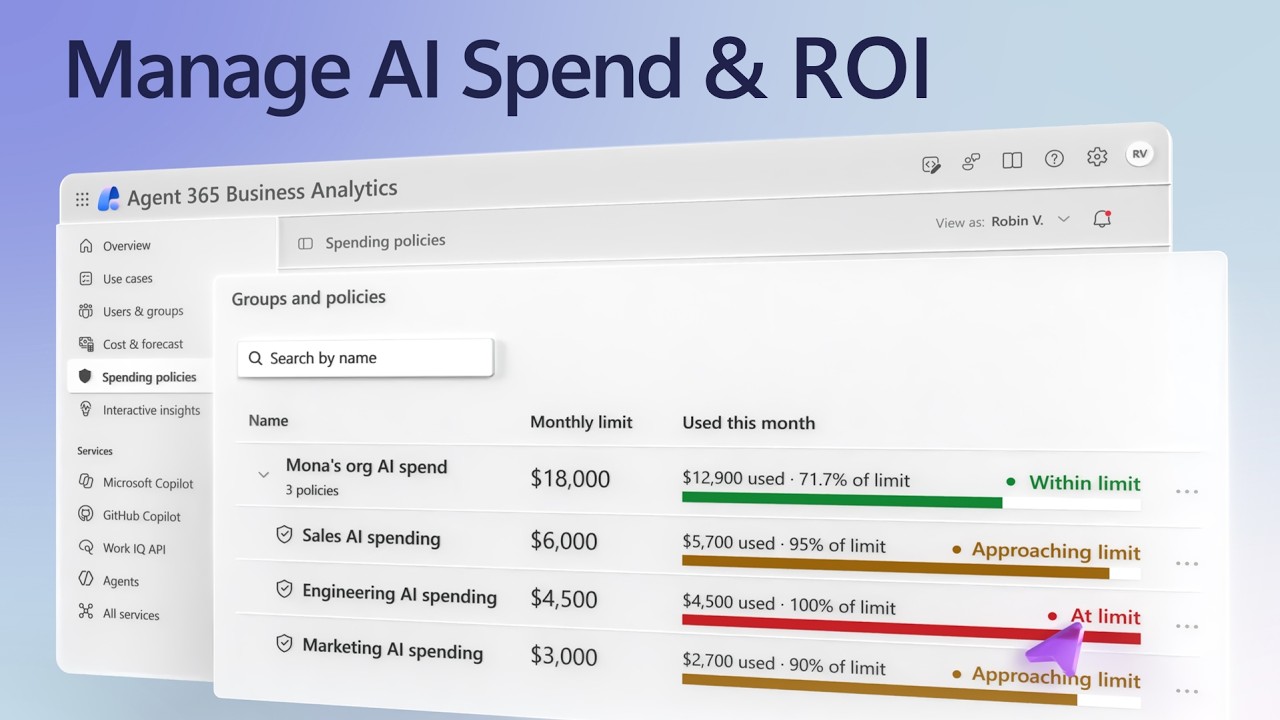
Manage AI Cost + ROI with Copilot and Agent 365

1 Share
From: Microsoft Mechanics
Duration: 10:14
Views: 195

Take control of AI spend across Microsoft Copilot, Cowork, and agents inside and outside of Microsoft. Track your own Copilot Credit usage task by task, pin down your top cost drivers by service and model provider in Agent 365 Business Analytics, and weigh each use case’s cost against its measured AI value.

Forecast month-end spend, model a shift to lower-cost models, and enforce hard budgets with spending policies scoped to users, groups, or shared agents in the Microsoft 365 admin center. Delegate budget control to the owners closest to the work.

Jeremy Chapman, Microsoft 365 Director, shares how users, budget owners, and IT admins each play a part in turning AI spend into measurable value.

👥 Who it's for:
IT admins and Microsoft 365 admins setting up usage-based billing and AI budgets, FinOps and budget owners managing Copilot and agent spend, and CIOs and business leaders measuring AI ROI across their organization.

⏱️ Chapters:
00:00 Control AI spend across Copilot and agents
00:46 Track your own Copilot usage and limits
01:22 How Copilot Credits measure AI consumption
01:36 Measure AI ROI in Agent 365 Business Analytics
02:52 Pin down top cost drivers by model
03:35 Spot top users and spread best practices
03:57 Weigh use case cost against AI value
05:04 Forecast month-end cost and model scenarios
05:51 Raise spending limits as a budget owner
06:37 Enable usage-based billing in Microsoft 365
07:19 Create spending policies with hard limits
08:35 Delegate budget roles to owners outside IT
09:32 Start with Business Analytics and admin setup

Every advanced AI task in Microsoft Copilot, from a simple prompt to a complex Cowork or agent workflow, consumes Copilot Credits. One Copilot Credit currently equals one cent in US dollars. Users check their own consumption under Usage details in Copilot, with a seven-day view, remaining monthly limit, and credits used per task.

Agent 365 Business Analytics gives managers, budget owners, and CIOs an organization-wide or filtered view of AI usage and cost by manager hierarchy, organization, or job function. Break down spend by service, model provider, and use case. Compare services like GitHub Copilot and Cowork, and use the combined view to see which models each service relies on and how that adds up to cost. The Use cases view maps sessions, cost, and AI value by business domain, with AI value calculated from the time it would take a person to do comparable work, using official sources including the US Department of Labor.

Cost & Forecast projects month-end cost and shows what drives increases and decreases by job function, model, and service. Model what-if scenarios, such as a spending cap, expanded access, or a shift to lower-cost models, and compare the results with current usage.

In the Microsoft 365 admin center, IT admins enable usage-based billing with an Azure subscription on pay-as-you-go or prepaid billing, then create spending policies under Cost Management. Scope policies by identity or by resource, such as a shared agent, set cumulative and per-user monthly limits, configure alerts, and control which models are allowed with templates. Assign Delegator, Writer, and Reader roles so budget owners outside IT manage policies directly from Agent 365 Business Analytics.

🔗 Related links:
— Check out Agent 365 Business Analytics at https://aka.ms/A365Analytics
— Activate usage-based billing and set up your policies at https://admin.microsoft.com

► Unfamiliar with Microsoft Mechanics?
Microsoft’s Official Video Series for IT
— Subscribe https://www.youtube.com/c/MicrosoftMechanicsSeries
— Microsoft Tech Community: https://techcommunity.microsoft.com/t5/microsoft-mechanics-blog/bg-p/MicrosoftMechanicsBlog
— Podcast: https://microsoftmechanics.libsyn.com/podcast
►Join us on social:
— https://twitter.com/MSFTMechanics
 — https://www.linkedin.com/company/microsoft-mechanics/
— https://www.instagram.com/msftmechanics/
— https://www.tiktok.com/@msftmechanics

#FinOps #MicrosoftCopilot #Agent365 #Microsoft365

Read the whole story
alvinashcraft
2 hours ago
reply
Pennsylvania, USA
Share this story
Delete
Next Page of Stories