 Log in

Why you're seeing more Next.js security advisories, and what we're doing about it.

|
Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
|

Pennsylvania, USA


https://www.youtube.com/watch?v=eK7msluMltY
Summary: Edge for Business is the most used enterprise browser in the world. At Microsoft Ignite 2026, we're introducing new ways for users and agents to get more done. Deeper integration with Microsoft 365 security capabilities helps IT protect and manage browser activity. We're also expanding our focus, supporting managed service providers (MSPs) with multi-tenant browser policy management through inforcer.
The browser looms large in a cloud-centered world. By an industry estimate, roughly 85% of work is now happening in the browser 1. Increasingly, it's a platform on which AI agents can act alongside people across websites and apps, inside an authenticated enterprise session. Reflecting these shifts, Forrester recently stated that the browser has evolved to a "first-class endpoint" in its "Top 10 Trends Shaping Endpoint Security in 2026" report.
For IT and security teams, that raises the bar for the browser. Today, Edge for Business is the most used enterprise browser in the world 2. This milestone is built on your trust. You do the critical work behind the scenes to keep your organizations secure and productive, and we're grateful for the opportunity to support you.
Looking ahead, our vision is to deliver the best enterprise browser for humans and agents—and expand our impact by helping managed service providers (MSPs) secure work for their customers. Read on to discover how we're starting to bring that vision to life at Microsoft Ignite 2026.
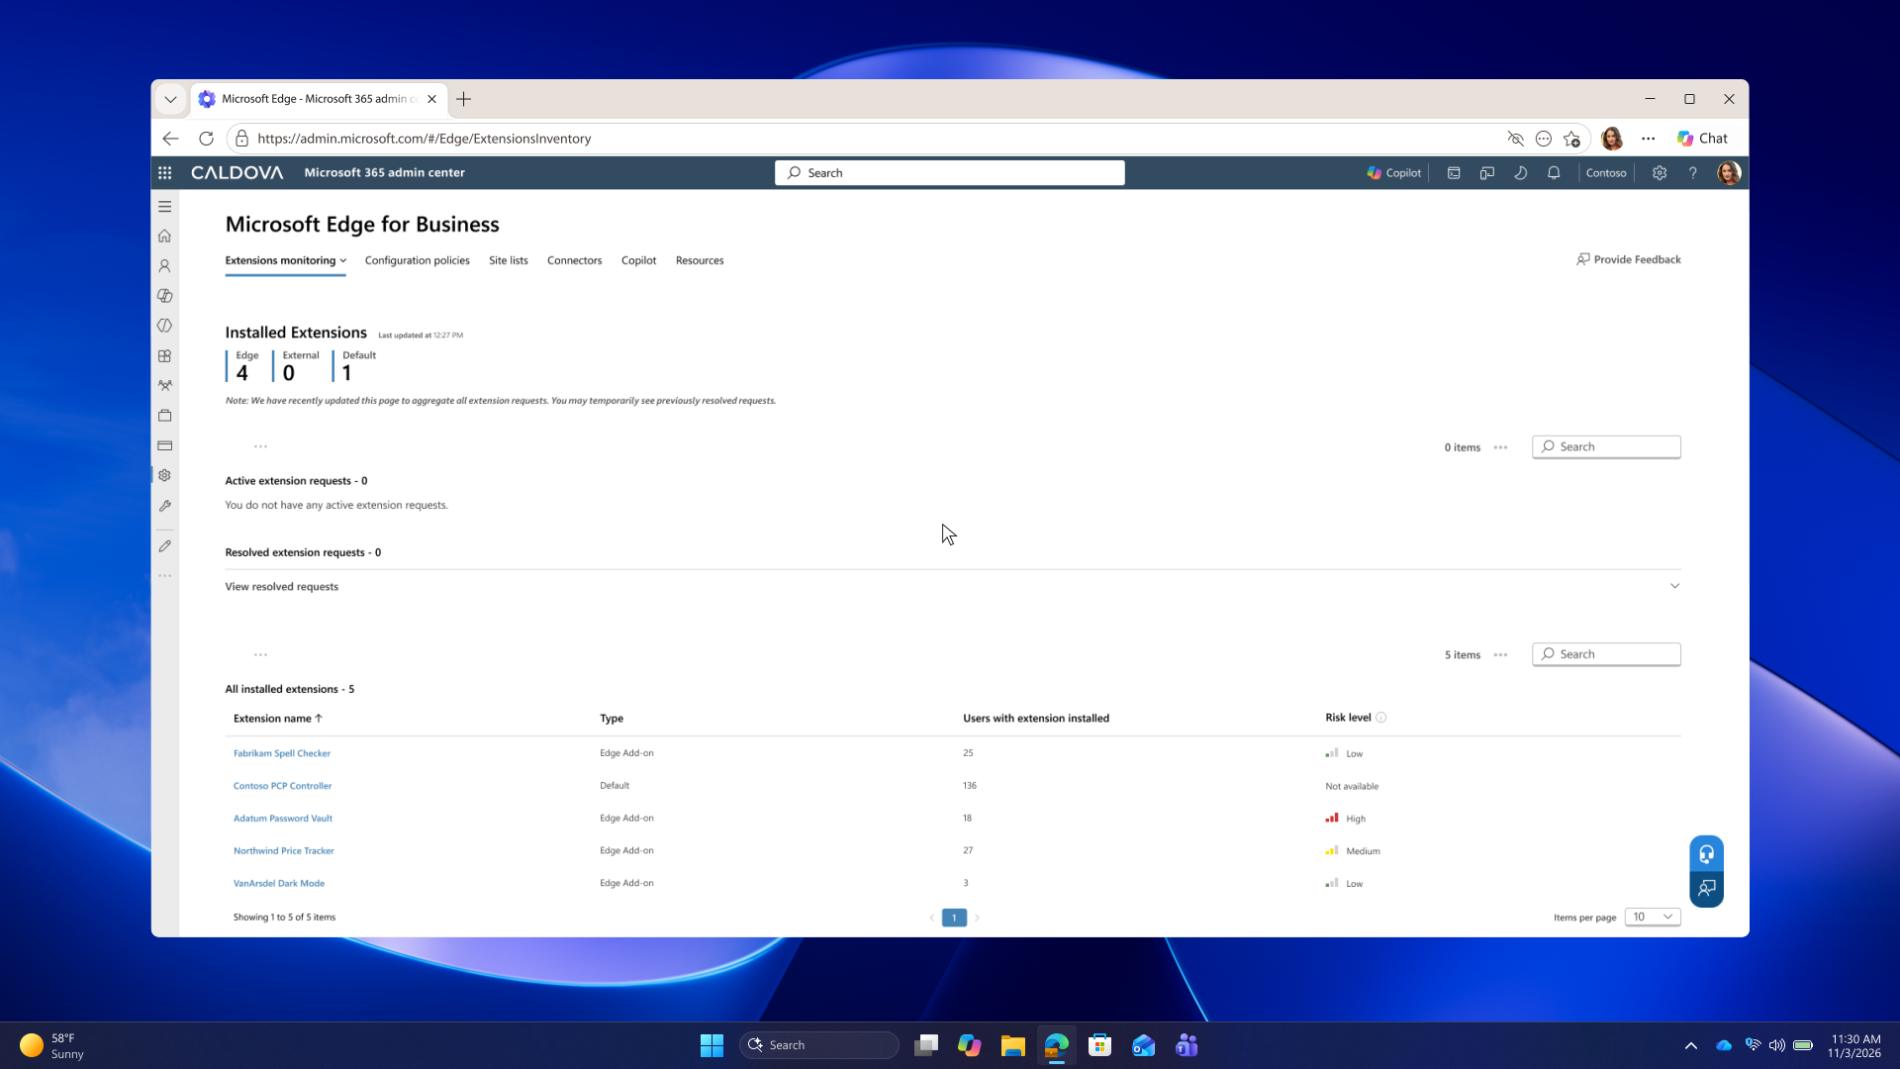 Generally available. Requires Microsoft 365 license.
An approved extension may still need boundaries. Only on Edge for Business, extension leak control prevents organization-installed extensions from reading content on protected pages. Those extensions can still work on other pages.
https://www.youtube.com/watch?v=zVRkf_640QM
Available in preview. Requires Microsoft 365 E3 licensing.
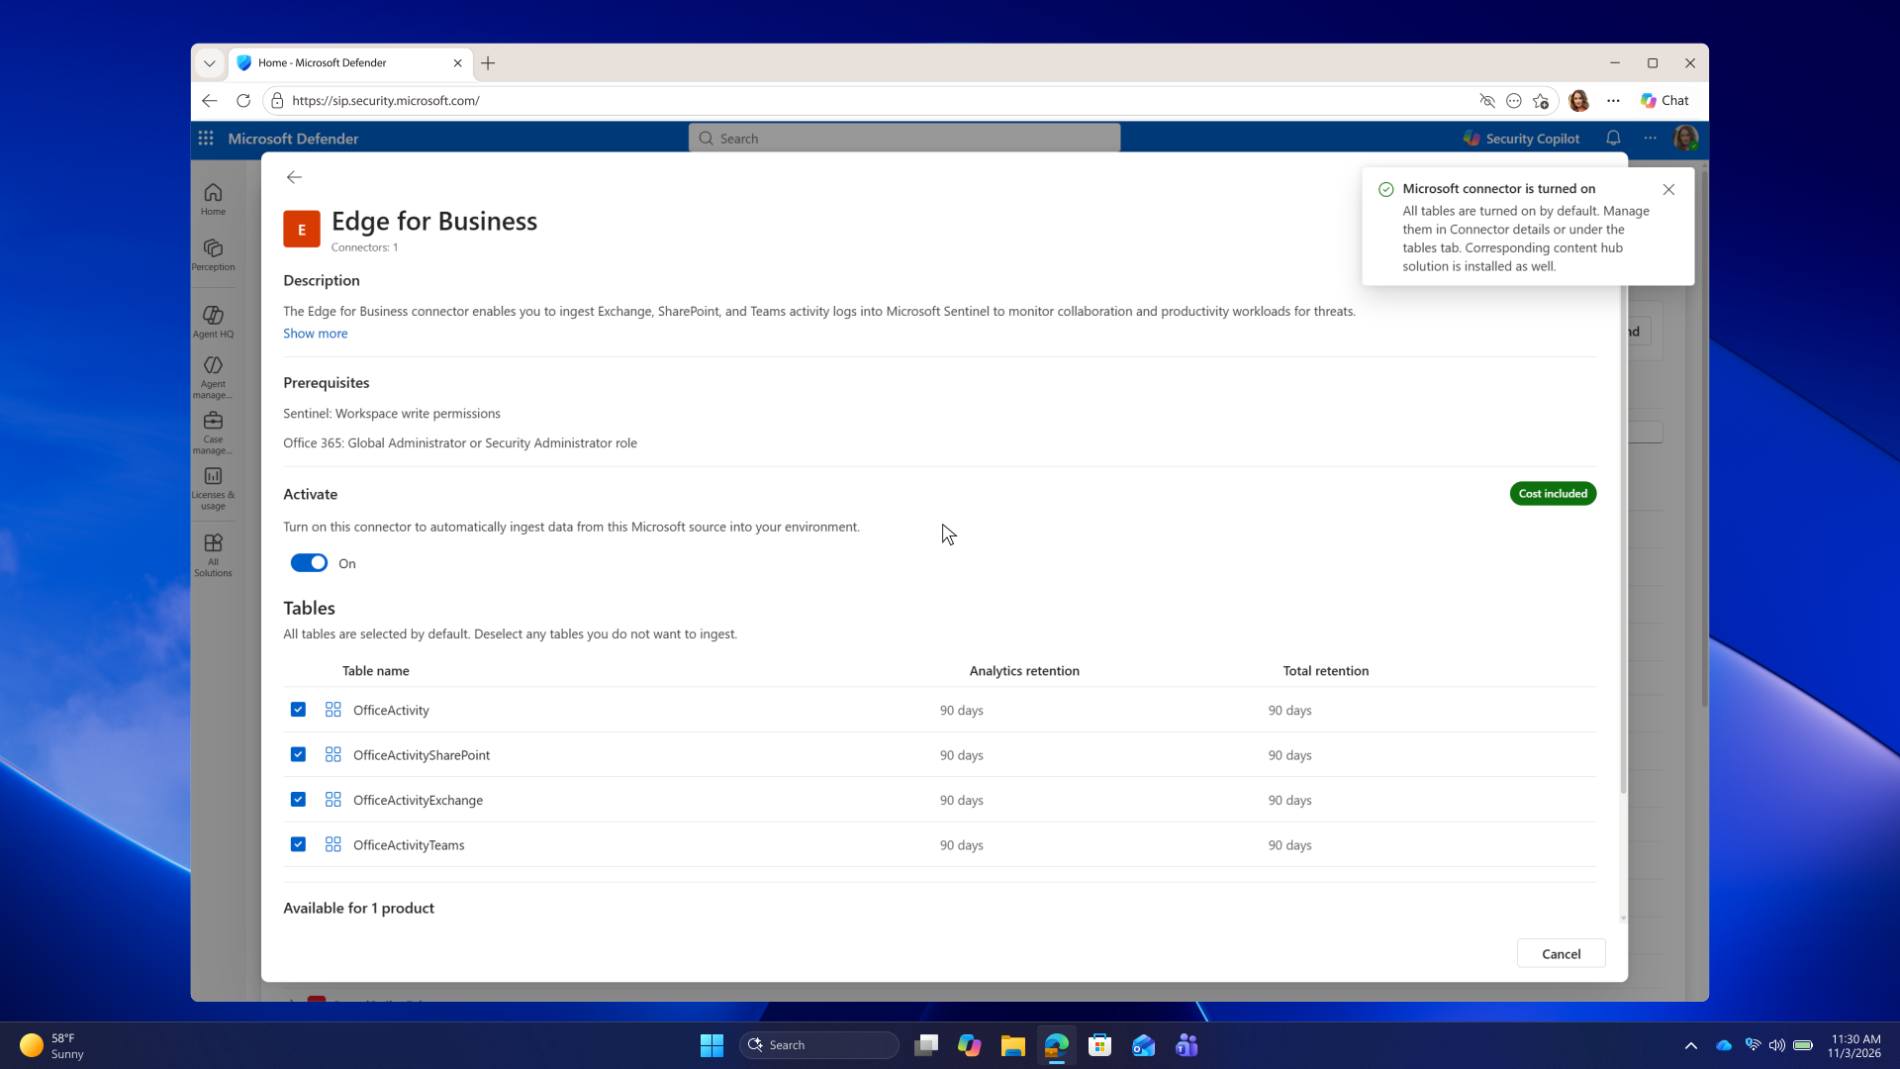 Available in preview. Requires Microsoft Sentinel licensing.
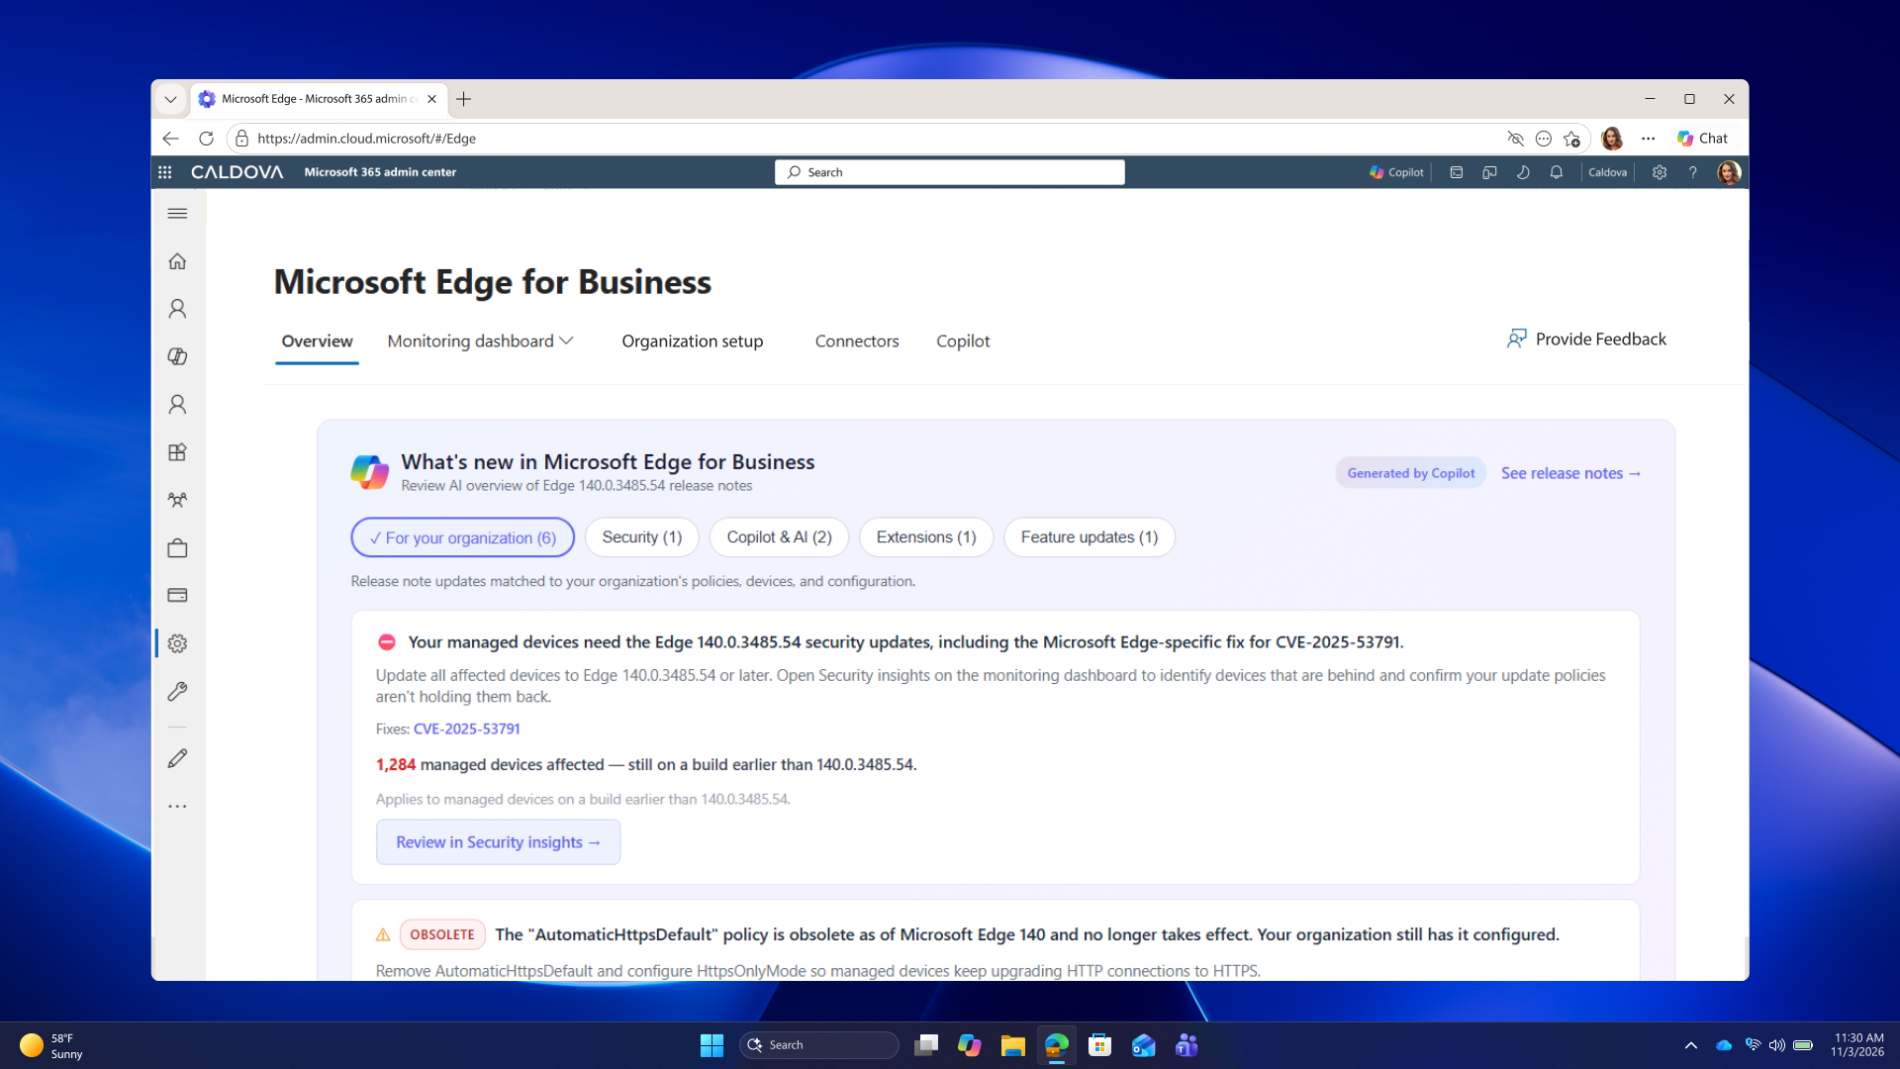 Available in preview with no additional licensing required.
Jump to
- Agents that work your way, on your terms: Reusable skills, faster skills, fewer tokens, agents in managed browsing, and more on governance and a system of safety.
- Everyday browsing, made smarter: Update web experiences without code, create an interactive brief from tabs, write and plan with context from your work.
- Browser security in a high-velocity threat environment: Updates with less disruption, manage extension risk, browser signals in Microsoft Sentinel, private web apps without a VPN, on-screen redaction.
- Browser security, strengthened by our partner ecosystem: Multi-tenant policy management with inforcer, partner connectors on more platforms, and Akamai Workforce Protector on mobile.
- How should IT teams get started? It's EZ
Agents that work your way, on your terms
Your organization is probably already juggling more than one agent. Alongside Microsoft Copilot, your users may rely on agents such as Claude or ChatGPT, in dedicated apps, command-line tools, or custom builds. Users want the power. You need the control. Whatever the agent, Microsoft or otherwise, it should do its best work in Edge for Business: faster, with fewer tokens, and more accurate results. IT and security teams get predictability too: agents can run in the managed browser you've configured, under your control and visibility. Today we're sharing the first building blocks.Delegate everyday browsing tasks to Cowork
At a glance: Cowork in Edge for Business now includes agentic browsing: it can complete multi-step tasks across websites on users' behalf. At Ignite last year, we introduced AI browsing with Copilot in Edge for Business, and many of you put it to work in preview. Thank you. We're excited to share agentic browsing is now part of Cowork, available via the sidepane, the new tab page, and web. With this, users have one place to delegate work, from creating docs to prepping for meetings or completing a task on the web. It's an easy way for users to get comfortable with agentic work, starting with small, everyday tasks, so they can get back to the work that takes creativity, judgment, and complex thinking. https://www.youtube.com/watch?v=-oSn_uaNILs Generally available. Requires Microsoft 365 Copilot license with usage-based billing enabled.Turn complex tasks into Cowork skills by simply recording them
At a glance: Skills recorder in Edge for Business turns a workflow into a reusable, sharable Cowork skill. Cowork handles everyday tasks well. But some work is more complex: it can take many steps, span multiple systems, and depend on specialized knowledge. With skills recorder, a user can record themselves completing an end-to-end process once and turn it into a skill that can be shared with teammates. And because the skill follows the same proven steps every time, that means fewer tokens spent and more consistent results. https://www.youtube.com/watch?v=pEnuYGyqdUY Available in preview by end of year. Requires Microsoft 365 Copilot license with usage-based billing enabled.Faster skills that use fewer tokens
At a glance: Edge for Business is working to help any agent complete common web tasks faster and with fewer tokens. We're working on optimizing how agents carry out the most common actions on the world's most popular websites. Regardless of the agent being used, Edge for Business will take the most token-efficient path to task completion. Early internal tests show an average of 30% less token usage. It's early, but the direction is clear: faster results, fewer tokens per task, and more consistent execution. https://www.youtube.com/watch?v=pS05FFr7Z0QPut browser agents on managed ground
At a glance: The managed agent browsing experience in Edge for Business helps IT bring Microsoft and other providers into a governed browser, under the policies IT already manages. Every agent that opens a browser raises the same practical questions: Can the agent access more than the person it represents? Do data protections still apply? Can users and admins tell whether a person or an agent is working? The new managed agent browsing experience enables IT to help enforce the use of Edge for Business by agents from Microsoft and other providers. This helps ensure that whenever an agentic task needs a browser, it occurs within the bounds of a governed browser. Each agent works in a dedicated window with its own Microsoft Entra agent identity, and operates within the user's existing permissions and organizational policies. Visual cues make it clear when a window belongs to an agent. Available in preview with Microsoft 365 E5 license.What's next: see and govern browser agents alongside other agents
At a glance: Our vision is to bring browser agents into Agent 365 and Microsoft Entra logs, so you can govern them alongside other agents and tell their actions apart from a person's. Our vision is to make agents running in Edge for Business visible and governable across Microsoft's identity and management tools. Because each agent session carries its own Entra agent identity, you'll be able to view browser agents in Agent 365 alongside the rest of your organization's agents. In the future, see which agents are in use and who's using them, apply policies, and block or quarantine an agent that isn't approved or is exhibiting risky behavior. When you need to investigate, Microsoft Entra logs will show which agent took an action and which user it was acting for, so agent actions are easy to tell apart from those of a person. https://www.youtube.com/watch?v=0_R0vy13KTYAn integrated system of safety for built-in AI
At a glance: AI built into Edge for Business is backed by existing enterprise protections, policy-based rollout, and safeguards for agentic browsing. The business wants AI now. You want to keep that progress secure. With Edge for Business, you don't have to choose. Its system of safety for built-in AI is anchored on a philosophy of "controls-in-depth":- Start with a secure enterprise browser foundation: Edge for Business provides a governed base. It enforces your organization's existing protections on built-in AI experiences, including Purview Data Loss Prevention and session controls. In preview, Protected session creates an isolated, secure chat session where Copilot can interact with protected content while helping preserve organizational data policies.
- Enterprise data protection (EDP): You already know and trust EDP for email and other files – the same promise applies to Copilot. Prompts, responses, and files stay within your tenant and aren't used to train models.
- Policy-based control: Advanced AI capabilities come with policies, so IT can configure and manage how they're used across your organization.
- Purpose-built agentic safeguards: Cowork browses within the user's existing permissions and organizational policies. Users stay in control: Cowork hands back sign-ins and payments, asks before sensitive actions, and can be watched or stopped at any time.
Everyday browsing, made smarter
Not every task needs an agent. Built-in AI in Edge for Business helps make existing workflows faster and better, from writing to reshaping the sites users rely on.Make web experiences better with Remix
At a glance: Remix in Edge for Business lets users customize how a website looks and works without writing code or changing the underlying site. Users often rely on poorly designed or hard-to-navigate sites, including legacy apps and dashboards without developer support. With Remix, they can clear away clutter, add missing tools, or change a page's look—without waiting for a fix or writing code. To remix a page, they can choose from preset themes and fonts, or describe a custom Remix in plain words. Remixes are stored locally, and users can turn them on and off with a simple toggle. https://www.youtube.com/watch?v=Yh4xwjzNicQ Generally available.Turn information across tabs into an interactive brief
At a glance: Interactive brief in Edge for Business quickly turns information across your browser tabs into a polished, interactive page you can explore and share. An executive asks for a status update. You have the data, but it's scattered and you don't know what they want to dig into. Instead of building a presentation to anticipate every question, interactive brief quickly turns the information across your browser tabs into an interactive page that can be explored during the meeting and shared afterward. Each brief is saved to your OneDrive as a snapshot, shared just like any other OneDrive file, and governed by the policies IT already manages. No new shadow IT problem. https://www.youtube.com/watch?v=OKISxyWcqE4 Available in preview by end of year. Requires Microsoft 365 Copilot license with usage-based billing enabled.Get writing help, informed by your work
At a glance: Writing assistance in Edge for Business helps users write in any form field with context from their work. Writing assistance in Edge for Business helps users draft and edit text in form fields, including on internal and line-of-business sites that rarely have writing help built in. Connected to Work IQ, it can write using context from the user's calendar, files, and more. https://www.youtube.com/watch?v=nxx8UrxDpCQ Available in preview. Work grounding requires a Microsoft 365 Copilot license.Get suggested next steps with Journeys
At a glance: Journeys in Edge for Business suggests next steps based on your work and browsing. Piecing together status and action items across calendars, emails, and chats takes time. Journeys—shown as "Get things done" on a new tab page—performs that legwork and suggests next steps on workstreams, based on the user's work and browsing context. Available in preview. Requires Microsoft 365 Copilot license.Browser security in a high-velocity threat environment
The best enterprise browser for humans and agents needs more than agent guardrails: a rock-solid security foundation for today's enterprise browsing must be in place. With cyberthreats moving at a historic pace, you need practical security solutions now.Apply urgent browser updates with less disruption
At a glance: Edge for Business helps you apply security fixes faster with fewer interruptions to users. Restart to update on idle, Security Insights, and Security Update Alerts are available today, and Microsoft is exploring seamless updates that avoid restarts. Applying urgent security fixes is critical. The challenge is doing so without repeatedly interrupting employees. Microsoft is exploring seamless updates to update Edge without closing work or requiring restarts. An early prototype demonstrates the ambition and invites industry discussion. Available today, Restart to update on idle can relaunch Edge for Business during an idle period. This shrinks the gap between patch availability and installation. To monitor Edge versions across your estate, turn on Security Insights. To help improve the signal-to-noise ratio, set Security Update Alerts to notify when updates meet your chosen severity threshold. Learn more in our recent blog.See and control extension risk
At a glance: Edge for Business helps you assess extension risk with Extension safety, and protect page content with Extension leak control. Extensions can expand what employees can do, but they are often vectors of risk. Extension safety provides an organization-wide inventory with Akamai and Spin.AI risk scores at the extension and version level. Now it's easier for admins to assess risk and make allow and block decisions.
Generally available. Requires Microsoft 365 license.
An approved extension may still need boundaries. Only on Edge for Business, extension leak control prevents organization-installed extensions from reading content on protected pages. Those extensions can still work on other pages.
https://www.youtube.com/watch?v=zVRkf_640QM
Available in preview. Requires Microsoft 365 E3 licensing.
Bring browser signals into Microsoft Sentinel
At a glance: A new connector brings Edge for Business browser activity into Microsoft Sentinel. A new native connector for Edge for Business brings browser security events and audit logs into Microsoft Sentinel, adding context for SOC teams and eliminating a browser blind spot.
Available in preview. Requires Microsoft Sentinel licensing.
Access private web apps without a separate VPN client
At a glance: Microsoft Entra Global Secure Access in Edge for Business lets users reach private web apps with just their work profile, no VPN client required. VPN and VDI have been the traditional solutions for secure access to private company web apps from a personal laptop. This requires software installation, extra user steps, and another client for IT to support. Microsoft Entra Global Secure Access in Edge for Business lets users reach approved private web apps simply through their signed-in Edge work profile, skipping a separate VPN or access client altogether. IT targets the access path and Global Secure Access policies to employees' work accounts. Work identity is now the key to secure private access. https://www.youtube.com/watch?v=Gj9wIWbvAcs Available in preview. Requires Microsoft 365 E7 license.Reduce sensitive information exposed on screen
At a glance: Redaction leak control in Edge for Business blurs sensitive information on protected pages, and users can reveal it when needed. In call centers and other shared environments, IT needs to obscure sensitive on-screen data without blocking legitimate access or disrupting work. Redaction leak control visually blurs supported sensitive information on data loss prevention-protected pages. Users can reveal a value when needed, then hide it again. https://www.youtube.com/watch?v=ggTo0XJ_nBs Available in preview with Microsoft 365 E5 license.Easily turn release notes into action
At a glance: AI insights in the Edge management service turns release notes into tailored recommendations for your tenant. Release notes can be dense, but you need to know which browser policies affect your environment. AI insights in the Edge management service summarizes the latest release notes and recommends next steps for your tenant.
Available in preview with no additional licensing required.
Browser security, strengthened by our partner ecosystem
We're expanding our focus to support MSPs, who do critical work managing security for small and medium-sized businesses. We're also helping customers build on their existing security investments—not just Microsoft's. Our connector program helps bring the security tools you already use into the browser—and we're expanding support across more platforms.Manage browser policies across customer tenants with inforcer
At a glance: Through inforcer, MSPs can apply a recommended Edge for Business security baseline across multiple customer tenants on Windows and macOS. For MSPs, managing browser policies customer by customer takes time and can lead to settings drift. Edge for Business is introducing a recommended browser security baseline with inforcer, built on Microsoft and CIS security guidance and inforcer's experience across real MSP tenants. In inforcer, MSPs can apply the managed baseline across multiple tenants and choose how strictly to align each, or build their own. This not only saves time but also gives MSPs a foundation for managed browser security offerings. The baseline supports Windows and macOS, and each customer tenant requires a Microsoft Intune license. https://www.youtube.com/watch?v=bBk9JGm1frI Multi-tenant browser policy configuration through inforcer is generally available.Extend partner security connectors to macOS, iOS, and Android
At a glance: Edge for Business' reporting connectors now support macOS, iOS, and Android, and device trust connectors now support macOS. The Edge for Business connector ecosystem enables you to bring the security tools you already use into the browser. Now, we're extending that reach to more platforms. Our reporting connector now supports macOS, Android, and iOS in addition to Windows, with partners including Devicie. This gives IT teams a more complete view of browser activity across devices, helping ensure consistent monitoring and policy enforcement. We're also expanding secure access. The device trust connector now supports macOS in addition to Windows, with partners including Cisco Duo and Omnissa. Visit Reporting connectors and Device trust connectors to learn more.Bring Akamai Workforce Protector policies to iOS and Android
At a glance: Organizations using Akamai Workforce Protector can now apply its AI, data loss prevention, and web security policies in Edge for Business on iOS and Android. Organizations using Akamai Workforce Protector can now apply the same AI usage, web and SaaS data loss prevention, and web security policies in Edge for Business on managed iOS and Android devices. IT deploys the extension through policy, so protection follows employees to mobile in Edge for Business. Read the announcement from AkamaiHow should IT teams get started? It's EZ.
At a glance: To get started with Edge for Business, go to aka.ms/ConfigureEdgeEZ and choose a guided path for configuring common scenarios. You don't need a multi-year plan to improve your browser security posture. Do just one thing: go to aka.ms/ConfigureEdgeEZ. Choose a common browser security scenario, and follow a guided path for configuration. You're doing critical work behind the scenes. We see you. We're here to make it easier for you. 1 Source: "The State of Workforce Security: Key Insights for IT and Security Leaders", Omdia, 2025. 2 Based on worldwide share of browser minutes of use on Windows devices at organizations with more than 1,000 employees. Windows is the world's most widely used enterprise PC operating system.
Pennsylvania, USA
Every major shift in computing has changed what people can do at work, and Windows has been at the center. Today, it runs critical work inside your organizations, on over a billion devices across the world. That is a privilege and a responsibility. It’s why, above all else, we’re moving faster than ever on security so you can build on a foundation of trust and lead in the era of Hybrid Intelligence.
Agents are the next shift in computing. Over the past year, organizations have moved AI from pilots into daily work, and agents are now taking on tasks across apps, files, and systems. In conversations with technology leaders, the questions they’re asking have evolved. They are past debating whether to adopt AI. They are turning to agents and want to know how to run them securely, and how to scale outcomes without cost or risk growing faster than value.
Today at Ignite, we announced:
 We’re also making device security easier to verify. Windows baseline protection, now in preview in the Windows Insider Program, brings foundational protections like secure boot, virtualization-based security and memory integrity together into one verifiable security state. People get better visibility into the security posture of their PC, and IT gets a clear yes-or-no answer for every device in the fleet. Application developers can use baseline protection to verify that the devices running their applications meet their security requirements. The baseline will continue to evolve as we raise the bar in security.
We are proud to be collaborating with partners from across the ecosystem to see how Windows baseline protection helps meet their needs.
 We’re also making it easier to protect your devices from the risks that come with elevated privilege. With Windows administrator protection, now generally available, IT can enable local administrators to run with standard user privileges by default. When a task needs administrator rights, Windows Hello verifies the user and grants those rights to that task alone. When the task ends, so do the elevated privileges, and the risk that came with them.
https://www.youtube.com/watch?v=lGpmGHrrZNg
The same AI that’s helping organizations scale is also helping attackers move faster. Our latest Microsoft Digital Defense Report found that weaponizing a vulnerability, which once took expert skills, now takes just one prompt. New vulnerabilities across the industry are on track to double this year. We’re using AI to stay ahead. MDASH, Microsoft Security’s multi-model agentic scanning harness, now scans Windows code at a scale we’ve never had before, finding vulnerabilities earlier and fixing them faster. In October alone, we shipped fixes for more than 1,100 vulnerabilities, more than in all of 2025. Those fixes only protect your employees once they reach your devices.
 Our fastest customers deploy security updates to more than two-thirds of their devices within a week. Windows Autopatch helps more organizations move at that speed: on average, Autopatch customers deploy updates over 40% faster than customers using on-premises management, and usage has grown more than 50% in the last year, to over 150 million enrolled devices. Autopatch now also gives IT more control over updates, better visibility into the features they include and fewer interruptions, with one reboot a month.
The same management principles now apply to apps. With Microsoft Intune Enterprise App Management, IT can deploy and manage apps at scale and can now preview automatic updates not just for the applications they deploy, but the applications people install themselves, with the same controls and deadlines they know from Windows Autopatch.
Windows is also standardizing on declarative management, so devices keep themselves in the state IT defines. Policies such as Wi-Fi and VPN apply, within minutes and stay protected from drift, even when a device is offline.
All of this builds on the improvements we’ve made to Windows quality throughout the year, across performance, reliability and craft.
Learn more about Windows security and management at Ignite.
 Leading agent builders and customers are integrating with MXC. OpenAI has turned MXC on by default in Codex, Meta is running MXC on tens of thousands of Windows devices, and more than 20 agent and app builders, including Anthropic, Box, Perplexity and Replit, are building on MXC.
https://www.youtube.com/watch?v=FXvmLQVadwg
Agent 365 governance and policies extend to local agents, including on Windows, so together with Microsoft Entra, Intune, Defender and Purview, organizations can govern agents with the practices they already use.
Learn more about Windows security, management, and agent governance at Ignite.

- A trusted, secure, and more resilient foundation. The Windows endpoint security platform and Windows administrator protection are now generally available, Windows baseline protection is in preview, and Windows Autopatch customers deploy updates over 40% faster than with on-premises management.
- The most secure platform for agents. New containment capabilities in Microsoft Execution Containers (MXC), which OpenAI and Meta are already building on, and Windows 365 for Agents, now eligible for Copilot Credits.
- Hybrid Intelligence at work. GitHub Copilot Fusion can now route coding work to local models on developer PCs, in preview, and local context, actions and models are coming soon to Copilot on Copilot+ PCs.
- One estate, from the PC to Azure built as connected AI infrastructure. Direct Stream for Windows 365, and Windows Server 2028 in public preview, with Microsoft Foundry and support for new AI hardware from AMD and NVIDIA.
A trusted, secure, and more resilient foundation
Critical work happens on Windows, and staying protected while threats evolve has never been more important. That starts with a trusted, secure, and more resilient Windows foundation. We are making investments to harden the platform, make it easier to protect and manage devices, and keep them current. Historically, some security protections ran in the Windows kernel, where one failure could affect the entire device. In 2024, we started working with our security partners on a more resilient approach. Today, the Windows endpoint security platform is generally available. It lets security providers move critical protections from kernel mode to user mode, making Windows more resilient while preserving the protection customers expect. We are deeply grateful to the ecosystem partners who have built on the platform with us, including Bitdefender, CrowdStrike, ESET, SentinelOne, Sophos, Trellix and TrendAI.
We’re also making device security easier to verify. Windows baseline protection, now in preview in the Windows Insider Program, brings foundational protections like secure boot, virtualization-based security and memory integrity together into one verifiable security state. People get better visibility into the security posture of their PC, and IT gets a clear yes-or-no answer for every device in the fleet. Application developers can use baseline protection to verify that the devices running their applications meet their security requirements. The baseline will continue to evolve as we raise the bar in security.
We are proud to be collaborating with partners from across the ecosystem to see how Windows baseline protection helps meet their needs.
We’re also making it easier to protect your devices from the risks that come with elevated privilege. With Windows administrator protection, now generally available, IT can enable local administrators to run with standard user privileges by default. When a task needs administrator rights, Windows Hello verifies the user and grants those rights to that task alone. When the task ends, so do the elevated privileges, and the risk that came with them.
https://www.youtube.com/watch?v=lGpmGHrrZNg
The same AI that’s helping organizations scale is also helping attackers move faster. Our latest Microsoft Digital Defense Report found that weaponizing a vulnerability, which once took expert skills, now takes just one prompt. New vulnerabilities across the industry are on track to double this year. We’re using AI to stay ahead. MDASH, Microsoft Security’s multi-model agentic scanning harness, now scans Windows code at a scale we’ve never had before, finding vulnerabilities earlier and fixing them faster. In October alone, we shipped fixes for more than 1,100 vulnerabilities, more than in all of 2025. Those fixes only protect your employees once they reach your devices.
Our fastest customers deploy security updates to more than two-thirds of their devices within a week. Windows Autopatch helps more organizations move at that speed: on average, Autopatch customers deploy updates over 40% faster than customers using on-premises management, and usage has grown more than 50% in the last year, to over 150 million enrolled devices. Autopatch now also gives IT more control over updates, better visibility into the features they include and fewer interruptions, with one reboot a month.
The same management principles now apply to apps. With Microsoft Intune Enterprise App Management, IT can deploy and manage apps at scale and can now preview automatic updates not just for the applications they deploy, but the applications people install themselves, with the same controls and deadlines they know from Windows Autopatch.
Windows is also standardizing on declarative management, so devices keep themselves in the state IT defines. Policies such as Wi-Fi and VPN apply, within minutes and stay protected from drift, even when a device is offline.
All of this builds on the improvements we’ve made to Windows quality throughout the year, across performance, reliability and craft.
Learn more about Windows security and management at Ignite.
Hybrid Intelligence on Windows
The same trusted foundation that applies to your employees extends to AI and agents on Windows. When an agent acts on your behalf, you need to know what it can access and what it does. That's where Hybrid Intelligence begins. Hybrid Intelligence on Windows brings together a secure agent platform and intelligent model routing across a broad range of Windows PCs powered by capable silicon. Hybrid Intelligence uses the right model and compute for each task, on the device or in the cloud. The result is AI that's secure by design, smarter about token spend, and more useful every day.Building Windows to be the most secure platform for agents
Agents bring big productivity gains, and because they can work across files, networks and apps, they also bring new security risks. Customers shouldn't have to choose between giving agents free rein and blocking them entirely. That's why we're building containment, identity and manageability into Windows to run and manage agents securely: Containment: limit what an agent can access and do. Identity: tell an agent's activity apart from a person's. Manageability: govern access and monitor what agents do. Microsoft Execution Containers (MXC) has been generally available on Windows 11 since October. MXC gives each agent a contained environment, with policies for which files and networks it can reach, enforced by Windows at runtime. MXC works on Windows, Linux and macOS, and on Windows it’s built into the operating system, which gives organizations more control of their data and a broader range of containment options, from process and session containers to WSL containers, virtual machines and Windows 365 for Agents. Since general availability, we’ve improved quality and made agent identity harder to tamper with. At Ignite, we’re adding:- Process container improvements, in preview, which give each agent a protected workspace with clear limits on what it can talk to, which networks it can reach and how it proves its identity, reducing the risk that an agent reaches the wrong data or affects the rest of the device.
- Learning and permissive modes, now generally available, which let IT observe how an agent normally works with system services before enforcing restrictions, so policies roll out without breaking legitimate work.
- Local Micro VMs, now experimental, give higher-risk workloads a hardware-backed virtualized boundary, with hardware-enforced isolation.
Leading agent builders and customers are integrating with MXC. OpenAI has turned MXC on by default in Codex, Meta is running MXC on tens of thousands of Windows devices, and more than 20 agent and app builders, including Anthropic, Box, Perplexity and Replit, are building on MXC.
https://www.youtube.com/watch?v=FXvmLQVadwg
Agent 365 governance and policies extend to local agents, including on Windows, so together with Microsoft Entra, Intune, Defender and Purview, organizations can govern agents with the practices they already use.
Learn more about Windows security, management, and agent governance at Ignite.
Windows 365 for Agents
Some agents need a computer of their own. Windows 365 for Agents gives them secure Cloud PCs, joined to Microsoft Entra and managed in Intune like any other PC in your fleet. Agents use them the way people do. They see the screen, click, type and move data between apps, so they can work in line-of-business, browser, legacy and on-premises Windows apps, including apps without an API. Windows 365 for Agents is available as a computer-use tool in Microsoft Copilot Studio, is coming to Microsoft Foundry in preview early next year and is now eligible for Copilot Credits, bringing it into one billing, governance and cost-management experience. Agents can now reach on-premises apps using agent identities, in preview, and persistent agent Cloud PCs for long-running, always-on work are coming to Frontier preview. Microsoft’s own business operations team uses Windows 365 for Agents to process orders and has cut processing time by 60%. Learn more about Windows 365 for Agents.Bringing local context, actions, and diagnostics to Copilot with Hybrid Intelligence
Copilot is AI built for work, and on Windows it can do even more. Three local capabilities are coming soon to Copilot+ PCs, and they'll make Copilot more helpful in the moments that matter most at work. The first is local context. Much of what people work on lives on their PC: the files they have open, the apps they're using, and the current state of their device. With permission, Copilot can use that information to offer better help, bringing local context into the flow of work. The second is local actions. Helpful AI doesn't stop at answers. Copilot will be able to take action across Windows, from working with files to helping diagnose PC issues, while the user stays in control. The third is local models. Not every task needs the cloud. Copilot will increasingly use models running right on the PC and reach to the cloud when a task calls for it, so each task runs where it makes the most sense, making token costs go further. https://www.youtube.com/watch?v=R6WkUkvIcC8 Here's what that looks like in practice. With local file actions in Copilot, people can ask Copilot in plain language to find, organize, move, copy or rename files. Tidying a cluttered Downloads folder or pulling project files together takes a sentence, and your employees can spend time on more important activities while Copilot does the work on Windows. https://www.youtube.com/watch?v=1TVVgqdlWOg Local PC diagnostics brings the same simplicity to troubleshooting. Copilot can run a read-only scan of the system to help find the root cause of errors or performance issues, then explain what's going on in clear terms. Figuring out why your Bluetooth audio isn’t working or why your network connection is slow takes a quick question instead of a support call. These capabilities can help resolve many of the most common reasons people call IT support. Employees get time back, and IT teams spend less time on tickets and more on work that moves the business forward. And building on the new Windows Search experience that makes it faster to find what you need and take action, we’re also now making it seamless to move into Copilot right from that very flow, for people who choose it.Bringing Hybrid Intelligence to GitHub Copilot on Windows
Developers are some of the biggest consumers of AI tokens. GitHub Copilot Fusion routes each coding task to the right model, and it can now tap into local models like MAI Code 1.1 Flash on developer PCs powered by NVIDIA RTX Spark and now extending to AMD Ryzen™ AI Max Series and Ryzen™ AI Max 400 Series processors. Hybrid Intelligence is available on the GitHub Copilot app, CLI and VS Code in preview. Several Fortune 500 companies are already piloting this experience. We’re also working with Adobe, Autodesk, Dell, HP, Insight, NVIDIA and PwC in the Windows Hybrid Intelligence pilot to bring local models into their development workflows.
“Adobe’s flagship Windows apps like Premiere and After Effects already use local AI to deliver creative value to our users. Like many leading organizations, we’re looking to optimize growing AI spend, both ours and our customers’, without giving up access to frontier capabilities. We’re excited for more ways to harness hybrid intelligence to empower our developers to run key workflows in the right place, whether that’s local or cloud.”
— Ely Greenfield, CTO and EVP of Adobe’s Creative Products
Agent builders like Hermes, OpenClaw, Perplexity, Replit and more are building local AI experiences on Windows. Christie’s, the fine art and luxury auction house, uses Replit’s agent on Windows to work with private art collection data that never leaves the device. https://www.youtube.com/watch?v=0fjfAhKT0sAOne estate, from the PC to Azure built as connected AI infrastructure
Hybrid intelligence extends across your entire Windows estate. Windows connects PCs, servers and Azure as one system, with trust and intelligence spanning them all, so you can match the model and the compute to the work. That makes your PCs and servers part of your AI infrastructure, and that infrastructure becomes how you grow your core business, scale expertise and accelerate time to market. PCs for every role. For knowledge work, that’s a Copilot+ PC, many powered by Intel Core Ultra. For builders, Windows supports the broadest range of devices, from PCs powered by NVIDIA RTX Spark, like Surface Laptop Ultra, to PCs with AMD Ryzen AI Max processors. For teams that need frontier models on device, NVIDIA DGX Station for Windows brings trillion-parameter models to the deskside. AMD, Intel, NVIDIA and Qualcomm bring this portfolio to life at every tier, in devices from every major PC maker. Cloud PCs for everyone. Windows 365 is the same Windows, with the same apps and the same identity, streamed from the Microsoft Cloud, and tens of thousands of organizations rely on it. Today, we’re introducing Direct Stream, the streaming technology behind Windows 365 and Azure Virtual Desktop. It brings together years of work on connection reliability, speed, transport security and in-session performance to make a Cloud PC feel like a local PC. People connect within seconds, with nearly 300% improvement in connection reliability on challenging networks compared with when Windows 365 first launched. With NVIDIA, GPU-enabled Cloud PCs, coming in preview early next year, will stream full 4:4:4-equivalent color and sharper text to up to two 4K displays at 60 frames per second, with low latency and less bandwidth. Cloud PCs, including GPU-enabled configurations, can also run compatible AI models, giving developers more compute with predictable subscription costs. That changes who Windows 365 is for. Now it’s an option for everyone in your organization, and knowledge workers can make it their everyday PC. With IT budgets tight, it can also extend the life of PCs you aren’t ready to replace, giving anyone more compute in minutes with no new hardware. Learn more about what’s new in Windows 365, including Windows 365 for Agents. Servers that run AI next to your data. Your servers hold the mission-critical apps and data your business depends on. Windows Server 2028, now in public preview, extends the trusted foundation to the datacenter with new security hardening, including Trusted Launch virtual machines, post-quantum cryptography and a hardened OS baseline. For the first time, endpoint teams can manage servers and PCs as one Windows fleet with Intune and Windows Autopatch, while infrastructure teams use Azure Arc. Your servers will become token factories, built for intelligence you can own. That’s why we’re extending Microsoft Foundry to Windows Server 2028 and expanding hardware choice. AMD’s MI350P accelerator will be available in preview in the first half of 2027 for Windows Server 2025 and later, and NVIDIA DGX Station for Windows, with the GB300 Grace Blackwell Ultra Desktop Superchip and up to 748 GB of coherent memory, will support Windows Server 2028 at general availability. Organizations building agents on an open model like NVIDIA Nemotron now have one path: build on a Windows PC, run on Windows Server next to their data and scale to Azure when they need more.Where to start in 2027
Every hardware decision you make in the next 12 to 18 months is an AI decision. It will shape what your teams can do, and what your tokens cost, until your next refresh. As you plan for 2027, here’s where to start:- Strengthen the foundation now. Deploy updates with Windows Autopatch, turn on Windows administrator protection and evaluate Windows baseline protection.
- Secure your agentic workflows. Set MXC policies with Intune to control what your agents can access within your organization.
- Start piloting Hybrid Intelligence in GitHub Copilot on Windows. For your developers, start leveraging Copilot Fusion on Windows to route coding workflows to local models and save tokens.
- Plan your refresh by role, with Copilot+ PCs and Windows 365 in one plan, so every person gets the compute their work needs.
- Bring AI to your data. Test Windows Server 2028 in the Windows Insider Program for Windows Server, or apply to the Windows Server TAP for earlier access.
Pennsylvania, USA
AI is changing the threat landscape as fast as it is changing the way we work. Attackers are using AI to find vulnerabilities, build exploits and scale their campaigns faster than ever, shrinking the time between a weakness being discovered and being used against an organization.
In this environment, the fundamentals matter more than ever. Devices that are configured securely and patched quickly remain one of the most effective defenses, and the security strategy you have for your users and data must now extend to AI and agents as well.
Windows can help enforce identity and security controls on the devices where people, apps, and data intersect. Together with Microsoft security and management solutions, as well as tools like Agent 365, Windows provides a trusted foundation that helps organizations start secure, protect what matters, and manage AI securely.
At Microsoft Ignite 2026, we're advancing that foundation across Windows with stronger protections by default, hardware-backed security, updated passwordless experiences, resilience and recovery, and new controls for AI agents. These investments extend the work we shared at Build 2026, and take the next step toward a Windows environment designed for the security demands of the AI era.
 Partners collaborating with the Windows endpoint security platform[/caption]
Alongside the Driver Quality Initiative and broader work to reduce kernel exposure and strengthen recovery, these investments are helping make Windows more resilient by design.
See what's changing with Windows endpoint security platform GA, driver quality and ecosystem resilience
We also know how important it is for users and organizations to better understand the security state of their devices. With Windows baseline protection, now available in preview, Windows brings foundational protections, including secure boot, virtualization-based security, and memory integrity together into a single, versioned security state. Instead of requiring customers and applications to understand and check individual protections, baseline protection makes it easier for users and IT to understand whether a device is in a measurable security state, to keep it up to date with the latest security safeguards, and, when stronger assurance is required, verify that state through hardware-backed attestation. It also provides developers a way to ensure that a Windows device running their applications is operating in a secure state. Windows baseline protection will continue to evolve as more security capabilities are added.
[caption id="attachment_180591" align="alignnone" width="1024"]
 Windows baseline protection as part of the Windows settings experience[/caption]
Baseline protection will show up in an updated Windows Settings experience, making security and privacy protections easier for people to understand.
Learn how Windows is making its security foundation easier to establish, understand and verify with baseline protection
A trusted foundation must also prepare for threats that emerge before they become practical at scale. At Ignite, Windows is expanding post-quantum protection in the Windows TLS stack, including pure post-quantum key exchange and authentication, while advancing a broader crypto-agile foundation across the platform. These investments give organizations practical steps they can begin taking now while preparing for a multi-year transition across applications, infrastructure and identity.
Explore the new post-quantum TLS capabilities and how to begin preparing
Together, these investments help organizations establish a known and measurable security state, build on a more resilient platform, and prepare that foundation for emerging threats.
 Windows Hello Face and PIN sign in available at Windows sign-in[/caption]
Administrator protection helps users operate with standard permissions by default and elevate privileges when needed, reducing the risk associated with standing administrator access.
Dive into passwordless, hardware-backed credentials and expanded authentication scenarios
Keeping a device secure is an ongoing process, not a one-time configuration. Investments across Windows Autopatch, declarative management, and recovery help IT maintain intended state, respond to risk, and restore operations after disruption.
See how Windows management and recovery capabilities help organizations stay secure through change
We're also advancing how organizations manage the broader Windows estate. New Intune capabilities simplify application deployment, inventory, and lifecycle management, helping applications remain current and governed alongside the devices where they run.
Microsoft is also extending Intune and Windows Autopatch to eligible Windows Server scenarios, in preview, helping endpoint teams manage configuration, compliance, applications, updates, and security across Windows clients and supported servers. This extends consistent management and security across more of the Windows estate, while complementing Azure Arc for cloud-native server management.
Learn more about Microsoft Intune’s new capabilities across Windows Server, app management and more
Helping organizations start secure and stay secure
The Windows security foundation is evolving. Windows is becoming more secure and resilient, out of the box, to help organizations and users stay productive and protected. At Ignite, we’re sharing investments that strengthen Windows from hardware and cryptography through the operating system and security ecosystem. Last year, we shared how Windows was working with security partners to evolve our platform to better integrate with the ecosystem, while remaining resilient. We can now share that the Windows endpoint security platform is reaching general availability on Windows 11. This marks an important milestone in Microsoft's work with the security ecosystem to reduce reliance on kernel drivers while preserving the capabilities security solutions depend on. We thank the partners who have joined us on this journey: [caption id="attachment_180595" align="alignnone" width="940"] Partners collaborating with the Windows endpoint security platform[/caption]
Alongside the Driver Quality Initiative and broader work to reduce kernel exposure and strengthen recovery, these investments are helping make Windows more resilient by design.
See what's changing with Windows endpoint security platform GA, driver quality and ecosystem resilience
We also know how important it is for users and organizations to better understand the security state of their devices. With Windows baseline protection, now available in preview, Windows brings foundational protections, including secure boot, virtualization-based security, and memory integrity together into a single, versioned security state. Instead of requiring customers and applications to understand and check individual protections, baseline protection makes it easier for users and IT to understand whether a device is in a measurable security state, to keep it up to date with the latest security safeguards, and, when stronger assurance is required, verify that state through hardware-backed attestation. It also provides developers a way to ensure that a Windows device running their applications is operating in a secure state. Windows baseline protection will continue to evolve as more security capabilities are added.
[caption id="attachment_180591" align="alignnone" width="1024"] Windows baseline protection as part of the Windows settings experience[/caption]
Baseline protection will show up in an updated Windows Settings experience, making security and privacy protections easier for people to understand.
Learn how Windows is making its security foundation easier to establish, understand and verify with baseline protection
A trusted foundation must also prepare for threats that emerge before they become practical at scale. At Ignite, Windows is expanding post-quantum protection in the Windows TLS stack, including pure post-quantum key exchange and authentication, while advancing a broader crypto-agile foundation across the platform. These investments give organizations practical steps they can begin taking now while preparing for a multi-year transition across applications, infrastructure and identity.
Explore the new post-quantum TLS capabilities and how to begin preparing
Together, these investments help organizations establish a known and measurable security state, build on a more resilient platform, and prepare that foundation for emerging threats.
Protect what matters to your organization, wherever the work happens
A secure starting point isn’t enough. Organizations must remain confident in their IT security as technology evolves. Windows, Microsoft Entra, Microsoft Purview and Microsoft Intune help organizations do exactly that: protect identity and data, manage apps and devices, and stay current and recoverable throughout the device lifecycle. For identity and access management, Windows continues to offer new and improved ways of signing in securely with more passwordless options. Windows Hello improvements make passwordless sign-in more consistent and get you to your desktop faster, new observability gives IT greater insight into whether users authenticate using biometrics or PIN, expanded Web sign-in brings passwordless access to more devices. There are also improvements to security key sign-in, with Windows showing you where to tap on the display, and security key management make security keys easier to use and manage. [caption id="attachment_180592" align="alignnone" width="931"] Windows Hello Face and PIN sign in available at Windows sign-in[/caption]
Administrator protection helps users operate with standard permissions by default and elevate privileges when needed, reducing the risk associated with standing administrator access.
Dive into passwordless, hardware-backed credentials and expanded authentication scenarios
Keeping a device secure is an ongoing process, not a one-time configuration. Investments across Windows Autopatch, declarative management, and recovery help IT maintain intended state, respond to risk, and restore operations after disruption.
See how Windows management and recovery capabilities help organizations stay secure through change
We're also advancing how organizations manage the broader Windows estate. New Intune capabilities simplify application deployment, inventory, and lifecycle management, helping applications remain current and governed alongside the devices where they run.
Microsoft is also extending Intune and Windows Autopatch to eligible Windows Server scenarios, in preview, helping endpoint teams manage configuration, compliance, applications, updates, and security across Windows clients and supported servers. This extends consistent management and security across more of the Windows estate, while complementing Azure Arc for cloud-native server management.
Learn more about Microsoft Intune’s new capabilities across Windows Server, app management and more
Manage agents securely
AI introduces new security risks. Agents can access resources, use tools, and take action on behalf of people and organizations. That means agentic security isn’t just about securing the agents themselves — it’s about giving users the ability to trust and control the agents running on their devices. People need confidence that agents act only in ways they have authorized, don’t harm their devices or data, and that every action an agent takes is governed. Windows is building that foundation through agent identity, containment, isolation, policy, observability, and governance. Announced last month, Microsoft Execution Containers provide governed boundaries for agent execution, helping organizations contain agent activity and maintain control over access to resources and tools. Together with Microsoft management and security solutions, these protections help organizations move agents from experimentation toward enterprise deployment without giving up control. Learn how to take governed AI agents from experimentation toward enterprise deployment Together, these capabilities help organizations give agents room to act while keeping identity, permissions, data access, tools, and execution boundaries under enterprise control.One connected system of protection
Organizations shouldn't have to stitch protections together. Windows brings identity, security and management together where work happens, providing a trusted foundation for protecting your users, data, apps and AI. Together with Microsoft Security and Microsoft Intune, Windows helps you secure and manage your organization through one connected platform, wherever you are on your AI journey.Experience Windows Security at Ignite
At Microsoft Ignite, customers can explore this story through sessions spanning a more secure-by-default Windows, platform and credential protection, modern management, resilience and recovery, and governed AI agents. In particular, Windows security principles and latest technology will be shared in the following sessions:- BRK405 | What's new in Windows security: Start secure, protect what matters, prepare for the AI era
- BRK398 | From Prevention to Recovery: building a more resilient Windows estate
- BRK392 | Future-proof your App: Prepare for evolving Windows security standards
Learn more
Explore the Windows Security Guide and Microsoft Learn for practical guidance on establishing a secure foundation, protecting your organization as technology evolves, and preparing for the AI era.
Pennsylvania, USA
As AI agents become more capable, they promise substantial productivity gains across enterprise workflows. At the same time, they can collapse familiar execution boundaries and introduce new risk paths—from agent to human, agent to agent, agent to tools, and agent to applications. That tension can leave organizations facing an unacceptable choice: give agents broad access and hope nothing goes wrong or block them and forgo the value they can deliver.
Traditional application controls remain essential, but they were not designed to express the full context of an agent’s execution across tools, child processes, files, network endpoints, and long-running sessions.
Running agents safely at enterprise scale requires three foundational operating-system primitives: identity, containment, and manageability.


Identity
When an agent operates on a user’s behalf, its actions must be distinguishable from the user’s own activity. Agent identity creates this separation, making agent activity identifiable so organizations can apply appropriate security, access, and governance controls. Windows and Microsoft Entra are working together to support agent identity across local and cloud interactions. Microsoft Entra Agent ID provides the identity foundation for governing agent access to resources, while Windows provides the local isolation boundaries that help separate agent activity from the user.Containment
Containment limits agent behavior to only the resources required for the assigned task. Microsoft Execution Containers (MXC) provide platform-enforced boundaries for this control. For example, if an agent is asked to build a website, it should access the project folder only, not personal files or unrelated sensitive data. MXC enforces those boundaries through Windows platform controls, not just policy guidance. Different agent patterns require different containment strength. A coding assistant may need lightweight process isolation, while a fully autonomous agent may require stronger isolation, including separate Windows sessions. Windows provides this containment spectrum so isolation can be matched to workload risk.Management
Organizations need centralized visibility and control over agent deployment, access, and policy enforcement. Windows connects agent operations to the Microsoft security and management ecosystem.- Microsoft Intune and other MDM solutions define and manage agent containment, configuration and compliance policy.
- Microsoft Entra governs identity, authentication, and access.
- Agent 365, Microsoft Defender, and Microsoft Purview extend observability, security, and management into agent activity workflows.
Why identity is foundational
Identity is the control anchor across all three domains. It establishes which agent is acting, enables the correct containment model, and carries policy context into interactions across devices, applications, and cloud services. The target state is consistent governance across endpoint and cloud, rather than fragmented controls.
Where Microsoft Execution Containers (MXC) fits in an enterprise agent-security strategy
Microsoft Execution Containers (MXC) should be treated as a key layer in a defense-in-depth architecture, as it connects with identity, endpoint, data, or application controls. Its distinctive role is to govern execution: which resources a local agent process can reach, and how strongly the workload is isolated. This closes the gap between granting a user access and constraining what an agent running on that user’s behalf can do. The strongest design separates responsibilities across the control plane:- Identity and access with Microsoft Entra Agent ID: Agent identity helps distinguish agent activity from a user’s own activity so organizations can apply appropriate access, security, and governance controls. Microsoft Entra Agent ID provides the identity foundation for supported agent scenarios, including identifying agent activity and enabling access controls as agents interact with cloud resources. On Windows, local security boundaries can further isolate an agent’s processes and resource access from the user. Together, these capabilities help organizations distinguish and govern agent activity across local and cloud interactions, with support varying by agent and scenario.
- Local agent containment with Microsoft Execution Containers (MXC): MXC is the policy-driven containment layer. Agents who adopt it run supported execution inside an OS-enforced boundary. MXC applies runtime controls over what the agent can read/write (for example, local files), which resources it can call, and what requests or results can flow to permitted endpoints and MCP servers.
- Securing AI on the endpoint with Microsoft Intune: Intune delivers MXC containment policy for managed Windows devices, so agent workloads run within enterprise-defined boundaries. Intune also governs agent access to company resources through device compliance, protects work data with app protection policies for supported agents, restricts unauthorized agents, and applies policy to enable Microsoft Defender runtime protection.
- Local-agent discovery, runtime protection, and investigation with Microsoft Defender: Microsoft Defender discovers supported local agents and provides endpoint context, including associated users, devices, processes, and configured MCP connections. Runtime protection helps detect and block malicious instructions and tool interactions in supported agent workflows, while alerts and investigation capabilities help security teams understand and respond to threats.
- Data loss prevention for local agents with Microsoft Purview: Microsoft Purview extends data loss prevention policies to supported local-agent interactions, including prompts and tool calls, helping organizations detect and block inappropriate sharing of sensitive information. This enables organizations to apply data protection policies as agents work with enterprise information.
- Bring local AI agents under management with Microsoft Agent 365: As organizations adopt local AI agents, they need a consistent way to understand where agents are operating, what they can access, and which ones are authorized. Microsoft Agent 365 brings supported local agents and their MCP connections into a unified Agent registry, giving administrators visibility into their AI estate and the tools agents use. With Dynamic Agent Risk, agent templates, and integrated Microsoft security controls, organizations can prioritize risks, apply governance policies at scale, bring approved agents under management, and restrict unauthorized agents.
Prepare before you deploy
Begin with an inventory of the current state of your enterprise’s agent use. This includes what agents are operating in the enterprise today and under what identities and credentials, who is using agents, what they are using agents for (types of workloads), the tools and plug-ins each type of workload invokes, the files and directories it touches, and the network destinations it calls. A good starting point for this inventory is the Agent 365 Registry, which includes an inventory of agents in your enterprise. To address technical readiness, inventory and align with prerequisite OS and software versions. For each workload, document four views:
- Business objective: the user outcome and why agent access is required.
- Execution model: how work is performed across process flows, tools, commands, files, and endpoints.
- Control boundaries: where identity context, data sensitivity, network exposure, or administrative privilege changes require controls.
- Operating readiness: required OS and agent versions, management settings, security policies, deployment groups, support readiness, and rollout governance.
Roll out Microsoft Execution Containers (MXC) progressively
1. Observe Before Enforce (Policy Evidence Phase)
Least-privilege policy design is hard when you do not yet know every resource an agent workload needs. This phase exists to close that gap. On Windows, MXC process containment can generate activity evidence that shows what the workload attempted to access, so teams can refine policy before production enforcement. Use this phase to capture real operating behavior, not only a scripted happy path. Include first-run setup, authentication, updates, error recovery, and low-frequency workflows. MXC now supports three operating states during policy development:- Enforcement: ungranted access is blocked; no activity report. Use when running production policy.
- Learning - enforced + recorded: ungranted access is blocked and recorded in an activity report. Use to diagnose containment failures and confirm only required access is granted.
- Permissive - allowed + recorded: access that policy would deny is allowed but recorded. Use in controlled pilots to observe behavior without interrupting users.
2. Develop the minimum policy that supports the workload
Translate validated activity into least-privilege policy. Prefer explicit access to the folders, domains, and tools the workload requires. Keep policy modular so a risky capability can be adjusted without reopening the entire environment. Record the rationale, owner, review date, and emergency rollback for every exception.3. Validate in deployment rings
Use rings that increase both scale and diversity. A practical pattern is:- Ring 0 — technical validation: limited number of users operated by the deployment team; prove assignment, version checks, telemetry, exclusion, and rollback.
- Ring 1 — informed early adopters: limited number of users close to the workload; validate real tasks and support documentation.
- Ring 2 — limited production: increased scale of users across representative device and network conditions.
- Ring 3 — broad deployment: expand only after success criteria and support capacity are met.
4. Match enforcement to confidence
Treat containment posture as a lifecycle decision. Early-stage workloads often have unclear dependency patterns, so start them in an observe-first posture to gather evidence and reduce disruption. As behavior becomes predictable and policy coverage is proven, promote those workloads to full enforcement. For mission-critical workloads, predefine a break-glass fallback (for example, temporary permissive mode) so operations can continue if a policy issue unexpectedly blocks business work. That fallback must be tightly governed: limited duration, explicit approval, full logging, post-incident review, and a named owner accountable for returning to enforcement. This keeps continuity without turning exception handling into a standing loophole.5. Preserve an opt-out and rollback path
Test exclusion as a first-class deployment feature. Confirm that removing a user or device from assignment removes the intended settings and that previous values return to the expected state. Document whether groups are user- or device-based, who can modify membership, propagation time, and what users should do while rollback completes.Create and distribute Microsoft Execution Containers (MXC) policies through your endpoint and mobile device management (MDM) system
Your endpoint management service or mobile device management (MDM) system is an enterprise distribution point for MXC policy. It turns the containment decisions developed from the observe-before-enforce evidence phase into managed configuration that can be assigned, validated, expanded, and rolled back consistently across eligible Windows devices.Build the policy
In the MDM admin center, select the agent, then configure it to run in an MXC container, define approved file-system locations with read or write permissions, and set network access. Before assignment, confirm that targeted devices run an MXC-capable Windows build and that the supported agent version is installed. Use observations from the observe-before-enforce evidence phase, not as a complete policy specification, but as signal. Its results can help create file, registry, clipboard, and UI access policies; other recorded activity does not map directly to policy settings, and some resource failures are not logged. Review the file paths, network destinations, and tools required for validated workflows, then configure the applicable supported controls and test the workload with containment enabled. Keep exceptions explicit, owned, and reviewable. Where the management experience supports it, separate policy modules so an organization can change one resource boundary without reopening every permission.Configure MXC with Intune (Private Preview)
-
Define the containment objective
- Decide which agent workloads the policy should cover (all MXC-capable agents, or a specific agent such as GitHub Copilot CLI).
- Set the principle of least privilege for file, network, and tool access. Treat Intune MXC policy as the enterprise ceiling for access. User/session guardrails may be available within agents, so users can further scope access within IT-defined limits.
-
Scope policy in Intune
- Create an MXC containment policy in Intune.
- If needed, scope by agent so one policy applies only to a named agent workload.
-
Configure file system boundaries
- Allow read/write and read-only access as appropriate to locations needed for work, troubleshooting, context or agent functioning (e.g. the agent’s own install path, script execution tools).
- Deny access to sensitive locations (for example, corporate OneDrive folders, program files, core system files).
-
Configure network and runtime controls
- Define allowed and blocked network destinations.
- Configure whether permissive operation is allowed for approved diagnostic/pilot scenarios.
-
Publish and validate policy
- Assign it to the target device/user groups (pilot first, then broader deployment rings).
- Confirm policy applies successfully on eligible Windows devices.
- Validate that normal development workflows still function inside approved boundaries.
-
Verify expected developer behavior
- Inside approved write scope : agent can inspect and modify files.
- Outside approved write scope: agent can read but cannot modify them.
- Denied sensitive paths: access attempts are blocked
-
Operate as a controlled lifecycle
- Start with pilot assignments, monitor outcomes, then expand by ring.
- Keep exception paths explicit, time-bound, and approved.
- Roll back assignments if a policy change impacts business-critical workflows.
Package the complete deployment
Microsoft Intune policy is only one part of the MDM deployment. Coordinate the following assignments and prerequisites:- Agent readiness: deploy or update the supported agent version and use detection logic to identify eligible installations.
- MXC configuration: assign container execution, file access, network access, and related managed settings.
- Security configuration: deploy Microsoft Defender AI agent runtime protection settings through supported Microsoft Intune or other MDM policies or centrally managed scripts, as appropriate for the selected inspection method. More information on how here: https://learn.microsoft.com/en-us/defender-endpoint/configure-ai-agent-runtime-protection#deploy-settings-throughout-your-organization-with-microsoft-intune
- Operations: publish user communications, support guidance, diagnostics, escalation ownership, and rollback instructions before promotion.
Validate delivery before expanding
Use Microsoft Intune or other MDM reporting to confirm that targeted eligible devices received and applied the policy. Validate the effective MXC behavior on representative endpoints, not merely that assignment succeeded. Test normal workflows, expected denials, agent-version sequencing, exclusion, and rollback. A production gate should require reliable policy application within the organization’s standard MDM service levels and evidence that administrators can create, assign, and validate the policy without engineering assistance.Monitor agent activity and respond through Microsoft Defender and Microsoft Purview
After Microsoft Intune or other MDM distributes the policy, Microsoft Defender and Microsoft Purview provide complementary operational views. Defender focuses on agent inventory, runtime threats, alerts, investigation, and endpoint response. Purview applies data loss prevention controls when an agent handles sensitive information. Together with MXC execution telemetry, they help security teams distinguish malicious activity, incomplete policy, product defects, and expected limitations.Use Microsoft Defender for runtime protection and investigation
Onboard eligible devices to Microsoft Defender for Endpoint, keep Microsoft Defender Antivirus and security intelligence current. Ensure Antivirus is running with real-time protection enabled. Enable AI agent runtime protection using agent-native event inspection, network inspection, or both, according to the target agent’s supported inspection methods. Begin in Audit mode for early rings so activity is inspected and reported without interrupting the agent. After validating alert quality and workflow compatibility, move mature rings to Block mode. In Block mode, Defender stops supported malicious activity and can notify the user in the agent and through Windows Security. Confirm that local agents appear in the Defender local AI agent inventory. For an investigation, review the agent record, device timeline, related incident, initiating user, process tree, network activity, and protection state. Use Advanced Hunting where deeper correlation is required. The rollout should demonstrate that a prompt-injection attempt or other supported malicious behavior produces the expected alert in Audit mode and is prevented in Block mode.
Use Microsoft Purview to protect sensitive data
Configure Microsoft Purview Endpoint Data Loss Prevention for supported local agents. Define the sensitive information types and agent interactions the organization needs to govern, scope the policy to the intended agents and endpoints, and choose an enforcement action. Purview can evaluate sensitive data used in prompts, tool invocation, and tool output where supported. A matched rule can block the interaction and explain to the user that organizational data-protection policy prevented the action. Start with a controlled test policy—for example, blocking a test sensitive-information pattern for the target agent—then wait for policy synchronization and verify the effective policy on the endpoint before testing. Exercise both direct prompt sharing and agent access to a test file. Expand the rule only after confirming that detections are accurate and that legitimate workflows remain usable. Keep policy creation centralized; endpoint enablement and policy receipt should be validated per device, but administrators should not recreate the Purview policy on every endpoint.
Define the response loop
- Detect: receive an MXC denial, Defender alert, Purview DLP event, or anomalous behavior signal.
- Establish context: identify the agent, user, device, process chain, tool, file or data type, network destination, and effective protection mode.
- Classify: determine whether the event is malicious, an expected workflow blocked by incomplete policy, a product or capability gap, or a by-design limitation.
- Contain: use Defender endpoint response, Purview enforcement, identity controls, MXC policy, or MDM group exclusion as appropriate.
- Correct and validate: adjust the workload or policy, retest in a lower ring, and confirm the expected Defender and Purview evidence before redeployment.
- Learn: update the inventory, policy rationale, support article, detection logic, and ring-promotion criteria.
End-to-end deployment example: GitHub Copilot CLI
Consider a managed rollout of GitHub Copilot CLI with MXC protections. The enterprise begins by identifying the supported Windows build and the oldest GitHub Copilot CLI release it will allow for rollout. It then enables GitHub Copilot CLI and its managed settings for the GitHub enterprise, creates target and opt-out groups, and validates the required identity and security settings. Endpoint management then assigns the CLI configuration and MXC policy to a small test group. The team exercises representative workflows in Learning Mode, including repository access, shell commands, tool invocation, authentication, network calls, update behavior, and failures. Reviewers convert legitimate activity into a least-privilege policy and investigate anything unexpected. They confirm that unsupported devices are handled safely, that eligible devices receive the intended configuration, and that exclusion reverses assignment. After technical validation, the team expands to informed early adopters, then to a limited production cohort, and finally to broad deployment. At each gate, it reviews reliability, task success, performance, alerts, support contacts, and unresolved blockers. Native endpoint-management policy replaces temporary scripts wherever possible, and every ring has a documented rollback and support route. If your company is using Codex by OpenAI, you can read their guidance on enabling MXC and Windows deployment.Operational checklist
- Inventory agents, workloads, tools, identities, files, endpoints, and child processes.
- Confirm OS, agent, and management prerequisites on representative devices.
- Define the roles of MXC, endpoint management, identity, endpoint security, data security, and service governance.
- Create target and opt-out groups; document membership and propagation behavior.
- For workloads using Windows process containment through the MXC SDK, start in Learning Mode and exercise normal, edge, and failure workflows; confirm that the agent works with containment enabled before rollout.
- Review observed activity and author least-privilege policy with owners and rationale.
- Define ring audiences, promotion criteria, pause criteria, and rollback steps.
- Validate native policy availability in the production management tenant.
- Confirm Microsoft Intune or other MDM assignment and effective MXC configuration on representative eligible devices, including required agent-version detection and update sequencing.
- Align security settings and monitoring before increasing scale.
- Publish user communications, a support article, diagnostics, and escalation routing.
- Verify opt-out and rollback in Ring 0.
- Review telemetry, alerts, performance, task success, and support volume at every gate.
- Keep uncertain workloads observable; enforce where confidence is sufficient.
- Time-box permissive fallbacks and review every use.
- Run a post-deployment review and update the reusable playbook.
Govern agents at scale
Secure agent adoption is not a choice between moving quickly and applying control. The practical path is progressive: observe real behavior, turn evidence into policy, enforce in measured steps, and preserve a safe way to recover. MXC provides the execution boundary, while the surrounding enterprise stack paired with Windows supplies identity, distribution, detection, data protection, and operations. When those layers are planned together, organizations can move agents from experimentation to dependable production use—and repeat the process for the next workload.
Pennsylvania, USA

TL;DR: What Your Velocity Chart Cannot Tell the CFO
Sooner or later, someone in your organization shows a slide with a number about what AI did for your team: typically, the team’s “velocity” before and after the coding agents arrived, plus a percentage that looks like a return on the token bill. The number may even be “correct”; however, it answers a different question than the one finance is asking: A before-and-after comparison credits every change in that period to the agents, and measuring velocity is controversial for good reason under normal circumstances, which makes measuring AI impact by this means even more challenging.
A claim your team can defend starts elsewhere: with an honest grade of the evidence, a break-even test for every delegated AI workflow, and the creep check of the AI Delegation Audit, which catches the workflows that pass the test only because nobody reviews their output anymore. Each workflow then gets a keep, change, or retire decision in the Re-classification Log, and the result fits on one page that states what the team can claim and what it cannot. Bonus: For your own work, a small trial of eight to ten runs gives you a direction you can act on.

Pennsylvania, USA
Next Page of Stories