 Log in

Apple Foundation Models bring local AI, the fm CLI, and Private Cloud Compute into the Mac developer toolkit. Here’s how to understand the architecture and find practical uses alongside tools like Ollama.

|
Sr. Content Developer at Microsoft, working remotely in PA, TechBash conference organizer, former Microsoft MVP, Husband, Dad and Geek.
|

Pennsylvania, USA


In one of my recent side projects, TwistReader, I had Claude Code add a test project for one of my MAUI app’s view models. That should have been a completely boring, mechanical task. Instead, dotnet build started hanging for exactly five minutes at a time, and it took a proper investigation to figure out why. I am sharing this because the cause isn’t really about MAUI. It’s about what happens when a normal dotnet build runs inside an AI coding agent’s sandbox on macOS, and I suspect more people will run into this as agentic tools become part of the daily workflow. The first hang The plan was simple: add a plain net10.0 target framework to the app project next to net10.0-maccatalyst and net10.0-ios, so a desktop xUnit test project could reference the view models without needing a MAUI workload. This is the documented pattern, and it’s what I would normally just do without thinking twice. Inside the agent’s sandbox, the build just sat there: 1 Determining projects to restore... For five minutes. Then it exited, having done nothing. Isolating the variable Before chasing any theory, I have run the exact same command in my own VS Code terminal, outside the sandbox. That build finished in 1.4 seconds. Same project, same machine, same SDK. The only difference was the sandbox itself. That one comparison turned a vague “something is slow” into a concrete, reproducible problem, and it’s the move I would recommend first whenever an agent reports a build issue you can’t immediately explain: reproduce it yourself, unsandboxed, before blindly trusting any diagnosis from an LLM. Wall #1: MSBuild’s worker-node IPC A diagnostic-level build log (-v:diag) showed exactly where the process froze: right after NuGet’s restore-graph walk dispatched an MSBuild task with BuildInParallel=true against one of the project’s references. That task spawns a separate, out-of-process MSBuild worker node and talks to it over a Unix domain socket, which is just IPC (inter-process communication, the general term for how two separate processes on the same machine exchange data, whether that’s a socket, a named pipe, or shared memory). Claude Code’s sandbox blocks bind() on Unix sockets for child processes, so the handshake never completes. A project with no references (my Domain layer, for example) never needs this and built fine, with no sandbox changes at all. The app project, with three references, hit it immediately. The fix is to force a single MSBuild node, so it never tries to spawn a separate worker process in the first place: 1 dotnet build src/TwistReader.App -m:1 -nodeReuse:false I originally credited a sandbox setting I had added, allowLocalBinding, as part of this fix. It wasn’t. That setting only controls IP/TCP port binding, not Unix domain sockets. Those are gated by a separate setting, allowUnixSockets / allowAllUnixSockets, that I never touched. The -m:1 -nodeReuse:false flags above work because they avoid the Unix-socket operation entirely, not because anything granted permission for it. Codex caught this while reviewing the PR for this post, and I had Claude verify it against the sandbox’s own source. Wall #2: task-host IPC for ILLink With that fix in place, the build got much further, all the way to compiling the app project itself, before failing with: 1 2 error MSB4216: Could not run the "ComputeManagedAssemblies" task because MSBuild could not create or connect to a task host with runtime "NET" and architecture "arm64". Same root cause, different subsystem. ILLink’s ComputeManagedAssemblies task always runs in a dedicated out-of-process task host, for isolation, and that’s the same kind of socket IPC the sandbox blocks. This one turned out to have a proper, maintained fix. dotnet/macios added _UseDesktopTaskAssemblies specifically for this class of problem, originally for iOS (PR #25417), later extended to MacCatalyst, macOS, and tvOS (PR #25662). It forces those tasks to run in-process instead: 1 dotnet build src/TwistReader.App -f net10.0-ios -m:1 -nodeReuse:false -p:_UseDesktopTaskAssemblies=true With both flags, a build of my app project for iOS went from a five-minute hang to 9 seconds, sandboxed. The property applies to the MSBuild task host itself, not to any particular IDE, which is why it fixes the same failure here: an IDE is just a wrapper around the same dotnet/MSBuild invocation, and it’s that invocation, not what’s driving it, that hits the broken task host. It’s kept as an explicit, supported override today. Wall #3: the one I couldn’t fix The same combination of flags did not get me all the way to a real app build. Apple’s actool, which compiles asset catalogs for app icons and splash screens, needs to talk to the CoreSimulatorService daemon over XPC and write scratch files outside the sandbox’s allowed paths. Both are blocked, the same way opening another app is blocked in this sandbox: 1 2 actool error: CoreSimulatorService connection became invalid. actool error: You don't have permission to save the file "..." in the folder "T". I haven’t found a settings-based fix for this one, and it hits iOS and MacCatalyst identically, since both compile the same asset catalog. My first thought was that this must be the same problem CI runners deal with: Xcode and CoreSimulatorService need an Aqua session (a GUI-bound launchd session), not a plain SSH session, and self-hosted CI docs are explicit about that requirement. But that theory doesn’t hold up here. My Mac already has a logged-in Aqua session running. When Claude routed the build through launchctl asuser to explicitly bind it to that session, nothing changed: same CoreSimulatorService connection became invalid error, same permission denials on the scratch folder. So it isn’t a missing-session problem the way it is on headless CI. Something in the sandbox is denying the XPC call and the filesystem writes outright, regardless of session. For anything that actually needs actool to run, I let Claude just bypass the sandbox for that one command for now. If you’ve run into this with Claude Code’s sandbox, or know a way to get actool/CoreSimulatorService working without turning the sandbox off entirely, I would like to hear and discuss about it. Reach out to me in the comments or on my socials. Conclusion Three separate restrictions were stacking on top of each other, and it would have been easy to misdiagnose the first one and stop there. Forcing a single MSBuild node and also ILLink’s task host in-process fixed two of the three, and they are now my default flags for any sandboxed MAUI local build. The third, image resource compilation, still needs the sandbox turned off entirely. As always, I hope this post is helpful for some of you. Until the next post, happy coding, everyone! Disclaimer: The first draft of this post was written by Claude while we were working through this investigation together in a live debugging session. I reviewed and edited it before publishing. The title image of this post was created by ChatGPT, based on a prompt Claude prepared for this task.
Pennsylvania, USA

It’s the most wonderful time of the year and I won’t hear a thing to the contrary. Here are some festive ideas if you’re shopping around for something on the nerdier side.
(And if any of you are Grinchily just looking to treat yourself, I approve of this and suggest you scroll straight to the bottom.)
Maker Advent Calendar
First things first as we’re running out of time — not just because this calendar sells out most years, but because we are perilously close to Advent and need to gather our baubles and get it together.
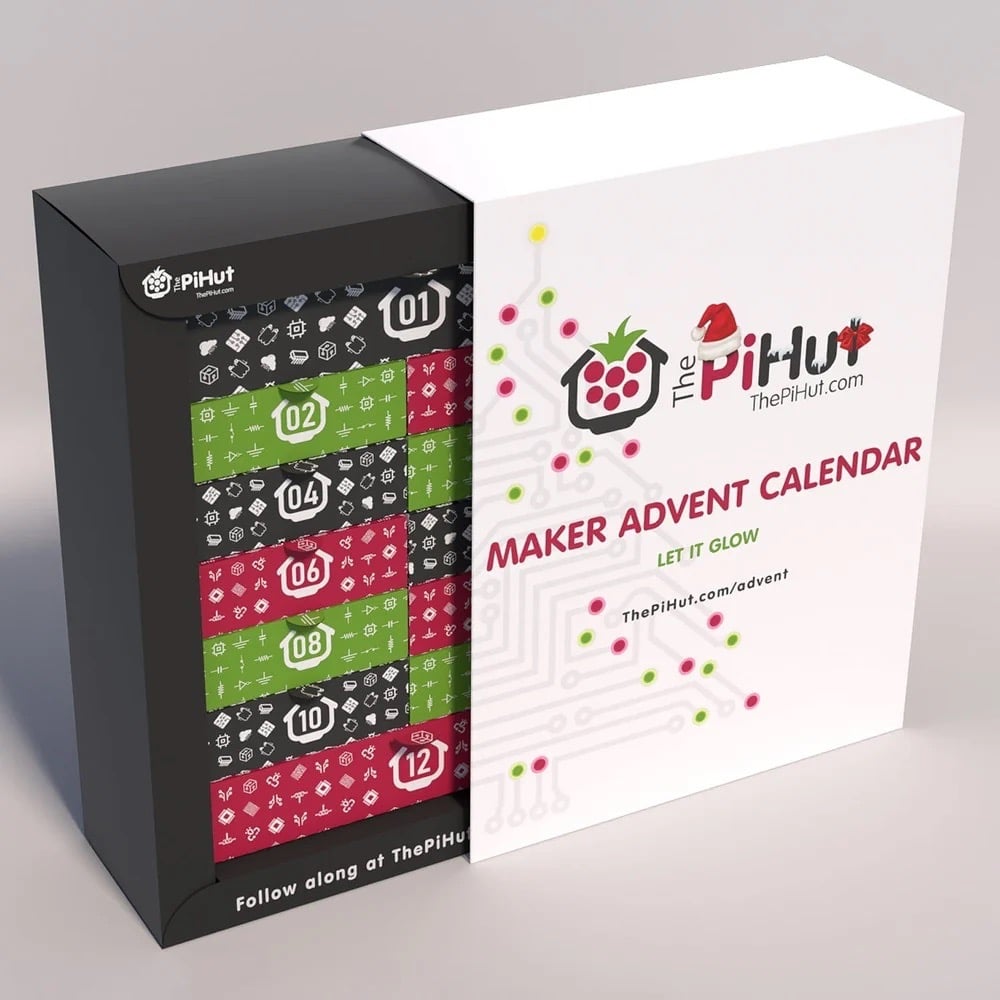
The Pi Hut’s Let it Glow Advent calendar features twelve days of fun dedicated to all things light up, flash, or blink. The first day of the calendar includes a Raspberry Pi Pico H microcontroller, a micro-USB cable, and a couple of breadboards to get you set up and ready for a December full of LED projects.
From December 1, you can follow along with The Pi Hut’s daily online box guides to help you make use of whatever you have just prised from behind that day’s calendar window. Sounds amazing.
Buy Maker Advent Calendar – Let it Glow (inc. Raspberry Pi Pico H) from The Pi Hut (£45).
Stocking fillers
If you’re not sure which boards, microcontrollers, or peripherals suit the needs and skill level of the maker you’re buying for, you can’t go wrong if you stick to the merry world of Raspberry Pi merchandise.
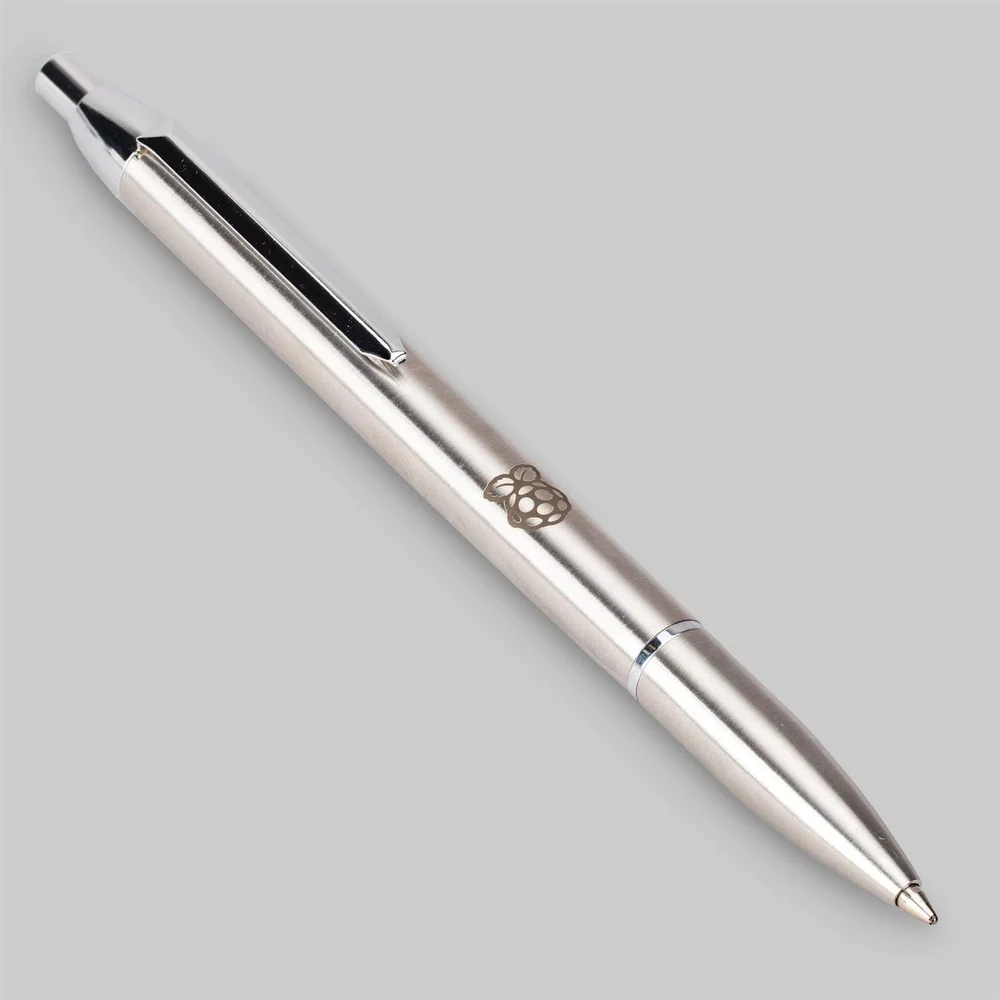
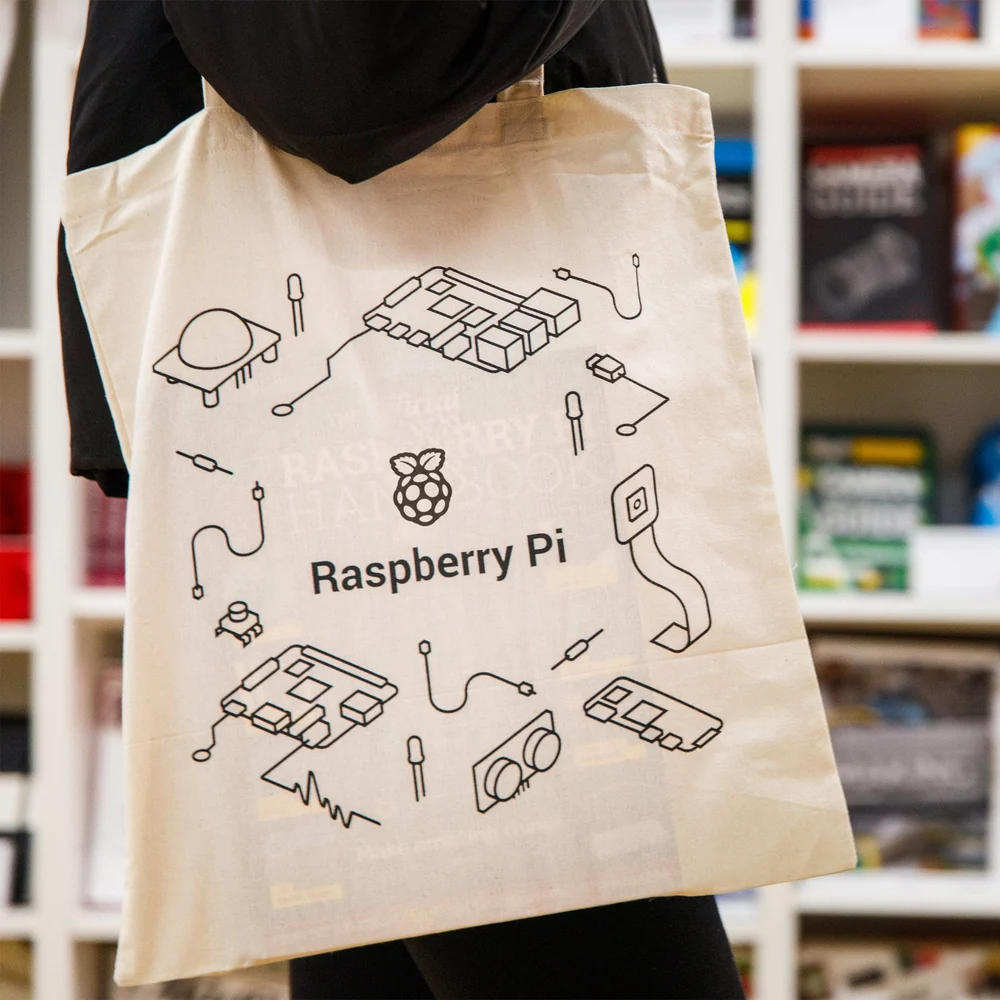
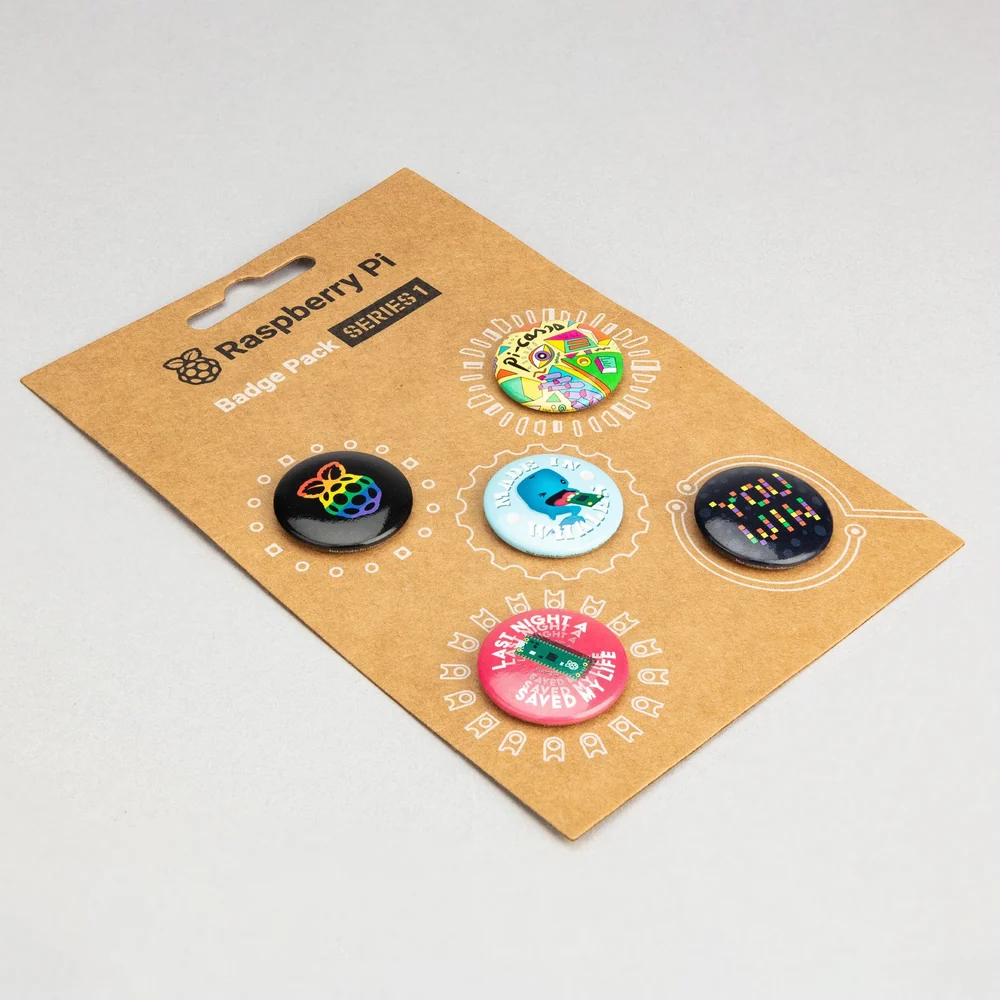
From mugs and mouse mats to stickers, tote bags, and clothing, there will be a bit of Raspberry Pi merch that will fit your gifting brief.

Pretty much all of our Approved Resellers offer merchandise for delivery. Visit our Raspberry Pi Approved Resellers page, scroll until you see your country or select ‘Rest of the world’, and get shopping!
Choosing the right hardware
I’ve tried to make a simplified list of groups of Raspberry Pi products to suit different styles of makers, as it’s likely you’re reading this blog as a gift-buyer for a Raspberry Pi lover and not necessarily a fan yourself. Here goes…
Plug-and-play desktops
If you want to gift someone a computer that just works, choose a Raspberry Pi 400, 500, or 500+. (You can save some money if the person you are buying for already has things like a mouse and an unused screen lying about…)
Raspberry Pi 400
Raspberry Pi 400 can be picked up from £57.60 if you don’t need additional bits like an SD card.
Raspberry Pi 400 is your complete personal computer, built into a compact keyboard. It’s also available as part of a complete kit including a mouse, a power supply, a preloaded SD card, an HDMI cable, and the official Raspberry Pi Beginner’s Guide. You can find these kits from £76.80.
Buy Raspberry Pi 400 (unit only) or a Raspberry Pi 400 Personal Computer Kit.
Raspberry Pi 500
Raspberry Pi 500 is a more refined and powerful model (available from £172.80) if you think the user will want to push their personal computer a little harder. This model is also available as a standalone unit or a full kit, from £192.
Buy Raspberry Pi 500 (unit only) or a Raspberry Pi 500 Desktop Kit.
Raspberry Pi 500+
If you are looking to push the boat out, Raspberry Pi 500+ is our premium desktop computer that lives inside a backlit, tactile, clicky keyboard that can be fully customised. This is a good choice if you’re after an extra special treat for a confident maker who takes pride in the way their workstation looks.
No screen? No stress.
If your giftee hasn’t got a display going spare, you can pick up an official Raspberry Pi Monitor, which is designed to work perfectly with all of the options above.
The prices listed above are cited online by Raspberry Pi Approved Resellers at the time of writing and do not include local taxes or shipping costs.
Affordable fun to throw inside multiple projects
If you know a maker who tends to burn through lots of hardware and is always showing you their latest build, they will probably be happier with a handful of our most affordable microcontrollers so they feel more confident to tinker away, break things, and have a go at new ideas.
Raspberry Pi Pico 2
Raspberry Pi Pico 2 is the next big tiny thing in computing. It’s a powerful, flexible microcontroller, available from £4.80.
You can pay a tiny bit more for a board with headers if you’re buying for someone who doesn’t own a soldering iron. And you can choose a Raspberry Pi Pico 2 W if you think they would benefit from having wireless capabilities. If you want both of those things, go for a Raspberry Pi Pico 2 W with headers.
But you can’t go wrong with a regular Raspberry Pi Pico 2 — they will definitely find something to do with it!
Niche choices for confident makers
If you know nothing about Raspberry Pi but you KNOW the person you got for Secret Santa is a true turbo nerd who could build an entire robot by themselves, they might get a kick out of some of these more niche products.
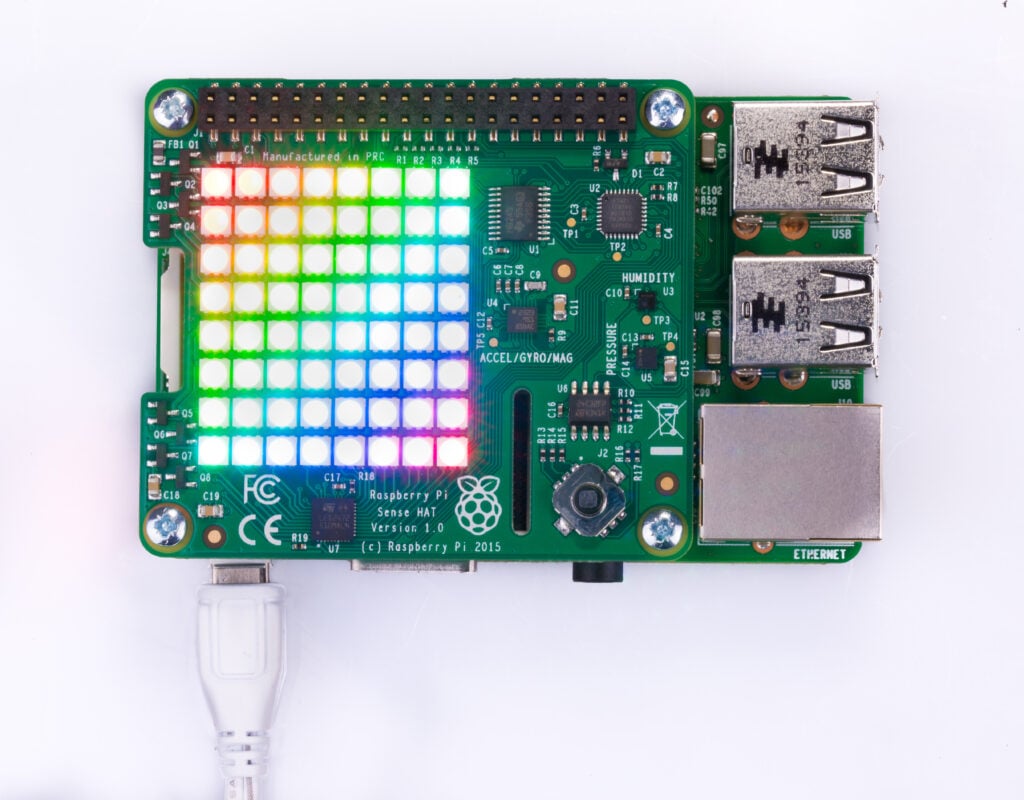
The Raspberry Pi Sense HAT is an add-on board that gives Raspberry Pi an array of sensing capabilities, allowing you to monitor pressure, humidity, temperature, colour, orientation, and movement. The bright 8×8 RGB LED matrix visualises data from the sensors, and the five-button joystick lets users interact with your projects.
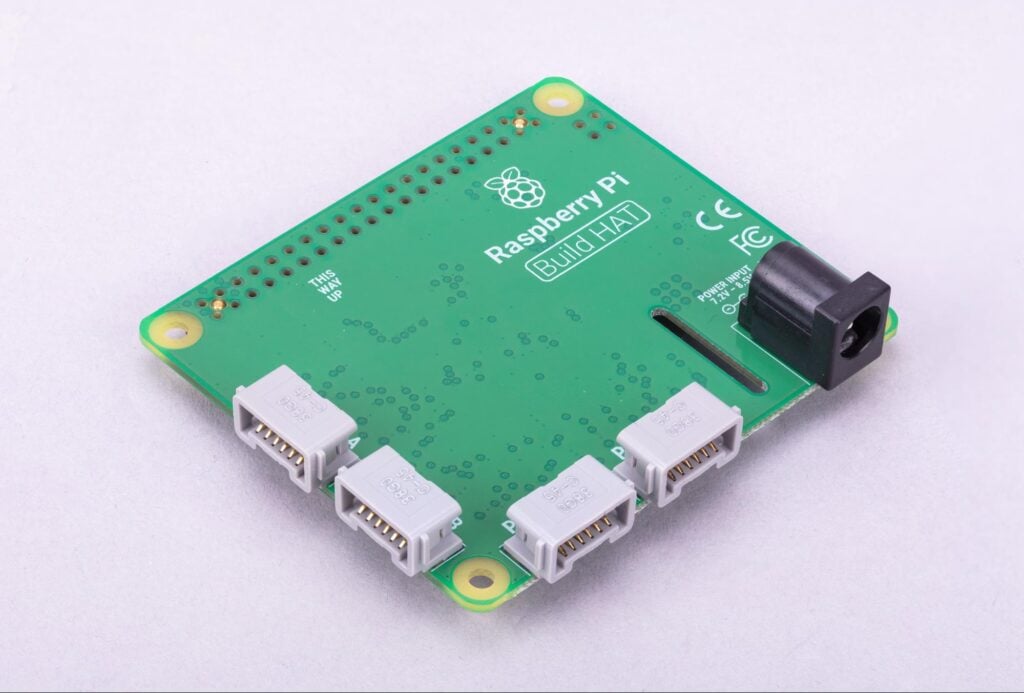
The Raspberry Pi Build HAT allows you to build robust, intelligent machines that combine Raspberry Pi computing power with LEGO components. (Also a great excuse to buy LEGO stuff!)
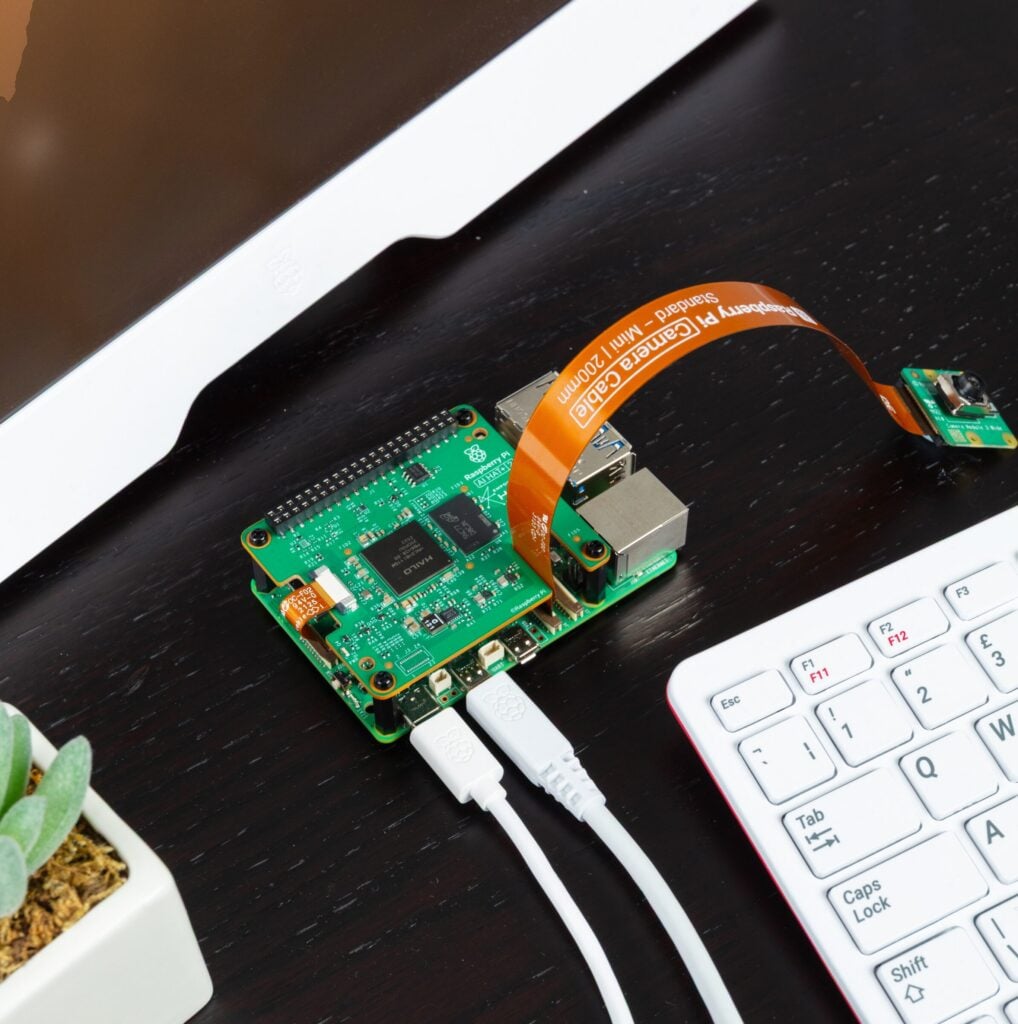
If generative AI is an achievable step for the maker in your life, and they already own a Raspberry Pi 5, the Raspberry Pi AI HAT+ 2 will blow their mind. Pair it with the Raspberry Pi AI Camera, which does vision AI on the camera itself, and you’re well on the way to a bird feeder that knows a robin from a blue tit.
Raspberry Pi for your bookshelf
Hardware is only half of the fun; the other half is working out what to build with it. Raspberry Pi Press has been busy this year, releasing a number of new titles you could gift someone on your nice list.
(Plus, books are the easiest thing to wrap, so it’s a no-brainer that will make the recipient brainier.)
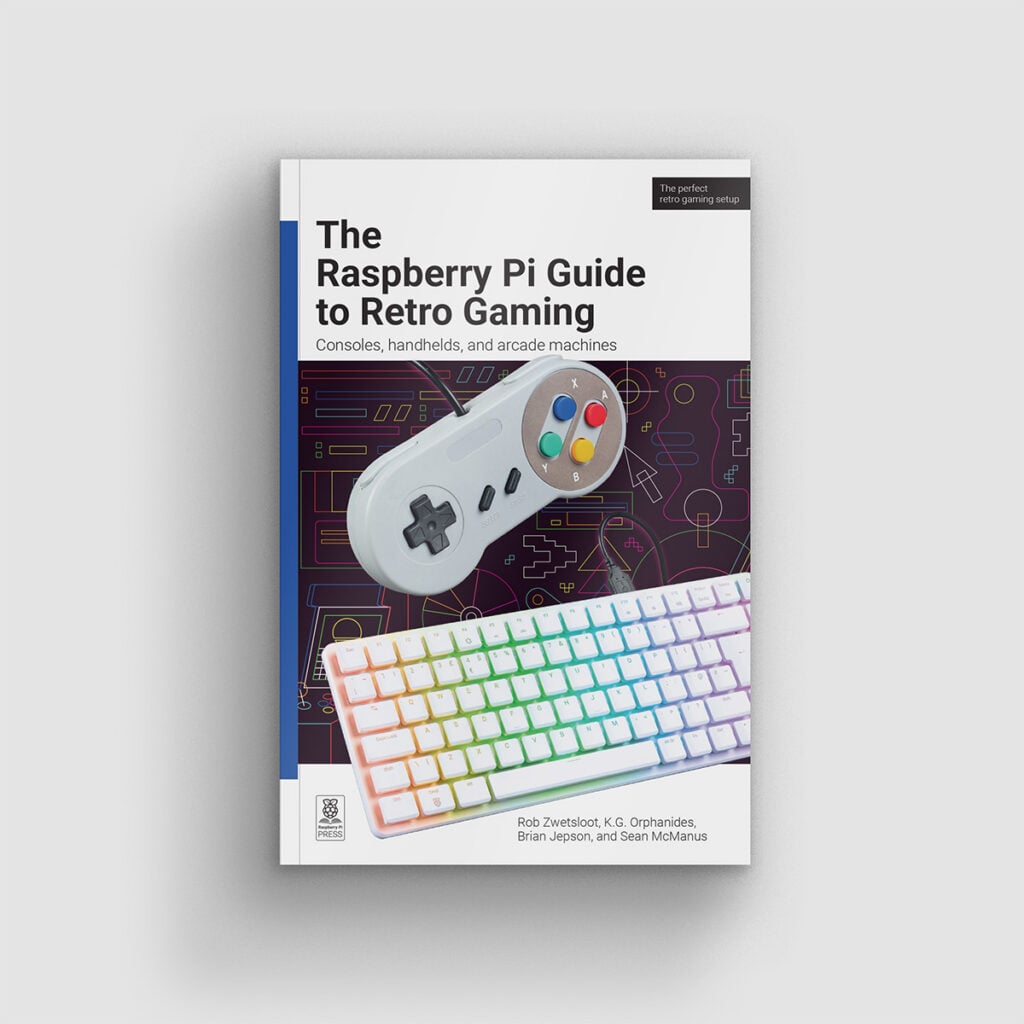
Raspberry Pi Guide to Retro Gaming
£9.99
Creating the perfect retro gaming setup in the comfort of your own home is easy with a Raspberry Pi.
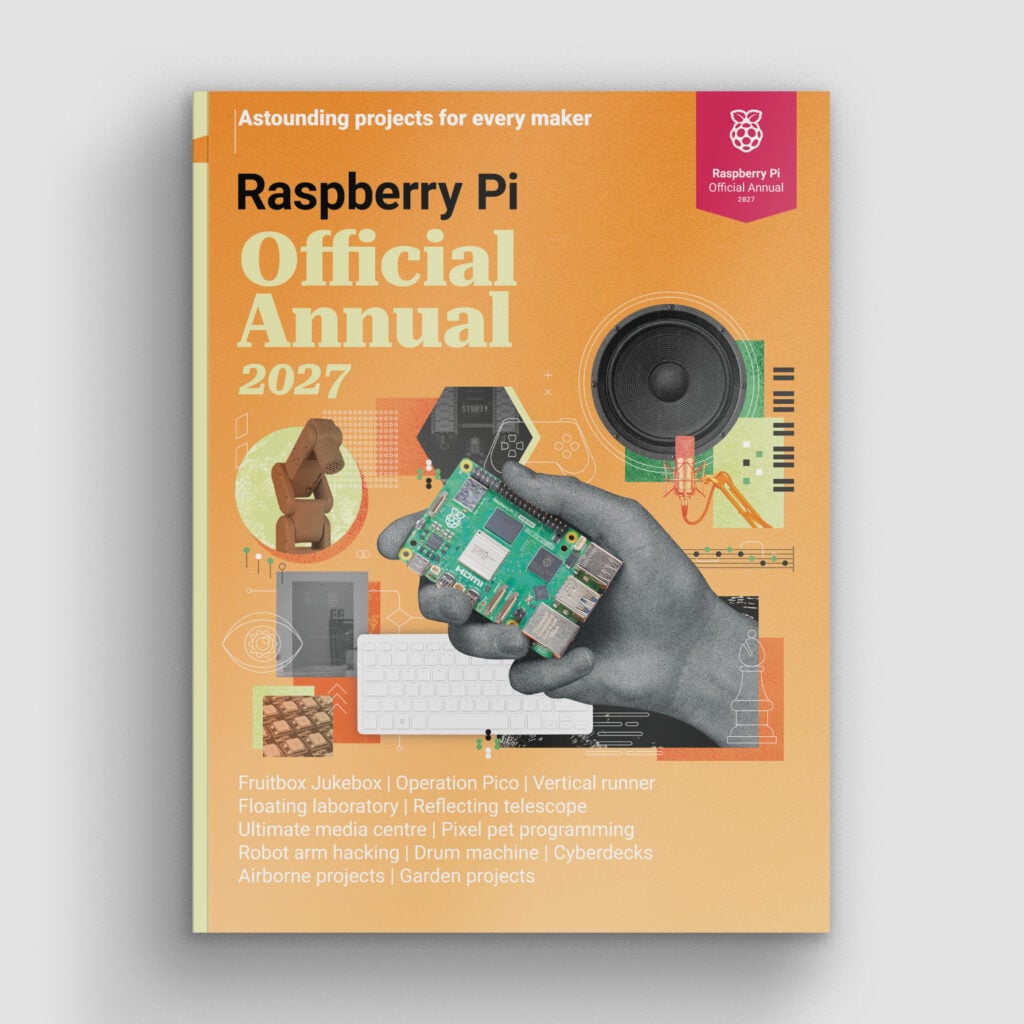
Raspberry Pi Official Annual 2027
£7.00
A big, chunky book of tutorials, projects, guides, and reviews. Yes, it’s 2027 already — at least on the cover. Consider it a stocking filler from the future.
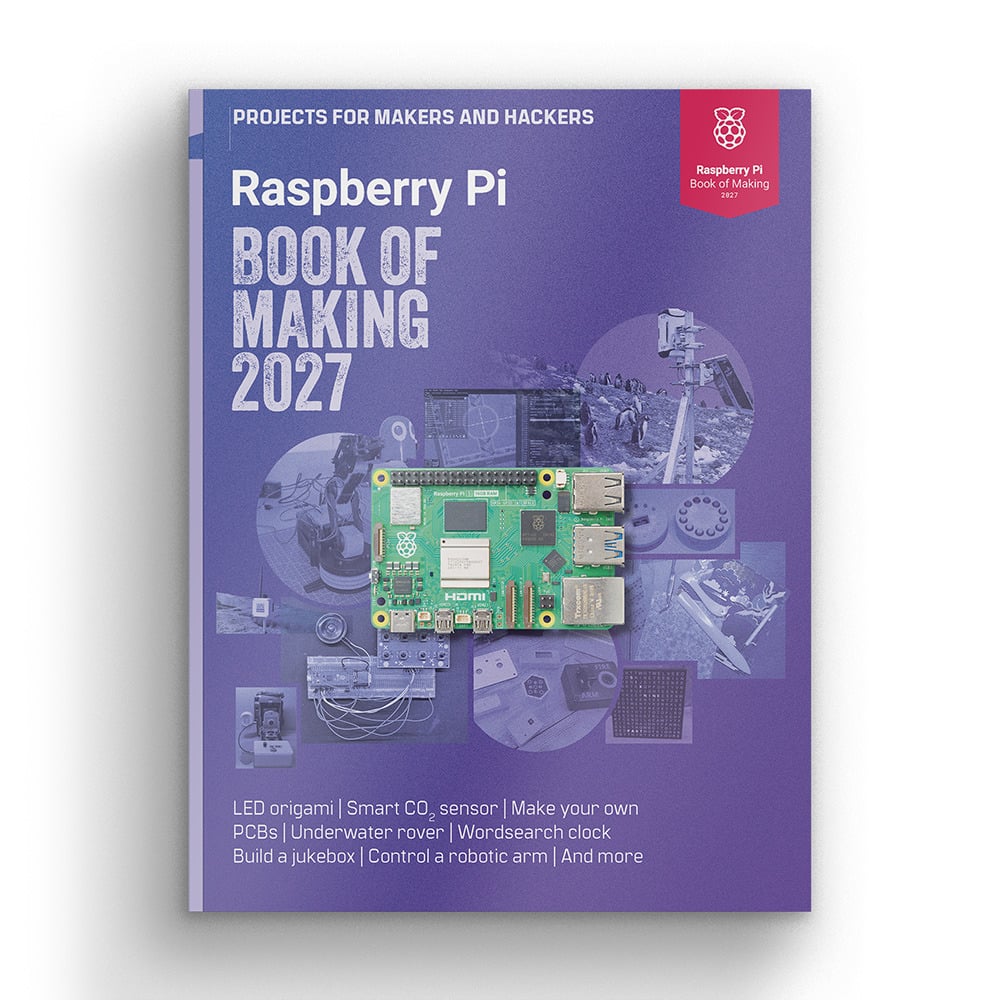
Raspberry Pi Book of Making 2027
£7.00
A digital-focused making book for anyone whose “one quick project” list has quietly become a spreadsheet.
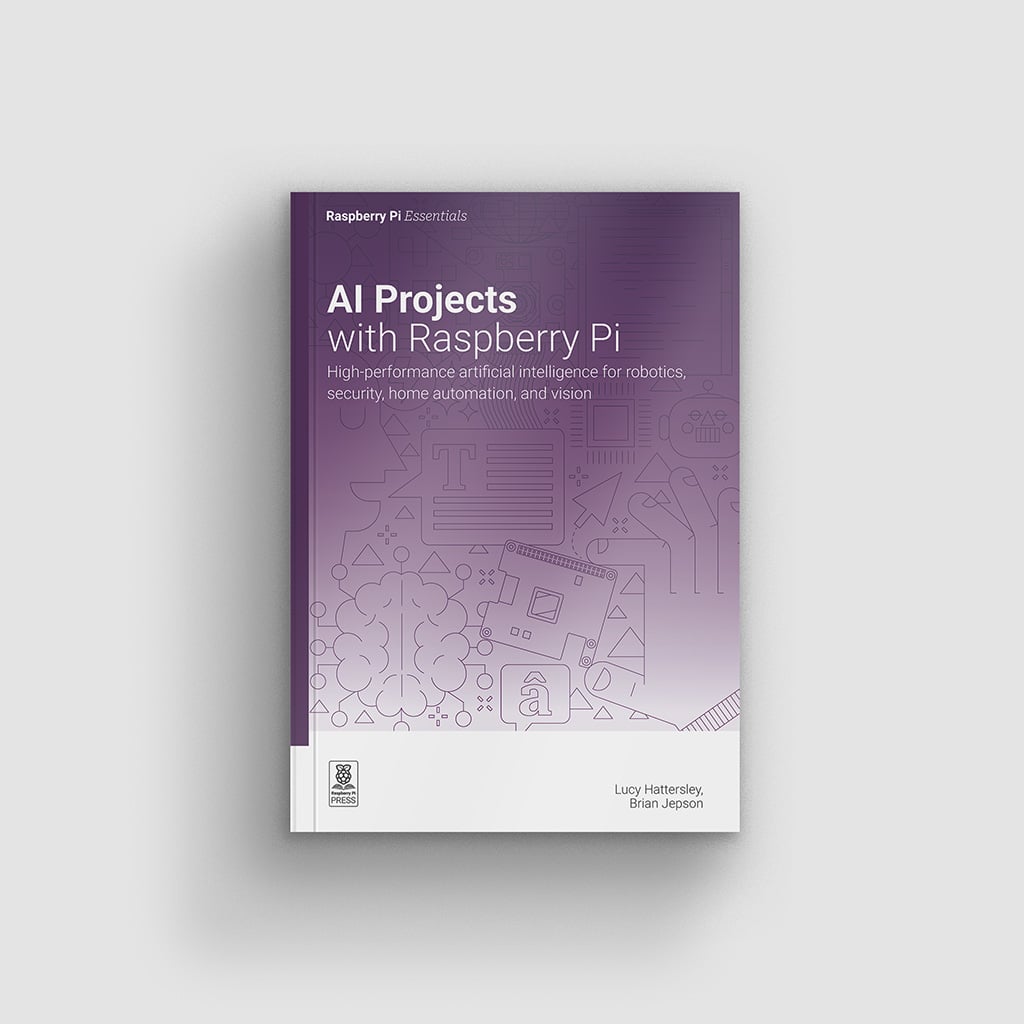
AI Projects with Raspberry Pi
£8.99
The perfect companion to our AI HATs and cameras. Build AI-powered projects that are clever, useful, or both.

Unplugged Tots
£19.99
Introduce your child to the foundations of computer coding and teach them the skills to take on their future, now.
Python Projects for Raspberry Pi
£19.99
Python that reaches out of the screen and pokes the real world: lights, sensors, buttons, and the general satisfaction of making something happen.

Buy a quick gift for yourself…
And if you need that fleeting but irrefutable high of buying and receiving something right now, we have good news…
We launched a brand new e-book offer this week, and better still, you can name your own price and get reading right away. The Humble Tech Book Bundle: Raspberry Pi Cyberdecks, Retro Games, and More from Raspberry Pi Press features five new books published this year, as well as some titles from years past.
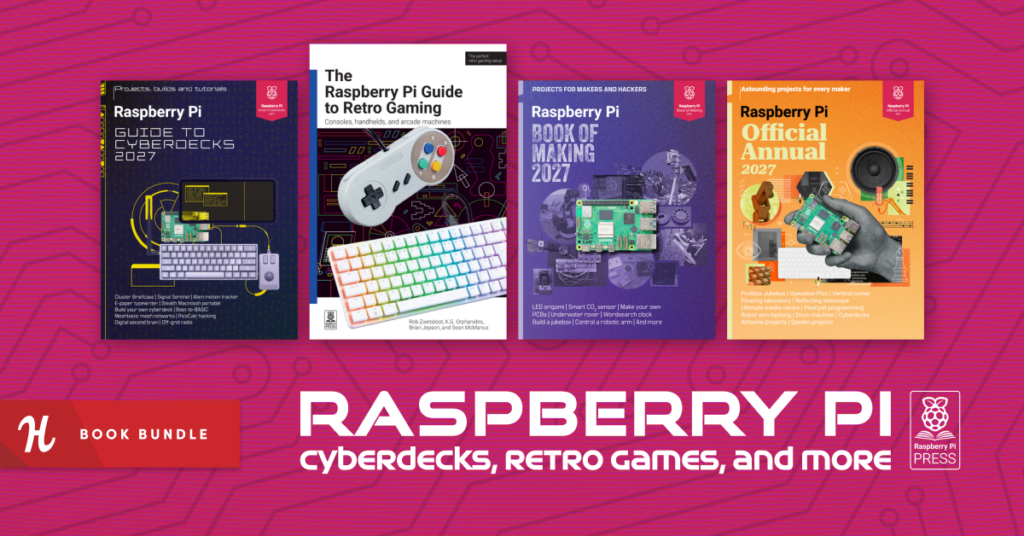
Perhaps most excitingly, the bundle includes the Raspberry Pi Guide to Cyberdecks 2027, which is exclusive to Humble Bundle donators — the rest of us won’t be able to get our hands on it until it is officially published next year!
Pay as little as £4 ($5). Normally, the total cost of the books included in this bundle is as much as £255 ($341), but you can choose the price you pay and support the Raspberry Pi Foundation in the process.
Check out all of the titles available in this brand-new Humble Bundle.
The post Raspberry Pi gift ideas for nerds appeared first on Raspberry Pi.
Pennsylvania, USA
Not every search problem requires AI, embeddings, or vector databases.
Most business applications simply need to handle real-world data imperfections: misspelled customer names, inconsistent product descriptions, duplicate records, incomplete entries, and user input that rarely matches stored data exactly. Traditional string-matching techniques such as LIKE, CHARINDEX, PATINDEX, Full-Text Search, and even Regular Expressions solve many search scenarios, but they often struggle when the data itself is imperfect.
In this session, we'll explore the newest fuzzy string-matching capabilities in Azure SQL and SQL Server and see where they fit within the broader SQL search ecosystem. Through practical demonstrations, we'll compare fuzzy matching against existing approaches including LIKE predicates, Full-Text Search, and Regular Expressions, helping you understand the strengths, limitations, and ideal use cases for each technique.
Using real-world scenarios such as customer lookup, product search, duplicate detection, master data management, data cleansing, and application search experiences, you'll learn how to build typo-tolerant and user-friendly applications without introducing unnecessary AI complexity.
✅ Let's connect:
LinkedIn - Anna Hoffman, https://www.linkedin.com/in/amthomas46/
Twitter - AzureSQL, https://aka.ms/azuresqltw
LinkedIn - Iqra Shaikh, https://www.linkedin.com/in/shaikhiqra/
🔴 Watch even more Data Exposed episodes: https://aka.ms/dataexposedyt
🔔 Subscribe to our channels for even more SQL tips:
Microsoft SQL / Azure SQL: https://aka.ms/msazuresqlyt
Microsoft SQL Server: https://aka.ms/mssqlserveryt
Microsoft Developer: https://aka.ms/microsoftdeveloperyt
#AzureSQL #SQL #LearnSQL

Pennsylvania, USA

Titles we almost went with this week
- Honey, I Shrunk the Cloud SQL Disk Using DMS
- EKS Auto Mode Opens the Gateway, and Ingress Gets Put Out to Pasture
- Cap It Like It’s Hot: Google Cloud Budgets Get Teeth
- Claude Code Eats OpenAI’s Lunch While Investors Check Their Wallets
- Google Cloud Spend Caps: Because “Oops” Shouldn’t Cost Five Figures
- Step Functions Teaches AI Agents to Follow the Steps
- Google Cloud Lets You Run VMware Yourself: Bare Metal, Bare Hands
RDS Snapshot Billing Finally Lets You Snap Back at Your Costs
Vault Me Maybe: Giving AI Agents a Real ID
Pacific Cable Sabotage Risk Has Big Tech Feeling Deep-Sea Anxious
A big thanks to this week’s sponsors:
We’re sponsorless! Want to get your brand, company, or service in front of a very enthusiastic group of cloud news seekers? You’ve come to the right place! Send us an email or hit us up on our Slack channel for more info.
Follow Up
01:19 Follow up from Show 372 – Are Microsoft’s recently patched vulnerabilities
being found internally or by outside researchers?
- Item to be followed up on: Determine whether Microsoft’s CVE discoveries are found internally or externally (A host states whether Microsoft’s recent surge in patched vulnerabilities came from internal AI-assisted discovery versus external researchers.)
- What we said in Episode 372: “Kind of what I wonder with some of these also is where are they finding the vulnerabilities? Is it end users who are finding them still, or external people, or is it them doing it internally and finding them? And they don’t really share those types of metrics.” [5:03] — Justin
- What was learned: Both — Microsoft has confirmed it’s a mix of internal AI-assisted discovery and external researchers (increasingly also using AI), and Microsoft has started sharing some detail on this split rather than staying fully silent.
- Microsoft’s MSRC blog says a larger share of this month’s patched issues were found internally, with many surfaced through AI investments.
- Microsoft credits a new multi-model AI-driven scanning harness (MDASH) with finding 16 vulnerabilities in one month, including 4 critical, before any human researcher.
- Some vulnerabilities were also credited to external researchers who collaborated with AI tools.
- Links for more information:
- https://www.microsoft.com/en-us/msrc/blog/2026/05/a-note-on-patch-tuesday
- https://blogs.windows.com/windowsexperience/2026/07/09/evolving-windows-vulnerability-management-to-meet-the-speed-of-ai-powered-discovery/
- https://www.microsoft.com/en-us/security/blog/2026/05/12/defense-at-ai-speed-microsofts-new-multi-model-agentic-security-system-tops-leading-industry-benchmark/
- https://www.microsoft.com/en-us/security/blog/2026/10/07/3-lessons-from-frontier-ai-vulnerability-research/
- https://www.bleepingcomputer.com/news/microsoft/microsoft-expects-more-windows-security-updates-from-ai-discovered-flaws/
General News
05:09China’s snooping around Pacific undersea cables raises risks for Big Tech – Ars Technica
- A new US-China Commission report ranks trans-Pacific subsea cables by sabotage risk, and Google- and Meta-owned routes land near the top, which matters for anyone relying on cloud backbone connectivity across the Pacific.
- The report, produced by the China Strategic Risks Institute for the US-China Economic and Security Review Commission, includes an interactive Vulnerability Index that ranks trans-Pacific cables by gray zone sabotage risk.
- Risk factors include seabed depth, nearby shipping traffic, cable ownership, proximity to China’s exclusive economic zone and broader territorial claims, and whether the cable connects to Taiwan.
- Most cable damage still comes from accidents like trawling nets and dragged anchors, but analysts are paying closer attention to suspicious incidents, including Chinese commercial ships under investigation for cable cuts in European and Asian waters and Chinese research vessels spending unusual time surveying cable routes.
- For cloud users, hyperscaler-owned private cables carry inter-region replication, backups, and AI training traffic, so a cut could mean higher latency or degraded cross-region failover.
- It is worth revisiting multi-region architectures that assume trans-Pacific paths are always available.
- The index could help prioritize where to place monitoring sensors and patrols, which raises the question of how much cable security should be a provider responsibility versus a government one.
06:42 Matt – “It’s an unprotected asset out there now… it’s another attack vector, and why you should always encrypt everywhere.”
AI Is Going Great – or How ML Makes Money
21:11 OpenAI Raises Less Than Half of $30 Billion Target in Latest Round
- OpenAI’s latest funding round is falling well short of target, and the numbers behind it say a lot about where the AI trade stands heading into a likely IPO.
- OpenAI has secured roughly $11 billion in commitments against a $30 billion target, at a $1.25 trillion valuation versus the $1.4 trillion it originally sought. It now hopes to raise up to $20 billion by courting family offices and high net-worth individuals.
- Investor appetite is cooling amid a broader tech selloff tied to disappointing earnings from Google, Amazon, and Intel.
- Investors are growing pickier about AI funding terms, which matters for cloud providers whose capex plans depend on continued AI demand.
- Anthropic’s Q1 to Q2 revenue more than doubled to $11.6 billion, with a small operating profit, versus OpenAI’s roughly 18% growth to $6.7 billion and deepening operating losses.
- Claude Code’s growth is cited as the main driver of Anthropic’s lead.
- OpenAI reportedly regained some market share from Anthropic after cutting prices on its latest models, according to third-party data. The price war could mean lower inference costs for developers and enterprises building on either platform.
- Both OpenAI (as soon as early next year) and Anthropic (expected next month) are heading toward public listings.
- Anthropic’s filing will give the first audited look at AI lab economics, which could reshape how the market values compute-heavy AI workloads and cloud AI spending.
10:53 Ryan – “The fact that this says that Anthropic has a small operating margin, like where they’re making profit, is crazy to me because I’ve never heard that anything AI makes a profit.”
12:06 Anthropic warns AI may soon begin recursive self-improvement
- Anthropic is warning that AI may soon begin recursive self-improvement, and it is floating the idea of a coordinated industry slowdown, which matters to anyone building on frontier models in the cloud.
- Anthropic says Claude now writes more than 80 percent of the code merged into its own systems, up from low single digits before Claude Code launched in early 2025, and engineers ship roughly eight times as much code per quarter as a few years ago.
- The company’s June 4 post “When AI Builds Itself” says recursive self-improvement (AI designing its successors with little human input) is not inevitable but could arrive sooner than institutions are ready for, raising the risk of humans losing control.
- Anthropic proposes a “global coordination mechanism” to slow or temporarily pause frontier development, loosely modeled on intermediate-range nuclear missile arms-control agreements.
- It gave few specifics beyond needing top labs to participate and a credible way to verify they slowed.
- Skeptics doubt feasibility and motive: Noah Giansiracusa of Bentley University calls a pause “literally impossible,” and Georgia Tech’s Mark Riedl calls it hype.
- The post also follows the withheld Mythos model, which was deemed too good at finding software vulnerabilities, and a confidential IPO filing.
- The practical takeaway is that AI-written code already makes up most of the output at a leading lab, raising questions about code review, security validation, and governance practices as AI coding tools spread into enterprise pipelines. Anthropic says it will spend the coming months convening governments, researchers, and rival labs to test whether a coordinated slowdown could work.
14:35 Ryan – “What I think they can’t do is get all of the China model providers, and other model providers globally, to agree. And I think that’s what you would have to do. Like, that’s why they’re comparing it to the nuclear missiles, is it’s more of a global concern because no one country wants to fall behind in their AI technology.” Security
- Cursor disclosed that a tampered copy of Anthropic’s Claude Code extension, version 2.1.313, was live in its VS Code extension marketplace for about 11 hours and tried to install an SSH backdoor on developer machines, which makes this a useful case study in IDE extension supply chain risk.
- Scope and timeline: The malicious package was available from roughly 2:27 am to 1:35 pm PT on October 29 and was not published by Anthropic. Cursor says at most 5,000 users were affected and it will contact them directly.
- Payload behavior: The extension collected hostname, username, OS, home directory, env var names, Git email, and public IP. It then tried to append an attacker SSH key labeled svc-telemetry to authorized_keys, enable the local SSH service, open a reverse tunnel, and persist via a LaunchAgent on macOS or a scheduled task on Windows.
- Limited blast radius, but still serious: Enabling the SSH service needs admin rights, so on most hosts the tunnel step failed. The key install, persistence scripts, and host-detail beacon still ran, and uninstalling the extension does not remove the standalone persistence scripts.
- Response and remediation: Cursor pulled the package, shut down and rebuilt the marketplace, rotated keys, audited other extensions, and had the hosting provider take down the attacker server.
- Users should check for the svc-telemetry key, run the provided macOS or Windows remediation scripts, and rotate credentials from a trusted system.
17:18 Ryan – “It’s a very limited blast radius but very serious.”
20:07 Introducing Zero Wire, a hub for investigating critical Internet vulnerabilities
- Cloudflare just launched Zero Wire, a public vulnerability intelligence feed on Cloudflare Radar aimed at helping security teams triage critical Internet-facing CVEs faster.
- Zero Wire is a curated feed rather than a full CVE catalog, focused on critical vulnerabilities in Internet-facing software such as web apps, runtimes, and exposed services. It is free to use and does not require being a Cloudflare customer.
- Each briefing is structured like an index card: plain-language explanation, who should investigate, recommended actions, and links to vendor advisories, CVE records, and CISA’s Known Exploited Vulnerabilities Catalog.
- Briefings are split into Needs attention and Reference, with a last-checked date and update chronology.
- The framing separates severity from evidence of exploitation, and Cloudflare adds network telemetry where relevant (for example, volume of requests matching WAF-managed rules for the php2shell PHP runtime issue).
- Cloudflare is explicit that matched requests are not a count of compromised systems.
- Each briefing includes a pre-built prompt for an AI agent to run a read-only assessment of deployed software, fixes, exposure, and compensating controls. Copying the prompt does not scan or change anything, so teams still need to run the assessment in their own environment.
- Cloudflare states a WAF rule is only a compensating control and not a substitute for patching, and that some issues fall outside the traffic it can inspect.
- Worth discussing whether a vendor-run advisory feed is trustworthy given the obvious tie-in to its own WAF products, and how this stacks up against existing sources like NVD and vendor advisories.
22:29 Ryan – “If you’re adding the context and the metadata of the vulnerabilities by the severity, you’re already sort of acknowledging that you can’t address everything, so I do think this will help a lot of teams because I think there’s really too much noise now in all the threat intel feeds.”
Cloud Tools
25:42 Building Self-Service into Terraform: Introducing Terraform Developer Portal
- HashiCorp has put Terraform Developer Portal into public preview, a native self-service layer in HCP Terraform that lets developers consume approved infrastructure without needing to know the underlying modules.
- Platform teams expose existing Terraform modules as curated Templates (for example, Create an Application Service) with defined inputs.
- Developers pick a Template, fill in the inputs, and Terraform handles provisioning.
- Provisioned infrastructure is represented as an Application, which can be extended with approved Add-ons such as a PostgreSQL database.
- Terraform Actions cover approved operational workflows beyond initial provisioning.
- It targets the tension between developer ease of use and platform team control: developers get a simpler catalog experience while platform teams keep governance over what gets provisioned and how.
- Agentic self-service is a notable angle. AI agents can discover available Templates, determine required inputs, and trigger provisioning or answer questions like whether the latest run succeeded, all through the same Terraform APIs and controls. tfctl and MCP are the programmatic and agent-discovery pieces.
- UI, CLI, API, and agents are positioned as different interfaces into one governed foundation, which is worth discussing against existing internal developer portal options like Backstage.
- It is available now in HCP Terraform accounts, with a getting started tutorial and documentation.
27:06 Ryan – “I don’t see any difference. We called this a service catalog back in the cloud custodian days.”
29:38 Strengthen security for agentic AI with new Vault, Verify, Boundary, and Secure Hub capabilities
- IBM and HashiCorp rolled out a roundup of agentic AI security updates across Vault, Boundary, Verify, and a new Secure Hub, aimed at treating AI agents as first-class identities in hybrid cloud environments.
- IBM Agent Identity is now GA and registers AI agents as first-class identities with ownership, delegated authority, task-scoped authorization, and audit trails, using Vault to protect agent credentials.
- Vault 2.2 adds vTPM support for Linux VMs so on-prem workloads authenticate with cryptographic proof instead of bootstrap secrets, addressing the Secret Zero problem. It also extends identity governance to AI and non-human identities, and adds PKI automation, public certificate management, and post-quantum readiness work.
- Vault Arc and Secure Hub are in public preview. Arc is a new Vault architecture with a new resource and IAM model, scoped and ephemeral authorization, and agent identity governance.
- Secure Hub gives centralized visibility, reporting, and governance across distributed Vault Enterprise and Arc environments.
- Boundary 1.1 adds app tokens, which let admins issue scoped, time-limited tokens for CI/CD and automation integrations in place of the previous multi-step, brittle authentication flow.
- Cross-account auto-discovery now needs the AWS plugin configured in only one account to discover VMs across multiple AWS accounts.
- Boundary also introduces an MCP server in public preview. Admins can manage and troubleshoot clusters in natural language from clients like Claude, Cursor, and Codex, and MCP-compatible agents can reach SSH and RDP targets through Boundary without custom code or client tools.
31:49 Ryan – “Agent execution and AI is changing the way we’re having to do identity. I think, you know, for a long time most of our use cases are we’ve been able to get away with, you know, acting on behalf of, right? But now we’re on the verge of those executions going to other environments, running on their own because you’ve configured them on a schedule.”
35:00 Introducing IBM Cloud Secrets Manager Vault Dedicated: HashiCorp Vault Enterprise, managed by IBM
- This week in new ways to spend all your money…
- IBM just launched a managed, dedicated version of HashiCorp Vault Enterprise on IBM Cloud, a notable early example of HashiCorp technology being folded into IBM’s cloud portfolio.
- IBM Cloud Secrets Manager Vault Dedicated runs Vault Enterprise on single-tenant infrastructure IBM operates, so customers skip deploying, patching, and running the Vault cluster themselves.
- It is positioned as a choice rather than a replacement: teams that want full operational control can keep self-managing Vault Enterprise, while others can hand infrastructure and operations to IBM and keep a consistent secrets and machine identity model.
- Vault’s existing integration ecosystem still applies, so the instance can secure workloads on IBM Cloud, on-premises, and in other clouds, which matters for hybrid and multicloud shops.
- IBM is pitching AI workloads as a driver: agents and AI apps need credentials for models, databases, APIs, and vector stores, and the same issuance, rotation, and audit controls apply to those machine identities.
- Worth noting: the launch is a concrete result of HashiCorp now being part of IBM, and the announcement is light on details like pricing, regions, SLAs, and how it compares to HCP Vault Dedicated, so those are open questions for listeners evaluating it.
AWS
36:38Amazon RDS for Oracle and SQL Server now support storage autoscaling on additional storage volumes
- AWS just extended RDS storage autoscaling to the additional storage volumes on Oracle and SQL Server, which matters if you’ve been hand-provisioning capacity on those big enterprise databases.
- Previously, autoscaling only covered the primary volume, so teams had to manually size each additional volume (up to three, for a total of 256 TiB). Now you set a maximum storage limit per additional volume, and RDS scales it up automatically with zero downtime.
- This addresses the classic trade-off: under-provision and risk application downtime, or over-provision and pay for unused capacity. Autoscaling monitors actual consumption and expands as utilization approaches provisioned capacity.
- Works on both new and existing database instances, and can be enabled through the console, CLI, or RDS API, so retrofitting into existing fleets should be low friction.
- No additional charge for the autoscaling feature itself. You only pay for the storage that is actually provisioned. Worth noting storage only scales up, so a maximum limit is the main cost guardrail.
- Available for RDS for Oracle and SQL Server in all commercial AWS Regions and GovCloud (US).
37:36 Matt – “It’s a great quality of life improvement for a feature that I didn’t know existed.”
38:52 AWS Step Functions workflows now available as AI agent tools
- AWS just made your existing Step Functions workflows callable by AI agents through the Bedrock AgentCore Gateway, giving agents a deterministic way to run business processes.
- Agents can now invoke Standard and Express Step Functions workflows as tools via AgentCore Gateway over the Model Context Protocol (MCP). The agent chooses when to run a workflow and what input to pass, while Step Functions executes each step exactly as defined.
- This addresses a core concern with agentic AI: non-deterministic behavior. Pushing multi-step processes like refund eligibility checks, manager approval, and crediting into a workflow means every run follows policy in the same order, regardless of how the model reasons.
- Agents can also look up workflow runs, so an operations agent could tell an on-call engineer which order runs failed overnight and at which step. That shortens the path from alert to fix.
- It reuses existing investments: Step Functions already orchestrates 220+ AWS services, so teams can expose current workflows to agents without rebuilding them.
- Available in all Regions where AgentCore Gateway is available, with no new pricing; you pay standard Step Functions and AgentCore Gateway rates.
40:18 Matt – “…to me, you probably weren’t using the right tool in the right place if you were upset that you were getting different answers every time with AI. You put enough constraints in, you can do enough prompt engineering and get it to be, but AI is inherently non-deterministic.”
41:52 Amazon EKS Auto Mode now supports Kubernetes Gateway API
- EKS Auto Mode now speaks Gateway API, so Kubernetes teams get the Ingress successor without running their own controller.
- EKS Auto Mode now supports Gateway and HTTPRoute resources and automatically provisions and manages the underlying AWS load-balancing infrastructure, with no separate controller to install or configure.
- Supported capabilities include HTTP and gRPC routing, weighted traffic splitting, header-based routing, and cross-namespace routing for multi-team clusters.
- It also automatically discovers TLS certificates through AWS Certificate Manager.
- Existing Ingress resources keep working alongside Gateway API resources, so teams can migrate incrementally instead of cutting over.
- Gateway API is the portable, vendor-neutral standard for Kubernetes traffic management, which helps reduce lock-in for multi-cloud shops. Canary and blue/green patterns via weighted splitting become declarative Kubernetes config instead of custom tooling.
- No extra charge for Gateway API support itself; it is included with EKS Auto Mode, and standard AWS load balancer charges apply for provisioned resources. Available in all Regions where EKS Auto Mode is supported.
45:08 Amazon RDS now supports per-snapshot billing
- AWS now lets you see the cost of each individual RDS snapshot instead of just a lump sum per database instance, which should make backup spend much easier to track.
- Previously, RDS snapshot charges were aggregated at the database instance level in the Cost and Usage Report and Cost Explorer. Now each snapshot’s cost is visible individually, so teams can see which specific snapshots drive backup spend.
- Cost allocation tags on snapshots are the mechanism for attributing costs. Teams will need to activate and apply tags to snapshots to get chargeback or showback by team, project, or environment.
- A practical use case is identifying old manual snapshots that quietly accumulate storage charges.
- This gives FinOps teams a clear path to cleanup decisions rather than guessing at the instance level.
- Enabled by default on all RDS snapshots at no additional charge, so there is nothing to opt into or deploy.
- Available for all RDS engines in all commercial AWS Regions and AWS GovCloud (US) Regions.
45:55 Matt – “This is really nice, as someone who’s had to dig through bills too many times… being able to get down to that granularity is really useful when you need it.”
GCP
46:37 VMware solution on Google Cloud
- Google Cloud just launched a self-managed VMware option that gives customers full admin control of VMware Cloud Foundation on dedicated bare metal, which matters for anyone planning a data center exit or VMware migration.
- This is a second deployment model alongside Google-managed Google Cloud VMware Engine.
- Customers run VCF 9.x themselves on dedicated Z3 bare metal, keeping control of maintenance windows, third-party monitoring tools, and existing operational playbooks.
- Each Z3 node (z3-highmem-192-highlssd-metal) has 96 physical cores on 4th Gen Intel Xeon, 1.5 TB RAM, 72 TB local NVMe, and 200 Gbps networking. Storage is vSAN ESA, with NetApp Volumes supported as an external datastore.
- Customers can bring portable Broadcom VCF subscriptions (BYOL) and apply Google Cloud commitments and Flex CUDs to the Z3 bare metal. Google claims NVMe memory tiering cuts server TCO by up to 40% and vSAN ESA cuts storage TCO by up to 39%. Specific per-node pricing was not published, so check with your account team.
- Workloads sit natively next to GCE and GKE with direct access to BigQuery, Gemini, and Cloud Run, plus networking via Andromeda and Network Connectivity Center. Up to 80% live patching coverage is also claimed to reduce planned downtime.
- Available in 22 regions at GA, with more planned.
- Additional details are available here.
47:29 Ryan – “The way I read this is that your stodgy old neckbeards that are in control of your VMware cloud that is hosted in your data center, they want all the control. And so they’re just moving it to Google Cloud because the business is making them go to the cloud. And so now they’re taking all the same problems of VMware and just moving it to some other hosting provider where there’s just an additional layer of complexity on top of those problems. So yeah, great, great idea.”
49:41 Oracle AI Database@Google Cloud: What’s new at Oracle AI World
- Google Cloud and Oracle used Oracle AI World to announce a batch of integrations tying Oracle AI Database@Google Cloud to BigQuery, Gemini, and agentic AI workflows, so this is a roundup of everything announced. That we care about
- Remote MCP Server with the IAM-governed ExecuteSQL Data API is now GA, letting AI agents run SQL against Oracle databases using Secret Manager for credentials and Google Cloud IAM for access control, with no bastion VMs, plaintext passwords, or custom NL-to-SQL middleware.
- Gemini connector for Oracle AI Database (preview) enables natural language queries against Oracle data inside the Gemini app, grounded via Knowledge Catalog integration (also preview) so responses stay limited to data each user is authorized to see. Oracle in Gemini Enterprise is available today, with 135+ prebuilt skills.
- Gemini models are also being embedded in Oracle Fusion AI Agent Studio and NetSuite.
- Data integration now offers several patterns.
- Bi-directional Iceberg access (in preview) lets Oracle Autonomous AI Database and Google’s borderless Lakehouse read and write shared Iceberg tables in Cloud Storage without ETL.
- OCI GoldenGate CDC streams from Oracle redo logs into BigQuery with sub-second freshness.
- BigQuery query federation (preview) uses EXTERNAL_QUERY to run live Oracle SQL from BigQuery with zero copy, which suits ad-hoc joins and fraud checks.
52:08 Ryan – “I can see how I would have used this, but I don’t know that it’s a great idea.”
54:10 Cloud SQL blue-green deployments
- Google is bringing managed blue-green deployments to Cloud SQL for MySQL in preview, aiming to turn major version upgrades from weekend projects into low-downtime operations.
- Cloud SQL creates a green clone of your production (blue) instance, upgrades it to the target version (for example, MySQL 8.0 to 8.4), and keeps it in sync via continuous replication.
- Switchover is available through the console or CLI scripts.
- During switchover, blue is briefly set to read-only, final data sync completes, and green is promoted.
- Enterprise Plus customers should see sub-second downtime; other editions will likely see longer, though Google did not publish figures.
- The existing IP address, instance name, and backups transfer to the new primary, so you don’t need to change connection strings or application configs. This removes one of the more painful parts of DIY blue-green setups.
- You can run real traffic and queries against green to validate performance before cutover, and delete the deployment without touching production if issues appear. The original instance remains as a safety net after switchover.
- Preview is limited to MySQL standalone primary instances, including HA configurations.
- PostgreSQL is listed as coming soon. Pricing was not stated, but green is a temporary second instance, so expect to pay for it while it exists.
55:49 Matt – “So I’ve used this on AWS’s feature, and it’s great. It’s a great way to go play and get things to make sure that they’re working before you go cut over to them.”
57:36 Use DMS to shrink Cloud SQL for SQL Server disk
- Google published a how-to showing that Database Migration Service, usually seen as a one-time onboarding tool, can also shrink an oversized Cloud SQL for SQL Server disk with minimal downtime.
- Cloud SQL disks only grow, so after archiving, purging, or a one-time spike from auto storage increase, you keep paying for peak provisioned capacity. Comparing the database/disk/quota and database/disk/bytes_used metrics in Cloud Monitoring shows when a shrink is worthwhile.
- The built-in storage shrink feature requires downtime proportional to total disk size, which can mean hours for multi-terabyte instances.
- The DMS approach instead provisions a new instance with a smaller disk, replicates continuously via full backup plus transaction log backups, and needs only a brief cutover.
- DMS replicates at the user database level only, so logins, SQL Server Agent jobs, linked servers, extended events, TDE certificates, and instance flags must be migrated manually before cutover. Using sp_help_revlogin preserves login SIDs and reduces cleanup work.
- Post-cutover, database users can be orphaned if login SIDs do not match, requiring detection with a diagnostic query and remapping via ALTER USER. The runbook overhead is a real trade-off against the native shrink’s simplicity.
- Cost savings come from reduced provisioned storage, but you run two instances during replication, so the savings depend on disk size and how long the overlap lasts.
59:26 Ryan – “I haven’t used it to shrink CloudSQL, but that’s a pretty smart use case…”
59:46 Google Cloud spend caps now generally available
- Google Cloud spend caps on Budgets are now generally available, giving teams a way to stop runaway costs without deleting resources, which is a pain point many Cloud Pod listeners have hit.
- Spend caps halt pay-as-you-go and CUD-covered usage once a budget threshold is hit, rather than deleting resources. Caps for AI services trigger within minutes using estimated live costs. Provisioned Throughput is never halted and continues serving traffic.
- A new spend caps API, part of the existing Cloud Billing Budgets API, lets teams programmatically apply, update, lift, or delete caps. A practical use is automatically applying a cap whenever a developer spins up a new sandbox project.
- Live cost reports in Cost Reports show the estimated costs that triggered enforcement, so teams can do root-cause analysis without waiting hours for standard billing pipelines to settle net costs.
- Automated monthly resets mean blocked services resume at the start of the next month.
- Previously, caps stayed locked until manually lifted in the UI. The manual override remains for teams whose governance requires an audit before resuming.
- Suggested rollout is non-production first, such as dev sandboxes, test clusters, and AI agent playgrounds.
- Default alerts go to billing admins and project owners at 50%, 80%, and 100% of the cap. Pairs with Early Anomalies Detection for a layered defense.
1:00:37 Ryan – “It’s funny that they specifically mentioned that the caps for AI services trigger within minutes, because you know what happened to cause this feature. Someone did a chatbot that went out of control and spent all their monies.”
Azure
1:02:00 Introducing the Microsoft Copilot harness: Unlocking the potential of truly multi-model agentic work
- Microsoft is opening up the agent harness that powers GitHub Copilot, Copilot Studio, and VS Code to outside developers through Microsoft Foundry, which matters if you’re building multi-model agents and don’t want to maintain your own orchestration layer.
- The Microsoft Copilot harness is the orchestration layer around the model (instructions, context, execution environment, controls), originally built by GitHub engineers and now standardized across Microsoft’s Copilot products. It’s now available as a fully managed option in Microsoft Foundry:
- It supports 20+ frontier models plus bring your own key, with routing of tasks to the appropriate model. The pitch is that customers avoid keeping up with and evaluating new models themselves, and can swap models without changing the harness or the rest of the stack.
- Technical details: the runtime was ported to Rust, which Microsoft says reduced session overhead and time-to-first-token. It supports open standards including MCP, agent skills, and agent plugins, and Microsoft runs the agent loop and sandbox with built-in governance.
- Delivery options: a downloadable SDK (https://github.com/github/copilot-sdk) or a cloud-hosted, Foundry-managed deployment. Microsoft says other harnesses and frameworks can still be used alongside it, keeping the platform open and interoperable.
1:06:17 Public Preview: JWT validation for Application Gateway for Containers
- Azure Application Gateway for Containers now supports centralized JWT validation in public preview, which matters for anyone tired of baking token checks into every microservice.
- JWT validation is configured through the AuthPolicy custom resource, so teams can enforce token signature, issuer, lifetime, and audience checks at the ingress layer instead of in each application.
- Signing keys are retrieved from a trusted HTTPS endpoint (typically a JWKS URI), which fits with identity providers like Microsoft Entra ID and other OIDC-compliant issuers.
- Moving auth to the gateway reduces duplicated validation code across services and gives platform teams a single, Kubernetes-native place to manage API authentication policy.
- Azure Storage Actions just picked up three enhancements to make automated blob and Data Lake data management less of a maintenance chore.
- Task definition updates now propagate automatically to existing assignments, so changing a storage task no longer requires manually touching every assignment that uses it.
- New execution controls give admins more say over when and how tasks run against Blob and Data Lake Storage data, which helps limit surprises on large datasets.
- Case-sensitive matching is now supported in conditions, which matters for object naming conventions, tag values, and metadata where case differences were previously treated as equal.
- Storage Actions is billed based on task executions and objects processed, so cost scales with usage.
Closing
And that is the week in the cloud! Visit our website, the home of the Cloud Pod, where you can join our newsletter, Slack team, send feedback, or ask questions at theCloudPod.net or tweet at us with the hashtag #theCloudPod
Download audio: https://episodes.castos.com/5e2d2c4b117f29-10227663/2695516/c1e-7nknsrqdz3f3j6xn-3443pv6oc57v-z4ct3j.mp3
Pennsylvania, USA

This message was just sent to Team XBOX employees globally.
Team,
Microsoft was founded on the belief that computing could put extraordinary capabilities in the hands of ordinary people. Gaming has been part of that story since the company’s beginning.
In 1979, we released Microsoft Adventure, a text-based game that looked more like MS-DOS than an early version of Minecraft. Adapted by a single programmer, Gordon Letwin, one of Microsoft’s first 13 employees and later an architect on OS/2, the game let players explore a digital world, collect treasure, solve puzzles, and encounter mythical creatures.
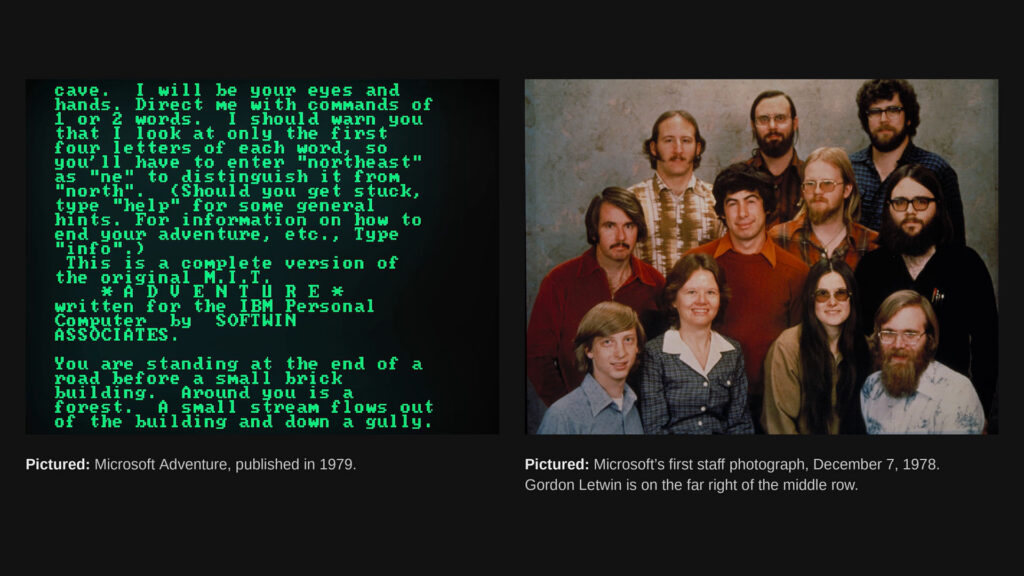
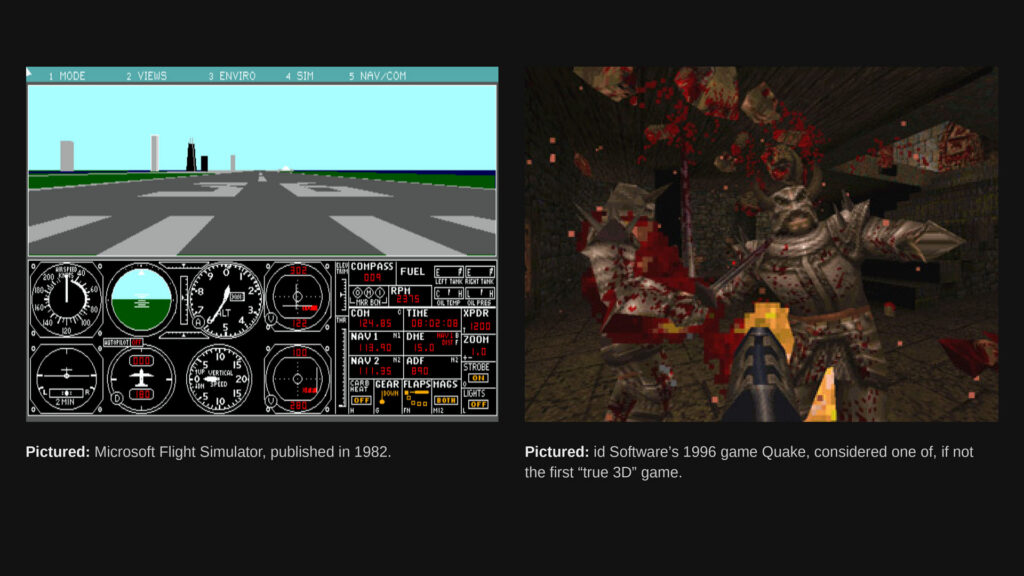
A few years later, Bruce Artwick brought the magic of flight to the 16-bit IBM PC, making it possible to fly a plane from your desk. Over the following decade, Microsoft published dozens of other titles including Minesweeper, Age of Empires, and another four Microsoft Flight Simulators, while Windows helped usher in 3D gaming with partners such as id Software (which would join XBOX some 24 years later).
In the mid-1990s, a small team working on DirectX, the technology that helped developers make games for Windows, had a big idea: using PC architecture to power the first American video game console in decades. Shortly thereafter, work began on the secret “Project Midway.”
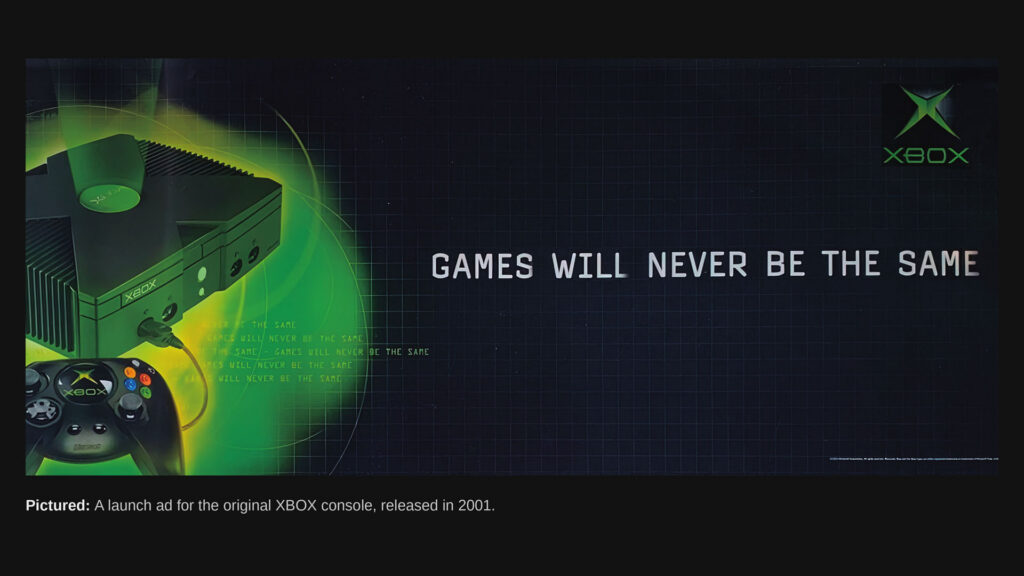
When the original XBOX launched in 2001, it was impossible to miss. It was 2-3x larger than rival consoles, with a giant X molded into a black enclosure and a bright alien green jewel at the center. It shipped with a hard drive when competitors asked players to buy standalone memory cards and an Ethernet jack when 9 in 10 households still used dial-up. It also boasted more than twice the processing power of the PlayStation and GameCube and pioneered dual analog controllers.
A year later, Xbox Live revolutionized online play with persistent friend lists and matchmaking, as well as a common service for developers to build connected experiences. And bringing all of this together was Halo: Combat Evolved, a launch title that not only defined XBOX but proved its first advertising campaign: “Games Will Never Be The Same.”
Twenty-five years later, XBOX has grown into one of the world’s largest gaming businesses. We’ve built four generations of XBOX consoles, with a fifth on the way. Today, our games reach more than a billion players every year spanning beloved and iconic franchises such as Call of Duty, Candy Crush, Diablo, Doom, Fable, Fallout, Forza, Gears of War, Halo, Minecraft, Overwatch, Sea of Thieves, The Elder Scrolls, StarCraft, Warcraft, Wolfenstein, and many more.
To Everyone Who Made XBOX, XBOX
XBOX has been built by generations of employees, studios, developers, and partners who believed in what gaming could become. To all of you, thank you. I especially want to recognize the 111 people across XBOX and our studios who have been here for 25 years or more. You’ve helped shape the history we’re celebrating today, and each of you will receive a special engraved console to commemorate what you’ve helped build.
Since joining XBOX, I’ve heard stories of friendships that began over a session and lasted a lifetime, of people who met the person they would marry, and of parents now sharing the games they grew up on with their children. I’ve also heard about people who are no longer with us, and how much those hours spent playing together still mean to those who love them. Ultimately, this is why we exist.
The story of XBOX has never been ours alone. Our fans have challenged us, cheered us on, held us accountable, and stuck with us. We’ve been celebrating this anniversary with fans around the world and special launches. Today, we are bringing the celebration home to Seattle.
The Next 25
Gaming has always been an industry driven by dreams. Not just the desire to bring something imagined to life, but to share it with others. Sometimes that dream is of a game, other times a console, a character, or an entire universe. The history of XBOX is a testament to the power of these dreams and how they can grow over time.
The first Microsoft Flight Simulator was just 160 KB, with 2D graphics, 16 colors, and 20 total airports. The 2024 version draws on more than 2.5 petabytes of data (more than 15 billion times the size of the original game). Its 200-million-square-mile map recreates almost every city, road, and landmark across the planet, with trillions of individually rendered trees and real-world weather reproduced in near real time.
While modern games demonstrate the heights of human craft in ways unimaginable just decades ago, the cost, resources, and risk required to create them have grown just as dramatically. As a result, too many ideas never become games, and too many games fall short of what their creators imagined. For decades, this has been the unavoidable tradeoff of ambition. We must change this.
Throughout human history, the scale of what we could create was determined by the people, capital, and resources we could command. That relationship is beginning to break. A single person will soon be able to wield capabilities that once required entire nations. A small team will be able to build worlds that today demand hundreds of developers and hundreds of millions of dollars. And our largest studios will be able to pursue ambitions as far beyond today’s games as Microsoft Flight Simulator 2024 is from its first entry in 1982.
I believe the future of gaming will look more like its beginning, when a small team with a big idea could change how the world plays. Our responsibility is to deliver great games, unmistakable hardware, and give more people the chance to make something the world has never seen.
Happy Birthday XBOX!
Asha
The post 25 Years of XBOX appeared first on XBOX Wire.
Pennsylvania, USA
Next Page of Stories