An anonymous reader quotes a report from The New York Times: School cellphone bans are beginning to modestly improve students' academic performance, according to the first large national analysis that compared students' test scores before and after the bans. Schools with strict bans -- requiring students to lock their phones in pouches all school day -- saw math and reading scores improve as if students had an additional week or two of school a year, the study found. It was published Tuesday by the Center for Education Policy Research at Harvard.
U.S. students' test scores began falling over a decade ago. The drop coincided with the rise of smartphones, raising questions about their role in the decline. The evidence so far on the academic effects of phone bans has been mixed. But the new study indicates they are starting to have an influence.
The study looked at 3.3 million students between 2021 and 2026. They were in third through 10th grade, attending 4,600 U.S. schools. Using scores on MAP tests, which track achievement from fall to spring, it compared the performance of students at schools that put in strict phone bans with those at similar schools that did not have such bans. The annual gains reversed about half the annual loss that an average student experienced in the years leading up to the pandemic. (Students lost even more ground during pandemic closures.) "The earlier studies on cellphone bans have been dismissed as implying small impacts, and in-school cellphone use has been ruled out as playing a big role in the decline," said Thomas Kane, a professor at the Harvard Graduate School of Education and an author of the study. "But we think that's mistaken."
At 9AM last Thursday, everything seemed normal. Microsoft employees were arriving on campus, ready for a regular day of emails and meetings. But barely an hour later, one of Microsoft's worst outages in history started to unfold, leaving employees, businesses, and many governments without access to Outlook emails for nearly 24 hours.
It all started in Switzerland, according to a source familiar with the outage. Exchange Online servers that power Outlook started to fall offline. The problem quickly spread to Mexico, and then to other countries around the world, as Microsoft's failover systems tried to shift email traffic elsewhere. Within a …
Satya Nadella, Microsoft Chairman and CEO, delivered the opening keynote at Ignite in San Francisco this morning. Here is an edited version of his remarks.
This week is about two things: First is how we capitalize on new capabilities that are growing exponentially. And second is how do we build the capability to deal with the consequences of these exponentials.
At times like these, I always find it helpful to be grounded in our mission: To empower every person and every organization on the planet to achieve more. In today’s world, that means building a frontier ecosystem. We need to parlay any technological advance into real outcomes and new points of leverage for people, organizations and society at large.
For us, that comes down to three things: Keeping human ambition at the center, ensuring your control of your organization’s intelligence and learning, and trust.
And so, our goal is to build a stack that addresses these three core architectural principles.
Copilot
Copilot is the new OS for work. Copilot brings together all the new form factors of human-computer interaction, whether it is Chat, Cowork, Code or Autopilot, into one experience. It also brings together the disparate categories of knowledge work, coding and business process. That is why we have all of Office with its richness built into Copilot. And underlying it is a model system that matches the right intelligence to the right context to the right form factor to accomplish the task.
Home gives you one place to start, whether you need a quick answer or want to assign and complete complex, multi-step tasks. Code brings the power of an infinite SaaS factory to every individual. It lets you build your own custom SaaS apps, dashboards and much more. And Autopilot is an autonomous agent that keeps moving your work forward 24×7 in all the places where you and your team collaborate.
Underlying all this is Work IQ. You can think of this as the most important database for any organization, with a deep understanding of people, their relationships, documents, emails, meetings, chats and projects that make up the fabric of work.
And we are going further. We are extending Copilot for specific roles: sales, legal, finance, service. We are organizing the skills, connectors and plugins for these roles across the entire surface area of Copilot.
And that includes third-party systems, too. In fact, today we are announcing new plugins for business applications, starting with Dynamics 365. And it is not just Dynamics. We are very excited to partner with Salesforce to bring Salesforce to Copilot.
And we are going beyond that as well. Up until now, we have mostly been in a single player world of people and their agent loops and swarms. But the time has come for a true multiplayer form factor, where people, their agents and other people are all driving towards a common goal, with shared context. This is Copilot Workspaces:
YouTube Video
Microsoft IQ
The idea behind IQ is to help every organization build, retain and continuously improve its own intelligence. Essentially, we are taking the system we built underneath Copilot and externalizing it as a first-class platform that embodies your organizational intelligence as an asset that you continuously build and control.
We are bringing together all of the data you have across Fabric, Foundry and Microsoft 365. And, of course, all the third-party context too. Microsoft IQ comes with hundreds of new connectors we are announcing today, so agents can get the full enterprise context where business gets done. And all this rich context manifests as business plugins that can be shared and inherited across the organization.
Models
For us, it is about mapping intelligence to a given task, with the best economics. This is something we can uniquely do in the context of real-world tasks by tuning our products, harness and tools, and the model system, end-to-end.
And today we are thrilled to announce Microsoft-Decision-1.1, which is now generally available and ready for enterprise deployment. We have added multimodal support. And we have improved performance, making decisions more accurate and responses faster. Already, more than 4,000 customers have used it. And we ourselves are using it for core tasks like routing, data labeling, personalization, content filtering and hundreds of other use cases.
Foundry of course has all the most popular closed and open weight models, too. We are very excited to bring GPT 6.2 to Foundry. It is a great model that sets a new bar for AI in professional work. And today we are announcing that Meta’s latest models are all coming to Foundry as well.
We are also innovating at the frontier with our own MAI model family that is both compute-efficient when it comes to pre-training and token-efficient when it comes to product deployment. Our goal is to put additional points on the frontier curve informed by real world task-performance.
And we are going further. We are announcing MAI Licensed Weights, meaning our trusted customers will now be able to get access to Microsoft AI model weights through our Frontier Co.
Today, we are introducing lots of new models. But I want to highlight two in particular:
First, Code. We are introducing our new flagship family of agentic coding models: Code 2. Code 2 is at the frontier of cost-performance for everyday enterprise coding tasks. It excels in taking code to production, deep debugging, multifile implementation, repo-wide reasoning and UI at a fraction of frontier cost.
Code 2 Flash is designed for fast, high-volume work like code explanations, targeted edits, routine fixes and rapid iterations. It brings near-flagship quality for a much lower cost. These models are both generally available today on GitHub Copilot, both in the model picker and as part of Copilot Fusion. They are also available in Foundry.
We are taking the same approach in cyber. Cyber 2 Flash is our most capable security model yet. It is a flash-sized model that delivers performance ahead of frontier models at a fraction of the cost per task. And, just as we have done with coding, we are co-designing the model with the tools and systems where it will be used. We are integrating Cyber 2 with Perception.
Agent 365
Successfully deploying AI systems starts with making sure you have observability at every layer of the stack. That is where Agent 365 comes in. It is a control plane that extends your existing governance, identity, security and management systems to the agents in your enterprise. We already have over 50 million agents in Agent 365.
And it includes FinOps, too. As AI scales, every organization needs a clear line between what it spends and the value AI creates. That is why today we are announcing Agent 365 Business Analytics. You can think of it as your ERP system for AI usage. You can see exactly what is driving spend. You can connect spend to outcomes to drive business value. And you can optimize ROI across different scenarios.
Security
The next thing I want to talk about is how you take the environment you have set up, from Copilot to IQ to Agent 365, and secure it. And that is where Perception and our security stack comes in. We are building an end-to-end trust platform. We are helping customers both secure their AI deployments and use AI to strengthen their security posture.
Perception is a complete agentic security system with teams of red, blue and green agents that run through playbooks to deliver security outcomes at machine speed, with you always in control.
Essentially, think about it like this: red team agents simulate attacks, blue team agents detect attacks and green team agents fix and remediate. With Playbooks, you can compose teams of agents to tackle complex jobs and trigger them to take action autonomously.
Perception helps connect all the signals, sensors and actuators across your identity, client, cloud, apps and agents to intelligence to secure your end-to-end environments. And I am very excited to share that Perception is now generally available.
In addition to the work we have been doing across our products, we are also working across the ecosystem to ensure everyone can innovate at speed and scale, safely. Today, we can see almost everything models touch. But we cannot see what happens inside the model. And what the model tells us about itself is not independent evidence. These nested black boxes are simply unacceptable. We need to be able to examine what AI sees and does, verify its actions independently and control what it is allowed to do.
That is why today we are also announcing the Microsoft AI Transparency Initiative.
There are three parts to this: First, we will expand our collaboration in NIST’s Agent Standards Initiative, drawing on its research to help lead the development of open, industry-wide standards for AI transparency, security and governance.
Second, we are taking a full ecosystem approach. Together, we can enable AI systems that are accountable, independently verifiable and safe by design, regardless of the model or provider. Already, 40 organizations are working with us on defining and applying these standards.
Third, we are working to incorporate the same standards in our products, including MAI models, Foundry and Copilot. Our ambition through our research, our product work and our ecosystem is to help establish an open industry standard that makes AI safer, more transparent and more accessible.
Cobalt 200 VMs
Underneath all of this is unbelievable silicon. We are building a heterogeneous platform working across the ecosystem to bring you all the latest innovation. We are also advancing our own hardware systems, co-designing silicon, servers and infrastructure to get more from every watt, chip and datacenter.
We just announced Maia 300, which will deliver 40 percent more tokens per watt compared with leading GPU-based systems. Azure Boost and Azure Integrated HSM move critical infrastructure and security functions into purpose-built silicon. And today we are announcing general availability of our next-generation Cobalt 200 VMs, which are our highest-performing general-purpose VMs with leading price-performance.
So, that is a quick walk through some of our news. When you look at all that is coming, it is clear that we are entering an era of ubiquitous intelligence. The key imperatives for us are to ensure human ambition, a firm’s control of its own intelligence and the diffusion of the benefits broadly. That is the promise of a frontier ecosystem. And that is what we are here to build together.
For more information on today’s announcements, check out the Book of News.
AI has made finding potential vulnerabilities fast and cheap. Fixing them still takes human judgment, and in open source, that work falls to maintainers. Many are already flooded with AI-generated security findings, including duplicates and reports that aren’t vulnerabilities at all. Another raw scan doesn’t help them. Anyone pointing a new model at a project should ask its maintainers first and come with fixes, not just findings.
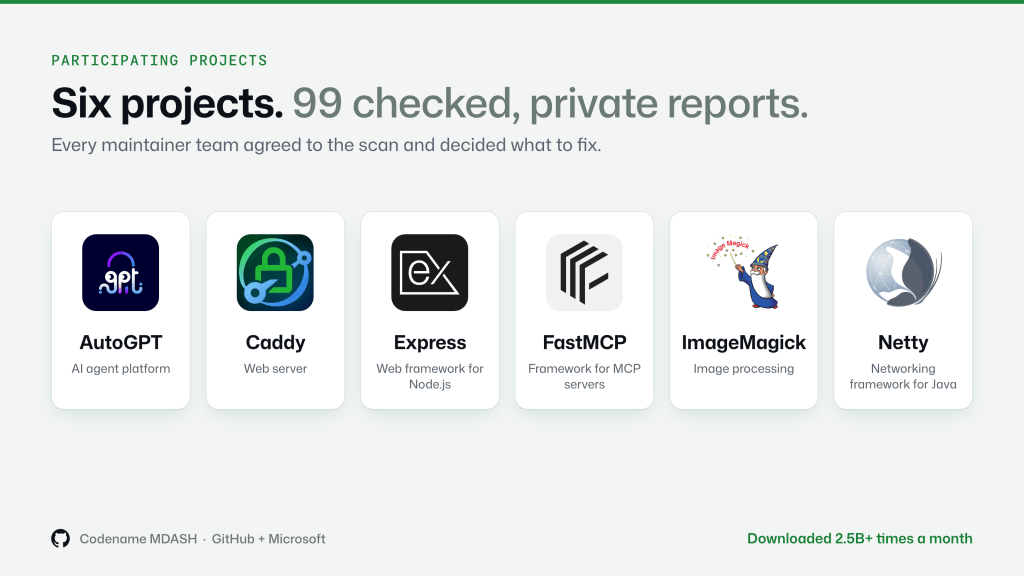
AI shouldn’t add to maintainers’ workload. So, with maintainers, GitHub and Microsoft ran a pilot together: could AI help maintainers ship fixes instead of handing them more findings?
GitHub and Microsoft are using Codename MDASH, Microsoft’s multi-model agentic scanning harness, to find and fix security vulnerabilities in widely used open source software, strengthening the foundation that much of the world’s code is built on.
The process
Our pilot had two goals: send only findings that matter, and never send a maintainer an unverified finding. Here’s how it worked:
Find.Codename MDASH, an AI system from Microsoft Security, scanned each project using Microsoft’s MAI Cyber model and suggested fixes for what it found.
Filter. An AI triage agent from the GitHub Security Lab, built on tailored Copilot skills, removed duplicates, checked validity, and focused on high-impact bugs, so maintainers never had to review raw scan results.
Report privately. Reports reached maintainers through GitHub private vulnerability reporting, with a proof of concept and a suggested fix.
Fix. Maintainers decided what to fix, how to fix it, and when.
Reports and fixes stayed on GitHub, where maintainers already work.
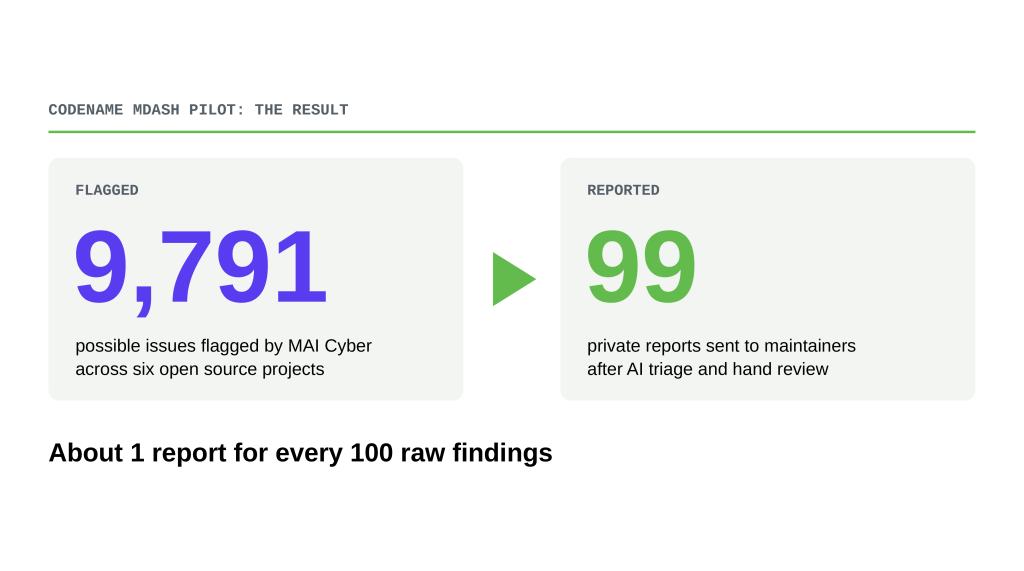
The result: Codename MDASH, using Microsoft’s MAI Cyber model, flagged thousands of possible issues across the six projects. After AI triage and hand review by seven Microsoft FORGE Lab researchers, maintainers received 99 private reports. As of November 15, they had fixed 55, and 14 of those fixes were already in a release.
What we learned
These lessons come from what the six projects fixed and what their maintainers chose to share. Six projects is a small sample, so read them as early lessons.
1. Fixes matter more than findings
Fixing is where maintainers spend their time. So every report arrived already checked, with a suggested fix to review, adapt, and merge. Maintainers started from a well-scoped patch, not a raw finding.
The first fixes shipped about a week after the initial scan. Caddy’s maintainers fixed all 22 of the reports they received in a week or less. Maintainers used the suggested fixes, some as written and some with changes.
AutoGPT’s maintainers had recently shipped a new check, and it was broken. The report landed three days later and pointed at the right line. They took the fix further than the suggested patch, wrote it within a day, and had it in production less than a week later.
Finding vulnerabilities is no longer our bottleneck. Fixing them is the hard part, and that depends on maintainers.
Netty maintainer
2. Codename MDASH, with researcher review, gave maintainers high-quality findings with fixes
Maintainers got a short list, not a flood. Express maintainers said the reports cut through the noise. Caddy maintainers said they surfaced obscure bugs and filled gaps that earlier reports had missed. For FastMCP, the scan went beyond what AI scanners had given them before. ImageMagick, maintained by a two-person team, received 22 reports.
AI did the finding, researchers did the checking, and maintainers stayed in charge.
One ImageMagick report looked like a kind of issue the maintainers had seen before. Its summary showed it wasn’t and pointed to the exact lines of code. They were able to push a fix in 15 minutes.
Normally, a security advisory would take us around 30 minutes to 1 hour on average to read, understand, and make a fix. It is a huge difference.
ImageMagick maintainer
Codename MDASH was able to find unknown, obscure security bugs in our project with succinct reports, and it filled in gaps from some prior reports that hadn’t been noticed.
Caddy maintainer
3. Open source still has gaps to close
The pilot worked because people did careful work at every step, and that work doesn’t scale yet. Seven researchers spent about two days per project checking findings by hand. Meanwhile, low-quality reports still reach maintainers every day.
For open source, fixes need to be delivered via private vulnerability reporting (PVR). Maintainers need to run CI/CD tests on private forks to verify those fixes. And to close the gap between defenders and attackers, maintainers need access to cyber-capable models to verify a proof of concept, before and after the fix.
The Codename MDASH scan provided unique insights into the security of our project above and beyond what AI scanners have provided us in the past
FastMCP maintainer
Why it matters
If you’re a maintainer, this approach changes what a security report costs you. A checked, private report that comes with a suggested fix takes less of your time. You shouldn’t have to triage a scanner’s output. That’s the sender’s job.
If you use AI to find vulnerabilities in open source, maintainers’ feedback points to this standard:
Check every finding before you send it, against what the project already knows and against its threat model and security policy.
Report it privately.
Include a suggested fix. Let maintainers set the pace.
Features are easier and easier to ship, but in the future maintaining software will probably come down to who cares enough to manage the security.
AutoGPT maintainer
Codename MDASH is very useful for cutting through the noise of vulnerability reports.
Express maintainer
What you can do today
If you maintain any open source project, turn on private vulnerability reporting so researchers can report security issues to you without making them public. If your project is on GitHub, turn on core security features in about two minutes with gh-secure.
If you build on open source, turn on Dependabot alerts so you know when a dependency you use needs a security update.
If you send AI-generated vulnerability reports to open source projects, hold them to the standard above before you send them.
Repositories using GitHub code security can use agentic autofix to help automatically remediate their alerts with Copilot
What happens next
Fixes, where maintainers already work. GitHub is bringing these lessons into private vulnerability reporting and security advisories, where GitHub Security Lab is already investing to reduce the burden of low-quality reports on maintainers.
MAI Cyber 2. Today Microsoft announced MAI Cyber 2. The Codename MDASH pilot ran on the earlier MAI Cyber model. GitHub and Microsoft will keep working together to help secure open source.
Closing the gaps, starting with the GitHub Secure Open Source Fund. We’re working with Microsoft to scale researcher review without cutting corners. GitHub will offer every alumni project AI security scans, with findings checked before they’re reported privately. Alumni also get GitHub Copilot Max. We’ll bring this support to future sessions of the Fund.
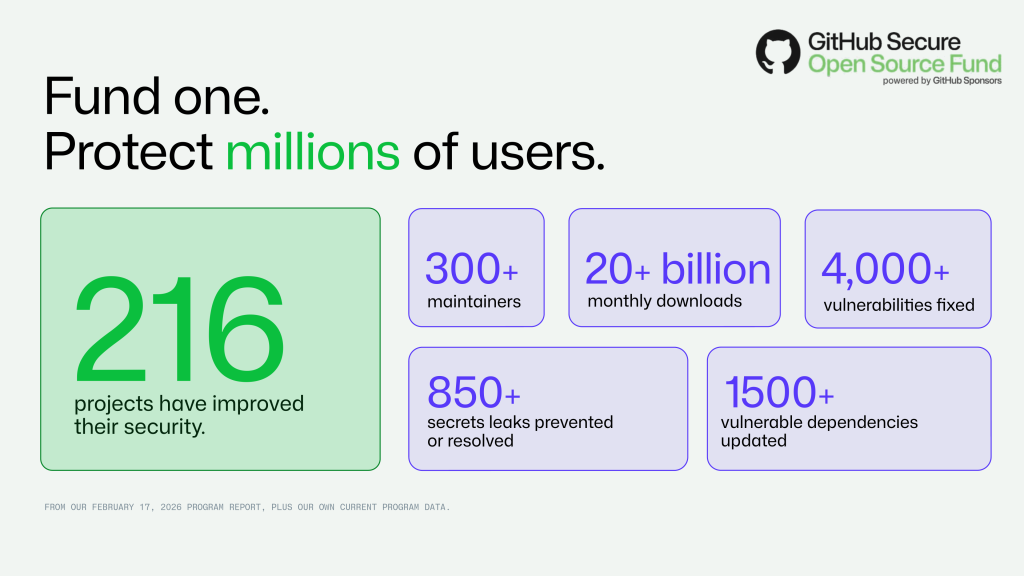
Everyone downstream benefits from this system. When a maintainer publishes a security advisory on GitHub and it’s reviewed for the GitHub Advisory Database, Dependabot can alert the repositories that depend on that package. That’s the idea behind the GitHub Secure Open Source Fund: 216 projects so far, with more than 300 maintainers fixing more than 4,000 vulnerabilities in software downloaded more than 20 billion times a month.
Thank you
To the maintainers of AutoGPT, Caddy, Express, FastMCP, ImageMagick, and Netty: thank you for your time, your trust, and your feedback. Thank you also to the Codename MDASH team at Microsoft Security, the MAI Cyber team, the researchers of Microsoft FORGE Lab, and GitHub Security Lab.
Maintainers do the fixing. Our job is to make sure they never do it alone.
Hear from maintainers about their experience with Codename MDASH. 👇
About the GitHub Secure Open Source Fund
All six projects in this pilot are alumni of the GitHub Secure Open Source Fund, which gives each project $10,000 through GitHub Sponsors, plus security training and a supportive alumni community.
The GitHub Secure Open Source Fund, powered by GitHub Sponsors, funds open source projects that underpin the digital supply chain, catalyze innovation, and are critical to the AI stack. Want your company to help secure the open source it depends on? Become a funding partner through the Fund page. Learn more about the Fund or apply.
Through the Fund, maintainers receive security training and Azure credits from Microsoft for Startups. That support sits alongside Microsoft’s European Security Program and its Secure Future Initiative, whose principle is security above all else. Most organizations are downstream in the same way. If your software depends on open source, do the same: back the maintainers you rely on.
A year ago, finding a serious, exploitable vulnerability was slow and expensive work done by elite security researchers. That’s no longer true. Over the past 12 months, frontier AI models have become remarkably good at discovering and exploiting software vulnerabilities, and similar levels of capability are quickly becoming available in open weights models with limited cyber guardrails. Attacks that once required specialized resources are now within reach of almost anyone.
We saw what that looks like in a single week this fall when PHP disclosed two critical remote code execution (RCE) vulnerabilities, flaws that let an attacker take control of a server with a single request over the internet.1 At the time of disclosure, tens of millions of internet-facing PHP services were running affected versions. Nearly two weeks later, about 29 million services remained vulnerable. Behind those servers are banks, healthcare providers, energy companies, and much of the infrastructure the internet runs on. And that same day brought five other major disclosures across the industry.
Turning a flaw like the PHP one into a working attack once took a specialist team months. Within roughly a day of PHP2Shell’s disclosure, security researchers had developed a working, weaponized exploit. By the following week, that research had expanded to cover additional PHP versions and configurations. The time from discovery to exploit is shrinking from months to minutes.
The physics of cybersecurity are changing, and fast.
AI is amplifying risk. Attackers can now find and exploit gaps faster than defenders can close them.
Attacks are becoming fully automated. AI has moved from assisting attackers, to executing their tasks, to planning and running entire campaigns on its own.
Agents are the new insiders. While not inherently malicious, they perform tasks and business workflows at machine speed, around the clock, and have broad access to data, apps, tools, and other agents. Like any insider, they can make mistakes, be manipulated, or be compromised.
What we built for humans does not scale for AI. Frontier Transformation starts with business outcomes and a simple idea: technology was invented to serve humanity, not the other way around. To help organizations bring their ideas to life and innovate safely in the agentic era, we need a new cyber stack, built for agentic security.
A new cyber stack, built to fight AI with AI
The Microsoft cyber stack has three layers:
Signals, sensors, and actuators. This foundational layer is powered by sensors and actuators in Microsoft Defender, Microsoft Entra, Microsoft Intune, Microsoft Purview, Microsoft Sentinel, the network, the operating system, the browser, and our hyperscale cloud. Sensors tell you something is wrong. Actuators let you do something about it: contain a device on the network, revoke an identity’s access, or block an agent at the authorization layer. And because we know we’re not the only security solution provider in your environment, we connect to the wider ecosystem through more than 500 connectors. Together, Microsoft and partner sources produce more than 165 trillion signals a day,2 which, enriched by Microsoft and customer threat intelligence, fuel the context layer.
Context. This layer organizes those signals, together with each customer’s own environment, into agent-ready, real-time understanding of the digital estate that is optimized for precision, recall, and token efficiency.
Agents, harness, and models. On top are specialized security agents that work together as teams through playbooks, directed by a harness, and a multi-model approach that uses the right model for each task, designed to ensure effective and efficient security outcomes, at scale.
Perception brings the top of the stack together. It orchestrates red, blue, and green team agents through playbooks, working together in a closed loop to deliver security outcomes. Red team agents simulate attacks from an attacker’s perspective before a breach occurs. Blue team agents detect, triage alerts, and investigate attacks, freeing analysts to focus on the critical decisions that matter most. Green team agents fix and remediate.
Perception is built to help security teams move at machine speed, drive outcomes rather than tasks, and automate while staying in control. Your team sets the guardrails and signs off on high-impact actions, and automated triggers launch playbooks when an incident meets the criteria you set. New cost management dashboards and a cost estimator help you track AI usage, forecast spending, and connect costs to measurable security outcomes.
Agents are only as good as what they can see and what they can do. That’s why we are investing as much in the foundation as in the layers above it.
Integrated Security Operations Center (ISOC) in Microsoft Defender, generally available for core capabilities, is part of that foundation. ISOC brings security information and event management (SIEM) capabilities, user and entity behavior analytics (UEBA), threat intelligence, and threat protection and disruption together so you can start your journey to the agentic security operations center (SOC). Eligible Defender Suite, Microsoft 365 E5, and Microsoft 365 E7 customers receive all Microsoft Sentinel SIEM features, 90-day default data retention for Defender data, more than 500 connectors, reduced ingestion rates, and a built-in data lake. The complete breadth of SIEM capabilities is now in preview.
Read on to learn how Microsoft Perception, ISOC in Defender, and new capabilities across the stack work together to help customers secure their foundations, secure agentic insiders, and defend with agents.
Secure your foundations
Defending against AI-speed attacks starts with closing the doors attackers walk through first, and the scale of that work is increasing. In 2026, more than 96,000 vulnerabilities3 have been published to the CVE (Common Vulnerabilities and Exposures) Program, more than double 2024’s roughly 40,000 and more than 20 times the level of 2010,4 driven in part by AI-assisted vulnerability discovery tools.
Yet only 26% of vulnerabilities in the Cybersecurity and Infrastructure Security Agency (CISA) Known Exploited Vulnerabilities catalog were remediated in 2025, as remediation typically extends into weeks and months. AI finds those gaps faster than teams can close them. Today we’re announcing new capabilities to help.
Strengthen your security foundation with Perception. In preview in January 2027, new AI Readiness Initiatives in Perception turn Secure Now guidance into actionable plans with shared progress tracking, helping organizations close critical security gaps, and prepare for AI adoption. Initiatives focus on scenarios that help reduce AI-amplified risk such as modernizing authentication and deploying monthly updates.
Prioritize and reduce exposure with Perception agents and playbooks. Focus on the risks that matter most and coordinate remediation using threat intelligence and business context. Two new playbooks bring together green team agents, including the Posture Prioritization Agent, now generally available, and the Risk Reduction Agent, now in public preview. Coverage spans Microsoft, Amazon Web Services (AWS), and Google Cloud.
Vulnerability shielding, available in preview, helps protect vulnerable assets from exploitation by applying targeted, temporary protection to buy defenders time before they can apply a permanent patch. During routine operations the Risk Reduction Agent proactively suggests shielding when patches aren’t immediately available. During an active attack, vulnerability shielding helps reduce exposure to certain vulnerabilities by applying targeted, temporary protections while organizations prepare immediate remediation. In supported scenarios, these protections can include adjustments to network accessibility and permissions to help limit exposure.
Secure data across humans and agents with Microsoft Purview. Enhanced data classification drives precise protection with less manual effort, generally available in January 2027. Also entering preview in January: grounding protection for Copilot based on sensitive information types, which lets customers adopt Copilot without labeling every file first, and expanded data loss prevention (DLP) controls for prompts to Copilot and local agents running on Windows, which help protect sensitive data from leaking while customers use AI. Learn how Microsoft Purview accelerates data protection for the AI era.
Defend with agents
A SOC where people work through a queue of alerts by hand can’t keep up with increasingly autonomous attacks. Perception brings specialized red, blue, and green agents, and playbooks that automate common SecOps workflows, so defenders can get ahead.
Stop threats at machine speed with new Perception playbooks and agents.Accelerate threat detection, investigation, and response with new playbooks and four blue team agents, now generally available: Alert Triage Agent, Attack Investigation Agent, Detection Authoring Agent, and Threat Intelligence Agent. Helping teams move from detection to response faster, with less manual effort.
See it in action: Watch agents triage an incoming alert, investigate the attack end to end, and then improve detection rules that help identify similar threats in the future.
Stay ahead of attackers with new Perception playbooks and agents. Proactively find and validate weaknesses with playbooks that coordinate red team agents, including the Recon Agent, now generally available, and the Web App Pen Test Agent, now in preview, helping security teams identify and address vulnerabilities before attackers can exploit them.
See it in action: think like an attacker with the Protect web app playbook, which runs a pen test against your app, surfaces the weaknesses that matter, and drives the fix through to your code in GitHub.
Use Perception in your flow of work. Teams can now invoke Perception playbooks in Defender, connect through Model Context Protocol (MCP) and APIs to SIEM, security orchestration, automation, and response (SOAR), and IT service management tools, and bring in signals from AWS, Okta, and Salesforce. These integrations are in preview.
We are also expanding the preview of Codename MDASH, our agentic code scanner, which helps customers find and fix vulnerabilities. MDASH can now analyze repositories up to 5 GB, run in regulated clouds, and MDASH code scans can be used by the Web App Pen Test Agent to prioritize and fix vulnerabilities. MDASH adds more of the MAI Cyber family, including MAI Cyber 1.1 Flash and MAI-Cyber-2 in preview,5 improving efficiency while maintaining the quality of security findings. Learn more about MAI-Cyber-2.
Agents are the new insiders. They operate continuously, collaborate with other agents, change shape, and pursue goals in ways that can surprise the people who deployed them. To mitigate this risk we must discover agents, onboard them to management, secure and contain them, and do it continuously—even as their behavior and context change. Building on our October 2026 announcement, at Ignite we are introducing new capabilities to help customers secure agentic insiders, around the clock.
Continuously contain agentic insiders with new Perception playbooks and agents. Investigate and remediate AI posture risks and anomalous agent behavior with new playbooks and green team agents. Microsoft Entra ID Governance dynamic permissions grant task-scoped, time-bound access, while Conditional Access dynamic controls adjust protections as risk changes. These capabilities remain in limited preview.
Discover, govern, and secure agents with Microsoft Agent 365 and Microsoft Entra Suite capabilities for agentic insiders. Discovery expands by 35 local agent types, to 60 in total, including Claude Code, OpenAI Codex, and GitHub Copilot, plus third-party cloud agents on AWS and Google Cloud. Discovered agents receive a Microsoft Entra Agent ID and can be governed with Conditional Access. Intune policies contain supported local agents on the device. Additionally, Microsoft Autopilot agents get their own Agent user account and ID, so admins can enable Conditional Access, ID Protection, and access governance to the work an Autopilot does under its own identity. Defender and Microsoft Purview Data Loss Prevention protect runtime and sensitive data access, and Dynamic Agent Risk assesses each agent’s exposure, blast radius, and runtime behavior. Available in preview.
While these capabilities can enable customers to secure and contain agents, they will not give them insight into how the model behind an agent behaves. Without that visibility it is hard for customers to answer three basic questions about consequential AI activity:
What was the AI asked and authorized to do?
What happened between the request and the outcome?
Can we independently verify it?
That’s why Microsoft is announcing the next phase of our commitment to responsible AI: the AI Transparency Initiative. We believe every organization should be able to see what its AI accesses and does, independently verify those actions, and control what it is permitted to do, whatever model or provider it runs on. To that end, we are expanding our participation in the National Institute of Standards and Technology’s (NIST) SI Agent Standards Initiative,6 plus drawing on our own research to develop open, industry-wide standards for AI transparency, security, and governance. We’re shaping this approach with more than 40 organizations including Accenture, Adobe, KPMG, Mastercard, and Volvo Cars. And we will implement this work across Microsoft AI models and products, including Microsoft Foundry and Copilot.
The more agency we give AI, the more transparency we should expect in return.
AI is changing how attacks happen, and how security work gets done. Developers, IT, and security teams now share responsibility for building, managing, and securing AI, so Microsoft Foundry, Microsoft Agent 365, and Perception share the same signals and context. Inside the SOC, analysts need agents to defend at machine speed, which is why we’re building agentic security into the tools they already use.
Technology alone won’t get us there. Securing our own environment through the Secure Future Initiative has taught us a great deal, and our Frontier Security Engineers, services teams, and partners are working side by side with customers to put those lessons to work.
Join us at Microsoft Ignite, online or in person, to learn how Microsoft Perception, ISOC in Defender and new capabilities across the stack can help secure your organization at machine speed. We’d love to see you there.
To learn more about Microsoft Security solutions, visit our website. Bookmark the Security blog to keep up with our expert coverage on security matters. Also, follow us on LinkedIn (Microsoft Security) and X (@MSFTSecurity) for the latest news and updates on cybersecurity.
5Signing up does not guarantee access. Submissions are reviewed, and customers are onboarded based on need and prioritization. Customers should work with their account team to be formally nominated for the preview.
“Any sufficiently advanced technology is indistinguishable from magic.” – Arthur C. Clarke
Most developers now write less code by hand. Gergely Orosz recently posted that modern software engineering is no longer done without LLMs and will no longer be done without them. Some miss writing code, while others question how much of the code that agents produce should be read. Writing and reading code gave a lot of developers satisfaction and identity, and as Kent Beck has put it, a sense of competence. I saw this in real time.
Ten years ago, I’d sit at conferences and feel a sense of wonder whenever anyone was brave enough to do a live demo. I felt gleeful when they wrote lines of code, went back to fix mistakes, and made something cool and interesting appear on the screen in front of me. It was magical, and I’m sure that magic is why a lot of developers got into this industry. I can partly understand the sense of loss that people are experiencing. I saw magic, they were in charge of the craft of their code, and that hands-on task has now been given to agents. Where does that expertise go when AI is now writing so much of the code?
As Tim O’Reilly wrote in his recent Radar post, O’Reilly is a business built on cultivating and sharing human expertise. Our job is to find the high ground where that expertise still matters. For developers working in a new world of agentic software factories, I think the expertise you built writing and maintaining software hasn’t gone, it’s just moved. Your expertise now shapes how agents produce software and what evidence you need before we trust the result. To me, AI is enabling you to be magical faster.
Agents amplify whatever you give them, but you need to understand it in the first place. I couldn’t swarm a fleet of agents in the same way a developer can because I don’t have the expertise. You need to understand code. The expertise has gone to a new level of abstraction.
When I spoke recently with Avi Flombaum, the founder of Flatiron School, he agreed that developers’ value was never solely in writing or reading code. AI changes the mechanics, but experience still matters for understanding complex problem domains, articulating what needs to be built, and bringing judgment and ambition to the work. In a separate conversation with Ken Kousen, he pointed out, “We’ve been working with third-party code generators for years; we just called it outsourcing.” This new world of designing AI workflows, setting guardrails, and managing agents much as you would an engineering team, reveals a chance to use accumulated expertise more. It’s your software engineering expertise that matters.
Software factories make this shift especially visible. Companies are now putting agents to work across the development lifecycle, aiming to take work from an initial signal through implementation, validation, and deployment without a person at every step. But generating more code is only part of that process. Without changes elsewhere, you can burn a lot of tokens producing a pile of pull requests that someone still has to review. Anthropic’s AI-native SDLC playbook points out that speeding up implementation shifts pressure onto planning, testing, review, handoffs and approvals, and faster coding tools don’t speed those up on their own. Someone has to understand the whole process well enough to redesign it.
In a software factory, that judgment has to be built into the system. Humans design the workflow, define the conditions under which work can proceed, and decide which exceptions need their attention. Anthropic reports that Claude authors about 80% of the code merged into its codebase, alongside a review process that combines automated checks with human oversight according to risk.
The state of the code matters too. Adam Tornhill and the CodeScene research team found that across C++, Java, and Python codebases, agents working on unhealthy code used 35–45% more tokens to complete the same tasks. That makes refactoring the parts of a codebase agents touch most a sensible investment, but someone has to know which parts those are, decide what “better” looks like, and confirm that behavior hasn’t changed.
Context works the same way. In Port’s testing, giving agents structured context cut costs by about 58% compared with direct access to separate MCP servers. Adding instructions on where to find relevant information pushed the savings to around 80%. Those figures are specific to Port’s experiment, but the work behind them will be familiar to any experienced developer: knowing which relationships in a system matter, and keeping that knowledge accurate as the system changes. Testing tells you whether a particular change works, but evaluating the workflow tells you how reliably it produces acceptable changes and when a person needs to step in.
In Evals for AI Engineers, Shreya Shankar and Hamel Husain describe starting with real traces of what the system did. First comes open coding: reading the traces and writing short notes on what went wrong. Then comes axial coding: grouping those notes into failure categories based on what you actually see. A developer who has spent years debugging production systems will spot the failures that matter and set aside the ones that don’t far faster than someone who hasn’t. That’s where developers’ experience shows up now: in the problems they define, the standards they set, and the evidence they demand before anything ships.
Every shift in every industry has made some people miss the old ways, but the industry has survived. Back in December 2025 I wrote: “AI rewards strong engineering; it doesn’t replace it,” and I stand by that statement. Developers are still magical to me, even when they’re not the ones writing the code. I couldn’t build a software factory myself because I don’t have the years of experience it takes to know where agents should work, how to guardrail them, and how to judge what they produce. The developers who do are the ones I trust to build it. And, as Ben O’Mahony pointed out to me recently, “Those who have a lot of exposure to Agentic engineering have seen past the magic and are back to engineering!” It’s an exciting time to be involved.
Want to understand how to think about engineering craft in this new world? Join Avi Flombaum for his new series, The Agentic Rethink, starting Wednesday, Jan. 13, 2027, on the O’Reilly platform.
 Log in